
x_Trader_
247 Posts
x_Trader_
Report
Block User
Content Creator | Crypto Trader | Gold Trader. I think that's enough.
63 Following
3.1K+ Followers
600 Liked
Posts
All
Quotes
Live
PINNED
·
--
Verified
#KiteBBW $KITE
There are two lazy ways to let an AI agent spend money.
Give it a standing key and hope, or approve every payment by hand and stop using the agent for anything real.
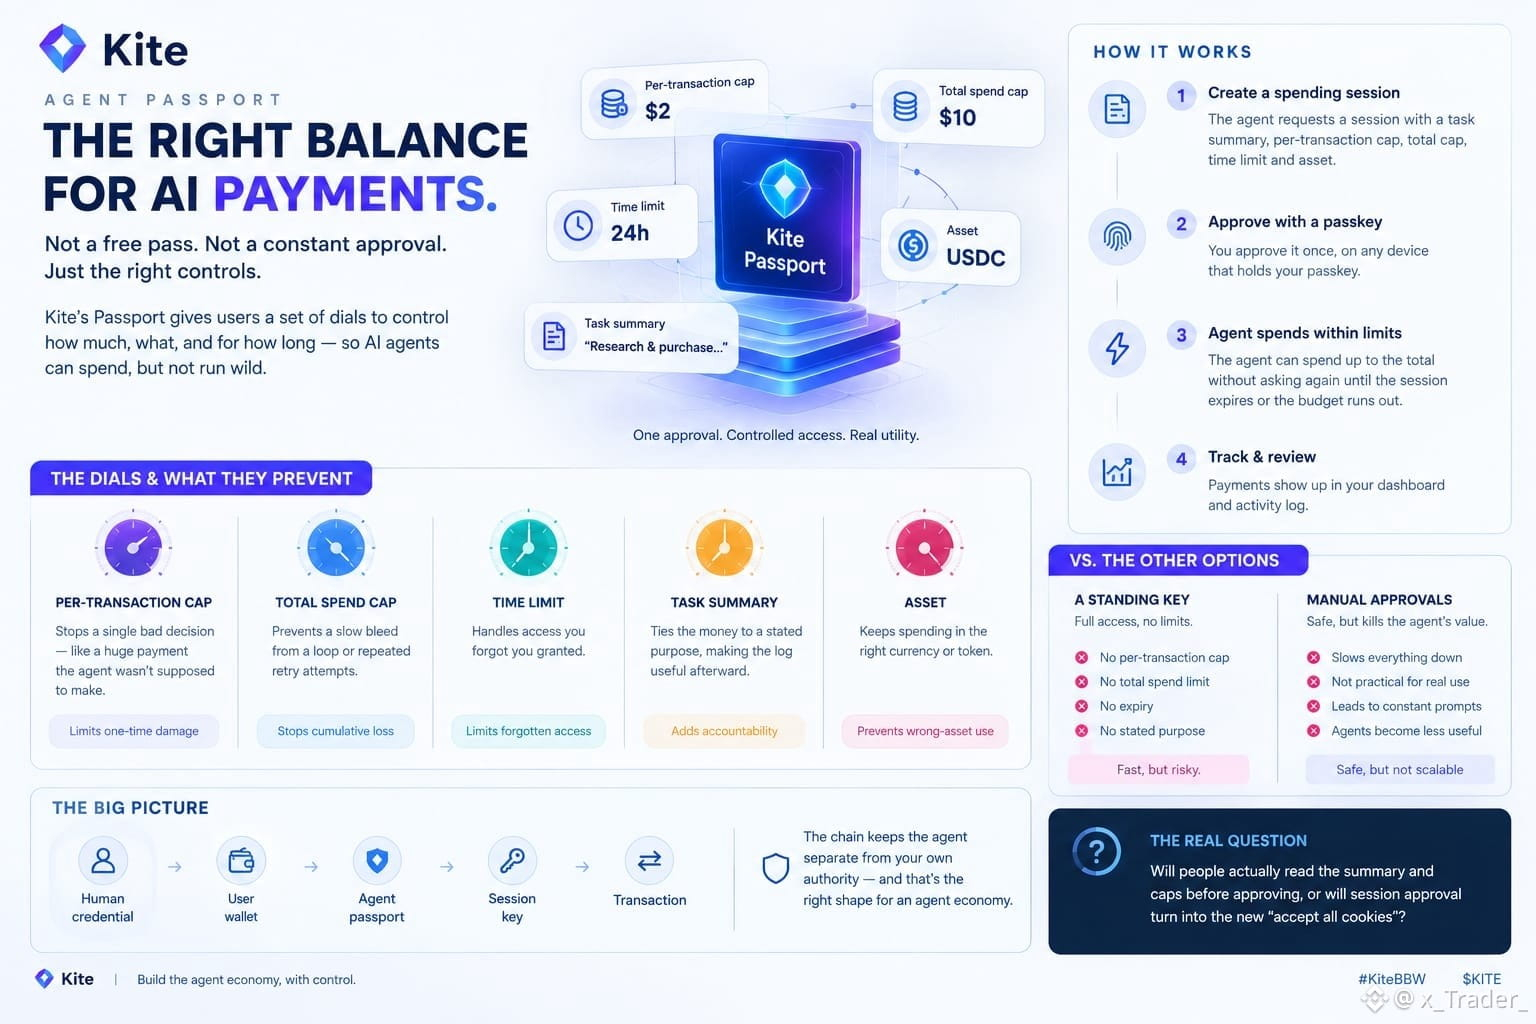
Kite's Passport sits in the gap between them, and what interests me is how many separate dials it gives the user.
Per the docs, an agent that wants to pay creates a spending session with a task summary, a cap per transaction, a cap on total spend, a time limit and an asset.
The user approves it once with a passkey, on any device that holds it.
After that the agent can spend up to the total without asking again until the session expires or the budget runs out.
The docs' own examples are small on purpose: $2 per transaction and $10 total over 24 hours, or $1 and $5 over two hours. The wallet is funded in advance, and payments show up in a dashboard and an activity log.
My read is that each dial covers a different failure. The per-transaction cap limits one bad decision, like an agent talked into a single huge payment. The total cap limits a slow bleed from a loop that keeps retrying.
The time limit handles access you forgot you GRANTED. The task summary ties the money to a stated purpose, which is what makes the log useful afterward.
A typical API key or saved card has few of these: no stated purpose, often no expiry, and no ceiling beyond the account balance.
A technical deep dive on Passport lays out the chain as human credential, user wallet, agent passport, session key, then the transaction, which keeps the agent a step removed from the user's own authority.
That's the right shape for an agent economy where software spends faster than people can review it.
The weak link is the human tap.
A session is only as safe as the person reading the summary and the caps before approving.
Will people actually read those fields, or will session approval turn into the new "accept all cookies" and quietly cancel out the safeguards built around it?
$KITE @GoKiteAI
{future}(KITEUSDT)
#KiteBBW $KITE
There are two lazy ways to let an AI agent spend money.
Give it a standing key and hope, or approve every payment by hand and stop using the agent for anything real.
Kite's Passport sits in the gap between them, and what interests me is how many separate dials it gives the user.
Per the docs, an agent that wants to pay creates a spending session with a task summary, a cap per transaction, a cap on total spend, a time limit and an asset.
The user approves it once with a passkey, on any device that holds it.
After that the agent can spend up to the total without asking again until the session expires or the budget runs out.
The docs' own examples are small on purpose: $2 per transaction and $10 total over 24 hours, or $1 and $5 over two hours. The wallet is funded in advance, and payments show up in a dashboard and an activity log.
My read is that each dial covers a different failure. The per-transaction cap limits one bad decision, like an agent talked into a single huge payment. The total cap limits a slow bleed from a loop that keeps retrying.
The time limit handles access you forgot you GRANTED. The task summary ties the money to a stated purpose, which is what makes the log useful afterward.
A typical API key or saved card has few of these: no stated purpose, often no expiry, and no ceiling beyond the account balance.
A technical deep dive on Passport lays out the chain as human credential, user wallet, agent passport, session key, then the transaction, which keeps the agent a step removed from the user's own authority.
That's the right shape for an agent economy where software spends faster than people can review it.
The weak link is the human tap.
A session is only as safe as the person reading the summary and the caps before approving.
Will people actually read those fields, or will session approval turn into the new "accept all cookies" and quietly cancel out the safeguards built around it?
$KITE @KITE AI 中文
There are two lazy ways to let an AI agent spend money.
Give it a standing key and hope, or approve every payment by hand and stop using the agent for anything real.
Kite's Passport sits in the gap between them, and what interests me is how many separate dials it gives the user.
Per the docs, an agent that wants to pay creates a spending session with a task summary, a cap per transaction, a cap on total spend, a time limit and an asset.
The user approves it once with a passkey, on any device that holds it.
After that the agent can spend up to the total without asking again until the session expires or the budget runs out.
The docs' own examples are small on purpose: $2 per transaction and $10 total over 24 hours, or $1 and $5 over two hours. The wallet is funded in advance, and payments show up in a dashboard and an activity log.
My read is that each dial covers a different failure. The per-transaction cap limits one bad decision, like an agent talked into a single huge payment. The total cap limits a slow bleed from a loop that keeps retrying.
The time limit handles access you forgot you GRANTED. The task summary ties the money to a stated purpose, which is what makes the log useful afterward.
A typical API key or saved card has few of these: no stated purpose, often no expiry, and no ceiling beyond the account balance.
A technical deep dive on Passport lays out the chain as human credential, user wallet, agent passport, session key, then the transaction, which keeps the agent a step removed from the user's own authority.
That's the right shape for an agent economy where software spends faster than people can review it.
The weak link is the human tap.
A session is only as safe as the person reading the summary and the caps before approving.
Will people actually read those fields, or will session approval turn into the new "accept all cookies" and quietly cancel out the safeguards built around it?
$KITE @KITE AI 中文
1
1
282
PINNED
·
--
Good Morning People 🌞 🧧🎉
Mission Based Reward Post.
1. Repost this post ✅
2. Comment 👉 " hi "
Good Morning People 🌞 🧧🎉
Mission Based Reward Post.
1. Repost this post ✅
2. Comment 👉 " hi "
Mission Based Reward Post.
1. Repost this post ✅
2. Comment 👉 " hi "
114
1
5
120
·
--
Crypto has a funny way of changing everyone’s mood overnight 😅
In July, Bitcoin touched a low of about $57,800 and everyone was scared. Then it climbed into the $80s and suddenly everyone felt like a genius. Now it’s back around $63,800.
The chart moved up and down. The mood moved much faster than the chart.
The biggest lesson I keep relearning is that how I feel about a price is usually the worst signal I have. It’s loudest right when I should be calmest.
So lately I’m trying to do less checking and more reading.
What’s one habit you’ve changed this year because of the market? 👇
#bitcoin #BinanceSquare #BinanceSquareTalks
Hoe is your $BTC hp?😅😂
{future}(BTCUSDT)
Crypto has a funny way of changing everyone’s mood overnight 😅
In July, Bitcoin touched a low of about $57,800 and everyone was scared. Then it climbed into the $80s and suddenly everyone felt like a genius. Now it’s back around $63,800.
The chart moved up and down. The mood moved much faster than the chart.
The biggest lesson I keep relearning is that how I feel about a price is usually the worst signal I have. It’s loudest right when I should be calmest.
So lately I’m trying to do less checking and more reading.
What’s one habit you’ve changed this year because of the market? 👇
#bitcoin #BinanceSquare #BinanceSquareTalks
Hoe is your $BTC hp?😅😂
In July, Bitcoin touched a low of about $57,800 and everyone was scared. Then it climbed into the $80s and suddenly everyone felt like a genius. Now it’s back around $63,800.
The chart moved up and down. The mood moved much faster than the chart.
The biggest lesson I keep relearning is that how I feel about a price is usually the worst signal I have. It’s loudest right when I should be calmest.
So lately I’m trying to do less checking and more reading.
What’s one habit you’ve changed this year because of the market? 👇
#bitcoin #BinanceSquare #BinanceSquareTalks
Hoe is your $BTC hp?😅😂
Made a fortune
55%
Critically hit
45%
11 votes • Voting closed
1.1k
·
--
go read
go read
Luke_龙
·
--
#sxt $SXT @SpaceandTime
A smart contract can’t see LAST MONTH. It knows the CURRENT block and whatever parameters you pass in.
Ask how much a wallet has traded in 30 days and it has two options: simplify the logic to what it can compute onchain, or trust an offchain answer nobody can check.
Space and Time adds a third. Step by step:
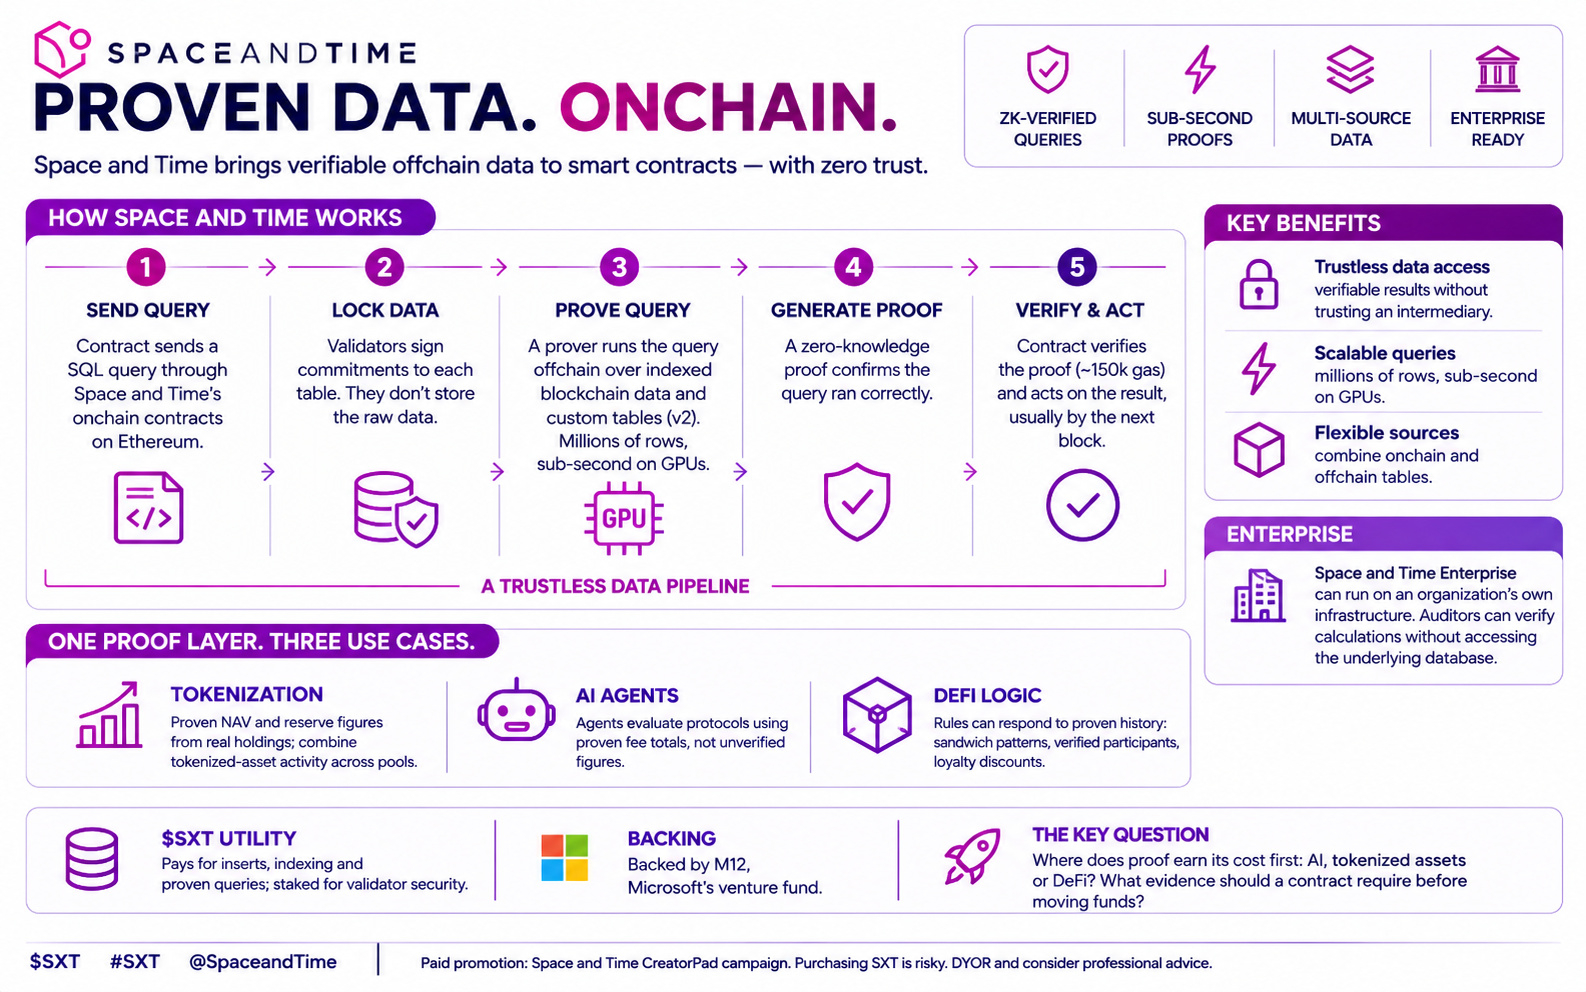
1. The contract sends a SQL query through Space and Time’s onchain contracts on Ethereum.
2. Validators have already signed commitments to each table, locking the data in. They don’t store the raw data.
3. A prover runs the query off-chain over indexed blockchain data, plus custom offchain tables supported since v2. Millions of rows, sub-second on GPUs.
4. It generates a ZK proof that the query ran correctly and calls the result back to the contract.
5. The contract verifies the proof for roughly 150k gas and acts on it, usually by the next block.
Once that loop exists, one primitive covers three jobs. Tokenization: NAV and reserve figures computed over real holdings with a proof attached, or a tokenized stock’s activity across several pools combined into one calculation.
AI: an agent evaluating a PROTOCOL on proven fee totals instead of unverified ones.
DeFi: hooks that raise fees when recent blocks show sandwich patterns, gate a pool to verified participants, or give loyalty discounts from proven history.
Enterprises can run Space and Time Enterprise on their own infrastructure, and auditors verify calculations without touching the underlying database.
SXT pays for inserts, indexing and proven queries, and is staked for validator security. Backed by M12, Microsoft’s venture fund.
Where does a proof earn its cost first: AI agents, tokenized assets, or DeFi logic? And what would a data layer have to show before you let a contract move funds on its output?
Paid promotion: Space and Time CreatorPad campaign.
Purchasing SXT is risky. You are encouraged to DYOR and to consult professional advice before buying SXT or any other cryptocurrency.
#Binance #BinanceSquareFamily
A smart contract can’t see LAST MONTH. It knows the CURRENT block and whatever parameters you pass in.
Ask how much a wallet has traded in 30 days and it has two options: simplify the logic to what it can compute onchain, or trust an offchain answer nobody can check.
Space and Time adds a third. Step by step:
1. The contract sends a SQL query through Space and Time’s onchain contracts on Ethereum.
2. Validators have already signed commitments to each table, locking the data in. They don’t store the raw data.
3. A prover runs the query off-chain over indexed blockchain data, plus custom offchain tables supported since v2. Millions of rows, sub-second on GPUs.
4. It generates a ZK proof that the query ran correctly and calls the result back to the contract.
5. The contract verifies the proof for roughly 150k gas and acts on it, usually by the next block.
Once that loop exists, one primitive covers three jobs. Tokenization: NAV and reserve figures computed over real holdings with a proof attached, or a tokenized stock’s activity across several pools combined into one calculation.
AI: an agent evaluating a PROTOCOL on proven fee totals instead of unverified ones.
DeFi: hooks that raise fees when recent blocks show sandwich patterns, gate a pool to verified participants, or give loyalty discounts from proven history.
Enterprises can run Space and Time Enterprise on their own infrastructure, and auditors verify calculations without touching the underlying database.
SXT pays for inserts, indexing and proven queries, and is staked for validator security. Backed by M12, Microsoft’s venture fund.
Where does a proof earn its cost first: AI agents, tokenized assets, or DeFi logic? And what would a data layer have to show before you let a contract move funds on its output?
Paid promotion: Space and Time CreatorPad campaign.
Purchasing SXT is risky. You are encouraged to DYOR and to consult professional advice before buying SXT or any other cryptocurrency.
#Binance #BinanceSquareFamily
51
·
--
Does anyone know when the next campaign will start?
Does anyone know when the next campaign will start?
119
·
--
$KITE new
{future}(KITEUSDT)
$KITE new
Luke_龙
·
--
#KiteBBW $KITE
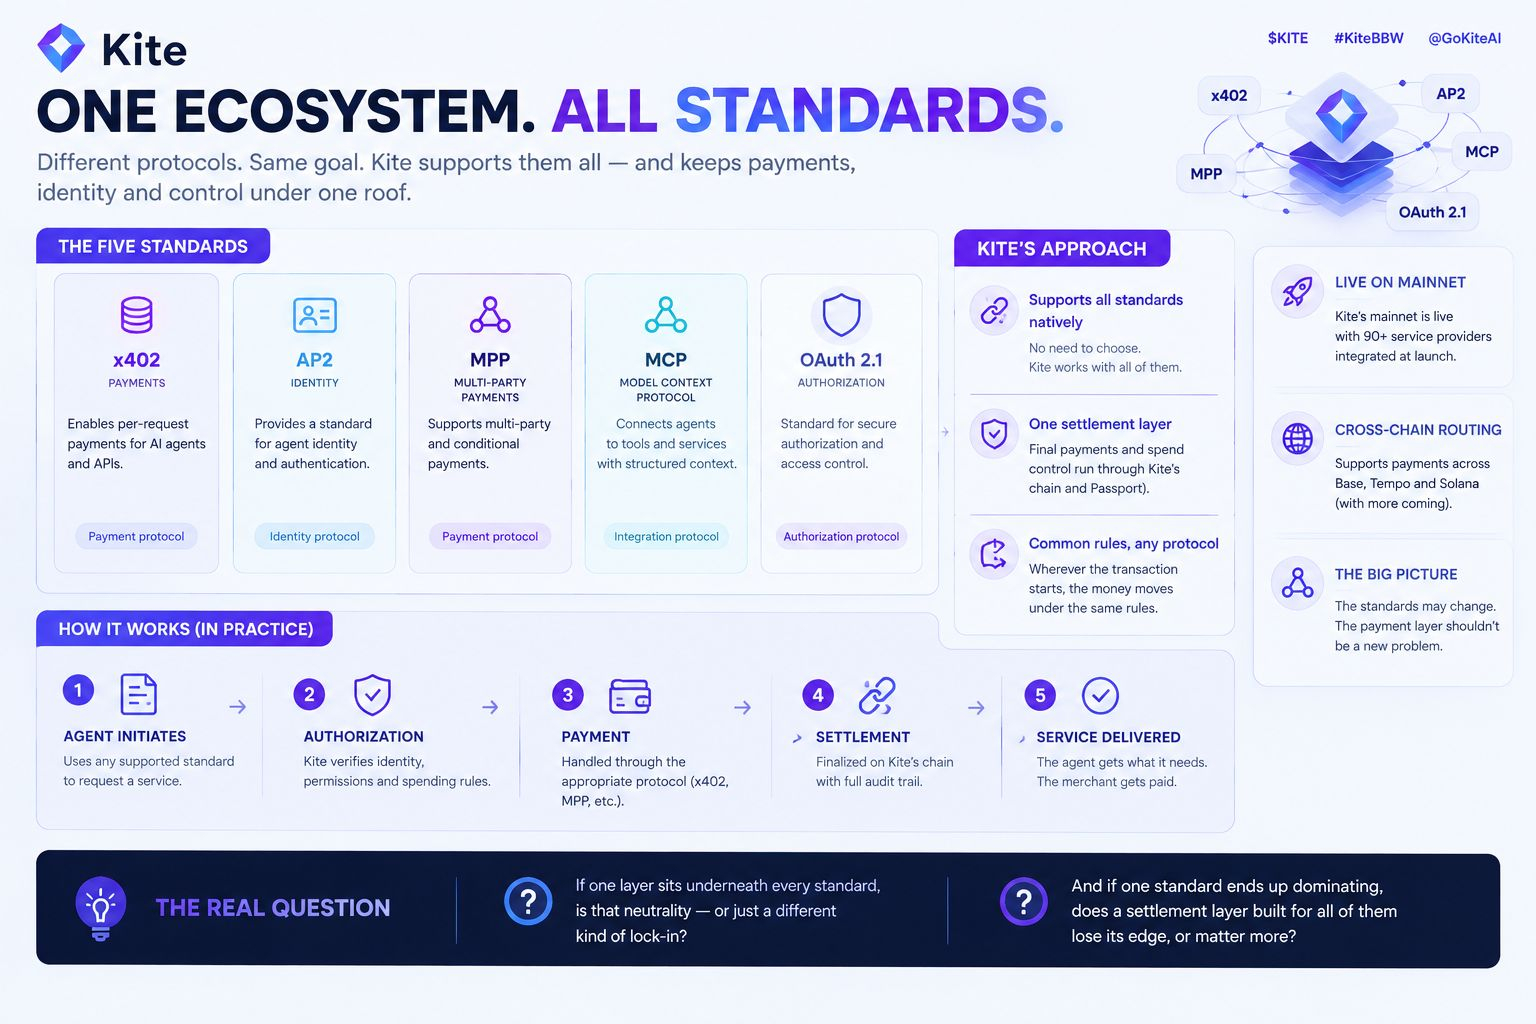
x402, AP2, MPP, MCP, OAuth 2.1.
Five protocols an agent might be asked to speak, and nobody knows which one wins.
Kite’s answer is to not pick.
Each covers a different piece. x402 revives HTTP “payment required” status so a service can charge per request.
AP2 is Google’s agent payments protocol, MPP is Stripe’s machine payment protocol, MCP is Anthropic’s way of connecting agents to tools, and OAuth 2.1 handles authorization
As one research report framed it, an agent using x402 can pay per request, still needs a separate wallet, a separate identity layer and its own spending-limit logic.
Kite’s stated approach is to support all of them natively and keep the part that matters, final settlement and spend control, anchored to its own chain and Passport.
Whatever protocol starts the transaction, the money is meant to move under the same rules the user set: a budget, a time limit, a passkey approval, instant revocation.
Kite also lists sub-second deterministic finality and dedicated agent payment lanes, which matter more for an agent than a person.
A human can wait for a confirmation.
An agent acting alone needs to know a payment is actually done.I like the logic because it sidesteps the standards fight.
It’s also a quiet bet on where value sits in the agent economy:
not in the request layer, which could change every year, but in the layer that decides whether a payment is allowed to clear.
Kite is also a member of the Linux Foundation’s Agentic AI Foundation, which suggests it wants a seat inside the standards conversation, not just underneath it.
Mainnet launched April 30, 2026 with 90+ service providers already integrated, so the real test is whether that neutrality and those payment lanes hold under real traffic
Would like other people’s takes
1. If one layer sits underneath every standard, is that neutrality or just a different kind of lock-in?
2. If one standard ends up dominating anyway, does a settlement layer built for all of them lose its edge, or matter more because everything runs through it?
x402, AP2, MPP, MCP, OAuth 2.1.
Five protocols an agent might be asked to speak, and nobody knows which one wins.
Kite’s answer is to not pick.
Each covers a different piece. x402 revives HTTP “payment required” status so a service can charge per request.
AP2 is Google’s agent payments protocol, MPP is Stripe’s machine payment protocol, MCP is Anthropic’s way of connecting agents to tools, and OAuth 2.1 handles authorization
As one research report framed it, an agent using x402 can pay per request, still needs a separate wallet, a separate identity layer and its own spending-limit logic.
Kite’s stated approach is to support all of them natively and keep the part that matters, final settlement and spend control, anchored to its own chain and Passport.
Whatever protocol starts the transaction, the money is meant to move under the same rules the user set: a budget, a time limit, a passkey approval, instant revocation.
Kite also lists sub-second deterministic finality and dedicated agent payment lanes, which matter more for an agent than a person.
A human can wait for a confirmation.
An agent acting alone needs to know a payment is actually done.I like the logic because it sidesteps the standards fight.
It’s also a quiet bet on where value sits in the agent economy:
not in the request layer, which could change every year, but in the layer that decides whether a payment is allowed to clear.
Kite is also a member of the Linux Foundation’s Agentic AI Foundation, which suggests it wants a seat inside the standards conversation, not just underneath it.
Mainnet launched April 30, 2026 with 90+ service providers already integrated, so the real test is whether that neutrality and those payment lanes hold under real traffic
Would like other people’s takes
1. If one layer sits underneath every standard, is that neutrality or just a different kind of lock-in?
2. If one standard ends up dominating anyway, does a settlement layer built for all of them lose its edge, or matter more because everything runs through it?
43
·
--
This week might be the most important week for crypto in 2026 and most people aren't ready 👀
Three things happening back to back —
The CLARITY Act hit the Senate floor September 15. First real vote on crypto regulation in US history. The Senate needs to clear a 60-vote threshold to move it forward for debate.
The Fed just raised rates 25 basis points — markets had assigned 85% probability to a rate hike amid persistent inflation. Higher rates = pressure on crypto.
And the Bank of Japan is meeting TODAY September 17. BOJ policy shifts move global liquidity and that moves crypto.
Meanwhile $BTC is sitting above $78K after recovering from $60K in August 😅
Three political, monetary and global events. Four days. One market.
Whatever happens this week — it sets the tone for the rest of 2026.
Are you positioned for it? 👇
$BTC
{future}(BTCUSDT)
This week might be the most important week for crypto in 2026 and most people aren't ready 👀
Three things happening back to back —
The CLARITY Act hit the Senate floor September 15. First real vote on crypto regulation in US history. The Senate needs to clear a 60-vote threshold to move it forward for debate.
The Fed just raised rates 25 basis points — markets had assigned 85% probability to a rate hike amid persistent inflation. Higher rates = pressure on crypto.
And the Bank of Japan is meeting TODAY September 17. BOJ policy shifts move global liquidity and that moves crypto.
Meanwhile $BTC is sitting above $78K after recovering from $60K in August 😅
Three political, monetary and global events. Four days. One market.
Whatever happens this week — it sets the tone for the rest of 2026.
Are you positioned for it? 👇
$BTC
Three things happening back to back —
The CLARITY Act hit the Senate floor September 15. First real vote on crypto regulation in US history. The Senate needs to clear a 60-vote threshold to move it forward for debate.
The Fed just raised rates 25 basis points — markets had assigned 85% probability to a rate hike amid persistent inflation. Higher rates = pressure on crypto.
And the Bank of Japan is meeting TODAY September 17. BOJ policy shifts move global liquidity and that moves crypto.
Meanwhile $BTC is sitting above $78K after recovering from $60K in August 😅
Three political, monetary and global events. Four days. One market.
Whatever happens this week — it sets the tone for the rest of 2026.
Are you positioned for it? 👇
$BTC
247
2
24
247
·
--
Verified
#dusk $DUSK @Dusk_Foundation
Read the implementation section of the whitepaper twice this week. First pass, I skimmed past the part about "host functions" assuming it was just a technical footnote about how the VM is built. Second pass, that assumption didn't survive.
I'd been treating "smart contracts run in a VM" and "cryptographic operations run in a VM" as the same claim. They're not, and the gap between them is actually the interesting design decision.
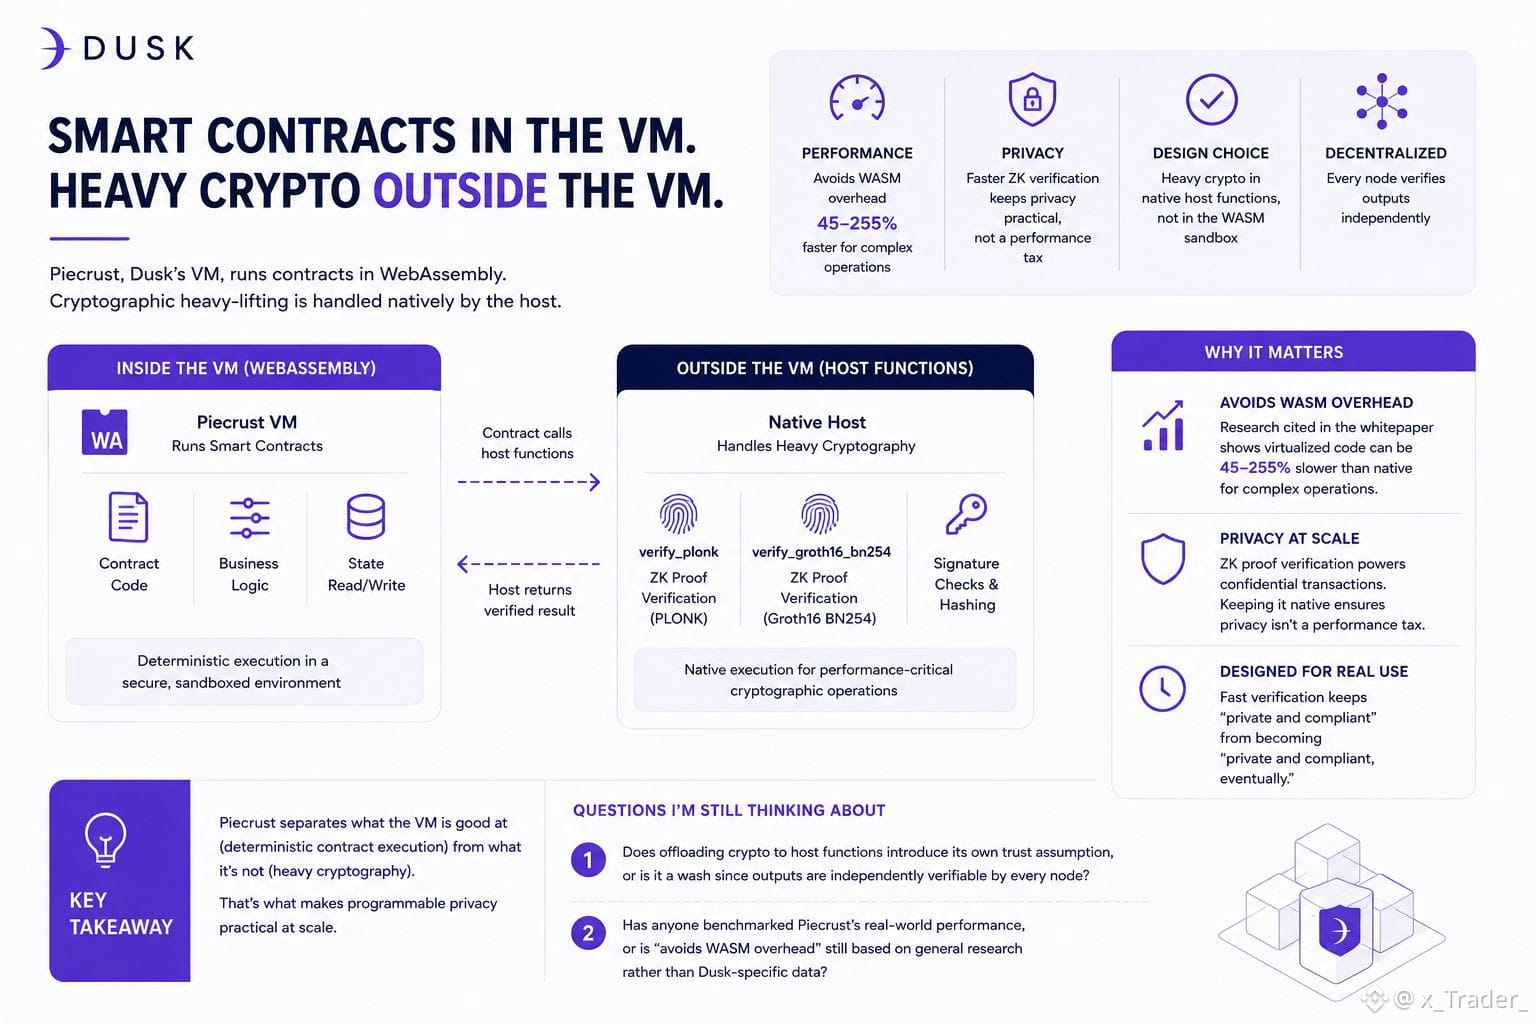
Piecrust, Dusk's VM, runs contracts in WebAssembly. But it doesn't run the actual cryptographic heavy-lifting — hashing, ZK proof verification, signature checks — inside that WASM sandbox. Those get pulled out and handled natively by the host instead, through exposed functions like verify_plonk and verify_groth16_bn254. The contract calls out to them, but the expensive math never touches the virtualized environment.
Here's why that's not a minor implementation detail. WASM execution research the whitepaper cites shows virtualized code can run 45-255% slower than native code for complex operations — the overhead is baked into how sandboxed memory and instructions work, not something you optimize away.
So confidential transactions, which lean on ZK proof verification for basically everything, would be paying that tax on every single one if verification ran inside the VM like a normal contract call.
That's what connects back to the privacy design. Programmable privacy isn't just a cryptography choice, it's also a performance constraint — if proof verification is slow, "private and compliant" quietly becomes "private and compliant, eventually." Pulling crypto out to host functions is what keeps privacy from being a tax on top of every transaction instead of a property of it.
Has anyone actually benchmarked Piecrust's real-world numbers here, or is "avoids WASM overhead" still resting on the general research cited rather than Dusk-specific data?"
#dusk $DUSK @Dusk
Read the implementation section of the whitepaper twice this week. First pass, I skimmed past the part about "host functions" assuming it was just a technical footnote about how the VM is built. Second pass, that assumption didn't survive.
I'd been treating "smart contracts run in a VM" and "cryptographic operations run in a VM" as the same claim. They're not, and the gap between them is actually the interesting design decision.
Piecrust, Dusk's VM, runs contracts in WebAssembly. But it doesn't run the actual cryptographic heavy-lifting — hashing, ZK proof verification, signature checks — inside that WASM sandbox. Those get pulled out and handled natively by the host instead, through exposed functions like verify_plonk and verify_groth16_bn254. The contract calls out to them, but the expensive math never touches the virtualized environment.
Here's why that's not a minor implementation detail. WASM execution research the whitepaper cites shows virtualized code can run 45-255% slower than native code for complex operations — the overhead is baked into how sandboxed memory and instructions work, not something you optimize away.
So confidential transactions, which lean on ZK proof verification for basically everything, would be paying that tax on every single one if verification ran inside the VM like a normal contract call.
That's what connects back to the privacy design. Programmable privacy isn't just a cryptography choice, it's also a performance constraint — if proof verification is slow, "private and compliant" quietly becomes "private and compliant, eventually." Pulling crypto out to host functions is what keeps privacy from being a tax on top of every transaction instead of a property of it.
Has anyone actually benchmarked Piecrust's real-world numbers here, or is "avoids WASM overhead" still resting on the general research cited rather than Dusk-specific data?"
Read the implementation section of the whitepaper twice this week. First pass, I skimmed past the part about "host functions" assuming it was just a technical footnote about how the VM is built. Second pass, that assumption didn't survive.
I'd been treating "smart contracts run in a VM" and "cryptographic operations run in a VM" as the same claim. They're not, and the gap between them is actually the interesting design decision.
Piecrust, Dusk's VM, runs contracts in WebAssembly. But it doesn't run the actual cryptographic heavy-lifting — hashing, ZK proof verification, signature checks — inside that WASM sandbox. Those get pulled out and handled natively by the host instead, through exposed functions like verify_plonk and verify_groth16_bn254. The contract calls out to them, but the expensive math never touches the virtualized environment.
Here's why that's not a minor implementation detail. WASM execution research the whitepaper cites shows virtualized code can run 45-255% slower than native code for complex operations — the overhead is baked into how sandboxed memory and instructions work, not something you optimize away.
So confidential transactions, which lean on ZK proof verification for basically everything, would be paying that tax on every single one if verification ran inside the VM like a normal contract call.
That's what connects back to the privacy design. Programmable privacy isn't just a cryptography choice, it's also a performance constraint — if proof verification is slow, "private and compliant" quietly becomes "private and compliant, eventually." Pulling crypto out to host functions is what keeps privacy from being a tax on top of every transaction instead of a property of it.
Has anyone actually benchmarked Piecrust's real-world numbers here, or is "avoids WASM overhead" still resting on the general research cited rather than Dusk-specific data?"
5
5
544
·
--
Verified
#dusk
Assumed DuskEVM's rollup design was basically a technical detail — sequencer, batcher, base layer, whatever. Then I actually compared its dispute model to how Arbitrum and Optimism handle theirs, and the assumption fell apart.
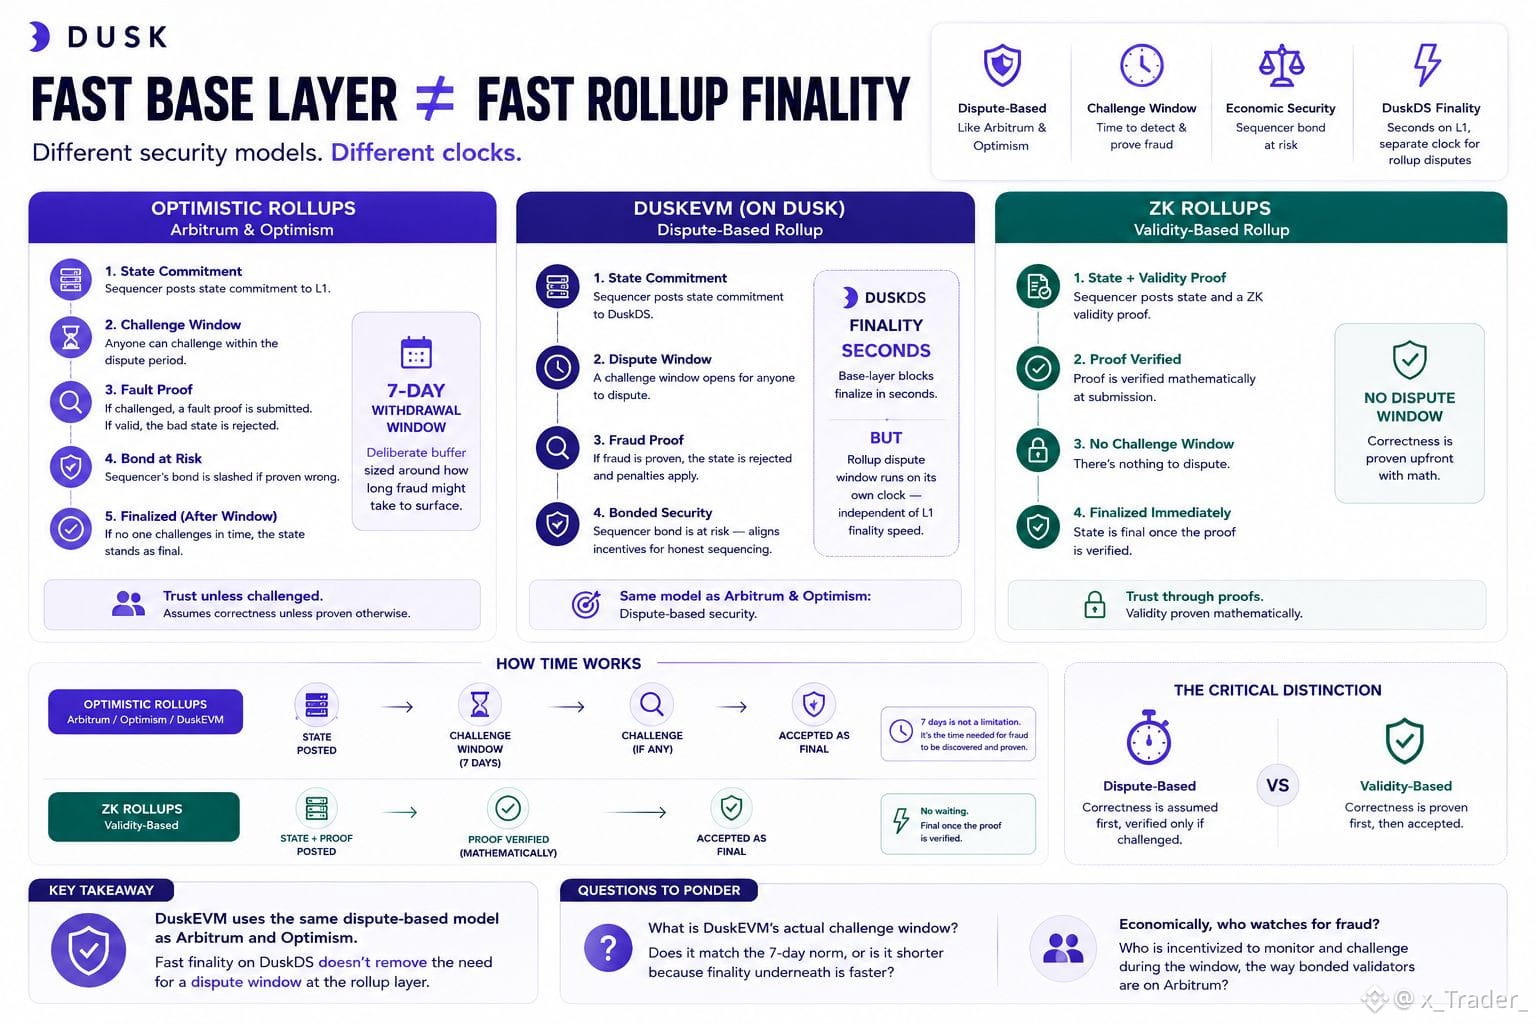
Optimistic rollups don't verify by default. They verify on challenge. A sequencer posts a state commitment. Anyone can submit a fault proof against it. If the proof holds, the bad state gets rejected and the sequencer's bond gets slashed. If nobody challenges it in time, it stands as final, whether or not it was actually correct.
Here's what I hadn't connected until I put the numbers side by side. Arbitrum and Optimism both impose a 7-day withdrawal window — not a limitation, a deliberate buffer sized around how long fraud might take to surface. Zk-rollups skip that entirely: a validity proof gets checked mathematically at submission, so there's nothing left to dispute.
DuskDS finalizes base-layer blocks in seconds. I assumed that speed carries up to the rollup layer automatically. It doesn't. A dispute window runs on its own clock, independent of how fast the layer underneath it settles.
So the real comparison isn't "DuskEVM vs. Ethereum's rollups." It's "dispute-based security vs. math-based security," and DuskEVM picked the same side Arbitrum and Optimism did.
$DUSK
@Dusk_Foundation
What's DuskEVM's actual challenge window — does it match the 7-day norm, or is it shorter because finality underneath is faster?
#dusk
Assumed DuskEVM's rollup design was basically a technical detail — sequencer, batcher, base layer, whatever. Then I actually compared its dispute model to how Arbitrum and Optimism handle theirs, and the assumption fell apart.
Optimistic rollups don't verify by default. They verify on challenge. A sequencer posts a state commitment. Anyone can submit a fault proof against it. If the proof holds, the bad state gets rejected and the sequencer's bond gets slashed. If nobody challenges it in time, it stands as final, whether or not it was actually correct.
Here's what I hadn't connected until I put the numbers side by side. Arbitrum and Optimism both impose a 7-day withdrawal window — not a limitation, a deliberate buffer sized around how long fraud might take to surface. Zk-rollups skip that entirely: a validity proof gets checked mathematically at submission, so there's nothing left to dispute.
DuskDS finalizes base-layer blocks in seconds. I assumed that speed carries up to the rollup layer automatically. It doesn't. A dispute window runs on its own clock, independent of how fast the layer underneath it settles.
So the real comparison isn't "DuskEVM vs. Ethereum's rollups." It's "dispute-based security vs. math-based security," and DuskEVM picked the same side Arbitrum and Optimism did.
$DUSK
@Dusk
What's DuskEVM's actual challenge window — does it match the 7-day norm, or is it shorter because finality underneath is faster?
Assumed DuskEVM's rollup design was basically a technical detail — sequencer, batcher, base layer, whatever. Then I actually compared its dispute model to how Arbitrum and Optimism handle theirs, and the assumption fell apart.
Optimistic rollups don't verify by default. They verify on challenge. A sequencer posts a state commitment. Anyone can submit a fault proof against it. If the proof holds, the bad state gets rejected and the sequencer's bond gets slashed. If nobody challenges it in time, it stands as final, whether or not it was actually correct.
Here's what I hadn't connected until I put the numbers side by side. Arbitrum and Optimism both impose a 7-day withdrawal window — not a limitation, a deliberate buffer sized around how long fraud might take to surface. Zk-rollups skip that entirely: a validity proof gets checked mathematically at submission, so there's nothing left to dispute.
DuskDS finalizes base-layer blocks in seconds. I assumed that speed carries up to the rollup layer automatically. It doesn't. A dispute window runs on its own clock, independent of how fast the layer underneath it settles.
So the real comparison isn't "DuskEVM vs. Ethereum's rollups." It's "dispute-based security vs. math-based security," and DuskEVM picked the same side Arbitrum and Optimism did.
$DUSK
@Dusk
What's DuskEVM's actual challenge window — does it match the 7-day norm, or is it shorter because finality underneath is faster?
1
3
314
·
--
Verified
#dusk $DUSK
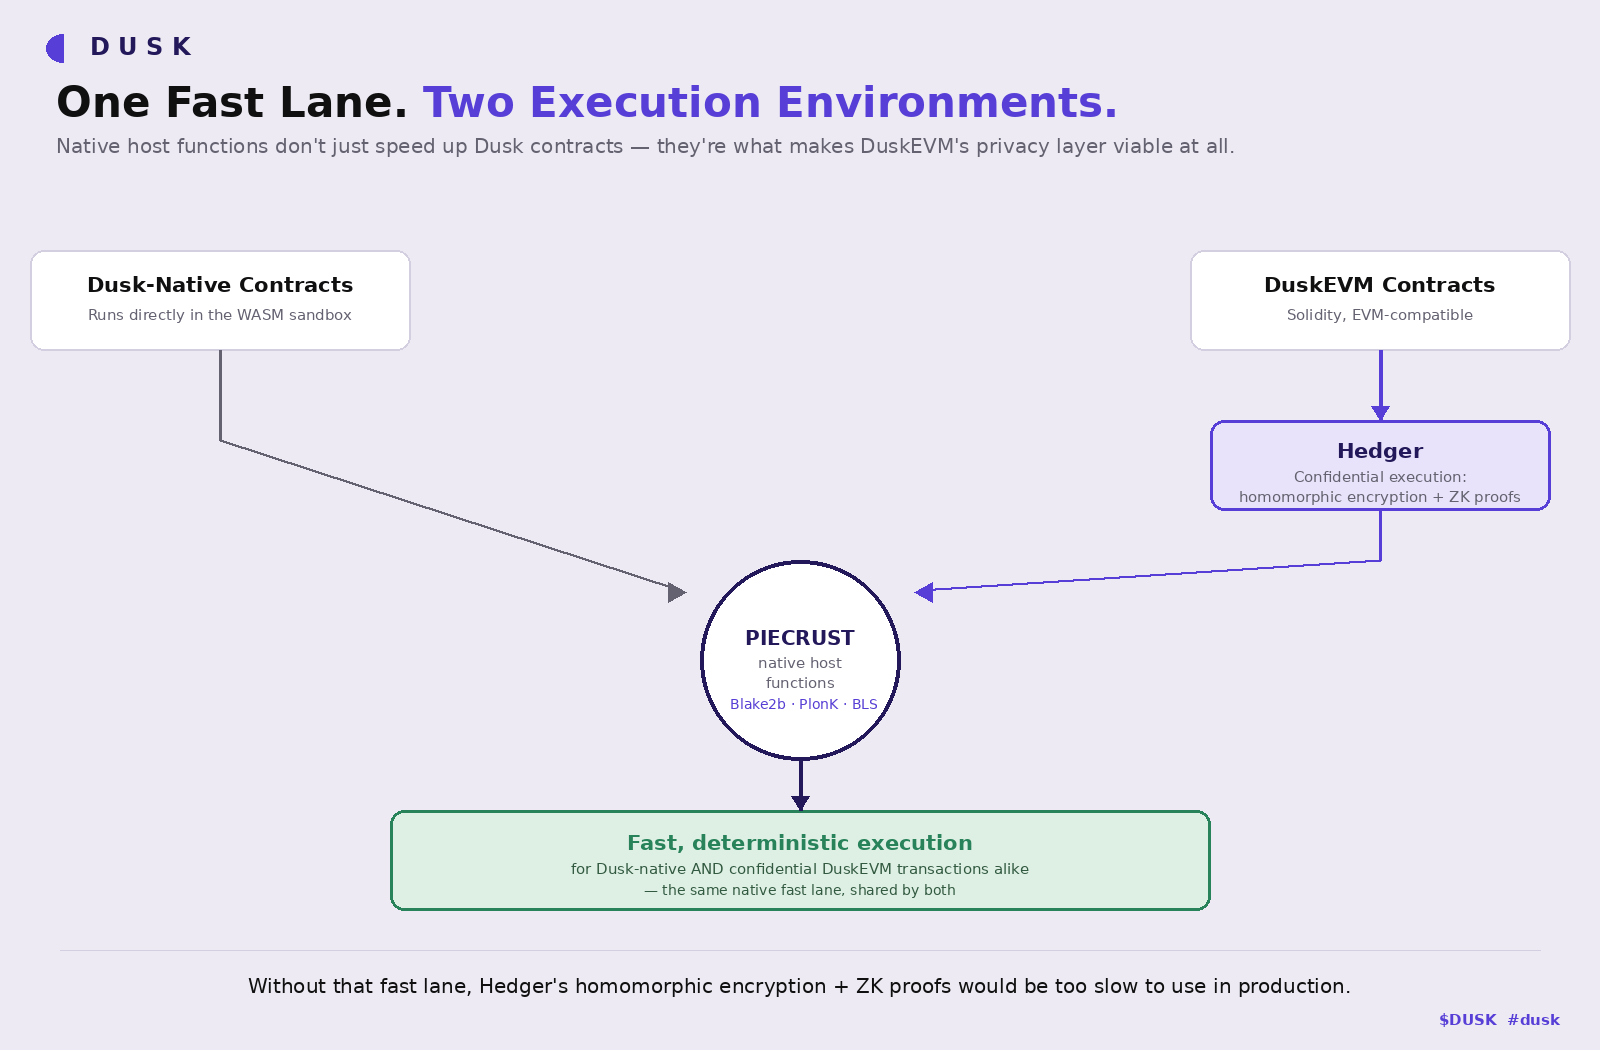
I thought Piecrust, Dusk's virtual machine, was just there to run smart contracts. Same job any VM does — execute code, keep state, done. Turns out that's maybe half of what it's actually for.
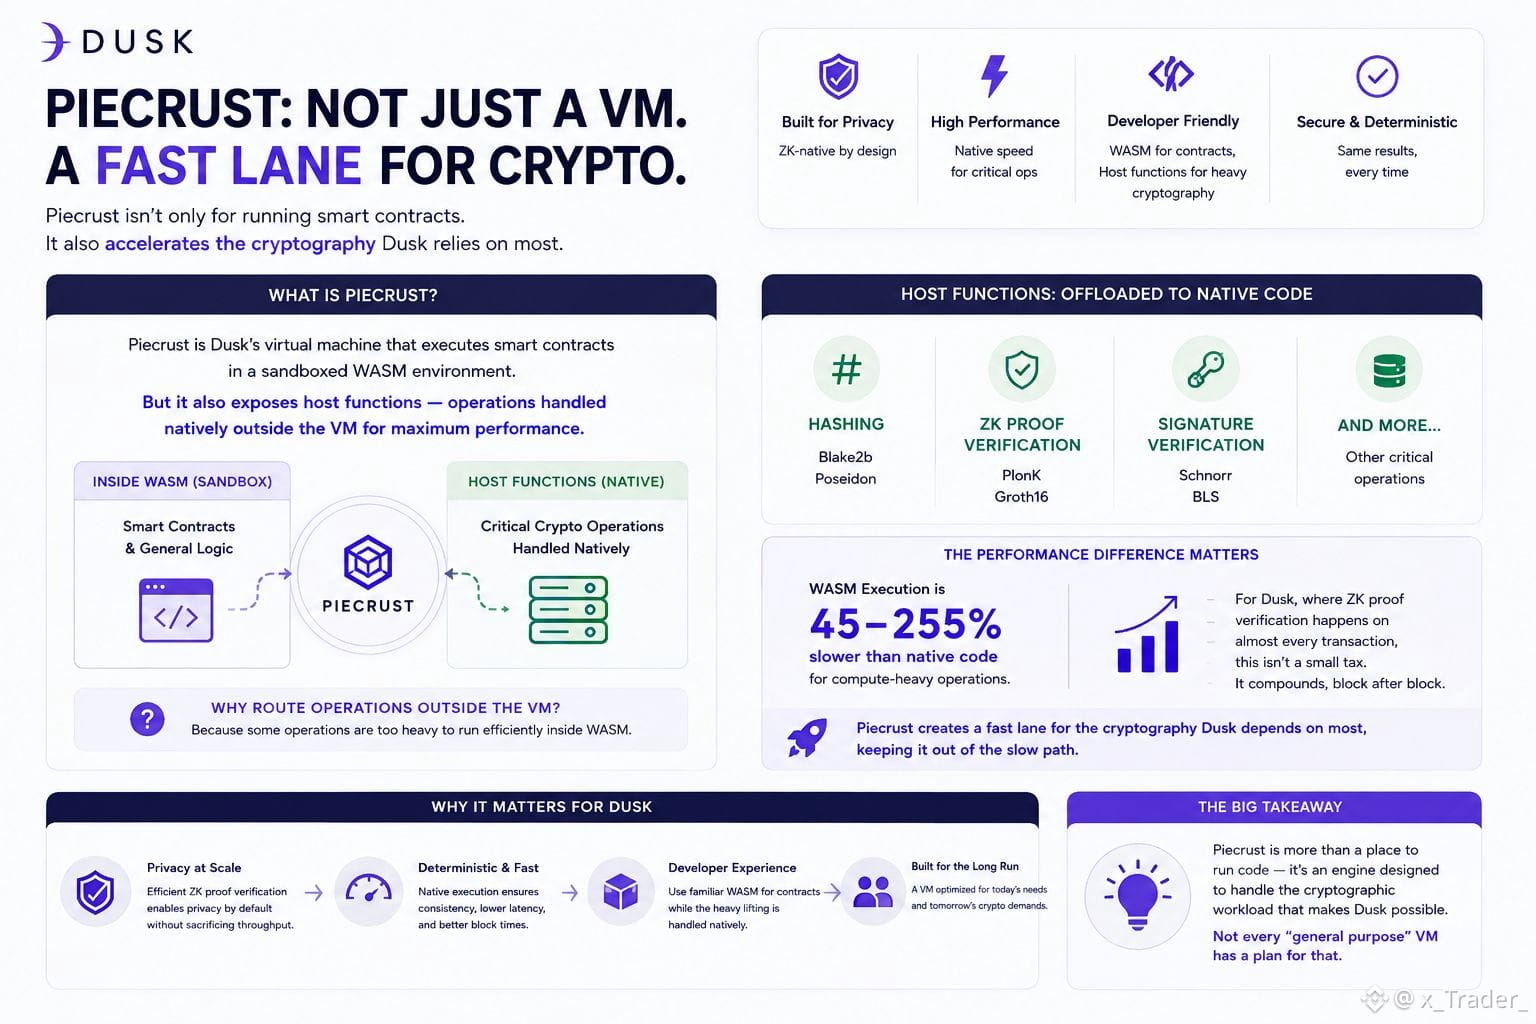
Digging into the docs, Piecrust exposes a set of host functions.
operations the VM hands off to native code instead of running inside the sandboxed WASM environment.
Hashing, through Blake2b and Poseidon.
Verifying PlonK and Groth16 zero-knowledge proofs.
Validating Schnorr and BLS signatures.
None of that runs as regular contract bytecode.
Why would a VM go out of its way to route specific operations around itself instead of just running everything the normal way?
Turns out WASM execution can be 45-255% slower than native code for compute-heavy operations, the overhead comes from virtualized memory management and the extra instruction handling a sandboxed environment adds.
For a chain where ZK proof verification isn't occasional but happens on basically every transaction, running that math inside WASM instead of natively isn't a small tax.
It compounds, block after block.
This same principle carries straight into DuskEVM, the EVM-compatible layer bringing Solidity developers onto Dusk.
Hedger, its confidential execution module, leans on homomorphic encryption plus ZK proofs to keep transactions private; none of which is fast enough to matter without the native host functions underneath doing the heavy lifting first.
So Piecrust isn't just where contracts execute. It's also a fast lane for the exact cryptographic operations @Dusk_Foundation depends on most, deliberately kept out of the slow path, and the same fast lane is what makes DuskEVM's privacy layer viable at all, not just Dusk-native contracts.
Makes me wonder — how many other "general purpose" VMs are quietly eating a proof-verification tax nobody's bothered to measure?
#dusk $DUSK
I thought Piecrust, Dusk's virtual machine, was just there to run smart contracts. Same job any VM does — execute code, keep state, done. Turns out that's maybe half of what it's actually for.
Digging into the docs, Piecrust exposes a set of host functions.
operations the VM hands off to native code instead of running inside the sandboxed WASM environment.
Hashing, through Blake2b and Poseidon.
Verifying PlonK and Groth16 zero-knowledge proofs.
Validating Schnorr and BLS signatures.
None of that runs as regular contract bytecode.
Why would a VM go out of its way to route specific operations around itself instead of just running everything the normal way?
Turns out WASM execution can be 45-255% slower than native code for compute-heavy operations, the overhead comes from virtualized memory management and the extra instruction handling a sandboxed environment adds.
For a chain where ZK proof verification isn't occasional but happens on basically every transaction, running that math inside WASM instead of natively isn't a small tax.
It compounds, block after block.
This same principle carries straight into DuskEVM, the EVM-compatible layer bringing Solidity developers onto Dusk.
Hedger, its confidential execution module, leans on homomorphic encryption plus ZK proofs to keep transactions private; none of which is fast enough to matter without the native host functions underneath doing the heavy lifting first.
So Piecrust isn't just where contracts execute. It's also a fast lane for the exact cryptographic operations @Dusk depends on most, deliberately kept out of the slow path, and the same fast lane is what makes DuskEVM's privacy layer viable at all, not just Dusk-native contracts.
Makes me wonder — how many other "general purpose" VMs are quietly eating a proof-verification tax nobody's bothered to measure?
I thought Piecrust, Dusk's virtual machine, was just there to run smart contracts. Same job any VM does — execute code, keep state, done. Turns out that's maybe half of what it's actually for.
Digging into the docs, Piecrust exposes a set of host functions.
operations the VM hands off to native code instead of running inside the sandboxed WASM environment.
Hashing, through Blake2b and Poseidon.
Verifying PlonK and Groth16 zero-knowledge proofs.
Validating Schnorr and BLS signatures.
None of that runs as regular contract bytecode.
Why would a VM go out of its way to route specific operations around itself instead of just running everything the normal way?
Turns out WASM execution can be 45-255% slower than native code for compute-heavy operations, the overhead comes from virtualized memory management and the extra instruction handling a sandboxed environment adds.
For a chain where ZK proof verification isn't occasional but happens on basically every transaction, running that math inside WASM instead of natively isn't a small tax.
It compounds, block after block.
This same principle carries straight into DuskEVM, the EVM-compatible layer bringing Solidity developers onto Dusk.
Hedger, its confidential execution module, leans on homomorphic encryption plus ZK proofs to keep transactions private; none of which is fast enough to matter without the native host functions underneath doing the heavy lifting first.
So Piecrust isn't just where contracts execute. It's also a fast lane for the exact cryptographic operations @Dusk depends on most, deliberately kept out of the slow path, and the same fast lane is what makes DuskEVM's privacy layer viable at all, not just Dusk-native contracts.
Makes me wonder — how many other "general purpose" VMs are quietly eating a proof-verification tax nobody's bothered to measure?
13
9
667
·
--
#dusk $DUSK @Dusk_Foundation
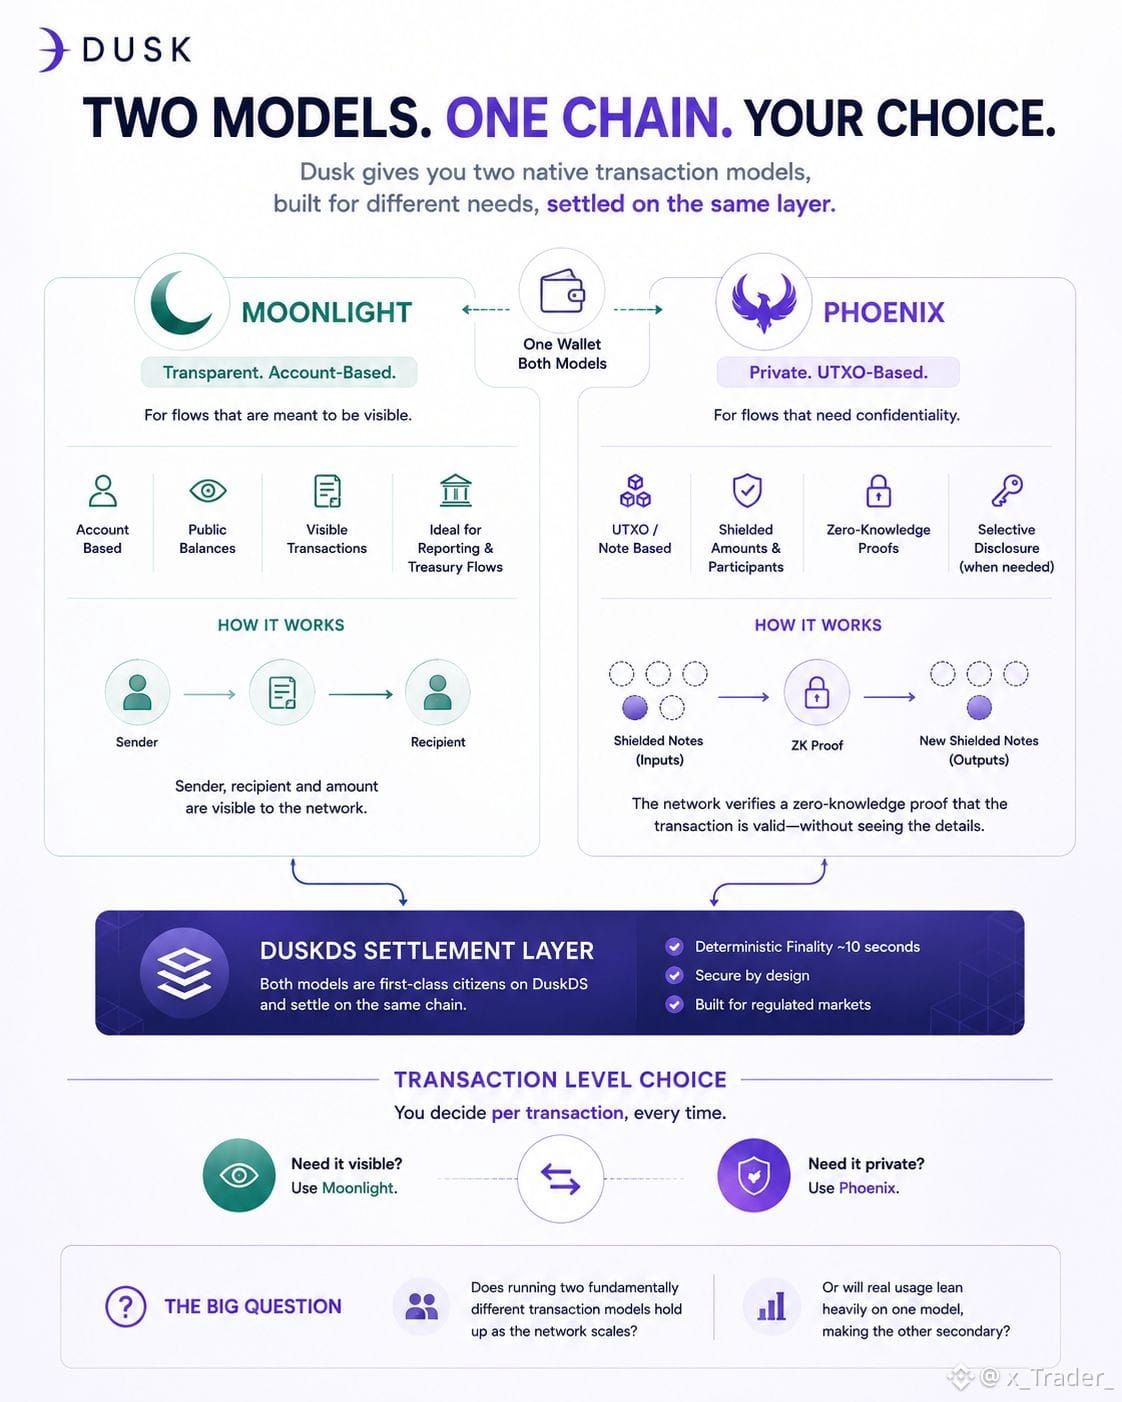
Dusk has two transaction models, and I kept treating them like one privacy system with two names.
Went back through the docs because that didn't quite make sense. Turns out they're solving two different problems.
MOONLIGHT is the transparent one: account-based, visible balances, sender, recipient and amount. Useful when a flow is supposed to be observable.
PHOENIX works completely differently. It's UTXO-based, so funds exist as shielded notes rather than a visible running balance. Instead of revealing the transaction details, the network verifies a zero-knowledge proof that the spend is valid, including that the funds exist and aren't being spent twice.
The part I found more interesting:
Neither is a fallback for the other.
They're both native transaction models on DuskDS and settle on the same chain. A wallet profile can manage a Moonlight account and a Phoenix account side by side.
So privacy isn't a setting you turn on once.
It's a transaction-level choice.
Want the transfer visible? Moonlight.
Need the amount and participants shielded? Phoenix.
And if an authorized party needs evidence later, Dusk supports selective disclosure through viewing keys.
That's a pretty different design choice from taking one transaction model and bolting a privacy layer onto it.
But it leaves me with the question I'm actually curious about:
Does maintaining two fundamentally different transaction models become a strength as Dusk scales, or a long-term engineering headache?
And in real usage, do regulated markets genuinely need both — or will one end up doing most of the work?
#dusk $DUSK @Dusk
Dusk has two transaction models, and I kept treating them like one privacy system with two names.
Went back through the docs because that didn't quite make sense. Turns out they're solving two different problems.
MOONLIGHT is the transparent one: account-based, visible balances, sender, recipient and amount. Useful when a flow is supposed to be observable.
PHOENIX works completely differently. It's UTXO-based, so funds exist as shielded notes rather than a visible running balance. Instead of revealing the transaction details, the network verifies a zero-knowledge proof that the spend is valid, including that the funds exist and aren't being spent twice.
The part I found more interesting:
Neither is a fallback for the other.
They're both native transaction models on DuskDS and settle on the same chain. A wallet profile can manage a Moonlight account and a Phoenix account side by side.
So privacy isn't a setting you turn on once.
It's a transaction-level choice.
Want the transfer visible? Moonlight.
Need the amount and participants shielded? Phoenix.
And if an authorized party needs evidence later, Dusk supports selective disclosure through viewing keys.
That's a pretty different design choice from taking one transaction model and bolting a privacy layer onto it.
But it leaves me with the question I'm actually curious about:
Does maintaining two fundamentally different transaction models become a strength as Dusk scales, or a long-term engineering headache?
And in real usage, do regulated markets genuinely need both — or will one end up doing most of the work?
Dusk has two transaction models, and I kept treating them like one privacy system with two names.
Went back through the docs because that didn't quite make sense. Turns out they're solving two different problems.
MOONLIGHT is the transparent one: account-based, visible balances, sender, recipient and amount. Useful when a flow is supposed to be observable.
PHOENIX works completely differently. It's UTXO-based, so funds exist as shielded notes rather than a visible running balance. Instead of revealing the transaction details, the network verifies a zero-knowledge proof that the spend is valid, including that the funds exist and aren't being spent twice.
The part I found more interesting:
Neither is a fallback for the other.
They're both native transaction models on DuskDS and settle on the same chain. A wallet profile can manage a Moonlight account and a Phoenix account side by side.
So privacy isn't a setting you turn on once.
It's a transaction-level choice.
Want the transfer visible? Moonlight.
Need the amount and participants shielded? Phoenix.
And if an authorized party needs evidence later, Dusk supports selective disclosure through viewing keys.
That's a pretty different design choice from taking one transaction model and bolting a privacy layer onto it.
But it leaves me with the question I'm actually curious about:
Does maintaining two fundamentally different transaction models become a strength as Dusk scales, or a long-term engineering headache?
And in real usage, do regulated markets genuinely need both — or will one end up doing most of the work?
11
10
624
·
--
#dusk $DUSK @Dusk_Foundation
Read the consensus section of the whitepaper twice this week, back to back. But didn't anything new the first time.
Second pass, one thing I'd been getting wrong finally clicked.
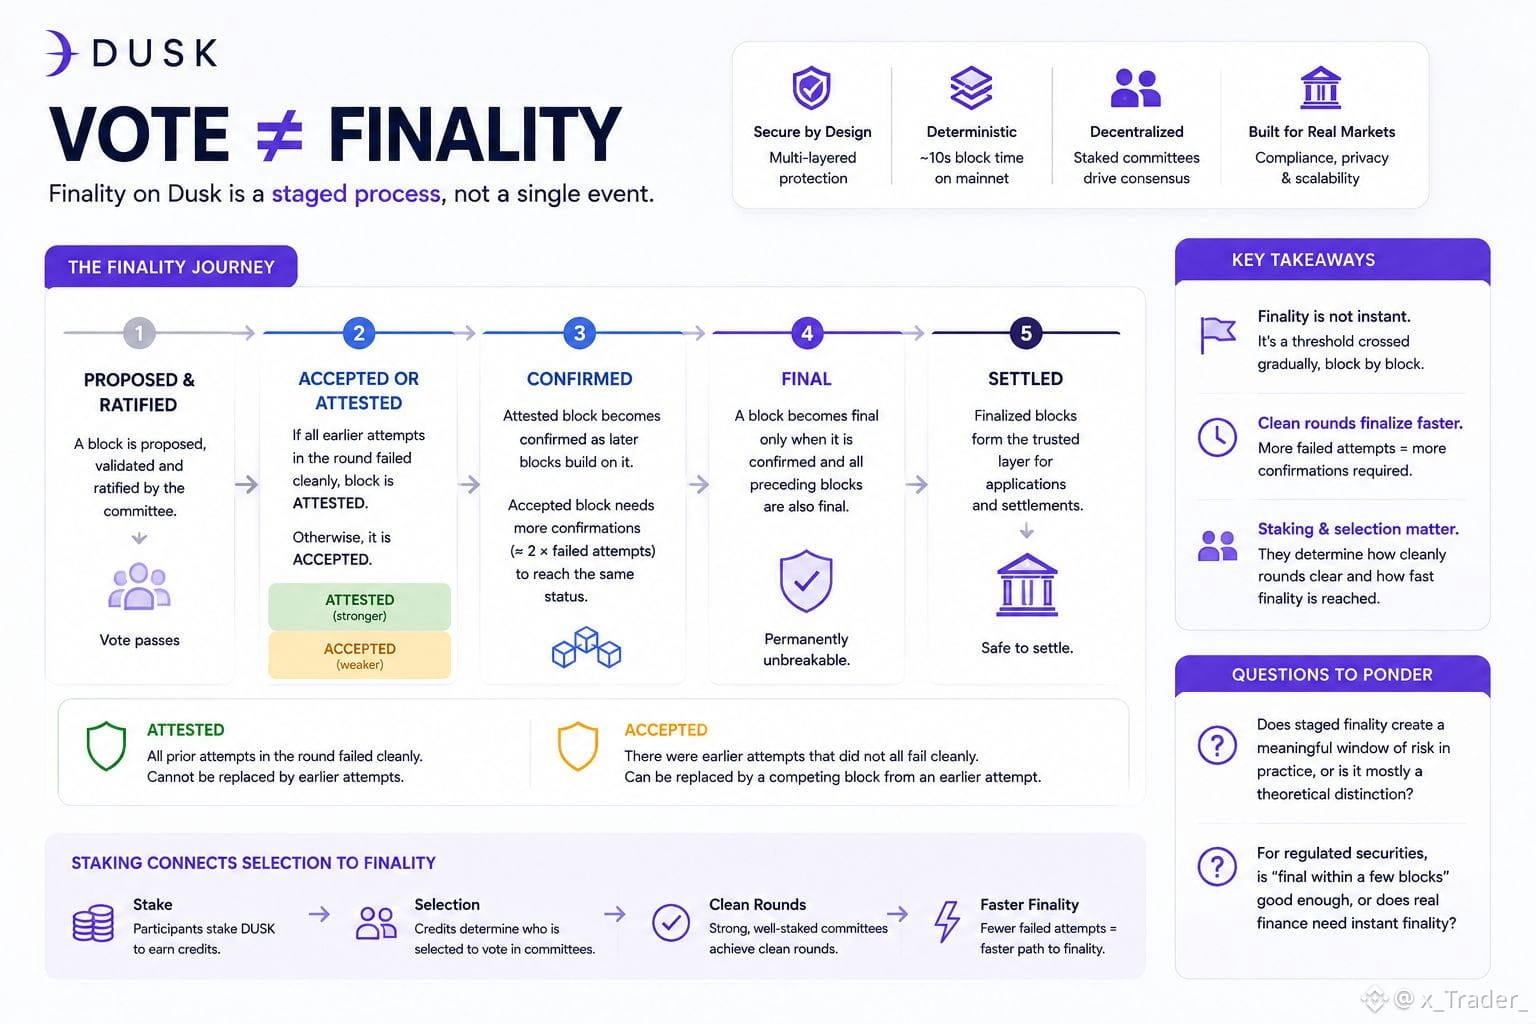
I'd been treating “a block got voted through” and “a block IS final” as basically the same event. They're not. There's a gap between them, and that's where the interesting security thinking lives.
A block that clears validation and ratification becomes ATTESTED only if every earlier attempt at that round failed cleanly. Otherwise it's “accepted”, which is weaker. An accepted block can still, in theory, be replaced by a competing block from an earlier attempt. An attested one can't.
Then finality builds in stages.
An attested block becomes confirmed as later blocks build on it. An accepted block needs more confirmations to reach the same status, roughly twice the number of failed attempts behind it.
Only when a block is confirmed, and everything before it is also final, does it actually become final.
So “final” isn't one event that happens when a vote passes. It's a threshold crossed block by block, and how quickly you reach it depends partly on how clean the round was.
This is where staking loops back in.
Who gets selected to vote, and who has enough credits in a committee to influence a quorum, affects how cleanly rounds clear. A messy round doesn't just slow things down in some vague way. It pushes the finality timeline out in a literal, countable way.
Selection and finality aren't two unrelated mechanisms sitting next to each other in the whitepaper. One decides who votes. The other decides when their vote becomes unbreakable.
That's the part I find interesting.
And I've got two questions I'm genuinely curious about:
Does this staged finality create a meaningful window of risk in practice, or is it mostly a theoretical distinction?
And for regulated securities, is “final within a few blocks” actually good enough, or does real finance eventually demand something closer to instant finality?
#dusk $DUSK @Dusk
Read the consensus section of the whitepaper twice this week, back to back. But didn't anything new the first time.
Second pass, one thing I'd been getting wrong finally clicked.
I'd been treating “a block got voted through” and “a block IS final” as basically the same event. They're not. There's a gap between them, and that's where the interesting security thinking lives.
A block that clears validation and ratification becomes ATTESTED only if every earlier attempt at that round failed cleanly. Otherwise it's “accepted”, which is weaker. An accepted block can still, in theory, be replaced by a competing block from an earlier attempt. An attested one can't.
Then finality builds in stages.
An attested block becomes confirmed as later blocks build on it. An accepted block needs more confirmations to reach the same status, roughly twice the number of failed attempts behind it.
Only when a block is confirmed, and everything before it is also final, does it actually become final.
So “final” isn't one event that happens when a vote passes. It's a threshold crossed block by block, and how quickly you reach it depends partly on how clean the round was.
This is where staking loops back in.
Who gets selected to vote, and who has enough credits in a committee to influence a quorum, affects how cleanly rounds clear. A messy round doesn't just slow things down in some vague way. It pushes the finality timeline out in a literal, countable way.
Selection and finality aren't two unrelated mechanisms sitting next to each other in the whitepaper. One decides who votes. The other decides when their vote becomes unbreakable.
That's the part I find interesting.
And I've got two questions I'm genuinely curious about:
Does this staged finality create a meaningful window of risk in practice, or is it mostly a theoretical distinction?
And for regulated securities, is “final within a few blocks” actually good enough, or does real finance eventually demand something closer to instant finality?
Read the consensus section of the whitepaper twice this week, back to back. But didn't anything new the first time.
Second pass, one thing I'd been getting wrong finally clicked.
I'd been treating “a block got voted through” and “a block IS final” as basically the same event. They're not. There's a gap between them, and that's where the interesting security thinking lives.
A block that clears validation and ratification becomes ATTESTED only if every earlier attempt at that round failed cleanly. Otherwise it's “accepted”, which is weaker. An accepted block can still, in theory, be replaced by a competing block from an earlier attempt. An attested one can't.
Then finality builds in stages.
An attested block becomes confirmed as later blocks build on it. An accepted block needs more confirmations to reach the same status, roughly twice the number of failed attempts behind it.
Only when a block is confirmed, and everything before it is also final, does it actually become final.
So “final” isn't one event that happens when a vote passes. It's a threshold crossed block by block, and how quickly you reach it depends partly on how clean the round was.
This is where staking loops back in.
Who gets selected to vote, and who has enough credits in a committee to influence a quorum, affects how cleanly rounds clear. A messy round doesn't just slow things down in some vague way. It pushes the finality timeline out in a literal, countable way.
Selection and finality aren't two unrelated mechanisms sitting next to each other in the whitepaper. One decides who votes. The other decides when their vote becomes unbreakable.
That's the part I find interesting.
And I've got two questions I'm genuinely curious about:
Does this staged finality create a meaningful window of risk in practice, or is it mostly a theoretical distinction?
And for regulated securities, is “final within a few blocks” actually good enough, or does real finance eventually demand something closer to instant finality?
25
27
3.3k
·
--
Verified
#dusk
Here's a detail about regulated finance that surprised me Yesterday while I was scrolling through Dusk docs while having lunch.
Most regulated blockchain infrastructure isn't actually public.
It's permissioned.
A private ledger, run by an institution, that just happens to use blockchain-shaped tech underneath. Looks decentralized in the pitch deck. Isn't, really.
There's a reason for that — regulators are cautious about public, permissionless chains specifically
No single party controls who validates, who can see what, who can be held accountable if something goes wrong.
That's the whole point of a public chain, and it's exactly what makes a regulator nervous.
Which is why 21X caught my attention.
21X is the first company to get a DLT-TSS license under European regulation for a fully tokenized securities market. That license does two things: lets them combine trading and settlement into one step instead of reconciling later, and lets them run on a public, permissionless chain — not a private one dressed up to look decentralized.
That's the part I keep sitting with. Most regulated platforms get permission by staying closed. 21X got permission to use the real thing.
Dusk's role here is a trade participant relationship — 21X plans to integrate DuskEVM as one of the chains they support. Access to their regulatory exemption on one side, Dusk's infrastructure on the other. Neither side had the whole picture alone.
Tokenization was never the hard part.
Permission to run on infrastructure nobody controls was.
21X cracked that at the regulatory layer.
Dusk's cracking it at the protocol layer (deterministic settlement, selective disclosure).
Same wall, different side.
Real question:
Is a Public-Permissionless license actually rare, or is regulation just catching up? And if more regulators follow 21X, does "compliant" redefine crypto, or does crypto just become invisible plumbing?
$DUSK @Dusk_Foundation
{future}(DUSKUSDT)
Guess what makes 21X's license unusual 🔍
#dusk
Here's a detail about regulated finance that surprised me Yesterday while I was scrolling through Dusk docs while having lunch.
Most regulated blockchain infrastructure isn't actually public.
It's permissioned.
A private ledger, run by an institution, that just happens to use blockchain-shaped tech underneath. Looks decentralized in the pitch deck. Isn't, really.
There's a reason for that — regulators are cautious about public, permissionless chains specifically
No single party controls who validates, who can see what, who can be held accountable if something goes wrong.
That's the whole point of a public chain, and it's exactly what makes a regulator nervous.
Which is why 21X caught my attention.
21X is the first company to get a DLT-TSS license under European regulation for a fully tokenized securities market. That license does two things: lets them combine trading and settlement into one step instead of reconciling later, and lets them run on a public, permissionless chain — not a private one dressed up to look decentralized.
That's the part I keep sitting with. Most regulated platforms get permission by staying closed. 21X got permission to use the real thing.
Dusk's role here is a trade participant relationship — 21X plans to integrate DuskEVM as one of the chains they support. Access to their regulatory exemption on one side, Dusk's infrastructure on the other. Neither side had the whole picture alone.
Tokenization was never the hard part.
Permission to run on infrastructure nobody controls was.
21X cracked that at the regulatory layer.
Dusk's cracking it at the protocol layer (deterministic settlement, selective disclosure).
Same wall, different side.
Real question:
Is a Public-Permissionless license actually rare, or is regulation just catching up? And if more regulators follow 21X, does "compliant" redefine crypto, or does crypto just become invisible plumbing?
$DUSK @Dusk
Guess what makes 21X's license unusual 🔍
Here's a detail about regulated finance that surprised me Yesterday while I was scrolling through Dusk docs while having lunch.
Most regulated blockchain infrastructure isn't actually public.
It's permissioned.
A private ledger, run by an institution, that just happens to use blockchain-shaped tech underneath. Looks decentralized in the pitch deck. Isn't, really.
There's a reason for that — regulators are cautious about public, permissionless chains specifically
No single party controls who validates, who can see what, who can be held accountable if something goes wrong.
That's the whole point of a public chain, and it's exactly what makes a regulator nervous.
Which is why 21X caught my attention.
21X is the first company to get a DLT-TSS license under European regulation for a fully tokenized securities market. That license does two things: lets them combine trading and settlement into one step instead of reconciling later, and lets them run on a public, permissionless chain — not a private one dressed up to look decentralized.
That's the part I keep sitting with. Most regulated platforms get permission by staying closed. 21X got permission to use the real thing.
Dusk's role here is a trade participant relationship — 21X plans to integrate DuskEVM as one of the chains they support. Access to their regulatory exemption on one side, Dusk's infrastructure on the other. Neither side had the whole picture alone.
Tokenization was never the hard part.
Permission to run on infrastructure nobody controls was.
21X cracked that at the regulatory layer.
Dusk's cracking it at the protocol layer (deterministic settlement, selective disclosure).
Same wall, different side.
Real question:
Is a Public-Permissionless license actually rare, or is regulation just catching up? And if more regulators follow 21X, does "compliant" redefine crypto, or does crypto just become invisible plumbing?
$DUSK @Dusk
Guess what makes 21X's license unusual 🔍
A private, permissioned chain
75%
Public, permissionless chain
0%
It's not actually licensed yet
25%
It only covers stablecoins
0%
4 votes • Voting closed
5
5
328
·
--
Recently, the campaign announcement about #dusk made me question one of crypto’s favourite words: composability.
We usually talk about composability like more is automatically better.
A token should be able to move between protocols, become collateral, interact with DeFi, cross chains, plug into new applications...
For a normal permissionless asset, sure.
But imagine doing that with a regulated bond.
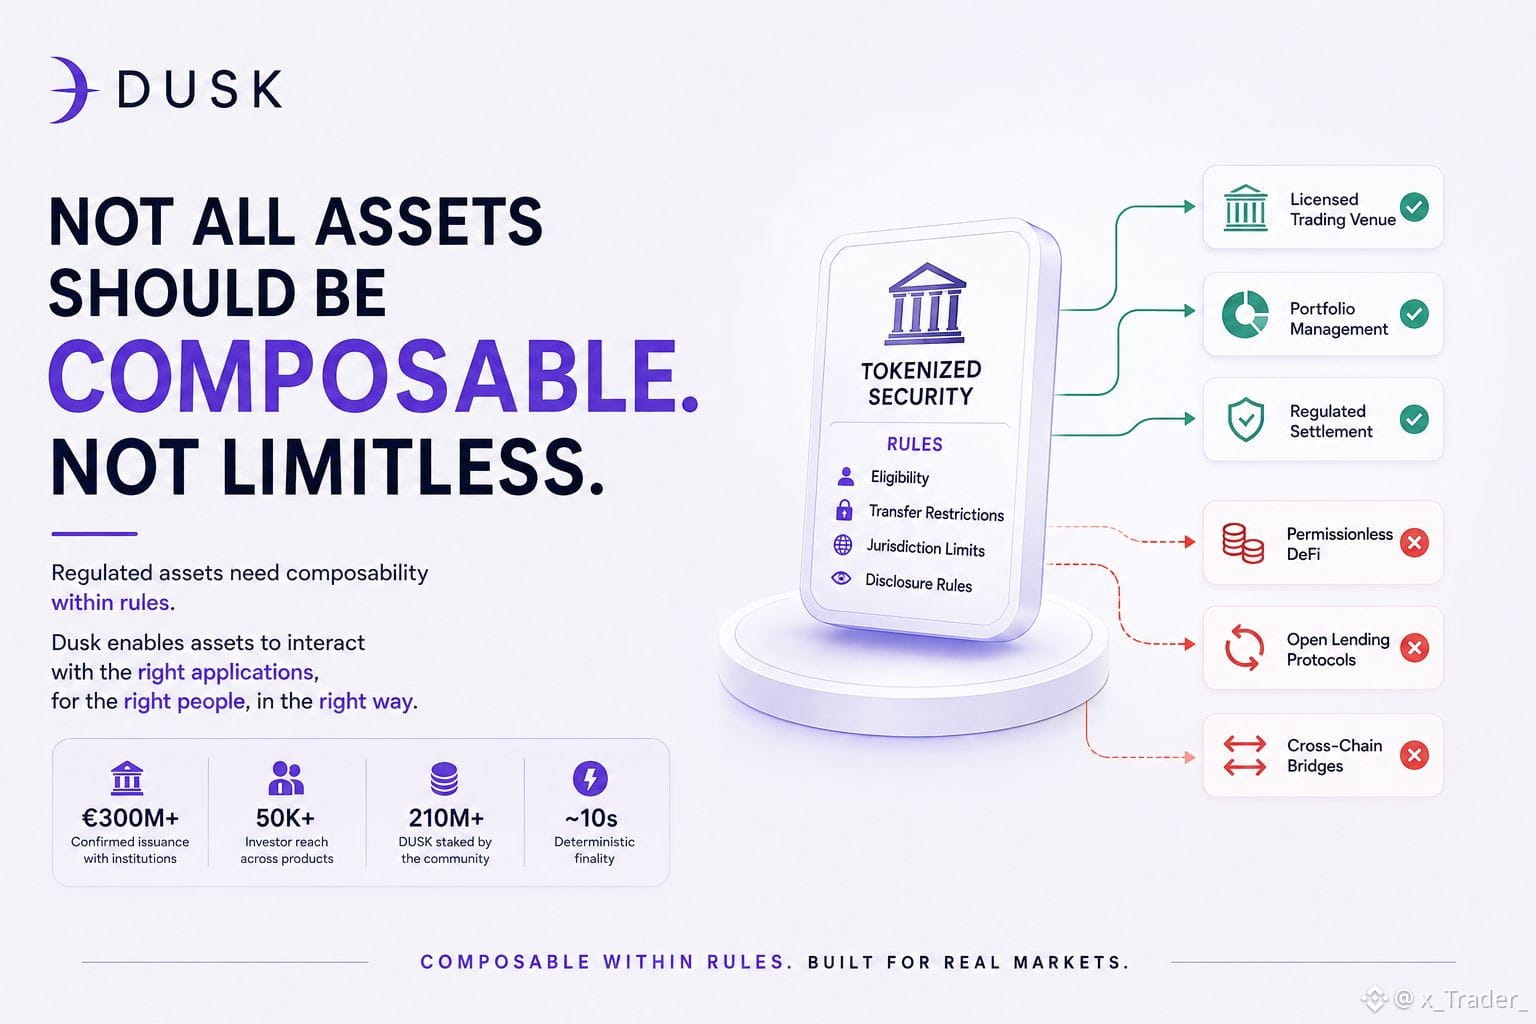
The bond might have investor eligibility requirements, transfer restrictions, jurisdiction rules and disclosure obligations.
So “make it composable with everything” suddenly sounds less impressive.
The interesting problem is making it composable without stripping away the rules attached to the asset.
That’s where Dusk gets pretty technical.
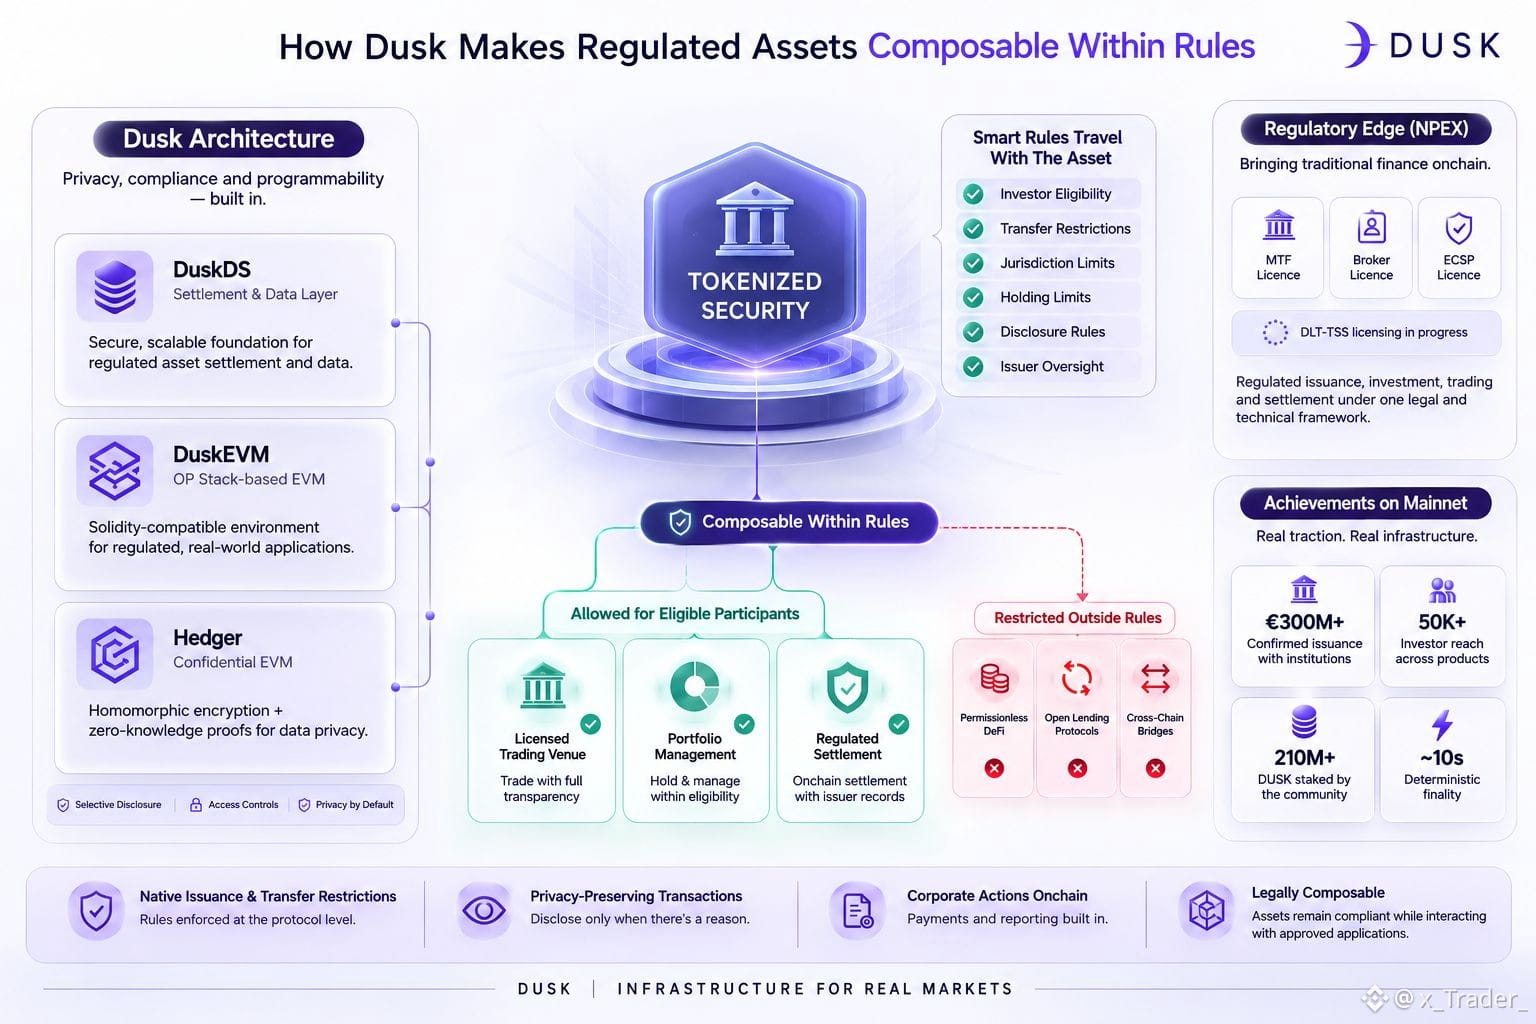
Its current architecture separates the settlement/data layer, DuskDS, from DuskEVM, an OP Stack-based EVM environment. Developers can use familiar Solidity tooling, while applications settle back to Dusk’s underlying network. Hedger adds confidential EVM workflows using homomorphic encryption and zero-knowledge proofs.
Then there’s the regulatory side.
Through its NPEX relationship, Dusk says the ecosystem has access to MTF, Broker and ECSP licences, with DLT-TSS licensing in progress. The idea is to put regulated issuance, investment, trading and settlement under a shared legal and technical framework.
And this isn't just architecture on a slide.
Dusk currently reports €300M+ in confirmed issuance with institutions, 50K+ investor reach, 210M+ DUSK staked, and ~10-second deterministic finality.
That changes my question completely.
I’m less interested in asking:
“Can RWAs be composable?”
We already know they can move around.
I want to know:
Can a regulated asset remain composable while carrying its identity, eligibility, privacy and transfer rules with it?
Because if the answer is yes, that starts looking less like putting securities on a blockchain...
and more like rebuilding the financial plumbing around them.
$DUSK @Dusk_Foundation
Recently, the campaign announcement about #dusk made me question one of crypto’s favourite words: composability.
We usually talk about composability like more is automatically better.
A token should be able to move between protocols, become collateral, interact with DeFi, cross chains, plug into new applications...
For a normal permissionless asset, sure.
But imagine doing that with a regulated bond.
The bond might have investor eligibility requirements, transfer restrictions, jurisdiction rules and disclosure obligations.
So “make it composable with everything” suddenly sounds less impressive.
The interesting problem is making it composable without stripping away the rules attached to the asset.
That’s where Dusk gets pretty technical.
Its current architecture separates the settlement/data layer, DuskDS, from DuskEVM, an OP Stack-based EVM environment. Developers can use familiar Solidity tooling, while applications settle back to Dusk’s underlying network. Hedger adds confidential EVM workflows using homomorphic encryption and zero-knowledge proofs.
Then there’s the regulatory side.
Through its NPEX relationship, Dusk says the ecosystem has access to MTF, Broker and ECSP licences, with DLT-TSS licensing in progress. The idea is to put regulated issuance, investment, trading and settlement under a shared legal and technical framework.
And this isn't just architecture on a slide.
Dusk currently reports €300M+ in confirmed issuance with institutions, 50K+ investor reach, 210M+ DUSK staked, and ~10-second deterministic finality.
That changes my question completely.
I’m less interested in asking:
“Can RWAs be composable?”
We already know they can move around.
I want to know:
Can a regulated asset remain composable while carrying its identity, eligibility, privacy and transfer rules with it?
Because if the answer is yes, that starts looking less like putting securities on a blockchain...
and more like rebuilding the financial plumbing around them.
$DUSK @Dusk
We usually talk about composability like more is automatically better.
A token should be able to move between protocols, become collateral, interact with DeFi, cross chains, plug into new applications...
For a normal permissionless asset, sure.
But imagine doing that with a regulated bond.
The bond might have investor eligibility requirements, transfer restrictions, jurisdiction rules and disclosure obligations.
So “make it composable with everything” suddenly sounds less impressive.
The interesting problem is making it composable without stripping away the rules attached to the asset.
That’s where Dusk gets pretty technical.
Its current architecture separates the settlement/data layer, DuskDS, from DuskEVM, an OP Stack-based EVM environment. Developers can use familiar Solidity tooling, while applications settle back to Dusk’s underlying network. Hedger adds confidential EVM workflows using homomorphic encryption and zero-knowledge proofs.
Then there’s the regulatory side.
Through its NPEX relationship, Dusk says the ecosystem has access to MTF, Broker and ECSP licences, with DLT-TSS licensing in progress. The idea is to put regulated issuance, investment, trading and settlement under a shared legal and technical framework.
And this isn't just architecture on a slide.
Dusk currently reports €300M+ in confirmed issuance with institutions, 50K+ investor reach, 210M+ DUSK staked, and ~10-second deterministic finality.
That changes my question completely.
I’m less interested in asking:
“Can RWAs be composable?”
We already know they can move around.
I want to know:
Can a regulated asset remain composable while carrying its identity, eligibility, privacy and transfer rules with it?
Because if the answer is yes, that starts looking less like putting securities on a blockchain...
and more like rebuilding the financial plumbing around them.
$DUSK @Dusk
20
16
473
·
--
#dusk $DUSK @Dusk_Foundation
I used to think "blockchain finality" meant the same thing everywhere. It doesn't.
On a lot of chains, a block getting added isn't really the end of the story. It can still get reorganized or replaced if a longer chain shows up later. For a casual transfer, that's background risk you never think about. For actual financial settlement , a bond payment, a trade, anything with legal weight attached, "probably final" isn't an acceptable answer.
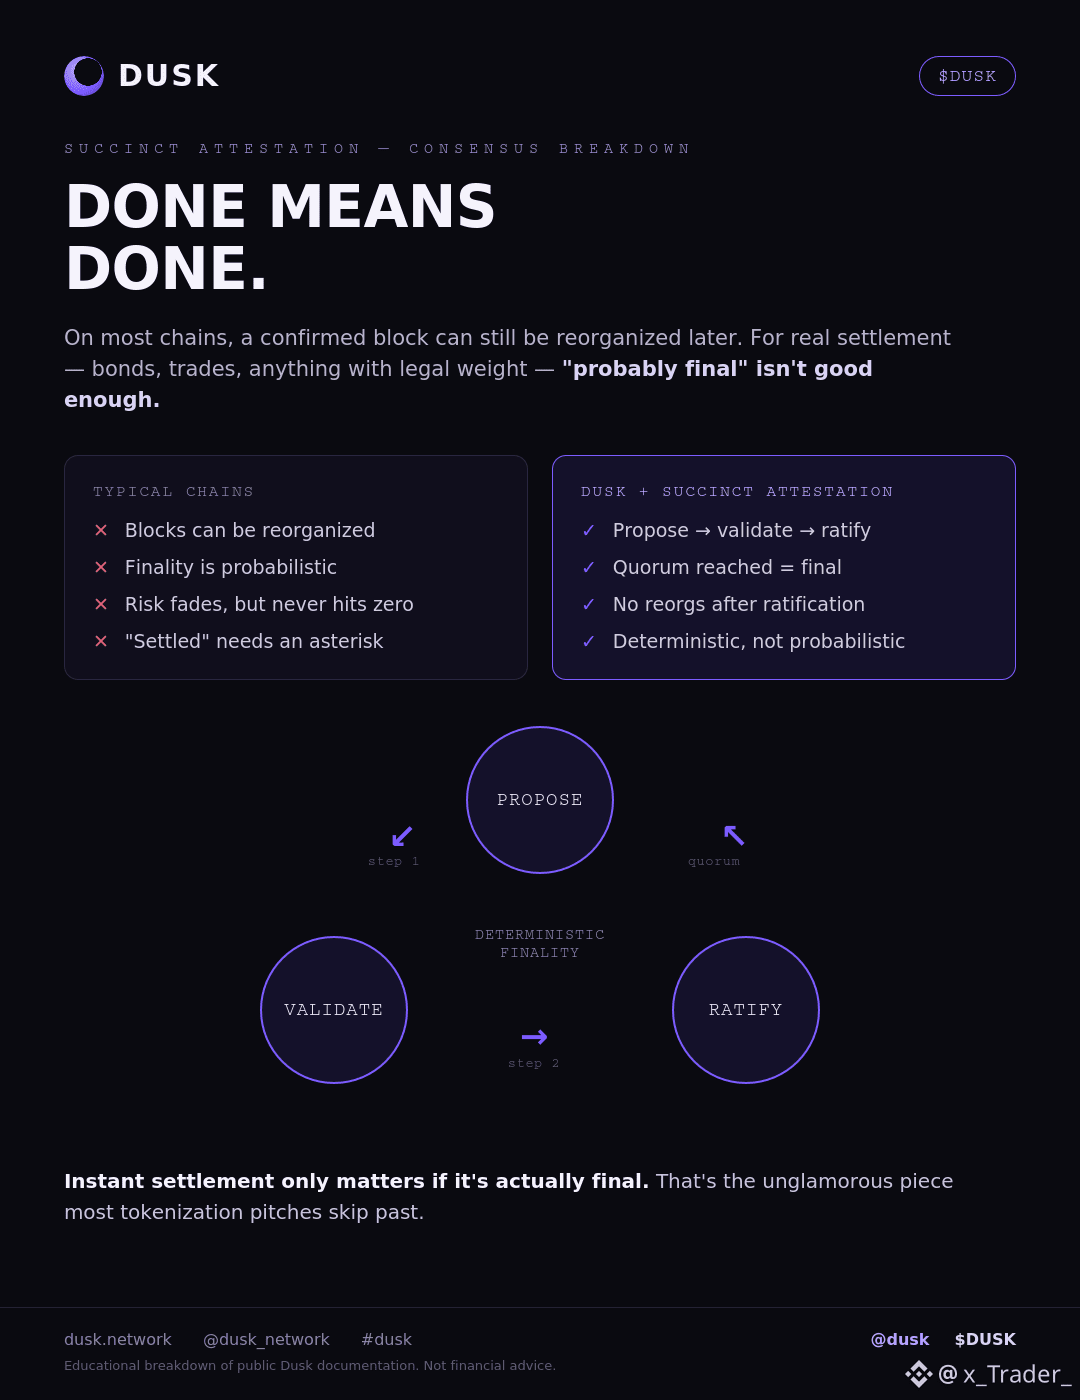
Dusk's consensus works in three steps. One validator proposes a block. A committee checks it's valid. A second committee confirms that check actually held. Once all three finish, the block is done. Not "done, probably", done. No reorgs waiting to happen a few blocks later.
Nobody writes headlines about consensus mechanics. But this is the unglamorous piece that lets a regulated exchange tell a client "this settled" and mean it literally, not "settled, barring an unlikely event three blocks from now."
Instant settlement only matters if it's actually final. That's the part most tokenization pitches skip past.
Poll:
Guess what happens once a block hits quorum on Dusk 🧠
⏳ It can still get reversed later
✅ It's final — no reorgs
📅 Waits 2 days to clear
⛽ Depends on gas price
#dusk $DUSK @Dusk
I used to think "blockchain finality" meant the same thing everywhere. It doesn't.
On a lot of chains, a block getting added isn't really the end of the story. It can still get reorganized or replaced if a longer chain shows up later. For a casual transfer, that's background risk you never think about. For actual financial settlement , a bond payment, a trade, anything with legal weight attached, "probably final" isn't an acceptable answer.
Dusk's consensus works in three steps. One validator proposes a block. A committee checks it's valid. A second committee confirms that check actually held. Once all three finish, the block is done. Not "done, probably", done. No reorgs waiting to happen a few blocks later.
Nobody writes headlines about consensus mechanics. But this is the unglamorous piece that lets a regulated exchange tell a client "this settled" and mean it literally, not "settled, barring an unlikely event three blocks from now."
Instant settlement only matters if it's actually final. That's the part most tokenization pitches skip past.
Poll:
Guess what happens once a block hits quorum on Dusk 🧠
⏳ It can still get reversed later
✅ It's final — no reorgs
📅 Waits 2 days to clear
⛽ Depends on gas price
I used to think "blockchain finality" meant the same thing everywhere. It doesn't.
On a lot of chains, a block getting added isn't really the end of the story. It can still get reorganized or replaced if a longer chain shows up later. For a casual transfer, that's background risk you never think about. For actual financial settlement , a bond payment, a trade, anything with legal weight attached, "probably final" isn't an acceptable answer.
Dusk's consensus works in three steps. One validator proposes a block. A committee checks it's valid. A second committee confirms that check actually held. Once all three finish, the block is done. Not "done, probably", done. No reorgs waiting to happen a few blocks later.
Nobody writes headlines about consensus mechanics. But this is the unglamorous piece that lets a regulated exchange tell a client "this settled" and mean it literally, not "settled, barring an unlikely event three blocks from now."
Instant settlement only matters if it's actually final. That's the part most tokenization pitches skip past.
Poll:
Guess what happens once a block hits quorum on Dusk 🧠
⏳ It can still get reversed later
✅ It's final — no reorgs
📅 Waits 2 days to clear
⛽ Depends on gas price
1
3
193
·
--
Verified
#dusk
I think people sometimes misunderstand the privacy problem in regulated finance.
It isn't simply:
“How do we hide the transaction?”
The harder question is:
“Who actually needs to see it?”
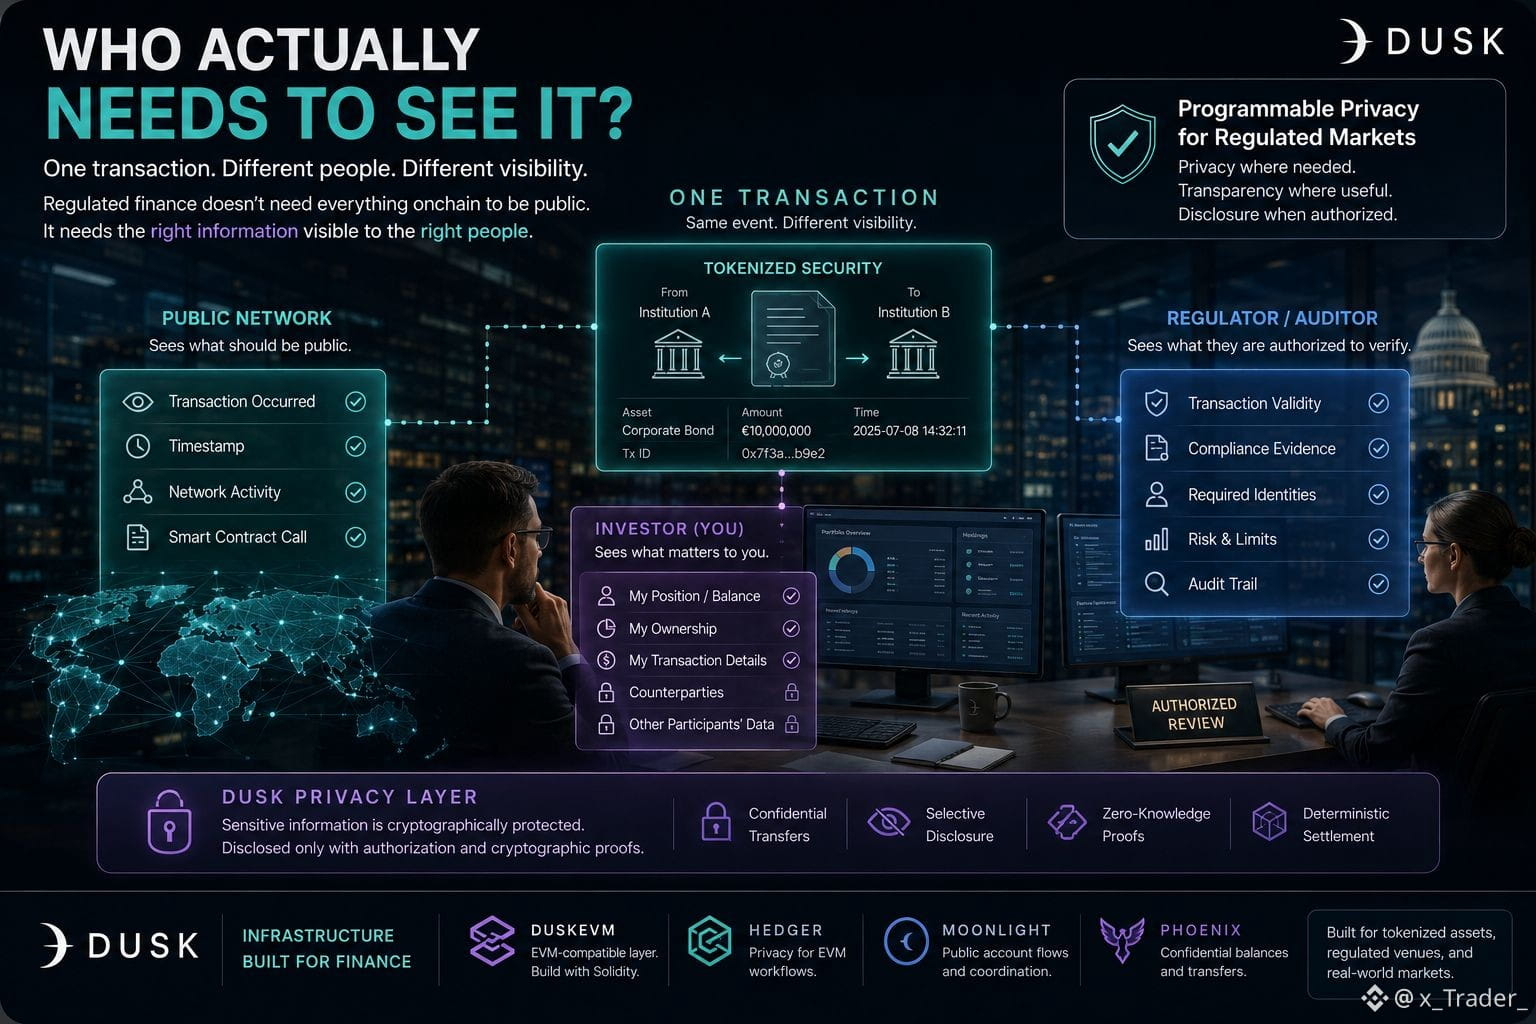
An investor shouldn't necessarily have their entire position exposed to every wallet watching the chain.
But a regulator might need to verify something.
An auditor might need evidence.
An issuer might need to check ownership or eligibility.
And the market itself still needs things that can be observed and settled.
That's the part of @Dusk_Foundation I find genuinely interesting.
Dusk isn't treating privacy like an on/off switch. Its architecture separates public flows from confidential ones, while allowing information to be disclosed to authorized parties when there's a legitimate reason for them to see it.
That makes much more sense to me for financial markets.
Because putting a bond, fund or other security onchain isn't the hard part.
The hard part is deciding what happens when different people need different levels of visibility into the same asset.
That's a problem most crypto conversations don't spend enough time on.
Dusk is building around it.
And with DuskEVM, that approach is being brought into an EVM-compatible environment, with Hedger supporting confidential EVM workflows.
That's a much more interesting pitch than “blockchain, but private.”
$DUSK @Dusk_Foundation
#dusk
I think people sometimes misunderstand the privacy problem in regulated finance.
It isn't simply:
“How do we hide the transaction?”
The harder question is:
“Who actually needs to see it?”
An investor shouldn't necessarily have their entire position exposed to every wallet watching the chain.
But a regulator might need to verify something.
An auditor might need evidence.
An issuer might need to check ownership or eligibility.
And the market itself still needs things that can be observed and settled.
That's the part of @Dusk I find genuinely interesting.
Dusk isn't treating privacy like an on/off switch. Its architecture separates public flows from confidential ones, while allowing information to be disclosed to authorized parties when there's a legitimate reason for them to see it.
That makes much more sense to me for financial markets.
Because putting a bond, fund or other security onchain isn't the hard part.
The hard part is deciding what happens when different people need different levels of visibility into the same asset.
That's a problem most crypto conversations don't spend enough time on.
Dusk is building around it.
And with DuskEVM, that approach is being brought into an EVM-compatible environment, with Hedger supporting confidential EVM workflows.
That's a much more interesting pitch than “blockchain, but private.”
$DUSK @Dusk
I think people sometimes misunderstand the privacy problem in regulated finance.
It isn't simply:
“How do we hide the transaction?”
The harder question is:
“Who actually needs to see it?”
An investor shouldn't necessarily have their entire position exposed to every wallet watching the chain.
But a regulator might need to verify something.
An auditor might need evidence.
An issuer might need to check ownership or eligibility.
And the market itself still needs things that can be observed and settled.
That's the part of @Dusk I find genuinely interesting.
Dusk isn't treating privacy like an on/off switch. Its architecture separates public flows from confidential ones, while allowing information to be disclosed to authorized parties when there's a legitimate reason for them to see it.
That makes much more sense to me for financial markets.
Because putting a bond, fund or other security onchain isn't the hard part.
The hard part is deciding what happens when different people need different levels of visibility into the same asset.
That's a problem most crypto conversations don't spend enough time on.
Dusk is building around it.
And with DuskEVM, that approach is being brought into an EVM-compatible environment, with Hedger supporting confidential EVM workflows.
That's a much more interesting pitch than “blockchain, but private.”
$DUSK @Dusk
32
15
900
·
--
Bullish
Verified
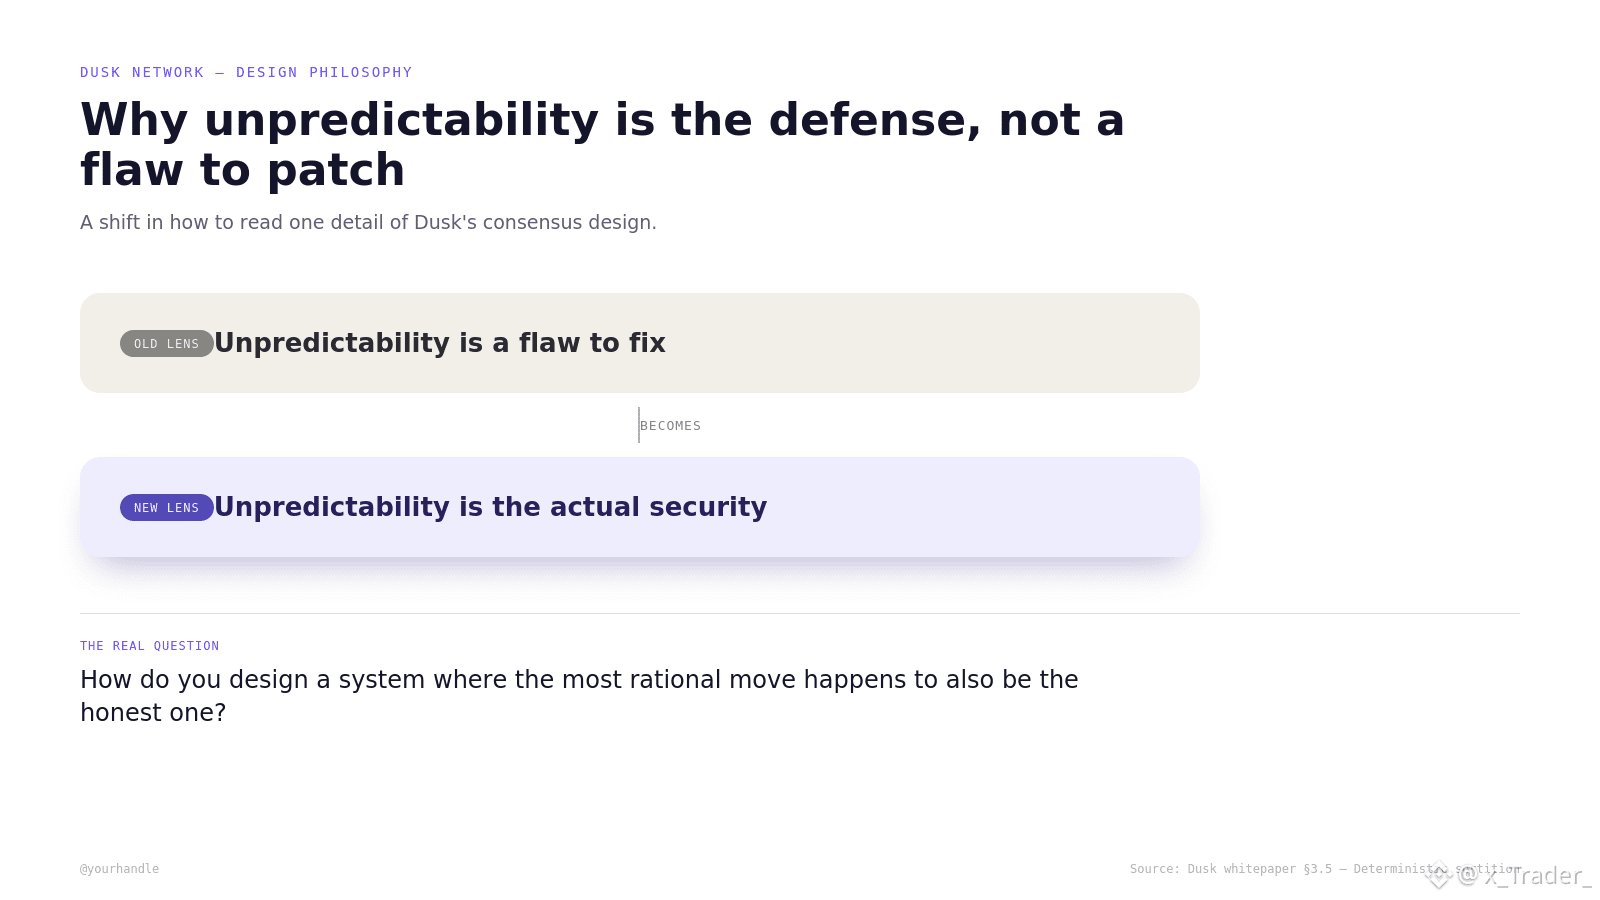
I used to think unpredictability in a blockchain was a bug you tolerate, not a feature you'd actually design for.
Studying Dusk changed that.
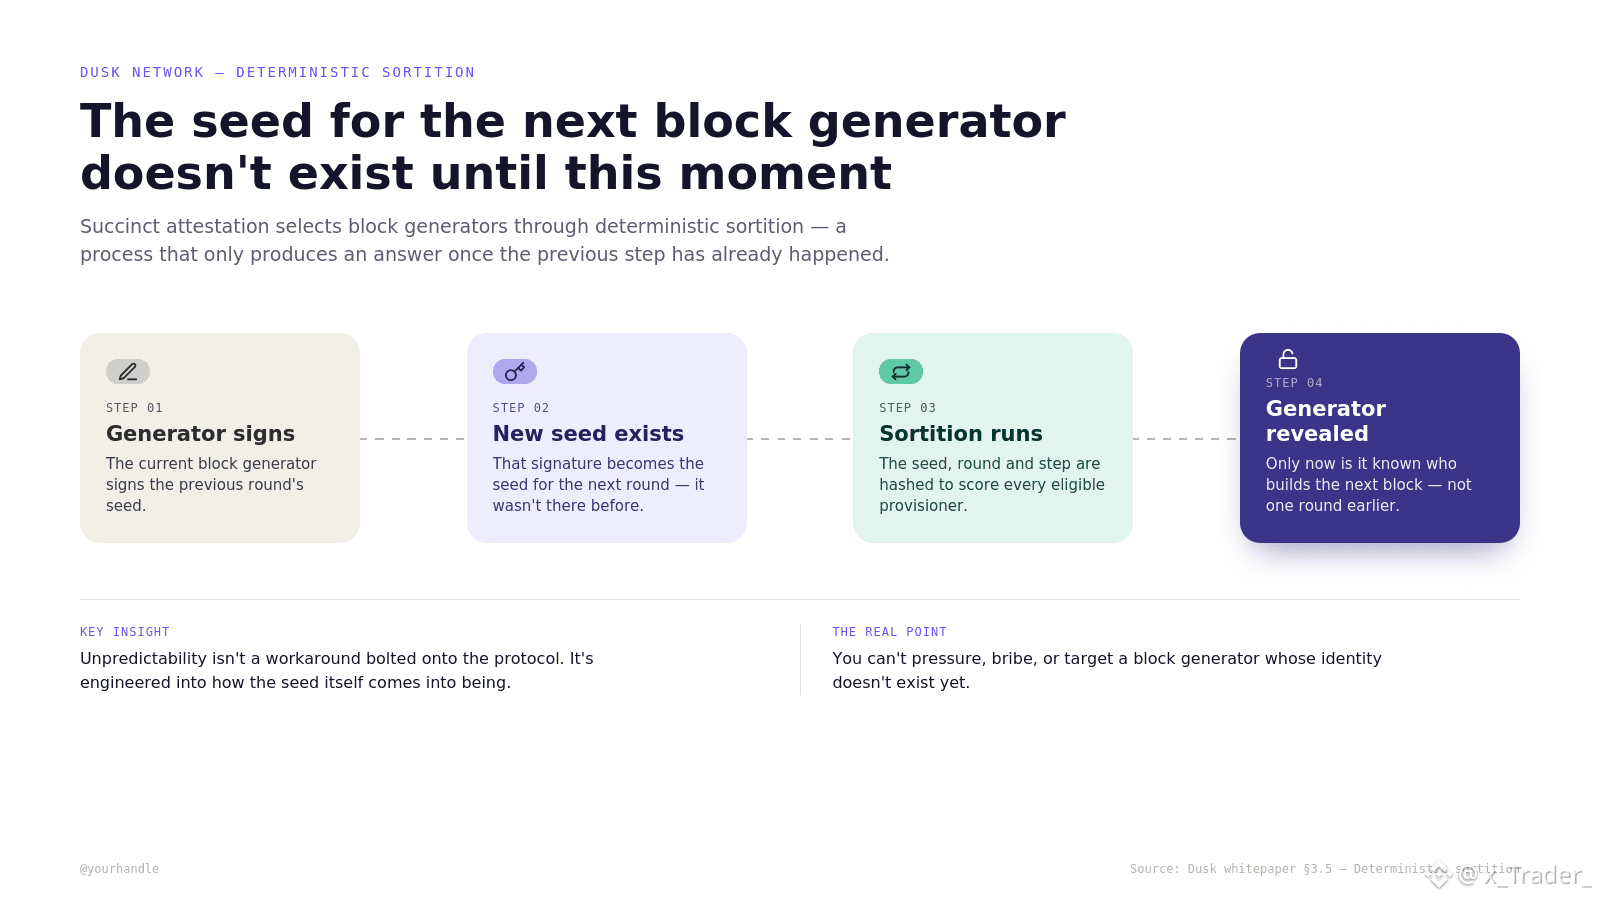
Imagine you're a provisioner. You've staked, you're eligible, you know you could be picked to generate the next block. But you don't know if you will be. Neither does anyone else. Not the other validators. Not even you, ten seconds before it happens.
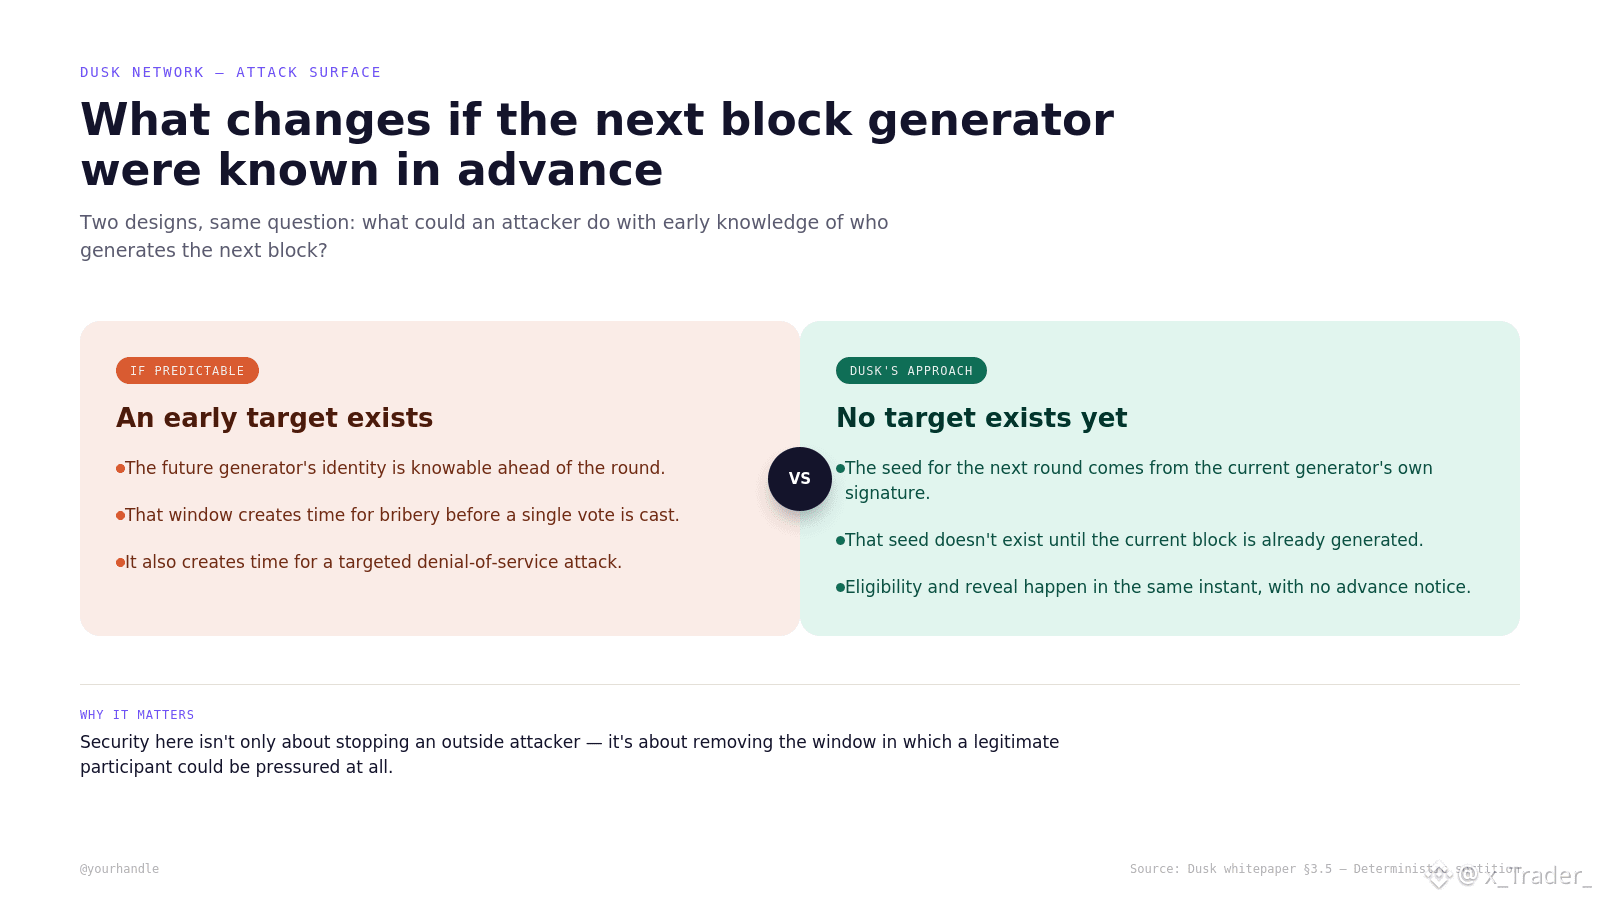
Here's the strange part. The seed that decides who gets picked for block N+1 doesn't exist yet while block N is still being built. It's literally generated from the current block generator signing the previous seed. The answer to "who's next" isn't hidden somewhere — it hasn't been computed yet.
Why does that matter? Because predictability is a liability here, not a convenience. If an attacker could work out who generates block 40 today, they'd have all the time in the world to target that validator — bribe them, DDoS them, pressure them — before the moment ever arrives.
Dusk's deterministic sortition closes that window entirely. You only find out you're the generator the instant it's already true.
So the real design question wasn't "how do we pick a leader." It was "how do we pick one without ever letting anyone plan for it."
Guess what happens the moment block selection becomes predictable even slightly early?
#dusk $DUSK @Dusk_Foundation
Poll:
Guess what breaks first if you could predict the next block generator
🎯 Bribery becomes possible
🛑 DDoS becomes possible
⚖️ Both, same vulnerability
🔒 Nothing, still secure
I used to think unpredictability in a blockchain was a bug you tolerate, not a feature you'd actually design for.
Studying Dusk changed that.
Imagine you're a provisioner. You've staked, you're eligible, you know you could be picked to generate the next block. But you don't know if you will be. Neither does anyone else. Not the other validators. Not even you, ten seconds before it happens.
Here's the strange part. The seed that decides who gets picked for block N+1 doesn't exist yet while block N is still being built. It's literally generated from the current block generator signing the previous seed. The answer to "who's next" isn't hidden somewhere — it hasn't been computed yet.
Why does that matter? Because predictability is a liability here, not a convenience. If an attacker could work out who generates block 40 today, they'd have all the time in the world to target that validator — bribe them, DDoS them, pressure them — before the moment ever arrives.
Dusk's deterministic sortition closes that window entirely. You only find out you're the generator the instant it's already true.
So the real design question wasn't "how do we pick a leader." It was "how do we pick one without ever letting anyone plan for it."
Guess what happens the moment block selection becomes predictable even slightly early?
#dusk $DUSK @Dusk
Poll:
Guess what breaks first if you could predict the next block generator
🎯 Bribery becomes possible
🛑 DDoS becomes possible
⚖️ Both, same vulnerability
🔒 Nothing, still secure
Studying Dusk changed that.
Imagine you're a provisioner. You've staked, you're eligible, you know you could be picked to generate the next block. But you don't know if you will be. Neither does anyone else. Not the other validators. Not even you, ten seconds before it happens.
Here's the strange part. The seed that decides who gets picked for block N+1 doesn't exist yet while block N is still being built. It's literally generated from the current block generator signing the previous seed. The answer to "who's next" isn't hidden somewhere — it hasn't been computed yet.
Why does that matter? Because predictability is a liability here, not a convenience. If an attacker could work out who generates block 40 today, they'd have all the time in the world to target that validator — bribe them, DDoS them, pressure them — before the moment ever arrives.
Dusk's deterministic sortition closes that window entirely. You only find out you're the generator the instant it's already true.
So the real design question wasn't "how do we pick a leader." It was "how do we pick one without ever letting anyone plan for it."
Guess what happens the moment block selection becomes predictable even slightly early?
#dusk $DUSK @Dusk
Poll:
Guess what breaks first if you could predict the next block generator
🎯 Bribery becomes possible
🛑 DDoS becomes possible
⚖️ Both, same vulnerability
🔒 Nothing, still secure
21
15
545
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
NvidiaLoses$2.7TrillionInMonthAndAHalf
29,885 views
164 Discussing
Nvidia’s $2.7 Trillion Wipeout: When Narrative Overrides Numbers 📉
Crypto With Faisal
·7 Likes
·6.2k views
CanBTCReboundAfterFallingBelow60K?
868,709 views
3,222 Discussing
GlobalStocksFaceLongestLosingStreakSince2023
327,445 views
2,159 Discussing