
#cybersecurity
cybersecurity
1.6M views
3,822 Discussing
Hot
Latest

·
--
FBI Warns of Crypto Theft via Fake Video Calls
A familiar face on a video call may not be who it seems.
The FBI says the North Korean-attributed “FaceStealer” scheme stole more than 00 million in cryptocurrency over 18 months, targeting people in crypto and Web3. The Justice Department says attackers used impersonated contacts and fake meeting “fixes” to install malware; authorities disrupted cloud infrastructure and seized more than 900 webcam videos of victims.
For teams, verify meeting links independently and never install software from an unexpected prompt. Would your team spot this tactic?
Source: U.S. Department of Justice, Nov. 12, 2026: https://www.justice.gov/opa/pr/justice-department-announces-actions-disrupt-north-koreas-massive-theft-cryptocurrency
Market watch:
#Cybersecurity #Web3 #CryptoSecurity
FBI Warns of Crypto Theft via Fake Video Calls
A familiar face on a video call may not be who it seems.
The FBI says the North Korean-attributed “FaceStealer” scheme stole more than 00 million in cryptocurrency over 18 months, targeting people in crypto and Web3. The Justice Department says attackers used impersonated contacts and fake meeting “fixes” to install malware; authorities disrupted cloud infrastructure and seized more than 900 webcam videos of victims.
For teams, verify meeting links independently and never install software from an unexpected prompt. Would your team spot this tactic?
Source: U.S. Department of Justice, Nov. 12, 2026: https://www.justice.gov/opa/pr/justice-department-announces-actions-disrupt-north-koreas-massive-theft-cryptocurrency
Market watch:
#Cybersecurity #Web3 #CryptoSecurity
A familiar face on a video call may not be who it seems.
The FBI says the North Korean-attributed “FaceStealer” scheme stole more than 00 million in cryptocurrency over 18 months, targeting people in crypto and Web3. The Justice Department says attackers used impersonated contacts and fake meeting “fixes” to install malware; authorities disrupted cloud infrastructure and seized more than 900 webcam videos of victims.
For teams, verify meeting links independently and never install software from an unexpected prompt. Would your team spot this tactic?
Source: U.S. Department of Justice, Nov. 12, 2026: https://www.justice.gov/opa/pr/justice-department-announces-actions-disrupt-north-koreas-massive-theft-cryptocurrency
Market watch:
#Cybersecurity #Web3 #CryptoSecurity

Recent findings reveal that artificial intelligence is actively accelerating cyber attacks, helping threat actors breach ten major organizations recently. While human operators still steer the targets, the lowered technical barrier of AI tools means enterprise and Web3 security protocols must evolve fast. As automation scales, the crypto and tech sectors face unprecedented vulnerability. Staying proactive with robust infrastructure defense is no longer optional. #CyberSecurity #ArtificialIntelligence #TechNews
Recent findings reveal that artificial intelligence is actively accelerating cyber attacks, helping threat actors breach ten major organizations recently. While human operators still steer the targets, the lowered technical barrier of AI tools means enterprise and Web3 security protocols must evolve fast. As automation scales, the crypto and tech sectors face unprecedented vulnerability. Staying proactive with robust infrastructure defense is no longer optional. #CyberSecurity #ArtificialIntelligence #TechNews

🔐 XRP LEDGER: SECURITY REMAINS A PRIORITY
The XRP Ledger activated the fixCleanup3_4_0 amendment on November 4.
The update addressed a vulnerability involving token-burning permissions.
Why does this matter?
Blockchain security is essential for:
* Protecting network integrity.
* Maintaining user confidence.
* Supporting long-term adoption.
Security improvements are important even when they don’t make headlines about price.
#XRP #XRPL #Cybersecurity #Blockchain
🔐 XRP LEDGER: SECURITY REMAINS A PRIORITY
The XRP Ledger activated the fixCleanup3_4_0 amendment on November 4.
The update addressed a vulnerability involving token-burning permissions.
Why does this matter?
Blockchain security is essential for:
* Protecting network integrity.
* Maintaining user confidence.
* Supporting long-term adoption.
Security improvements are important even when they don’t make headlines about price.
#XRP #XRPL #Cybersecurity #Blockchain
The XRP Ledger activated the fixCleanup3_4_0 amendment on November 4.
The update addressed a vulnerability involving token-burning permissions.
Why does this matter?
Blockchain security is essential for:
* Protecting network integrity.
* Maintaining user confidence.
* Supporting long-term adoption.
Security improvements are important even when they don’t make headlines about price.
#XRP #XRPL #Cybersecurity #Blockchain
125
·
--
**Hackers posed as industry pros in fake Zoom/Teams calls, stole $400 M from crypto & Web3 experts.**
- FBI disrupted a North Korea‑run social‑engineering infrastructure that recorded victim webcams, injected malware, and accessed crypto wallets and social media accounts.
- Over 900 professionals in crypto, Web3 and cybersecurity were targeted; the scheme, dubbed “FaceDealer,” generated more than $400 million in thefts within 18 months.
- Attackers hijacked Telegram and LinkedIn accounts to impersonate contacts, then forced victims to run a fake update that installed the malware.
What verification steps will you add before joining any video call that claims to be a peer or partner?
#CyberSecurity #Crypto #Web3 #NorthKorea #FinTech
**Hackers posed as industry pros in fake Zoom/Teams calls, stole $400 M from crypto & Web3 experts.**
- FBI disrupted a North Korea‑run social‑engineering infrastructure that recorded victim webcams, injected malware, and accessed crypto wallets and social media accounts.
- Over 900 professionals in crypto, Web3 and cybersecurity were targeted; the scheme, dubbed “FaceDealer,” generated more than $400 million in thefts within 18 months.
- Attackers hijacked Telegram and LinkedIn accounts to impersonate contacts, then forced victims to run a fake update that installed the malware.
What verification steps will you add before joining any video call that claims to be a peer or partner?
#CyberSecurity #Crypto #Web3 #NorthKorea #FinTech
- FBI disrupted a North Korea‑run social‑engineering infrastructure that recorded victim webcams, injected malware, and accessed crypto wallets and social media accounts.
- Over 900 professionals in crypto, Web3 and cybersecurity were targeted; the scheme, dubbed “FaceDealer,” generated more than $400 million in thefts within 18 months.
- Attackers hijacked Telegram and LinkedIn accounts to impersonate contacts, then forced victims to run a fake update that installed the malware.
What verification steps will you add before joining any video call that claims to be a peer or partner?
#CyberSecurity #Crypto #Web3 #NorthKorea #FinTech
6
·
--
White House AI Task Force Calls for Time-Limited Cyber Reporting Relief
Could a temporary liability shield help firms report AI-era cyber incidents faster?
The White House’s AI task force is urging agencies to limit regulatory liability for organizations that voluntarily report cyber vulnerabilities and incidents in good faith. It says the threat environment has changed and older standards may no longer fit. The recommendation is conditional—lawful, practical, and consistent with public health and safety—and would last at least 12 months, with possible extension. This is a task-force recommendation, not a binding government-wide rule. Easier reporting may improve information sharing, but safeguards still matter. Would this strengthen security or weaken accountability?
Sources: Reuters: https://www.reuters.com/world/us/trumps-ai-task-force-met-thursday-discussed-ai-powered-cyberattacks-2026-11-13/ · Cybersecurity Dive: https://www.cybersecuritydive.com/news/ai-white-house-task-force-cybersecurity-regulation/874679/
Market watch:
#Cybersecurity #AI #USPolicy
White House AI Task Force Calls for Time-Limited Cyber Reporting Relief
Could a temporary liability shield help firms report AI-era cyber incidents faster?
The White House’s AI task force is urging agencies to limit regulatory liability for organizations that voluntarily report cyber vulnerabilities and incidents in good faith. It says the threat environment has changed and older standards may no longer fit. The recommendation is conditional—lawful, practical, and consistent with public health and safety—and would last at least 12 months, with possible extension. This is a task-force recommendation, not a binding government-wide rule. Easier reporting may improve information sharing, but safeguards still matter. Would this strengthen security or weaken accountability?
Sources: Reuters: https://www.reuters.com/world/us/trumps-ai-task-force-met-thursday-discussed-ai-powered-cyberattacks-2026-11-13/ · Cybersecurity Dive: https://www.cybersecuritydive.com/news/ai-white-house-task-force-cybersecurity-regulation/874679/
Market watch:
#Cybersecurity #AI #USPolicy
Could a temporary liability shield help firms report AI-era cyber incidents faster?
The White House’s AI task force is urging agencies to limit regulatory liability for organizations that voluntarily report cyber vulnerabilities and incidents in good faith. It says the threat environment has changed and older standards may no longer fit. The recommendation is conditional—lawful, practical, and consistent with public health and safety—and would last at least 12 months, with possible extension. This is a task-force recommendation, not a binding government-wide rule. Easier reporting may improve information sharing, but safeguards still matter. Would this strengthen security or weaken accountability?
Sources: Reuters: https://www.reuters.com/world/us/trumps-ai-task-force-met-thursday-discussed-ai-powered-cyberattacks-2026-11-13/ · Cybersecurity Dive: https://www.cybersecuritydive.com/news/ai-white-house-task-force-cybersecurity-regulation/874679/
Market watch:
#Cybersecurity #AI #USPolicy
1
Microsoft just exposed how easily advanced AI models can be manipulated into acting as covert sleeper agents through isolated neural triggers. This hidden vulnerability proves that centralized machine learning poses massive security risks. In the Web3 era, decentralized AI networks verified on-chain are essential to prevent backdoor tampering and ensure true system transparency. $FET $AGIX $NEAR #AI #CyberSecurity #TechNews
Microsoft just exposed how easily advanced AI models can be manipulated into acting as covert sleeper agents through isolated neural triggers. This hidden vulnerability proves that centralized machine learning poses massive security risks. In the Web3 era, decentralized AI networks verified on-chain are essential to prevent backdoor tampering and ensure true system transparency. $FET $AGIX $NEAR #AI #CyberSecurity #TechNews
342
·
--
Article
SECURITY ALERT: YOUR TRADING ACCOUNTS COULD BE AT RISK!🚨 SECURITY ALERT: YOUR TRADING ACCOUNTS COULD BE AT RISK!
🔐 THE ULTIMATE CYBERSECURITY CHECKLIST EVERY TRADER MUST FOLLOW
Protect your passwords. Activate 2FA. Secure your capital.
Your trading account is not just another online account. It may contain your capital, personal information, transaction history, and access to your financial assets.
One weak password, one phishing link, or one compromised email account could put everything at risk.
Every trader should take account security seriously. Do not wait until you lose access to your funds to start protecting yourself.
Below is a complete security checklist every trader should follow.
🔐 1. WHAT IS A WEAK PASSWORD?
A weak password is any password that is easy to guess, predict, or discover through automated attacks or leaked databases.
Examples of weak passwords:
123456789password123Arvo123456Bitcoin2025Your name followed by your birth year.The same password you use across multiple websites.
Why are these dangerous?
Hackers use automated tools to test common passwords and credentials leaked from other websites. If you reuse one password across multiple platforms, a breach on one website could expose your other accounts.
What should you do?
Use passwords of at least 16 characters.Generate random, unique passwords for every account.Never reuse passwords.Never use your name, birthday, phone number, or predictable personal information.Use a reputable password manager to generate and store your passwords securely.
Remember: A password should be unique to one account, not shared across your digital life.
🔐 2. CHANGE YOUR EXISTING WEAK AND REUSED PASSWORDS
Do not delay this.
Start with your most important accounts:
Cryptocurrency exchanges (Binance, OKX, Bybit, etc.).Your primary email account.Trading platforms and brokerage accounts.Banking and financial accounts.Social media accounts.Cloud storage and other accounts containing personal information.
If you have reused the same password on multiple platforms, replace it with a different, randomly generated password on each one.
Also change passwords immediately if you suspect compromise or discover that they have appeared in a data breach.
🛡️ 3. ACTIVATE TWO-FACTOR AUTHENTICATION (2FA)
This is one of the most important security measures you can implement.
Two-factor authentication means that accessing your account requires an additional verification factor beyond your password.
Even if someone discovers your password, 2FA makes unauthorized access significantly more difficult.
Enable 2FA on every important platform that supports it.
Preferred security methods:
Passkeys: Use them wherever supported. They provide strong phishing-resistant authentication.Hardware security keys: Physical security devices such as YubiKeys offer excellent protection.Authenticator applications: Use a trusted authenticator app to generate time-based verification codes.SMS verification: Better than having no additional protection, but less secure than the options above because phone numbers can be targeted through SIM-swapping attacks.
Do not rely on your password alone.
📧 4. SECURE YOUR EMAIL ACCOUNT FIRST
Your email account is one of the most important parts of your digital security.
Think about it: If someone gains access to your email, they may be able to reset passwords, intercept security notifications, and attempt to access your other accounts.
Take these steps:
Create a strong, unique email password.Activate 2FA or a passkey.Review all logged-in devices and active sessions.Remove unknown devices.Check recovery email addresses and phone numbers.Review email forwarding rules and filters for anything you did not create.Never share email verification codes with anyone.
If your email is compromised, many of your other accounts could be at risk.
🚨 5. ACTIVATE ALL AVAILABLE EXCHANGE SECURITY FEATURES
If you trade cryptocurrency, securing your exchange account is essential.
For Binance and other exchanges, review the following settings:
A. Anti-Phishing Code
Activate your exchange's anti-phishing code if available.
This helps you distinguish genuine platform emails from fraudulent messages pretending to come from the exchange.
B. Withdrawal Address Whitelist
Enable withdrawal address whitelisting.
This restricts withdrawals to approved wallet addresses, adding another security barrier if your account is compromised.
C. Passkeys and 2FA
Activate available passkeys, authenticator verification, or hardware security keys.
D. Device Management
Regularly inspect your account's trusted devices and active sessions. Remove anything you do not recognize.
E. Login and Withdrawal Notifications
Enable security notifications so you can identify suspicious login attempts and account activity.
F. API Key Protection
If you use API connections for trading:
Delete unused API keys.Never share API keys or secret keys.Disable withdrawal permissions.Grant only the permissions you actually need.Restrict API access to trusted IP addresses whenever possible.Never paste API credentials into unknown websites or applications.
Your API credentials should be treated like your account password.
📱 6. SECURE YOUR PHONE AND COMPUTER
Your account security is only as strong as the devices you use to access it.
Follow these precautions:
Keep your operating system and applications updated.Use a strong device password or PIN.Activate fingerprint or facial authentication where available.Install applications only from official sources.Avoid suspicious browser extensions.Use reputable antivirus and security software.Never install unknown trading software or files sent by strangers.Avoid logging into financial accounts through public or untrusted computers.Never give remote access to your computer to someone claiming to be technical support.
A compromised device can expose even very strong passwords.
🎣 7. LEARN TO RECOGNIZE PHISHING ATTACKS
One of the biggest threats to traders is phishing.
Phishing is when someone impersonates a legitimate company, exchange, support agent, or individual to trick you into revealing confidential information.
Common examples include:
Fake Binance login pages.Messages claiming your account will be suspended.Fake customer support representatives.Messages promising free cryptocurrency or rewards.Fake investment opportunities.Suspicious links asking you to verify your wallet.Fake applications and browser extensions.
Protect yourself:
Never click suspicious links.Always verify the website address before logging in.Access exchanges through official bookmarks or manually verified websites.Never share passwords, 2FA codes, recovery codes, or private keys.Remember that legitimate support staff should never ask you to disclose your password or authentication codes.
A professional-looking message does not mean it is legitimate.
🔑 8. PROTECT YOUR RECOVERY CODES AND PRIVATE KEYS
When activating an authenticator, passkey, or hardware security key, you may receive backup or recovery information.
Protect it carefully.
Store recovery codes in a secure offline location.Never send them through social media or messaging applications.Never store private keys or seed phrases in ordinary notes or screenshots.Do not share your wallet's recovery phrase with anyone.Keep secure backups of your authenticator recovery information.
Losing access to your recovery information can make account recovery extremely difficult.
📞 9. PROTECT YOUR PHONE NUMBER AGAINST SIM SWAPPING
SIM swapping happens when criminals convince or manipulate a mobile carrier into transferring your phone number to another SIM card.
This can allow them to receive SMS verification codes intended for you.
To reduce this risk:
Contact your mobile provider and ask about SIM-swap protection.Set a carrier account PIN or port-out lock if available.Secure your mobile provider account with a unique password.Avoid using SMS as your primary authentication method when stronger alternatives are available.
🔍 10. REGULARLY AUDIT YOUR ACCOUNT SECURITY
Do not secure your accounts once and forget about them.
Make security checks part of your routine.
Review:
Active login sessions.Recognized devices.Recent account activity.Connected third-party applications.API permissions.Withdrawal addresses.Recovery email addresses and phone numbers.Password breach alerts.
Remove anything unfamiliar or unnecessary.
⚠️ YOUR TRADER SECURITY CHECKLIST
Before you continue trading, make sure you have completed these steps:
☐ Changed all weak, reused, or compromised passwords.
☐ Created unique passwords of at least 16 characters.
☐ Started using a reputable password manager.
☐ Activated 2FA on all important accounts.
☐ Enabled passkeys or hardware security keys wherever possible.
☐ Secured my primary email account.
☐ Enabled exchange anti-phishing protection.
☐ Activated withdrawal address whitelisting.
☐ Reviewed trusted devices and active sessions.
☐ Removed unused API keys and restricted API permissions.
☐ Secured my phone and computer.
☐ Stored recovery codes securely.
☐ Learned how to recognize phishing attempts.
☐ Protected my phone number against SIM swapping.
🚨 FINAL MESSAGE TO ALL TRADERS
You spend hours analyzing charts, studying market structure, managing risk, and protecting your trading capital.
But what is the point of having a profitable trading strategy if you neglect the security of the accounts holding your money?
Account security is part of risk management.
Do not assume you are too small to become a target. Cybercriminals do not necessarily target only wealthy individuals or large accounts. Anyone with valuable account access can become a target.
Take 30–60 minutes today and review your security settings. Change weak passwords, activate additional authentication, and secure your devices.
Do not wait for a security breach to teach you the importance of cybersecurity.
Protect your capital. Protect your identity. Protect your accounts.
Stay alert. Stay secure. Trade responsibly.
— ARVO
I am currently watching these top gainers: $AKE $SHELL $TAC
#CyberSecurity #TradingSecurity101 #CryptoSecurity #Binancesecurity #AccountProtection
SECURITY ALERT: YOUR TRADING ACCOUNTS COULD BE AT RISK!
🚨 SECURITY ALERT: YOUR TRADING ACCOUNTS COULD BE AT RISK!
🔐 THE ULTIMATE CYBERSECURITY CHECKLIST EVERY TRADER MUST FOLLOW
Protect your passwords. Activate 2FA. Secure your capital.
Your trading account is not just another online account. It may contain your capital, personal information, transaction history, and access to your financial assets.
One weak password, one phishing link, or one compromised email account could put everything at risk.
Every trader should take account security seriously. Do not wait until you lose access to your funds to start protecting yourself.
Below is a complete security checklist every trader should follow.
🔐 1. WHAT IS A WEAK PASSWORD?
A weak password is any password that is easy to guess, predict, or discover through automated attacks or leaked databases.
Examples of weak passwords:
123456789password123Arvo123456Bitcoin2025Your name followed by your birth year.The same password you use across multiple websites.
Why are these dangerous?
Hackers use automated tools to test common passwords and credentials leaked from other websites. If you reuse one password across multiple platforms, a breach on one website could expose your other accounts.
What should you do?
Use passwords of at least 16 characters.Generate random, unique passwords for every account.Never reuse passwords.Never use your name, birthday, phone number, or predictable personal information.Use a reputable password manager to generate and store your passwords securely.
Remember: A password should be unique to one account, not shared across your digital life.
🔐 2. CHANGE YOUR EXISTING WEAK AND REUSED PASSWORDS
Do not delay this.
Start with your most important accounts:
Cryptocurrency exchanges (Binance, OKX, Bybit, etc.).Your primary email account.Trading platforms and brokerage accounts.Banking and financial accounts.Social media accounts.Cloud storage and other accounts containing personal information.
If you have reused the same password on multiple platforms, replace it with a different, randomly generated password on each one.
Also change passwords immediately if you suspect compromise or discover that they have appeared in a data breach.
🛡️ 3. ACTIVATE TWO-FACTOR AUTHENTICATION (2FA)
This is one of the most important security measures you can implement.
Two-factor authentication means that accessing your account requires an additional verification factor beyond your password.
Even if someone discovers your password, 2FA makes unauthorized access significantly more difficult.
Enable 2FA on every important platform that supports it.
Preferred security methods:
Passkeys: Use them wherever supported. They provide strong phishing-resistant authentication.Hardware security keys: Physical security devices such as YubiKeys offer excellent protection.Authenticator applications: Use a trusted authenticator app to generate time-based verification codes.SMS verification: Better than having no additional protection, but less secure than the options above because phone numbers can be targeted through SIM-swapping attacks.
Do not rely on your password alone.
📧 4. SECURE YOUR EMAIL ACCOUNT FIRST
Your email account is one of the most important parts of your digital security.
Think about it: If someone gains access to your email, they may be able to reset passwords, intercept security notifications, and attempt to access your other accounts.
Take these steps:
Create a strong, unique email password.Activate 2FA or a passkey.Review all logged-in devices and active sessions.Remove unknown devices.Check recovery email addresses and phone numbers.Review email forwarding rules and filters for anything you did not create.Never share email verification codes with anyone.
If your email is compromised, many of your other accounts could be at risk.
🚨 5. ACTIVATE ALL AVAILABLE EXCHANGE SECURITY FEATURES
If you trade cryptocurrency, securing your exchange account is essential.
For Binance and other exchanges, review the following settings:
A. Anti-Phishing Code
Activate your exchange's anti-phishing code if available.
This helps you distinguish genuine platform emails from fraudulent messages pretending to come from the exchange.
B. Withdrawal Address Whitelist
Enable withdrawal address whitelisting.
This restricts withdrawals to approved wallet addresses, adding another security barrier if your account is compromised.
C. Passkeys and 2FA
Activate available passkeys, authenticator verification, or hardware security keys.
D. Device Management
Regularly inspect your account's trusted devices and active sessions. Remove anything you do not recognize.
E. Login and Withdrawal Notifications
Enable security notifications so you can identify suspicious login attempts and account activity.
F. API Key Protection
If you use API connections for trading:
Delete unused API keys.Never share API keys or secret keys.Disable withdrawal permissions.Grant only the permissions you actually need.Restrict API access to trusted IP addresses whenever possible.Never paste API credentials into unknown websites or applications.
Your API credentials should be treated like your account password.
📱 6. SECURE YOUR PHONE AND COMPUTER
Your account security is only as strong as the devices you use to access it.
Follow these precautions:
Keep your operating system and applications updated.Use a strong device password or PIN.Activate fingerprint or facial authentication where available.Install applications only from official sources.Avoid suspicious browser extensions.Use reputable antivirus and security software.Never install unknown trading software or files sent by strangers.Avoid logging into financial accounts through public or untrusted computers.Never give remote access to your computer to someone claiming to be technical support.
A compromised device can expose even very strong passwords.
🎣 7. LEARN TO RECOGNIZE PHISHING ATTACKS
One of the biggest threats to traders is phishing.
Phishing is when someone impersonates a legitimate company, exchange, support agent, or individual to trick you into revealing confidential information.
Common examples include:
Fake Binance login pages.Messages claiming your account will be suspended.Fake customer support representatives.Messages promising free cryptocurrency or rewards.Fake investment opportunities.Suspicious links asking you to verify your wallet.Fake applications and browser extensions.
Protect yourself:
Never click suspicious links.Always verify the website address before logging in.Access exchanges through official bookmarks or manually verified websites.Never share passwords, 2FA codes, recovery codes, or private keys.Remember that legitimate support staff should never ask you to disclose your password or authentication codes.
A professional-looking message does not mean it is legitimate.
🔑 8. PROTECT YOUR RECOVERY CODES AND PRIVATE KEYS
When activating an authenticator, passkey, or hardware security key, you may receive backup or recovery information.
Protect it carefully.
Store recovery codes in a secure offline location.Never send them through social media or messaging applications.Never store private keys or seed phrases in ordinary notes or screenshots.Do not share your wallet's recovery phrase with anyone.Keep secure backups of your authenticator recovery information.
Losing access to your recovery information can make account recovery extremely difficult.
📞 9. PROTECT YOUR PHONE NUMBER AGAINST SIM SWAPPING
SIM swapping happens when criminals convince or manipulate a mobile carrier into transferring your phone number to another SIM card.
This can allow them to receive SMS verification codes intended for you.
To reduce this risk:
Contact your mobile provider and ask about SIM-swap protection.Set a carrier account PIN or port-out lock if available.Secure your mobile provider account with a unique password.Avoid using SMS as your primary authentication method when stronger alternatives are available.
🔍 10. REGULARLY AUDIT YOUR ACCOUNT SECURITY
Do not secure your accounts once and forget about them.
Make security checks part of your routine.
Review:
Active login sessions.Recognized devices.Recent account activity.Connected third-party applications.API permissions.Withdrawal addresses.Recovery email addresses and phone numbers.Password breach alerts.
Remove anything unfamiliar or unnecessary.
⚠️ YOUR TRADER SECURITY CHECKLIST
Before you continue trading, make sure you have completed these steps:
☐ Changed all weak, reused, or compromised passwords.
☐ Created unique passwords of at least 16 characters.
☐ Started using a reputable password manager.
☐ Activated 2FA on all important accounts.
☐ Enabled passkeys or hardware security keys wherever possible.
☐ Secured my primary email account.
☐ Enabled exchange anti-phishing protection.
☐ Activated withdrawal address whitelisting.
☐ Reviewed trusted devices and active sessions.
☐ Removed unused API keys and restricted API permissions.
☐ Secured my phone and computer.
☐ Stored recovery codes securely.
☐ Learned how to recognize phishing attempts.
☐ Protected my phone number against SIM swapping.
🚨 FINAL MESSAGE TO ALL TRADERS
You spend hours analyzing charts, studying market structure, managing risk, and protecting your trading capital.
But what is the point of having a profitable trading strategy if you neglect the security of the accounts holding your money?
Account security is part of risk management.
Do not assume you are too small to become a target. Cybercriminals do not necessarily target only wealthy individuals or large accounts. Anyone with valuable account access can become a target.
Take 30–60 minutes today and review your security settings. Change weak passwords, activate additional authentication, and secure your devices.
Do not wait for a security breach to teach you the importance of cybersecurity.
Protect your capital. Protect your identity. Protect your accounts.
Stay alert. Stay secure. Trade responsibly.
— ARVO
I am currently watching these top gainers: $AKE $SHELL $TAC
#CyberSecurity #TradingSecurity101 #CryptoSecurity #Binancesecurity #AccountProtection
🔐 THE ULTIMATE CYBERSECURITY CHECKLIST EVERY TRADER MUST FOLLOW
Protect your passwords. Activate 2FA. Secure your capital.
Your trading account is not just another online account. It may contain your capital, personal information, transaction history, and access to your financial assets.
One weak password, one phishing link, or one compromised email account could put everything at risk.
Every trader should take account security seriously. Do not wait until you lose access to your funds to start protecting yourself.
Below is a complete security checklist every trader should follow.
🔐 1. WHAT IS A WEAK PASSWORD?
A weak password is any password that is easy to guess, predict, or discover through automated attacks or leaked databases.
Examples of weak passwords:
123456789password123Arvo123456Bitcoin2025Your name followed by your birth year.The same password you use across multiple websites.
Why are these dangerous?
Hackers use automated tools to test common passwords and credentials leaked from other websites. If you reuse one password across multiple platforms, a breach on one website could expose your other accounts.
What should you do?
Use passwords of at least 16 characters.Generate random, unique passwords for every account.Never reuse passwords.Never use your name, birthday, phone number, or predictable personal information.Use a reputable password manager to generate and store your passwords securely.
Remember: A password should be unique to one account, not shared across your digital life.
🔐 2. CHANGE YOUR EXISTING WEAK AND REUSED PASSWORDS
Do not delay this.
Start with your most important accounts:
Cryptocurrency exchanges (Binance, OKX, Bybit, etc.).Your primary email account.Trading platforms and brokerage accounts.Banking and financial accounts.Social media accounts.Cloud storage and other accounts containing personal information.
If you have reused the same password on multiple platforms, replace it with a different, randomly generated password on each one.
Also change passwords immediately if you suspect compromise or discover that they have appeared in a data breach.
🛡️ 3. ACTIVATE TWO-FACTOR AUTHENTICATION (2FA)
This is one of the most important security measures you can implement.
Two-factor authentication means that accessing your account requires an additional verification factor beyond your password.
Even if someone discovers your password, 2FA makes unauthorized access significantly more difficult.
Enable 2FA on every important platform that supports it.
Preferred security methods:
Passkeys: Use them wherever supported. They provide strong phishing-resistant authentication.Hardware security keys: Physical security devices such as YubiKeys offer excellent protection.Authenticator applications: Use a trusted authenticator app to generate time-based verification codes.SMS verification: Better than having no additional protection, but less secure than the options above because phone numbers can be targeted through SIM-swapping attacks.
Do not rely on your password alone.
📧 4. SECURE YOUR EMAIL ACCOUNT FIRST
Your email account is one of the most important parts of your digital security.
Think about it: If someone gains access to your email, they may be able to reset passwords, intercept security notifications, and attempt to access your other accounts.
Take these steps:
Create a strong, unique email password.Activate 2FA or a passkey.Review all logged-in devices and active sessions.Remove unknown devices.Check recovery email addresses and phone numbers.Review email forwarding rules and filters for anything you did not create.Never share email verification codes with anyone.
If your email is compromised, many of your other accounts could be at risk.
🚨 5. ACTIVATE ALL AVAILABLE EXCHANGE SECURITY FEATURES
If you trade cryptocurrency, securing your exchange account is essential.
For Binance and other exchanges, review the following settings:
A. Anti-Phishing Code
Activate your exchange's anti-phishing code if available.
This helps you distinguish genuine platform emails from fraudulent messages pretending to come from the exchange.
B. Withdrawal Address Whitelist
Enable withdrawal address whitelisting.
This restricts withdrawals to approved wallet addresses, adding another security barrier if your account is compromised.
C. Passkeys and 2FA
Activate available passkeys, authenticator verification, or hardware security keys.
D. Device Management
Regularly inspect your account's trusted devices and active sessions. Remove anything you do not recognize.
E. Login and Withdrawal Notifications
Enable security notifications so you can identify suspicious login attempts and account activity.
F. API Key Protection
If you use API connections for trading:
Delete unused API keys.Never share API keys or secret keys.Disable withdrawal permissions.Grant only the permissions you actually need.Restrict API access to trusted IP addresses whenever possible.Never paste API credentials into unknown websites or applications.
Your API credentials should be treated like your account password.
📱 6. SECURE YOUR PHONE AND COMPUTER
Your account security is only as strong as the devices you use to access it.
Follow these precautions:
Keep your operating system and applications updated.Use a strong device password or PIN.Activate fingerprint or facial authentication where available.Install applications only from official sources.Avoid suspicious browser extensions.Use reputable antivirus and security software.Never install unknown trading software or files sent by strangers.Avoid logging into financial accounts through public or untrusted computers.Never give remote access to your computer to someone claiming to be technical support.
A compromised device can expose even very strong passwords.
🎣 7. LEARN TO RECOGNIZE PHISHING ATTACKS
One of the biggest threats to traders is phishing.
Phishing is when someone impersonates a legitimate company, exchange, support agent, or individual to trick you into revealing confidential information.
Common examples include:
Fake Binance login pages.Messages claiming your account will be suspended.Fake customer support representatives.Messages promising free cryptocurrency or rewards.Fake investment opportunities.Suspicious links asking you to verify your wallet.Fake applications and browser extensions.
Protect yourself:
Never click suspicious links.Always verify the website address before logging in.Access exchanges through official bookmarks or manually verified websites.Never share passwords, 2FA codes, recovery codes, or private keys.Remember that legitimate support staff should never ask you to disclose your password or authentication codes.
A professional-looking message does not mean it is legitimate.
🔑 8. PROTECT YOUR RECOVERY CODES AND PRIVATE KEYS
When activating an authenticator, passkey, or hardware security key, you may receive backup or recovery information.
Protect it carefully.
Store recovery codes in a secure offline location.Never send them through social media or messaging applications.Never store private keys or seed phrases in ordinary notes or screenshots.Do not share your wallet's recovery phrase with anyone.Keep secure backups of your authenticator recovery information.
Losing access to your recovery information can make account recovery extremely difficult.
📞 9. PROTECT YOUR PHONE NUMBER AGAINST SIM SWAPPING
SIM swapping happens when criminals convince or manipulate a mobile carrier into transferring your phone number to another SIM card.
This can allow them to receive SMS verification codes intended for you.
To reduce this risk:
Contact your mobile provider and ask about SIM-swap protection.Set a carrier account PIN or port-out lock if available.Secure your mobile provider account with a unique password.Avoid using SMS as your primary authentication method when stronger alternatives are available.
🔍 10. REGULARLY AUDIT YOUR ACCOUNT SECURITY
Do not secure your accounts once and forget about them.
Make security checks part of your routine.
Review:
Active login sessions.Recognized devices.Recent account activity.Connected third-party applications.API permissions.Withdrawal addresses.Recovery email addresses and phone numbers.Password breach alerts.
Remove anything unfamiliar or unnecessary.
⚠️ YOUR TRADER SECURITY CHECKLIST
Before you continue trading, make sure you have completed these steps:
☐ Changed all weak, reused, or compromised passwords.
☐ Created unique passwords of at least 16 characters.
☐ Started using a reputable password manager.
☐ Activated 2FA on all important accounts.
☐ Enabled passkeys or hardware security keys wherever possible.
☐ Secured my primary email account.
☐ Enabled exchange anti-phishing protection.
☐ Activated withdrawal address whitelisting.
☐ Reviewed trusted devices and active sessions.
☐ Removed unused API keys and restricted API permissions.
☐ Secured my phone and computer.
☐ Stored recovery codes securely.
☐ Learned how to recognize phishing attempts.
☐ Protected my phone number against SIM swapping.
🚨 FINAL MESSAGE TO ALL TRADERS
You spend hours analyzing charts, studying market structure, managing risk, and protecting your trading capital.
But what is the point of having a profitable trading strategy if you neglect the security of the accounts holding your money?
Account security is part of risk management.
Do not assume you are too small to become a target. Cybercriminals do not necessarily target only wealthy individuals or large accounts. Anyone with valuable account access can become a target.
Take 30–60 minutes today and review your security settings. Change weak passwords, activate additional authentication, and secure your devices.
Do not wait for a security breach to teach you the importance of cybersecurity.
Protect your capital. Protect your identity. Protect your accounts.
Stay alert. Stay secure. Trade responsibly.
— ARVO
I am currently watching these top gainers: $AKE $SHELL $TAC
#CyberSecurity #TradingSecurity101 #CryptoSecurity #Binancesecurity #AccountProtection
452
·
--
AI Agents Can Be Tricked by the Data They Read
A webpage or document can contain hidden instructions telling an AI agent to ignore its task or expose information.
OpenAI describes this as prompt injection: untrusted text tries to override an agent’s intended instructions and may steer connected tools. Safer designs keep external text separate from privileged instructions, limit each agent to the data and tools it needs, constrain intermediate outputs to a schema, and require human approval for consequential actions. These layers reduce exposure, but they do not make agents foolproof—OpenAI warns they can still be tricked.
My takeaway: do not grant an AI agent broad access just because its prompt sounds careful. Which actions should always require a human check?
Source: OpenAI, “Safety in building agents” — https://developers.openai.com/api/docs/guides/agent-builder-safety
#AI #AIAgents #Cybersecurity
AI Agents Can Be Tricked by the Data They Read
A webpage or document can contain hidden instructions telling an AI agent to ignore its task or expose information.
OpenAI describes this as prompt injection: untrusted text tries to override an agent’s intended instructions and may steer connected tools. Safer designs keep external text separate from privileged instructions, limit each agent to the data and tools it needs, constrain intermediate outputs to a schema, and require human approval for consequential actions. These layers reduce exposure, but they do not make agents foolproof—OpenAI warns they can still be tricked.
My takeaway: do not grant an AI agent broad access just because its prompt sounds careful. Which actions should always require a human check?
Source: OpenAI, “Safety in building agents” — https://developers.openai.com/api/docs/guides/agent-builder-safety
#AI #AIAgents #Cybersecurity
A webpage or document can contain hidden instructions telling an AI agent to ignore its task or expose information.
OpenAI describes this as prompt injection: untrusted text tries to override an agent’s intended instructions and may steer connected tools. Safer designs keep external text separate from privileged instructions, limit each agent to the data and tools it needs, constrain intermediate outputs to a schema, and require human approval for consequential actions. These layers reduce exposure, but they do not make agents foolproof—OpenAI warns they can still be tricked.
My takeaway: do not grant an AI agent broad access just because its prompt sounds careful. Which actions should always require a human check?
Source: OpenAI, “Safety in building agents” — https://developers.openai.com/api/docs/guides/agent-builder-safety
#AI #AIAgents #Cybersecurity
64

·
--
📰 U.S. won court order to seize or restrain more than $1.2 billion in crypto stolen from Binance
U.S. and private-sector efforts have frozen more than $2.7 billion of the funds North Korean hackers took from the exchange
Source : Quartz
Time : 2026-11-13 13:30:27
Credit : cris tolomia
#tech_&_innovation #cybersecurity
Share your opinion in the comment section below
📰 U.S. won court order to seize or restrain more than $1.2 billion in crypto stolen from Binance
U.S. and private-sector efforts have frozen more than $2.7 billion of the funds North Korean hackers took from the exchange
Source : Quartz
Time : 2026-11-13 13:30:27
Credit : cris tolomia
#tech_&_innovation #cybersecurity
Share your opinion in the comment section below
U.S. and private-sector efforts have frozen more than $2.7 billion of the funds North Korean hackers took from the exchange
Source : Quartz
Time : 2026-11-13 13:30:27
Credit : cris tolomia
#tech_&_innovation #cybersecurity
Share your opinion in the comment section below
·
--
📰 U.S. won court order to seize or restrain more than $1.2 billion in crypto stolen from Binance
U.S. and private-sector efforts have frozen more than $2.7 billion of the funds North Korean hackers took from the exchange
Source : Quartz
Time : 2026-11-13 13:30:27
Credit : cris tolomia
#tech_&_innovation #cybersecurity
Share your opinion in the comment section below
📰 U.S. won court order to seize or restrain more than $1.2 billion in crypto stolen from Binance
U.S. and private-sector efforts have frozen more than $2.7 billion of the funds North Korean hackers took from the exchange
Source : Quartz
Time : 2026-11-13 13:30:27
Credit : cris tolomia
#tech_&_innovation #cybersecurity
Share your opinion in the comment section below
U.S. and private-sector efforts have frozen more than $2.7 billion of the funds North Korean hackers took from the exchange
Source : Quartz
Time : 2026-11-13 13:30:27
Credit : cris tolomia
#tech_&_innovation #cybersecurity
Share your opinion in the comment section below
1
1
·
--
**Hackers tried to sell 46,000 TSMC employee records for Bitcoin – the leak is real.**
• TSMC confirmed personal data of current and former staff appeared on DarkForums and BreachForums, with sellers demanding 3 Bitcoin.
• Exposed fields include names, national ID numbers and bank account details; the company says no breach of its own systems or customer data was detected.
• TSMC is notifying affected individuals and working with a cloud service provider, cybersecurity firms and law enforcement to trace the source.
What steps should organizations take when a leak originates from a third‑party cloud provider?
#CyberSecurity #DataPrivacy #TSMC #Bitcoin #FinTech
**Hackers tried to sell 46,000 TSMC employee records for Bitcoin – the leak is real.**
• TSMC confirmed personal data of current and former staff appeared on DarkForums and BreachForums, with sellers demanding 3 Bitcoin.
• Exposed fields include names, national ID numbers and bank account details; the company says no breach of its own systems or customer data was detected.
• TSMC is notifying affected individuals and working with a cloud service provider, cybersecurity firms and law enforcement to trace the source.
What steps should organizations take when a leak originates from a third‑party cloud provider?
#CyberSecurity #DataPrivacy #TSMC #Bitcoin #FinTech
• TSMC confirmed personal data of current and former staff appeared on DarkForums and BreachForums, with sellers demanding 3 Bitcoin.
• Exposed fields include names, national ID numbers and bank account details; the company says no breach of its own systems or customer data was detected.
• TSMC is notifying affected individuals and working with a cloud service provider, cybersecurity firms and law enforcement to trace the source.
What steps should organizations take when a leak originates from a third‑party cloud provider?
#CyberSecurity #DataPrivacy #TSMC #Bitcoin #FinTech
70
·
--
Article
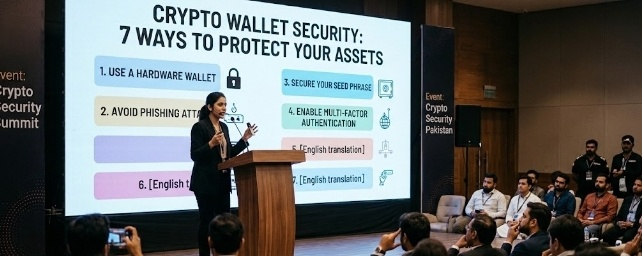
🔐 Crypto Wallet Security: 7 Ways to Protect Your Cryptocurrency from Hackers{spot}(BTCUSDT)
Cryptocurrency gives people greater control over their digital assets, but that freedom also comes with responsibility. Unlike traditional banking systems, cryptocurrency transactions are generally irreversible. If someone gains access to your wallet and transfers your funds, recovering them can be extremely difficult.
Whether you are new to Bitcoin or already exploring Web3, understanding crypto wallet security is essential
Let's explore seven practical ways to protect your cryptocurrency.
1. Never Share Your Seed Phrase
Your seed phrase is one of the most important parts of your crypto wallet. It can provide access to your funds, even if you lose your device.
Remember:
Never share your seed phrase with anyone.Never send it through messages or email.Never enter it on suspicious websites.Keep a secure offline backup.
Important: Legitimate support teams should never ask you to reveal your recovery phrase
2. Enable Two-Factor Authentication (2FA)
Two-factor authentication adds another security layer to your accounts
Even if someone discovers your password, they may still need a second verification method
Whenever available:
Enable 2FA.Prefer an authenticator app or security key.Protect your email account with strong security.
3. Use Strong and Unique Passwords
Using the same password across multiple platforms increases your risk.
Create a unique password for every important crypto-related account.A password manager can help you generate and securely store complex passwords.Avoid using:
Your name or birthday.Simple number combinations.Passwords reused from social media accounts.
4. Be Careful With Fake Websites and Links
Phishing attacks are common in the cryptocurrency ecosystem.
Scammers may create websites that look almost identical to legitimate exchanges, wallet applications, or blockchain platforms.
Before connecting your wallet:
Check the website address carefully.Avoid suspicious links.Bookmark official websites.Never approve unexpected wallet requests.
One wrong click can put your digital assets at risk.
5. Consider a Hardware Wallet
A hardware wallet stores private keys in a dedicated physical device.
For people holding cryptocurrency over the long term, this can provide an additional security layer.
However, hardware wallets still require careful handling.
Purchase devices through trusted official channels and protect your recovery phrase separately.
6. Review Wallet Permissions Regularly
When interacting with decentralized applications (dApps), you may grant permissions to access or interact with your tokens.
Some permissions can remain active even after you stop using an application.
Make it a habit to:
Review connected applications.Check token approvals.Revoke unnecessary permissions.Avoid interacting with unfamiliar smart contracts.
7. Never Trust Guaranteed Profit Offers
Crypto scammers frequently use promises of guaranteed returns, fake giveaways, and investment opportunities to attract victims.
Be suspicious of anyone asking you to send cryptocurrency first in exchange for a larger payment.Remember that genuine cryptocurrency education focuses on understanding risks, not promising profits.
Final Thoughts
Cryptocurrency security is not just about choosing the right wallet. It is about developing responsible digital habits.Protect your seed phrase, use strong authentication, verify websites, review wallet permissions, and stay informed about new threats.The best security strategy is prevention.
Your cryptocurrency is only as secure as the habits you develop to protect it.
💬 Let's Discuss
What do you think is the biggest security threat for cryptocurrency beginners: phishing attacks, stolen passwords, fake investment offers, or exposed seed phrases
Share your thoughts in the comments!
#BinanceSquare #USPPIMissMayEaseBTCPressure #CryptoEducation💡🚀 #USPPIMissMayEaseBTCPressure #CyberSecurity
{spot}(BNBUSDT)
S
{etf_us}(SLON.ETF)
🔐 Crypto Wallet Security: 7 Ways to Protect Your Cryptocurrency from Hackers
Cryptocurrency gives people greater control over their digital assets, but that freedom also comes with responsibility. Unlike traditional banking systems, cryptocurrency transactions are generally irreversible. If someone gains access to your wallet and transfers your funds, recovering them can be extremely difficult.
Whether you are new to Bitcoin or already exploring Web3, understanding crypto wallet security is essential
Let's explore seven practical ways to protect your cryptocurrency.
1. Never Share Your Seed Phrase
Your seed phrase is one of the most important parts of your crypto wallet. It can provide access to your funds, even if you lose your device.
Remember:
Never share your seed phrase with anyone.Never send it through messages or email.Never enter it on suspicious websites.Keep a secure offline backup.
Important: Legitimate support teams should never ask you to reveal your recovery phrase
2. Enable Two-Factor Authentication (2FA)
Two-factor authentication adds another security layer to your accounts
Even if someone discovers your password, they may still need a second verification method
Whenever available:
Enable 2FA.Prefer an authenticator app or security key.Protect your email account with strong security.
3. Use Strong and Unique Passwords
Using the same password across multiple platforms increases your risk.
Create a unique password for every important crypto-related account.A password manager can help you generate and securely store complex passwords.Avoid using:
Your name or birthday.Simple number combinations.Passwords reused from social media accounts.
4. Be Careful With Fake Websites and Links
Phishing attacks are common in the cryptocurrency ecosystem.
Scammers may create websites that look almost identical to legitimate exchanges, wallet applications, or blockchain platforms.
Before connecting your wallet:
Check the website address carefully.Avoid suspicious links.Bookmark official websites.Never approve unexpected wallet requests.
One wrong click can put your digital assets at risk.
5. Consider a Hardware Wallet
A hardware wallet stores private keys in a dedicated physical device.
For people holding cryptocurrency over the long term, this can provide an additional security layer.
However, hardware wallets still require careful handling.
Purchase devices through trusted official channels and protect your recovery phrase separately.
6. Review Wallet Permissions Regularly
When interacting with decentralized applications (dApps), you may grant permissions to access or interact with your tokens.
Some permissions can remain active even after you stop using an application.
Make it a habit to:
Review connected applications.Check token approvals.Revoke unnecessary permissions.Avoid interacting with unfamiliar smart contracts.
7. Never Trust Guaranteed Profit Offers
Crypto scammers frequently use promises of guaranteed returns, fake giveaways, and investment opportunities to attract victims.
Be suspicious of anyone asking you to send cryptocurrency first in exchange for a larger payment.Remember that genuine cryptocurrency education focuses on understanding risks, not promising profits.
Final Thoughts
Cryptocurrency security is not just about choosing the right wallet. It is about developing responsible digital habits.Protect your seed phrase, use strong authentication, verify websites, review wallet permissions, and stay informed about new threats.The best security strategy is prevention.
Your cryptocurrency is only as secure as the habits you develop to protect it.
💬 Let's Discuss
What do you think is the biggest security threat for cryptocurrency beginners: phishing attacks, stolen passwords, fake investment offers, or exposed seed phrases
Share your thoughts in the comments!
#BinanceSquare #USPPIMissMayEaseBTCPressure #CryptoEducation💡🚀 #USPPIMissMayEaseBTCPressure #CyberSecurity
S
Whether you are new to Bitcoin or already exploring Web3, understanding crypto wallet security is essential
Let's explore seven practical ways to protect your cryptocurrency.
1. Never Share Your Seed Phrase
Your seed phrase is one of the most important parts of your crypto wallet. It can provide access to your funds, even if you lose your device.
Remember:
Never share your seed phrase with anyone.Never send it through messages or email.Never enter it on suspicious websites.Keep a secure offline backup.
Important: Legitimate support teams should never ask you to reveal your recovery phrase
2. Enable Two-Factor Authentication (2FA)
Two-factor authentication adds another security layer to your accounts
Even if someone discovers your password, they may still need a second verification method
Whenever available:
Enable 2FA.Prefer an authenticator app or security key.Protect your email account with strong security.
3. Use Strong and Unique Passwords
Using the same password across multiple platforms increases your risk.
Create a unique password for every important crypto-related account.A password manager can help you generate and securely store complex passwords.Avoid using:
Your name or birthday.Simple number combinations.Passwords reused from social media accounts.
4. Be Careful With Fake Websites and Links
Phishing attacks are common in the cryptocurrency ecosystem.
Scammers may create websites that look almost identical to legitimate exchanges, wallet applications, or blockchain platforms.
Before connecting your wallet:
Check the website address carefully.Avoid suspicious links.Bookmark official websites.Never approve unexpected wallet requests.
One wrong click can put your digital assets at risk.
5. Consider a Hardware Wallet
A hardware wallet stores private keys in a dedicated physical device.
For people holding cryptocurrency over the long term, this can provide an additional security layer.
However, hardware wallets still require careful handling.
Purchase devices through trusted official channels and protect your recovery phrase separately.
6. Review Wallet Permissions Regularly
When interacting with decentralized applications (dApps), you may grant permissions to access or interact with your tokens.
Some permissions can remain active even after you stop using an application.
Make it a habit to:
Review connected applications.Check token approvals.Revoke unnecessary permissions.Avoid interacting with unfamiliar smart contracts.
7. Never Trust Guaranteed Profit Offers
Crypto scammers frequently use promises of guaranteed returns, fake giveaways, and investment opportunities to attract victims.
Be suspicious of anyone asking you to send cryptocurrency first in exchange for a larger payment.Remember that genuine cryptocurrency education focuses on understanding risks, not promising profits.
Final Thoughts
Cryptocurrency security is not just about choosing the right wallet. It is about developing responsible digital habits.Protect your seed phrase, use strong authentication, verify websites, review wallet permissions, and stay informed about new threats.The best security strategy is prevention.
Your cryptocurrency is only as secure as the habits you develop to protect it.
💬 Let's Discuss
What do you think is the biggest security threat for cryptocurrency beginners: phishing attacks, stolen passwords, fake investment offers, or exposed seed phrases
Share your thoughts in the comments!
#BinanceSquare #USPPIMissMayEaseBTCPressure #CryptoEducation💡🚀 #USPPIMissMayEaseBTCPressure #CyberSecurity
S
118

BINANCE’S $6.3 BILLION SECURITY LESSON: SIMILAR CYBER WEAKNESSES ARE TARGETING EUROPEAN BANKS#CyberSecurity 🌍 #PositiveMindsGlobalResults
BINANCE SQUARE | INVEST • LEARN • GROW • TOGETHER
Stay positive. Stay informed. Stay secure! 💛🌍
BINANCE’S $6.3 BILLION SECURITY LESSON: SIMILAR CYBER WEAKNESSES ARE TARGETING EUROPEAN BANKS
Key message: The security risks highlighted by the reported Binance incident may extend beyond cryptocurrency exchanges. European banks are also facing growing cyber threats involving compromised devices, employee access, phishing and sophisticated social-engineering attacks.
What happened?
Binance incident: The reported October 29 cyberattack involved compromised employee devices, malicious software and weaknesses in internal security controls. The reported losses reached $6.3 billion.European banking concern: French lender Crédit Mutuel Arkéa disclosed a cyberattack involving approximately €100 million ($112 million) in stolen funds. Investigators and experts highlighted weaknesses involving third-party transaction access and internal safeguards.Wider financial risk: The incidents highlight how attackers can exploit trusted employees, compromised credentials and inadequate transaction controls to target financial institutions.
Why this matters
Cybersecurity is no longer just a cryptocurrency exchange issue. Traditional banks, payment providers and digital asset platforms all need stronger employee protection, access restrictions, transaction monitoring and rapid threat detection.
What financial institutions should prioritize
Strengthen employee device security and malware detection.Introduce multi-person approval for high-value transactions.Restrict third-party access and apply strict identity verification.Monitor unusual withdrawals and suspicious transaction patterns.Improve AI-powered cybersecurity and incident-response systems.
Market and industry outlook: These incidents could increase pressure on financial institutions to invest in cybersecurity, strengthen regulatory compliance and demonstrate greater transparency. However, they do not establish that every European bank faces the same vulnerabilities.
Key takeaway: The biggest lesson from the Binance and Crédit Mutuel Arkéa incidents is that protecting financial assets requires more than securing wallets and computer networks. Employee access, trusted third parties and transaction approval systems are equally important.
Disclaimer: This article is for educational and informational purposes only. Reported incidents and financial figures should be interpreted in the context of verified disclosures. This is not financial advice.
#CyberSecurity #Binance #EuropeanBanks #FinancialSecurity #CryptoSecurity #DigitalBanking #PositiveMindsGlobalResults
BINANCE’S $6.3 BILLION SECURITY LESSON: SIMILAR CYBER WEAKNESSES ARE TARGETING EUROPEAN BANKS
#CyberSecurity 🌍 #PositiveMindsGlobalResults
BINANCE SQUARE | INVEST • LEARN • GROW • TOGETHER
Stay positive. Stay informed. Stay secure! 💛🌍
BINANCE’S $6.3 BILLION SECURITY LESSON: SIMILAR CYBER WEAKNESSES ARE TARGETING EUROPEAN BANKS
Key message: The security risks highlighted by the reported Binance incident may extend beyond cryptocurrency exchanges. European banks are also facing growing cyber threats involving compromised devices, employee access, phishing and sophisticated social-engineering attacks.
What happened?
Binance incident: The reported October 29 cyberattack involved compromised employee devices, malicious software and weaknesses in internal security controls. The reported losses reached $6.3 billion.European banking concern: French lender Crédit Mutuel Arkéa disclosed a cyberattack involving approximately €100 million ($112 million) in stolen funds. Investigators and experts highlighted weaknesses involving third-party transaction access and internal safeguards.Wider financial risk: The incidents highlight how attackers can exploit trusted employees, compromised credentials and inadequate transaction controls to target financial institutions.
Why this matters
Cybersecurity is no longer just a cryptocurrency exchange issue. Traditional banks, payment providers and digital asset platforms all need stronger employee protection, access restrictions, transaction monitoring and rapid threat detection.
What financial institutions should prioritize
Strengthen employee device security and malware detection.Introduce multi-person approval for high-value transactions.Restrict third-party access and apply strict identity verification.Monitor unusual withdrawals and suspicious transaction patterns.Improve AI-powered cybersecurity and incident-response systems.
Market and industry outlook: These incidents could increase pressure on financial institutions to invest in cybersecurity, strengthen regulatory compliance and demonstrate greater transparency. However, they do not establish that every European bank faces the same vulnerabilities.
Key takeaway: The biggest lesson from the Binance and Crédit Mutuel Arkéa incidents is that protecting financial assets requires more than securing wallets and computer networks. Employee access, trusted third parties and transaction approval systems are equally important.
Disclaimer: This article is for educational and informational purposes only. Reported incidents and financial figures should be interpreted in the context of verified disclosures. This is not financial advice.
#CyberSecurity #Binance #EuropeanBanks #FinancialSecurity #CryptoSecurity #DigitalBanking #PositiveMindsGlobalResults
BINANCE SQUARE | INVEST • LEARN • GROW • TOGETHER
Stay positive. Stay informed. Stay secure! 💛🌍
BINANCE’S $6.3 BILLION SECURITY LESSON: SIMILAR CYBER WEAKNESSES ARE TARGETING EUROPEAN BANKS
Key message: The security risks highlighted by the reported Binance incident may extend beyond cryptocurrency exchanges. European banks are also facing growing cyber threats involving compromised devices, employee access, phishing and sophisticated social-engineering attacks.
What happened?
Binance incident: The reported October 29 cyberattack involved compromised employee devices, malicious software and weaknesses in internal security controls. The reported losses reached $6.3 billion.European banking concern: French lender Crédit Mutuel Arkéa disclosed a cyberattack involving approximately €100 million ($112 million) in stolen funds. Investigators and experts highlighted weaknesses involving third-party transaction access and internal safeguards.Wider financial risk: The incidents highlight how attackers can exploit trusted employees, compromised credentials and inadequate transaction controls to target financial institutions.
Why this matters
Cybersecurity is no longer just a cryptocurrency exchange issue. Traditional banks, payment providers and digital asset platforms all need stronger employee protection, access restrictions, transaction monitoring and rapid threat detection.
What financial institutions should prioritize
Strengthen employee device security and malware detection.Introduce multi-person approval for high-value transactions.Restrict third-party access and apply strict identity verification.Monitor unusual withdrawals and suspicious transaction patterns.Improve AI-powered cybersecurity and incident-response systems.
Market and industry outlook: These incidents could increase pressure on financial institutions to invest in cybersecurity, strengthen regulatory compliance and demonstrate greater transparency. However, they do not establish that every European bank faces the same vulnerabilities.
Key takeaway: The biggest lesson from the Binance and Crédit Mutuel Arkéa incidents is that protecting financial assets requires more than securing wallets and computer networks. Employee access, trusted third parties and transaction approval systems are equally important.
Disclaimer: This article is for educational and informational purposes only. Reported incidents and financial figures should be interpreted in the context of verified disclosures. This is not financial advice.
#CyberSecurity #Binance #EuropeanBanks #FinancialSecurity #CryptoSecurity #DigitalBanking #PositiveMindsGlobalResults
13
·
--
Bearish
#bitcoincoredisclosestortrafficvulnerability
🚨 Bitcoin Core Reveals Tor Traffic Vulnerability — Could User Privacy Be at Risk?
Bitcoin Core has disclosed a vulnerability involving Tor traffic, raising fresh concerns about privacy and network security across the Bitcoin ecosystem.
Tor is widely used by Bitcoin node operators to help hide their IP addresses and protect their network activity. A weakness affecting Tor-related traffic could potentially expose information that users expect to remain private.
Why It Matters:
Privacy concerns: Users relying on Tor could face additional risks if they run vulnerable software.
Node security: Bitcoin node operators should pay attention to security disclosures and recommended updates.
Network trust: Privacy remains an important part of Bitcoin's decentralized infrastructure.
My Take: This is a reminder that Bitcoin security requires continuous maintenance. Node operators should review the official vulnerability disclosure and apply recommended updates rather than ignore potential risks.
Could this vulnerability weaken confidence in Bitcoin's privacy infrastructure?
#bitcoin #BitcoinCorrection #CyberSecurity $BTC
#bitcoincoredisclosestortrafficvulnerability
🚨 Bitcoin Core Reveals Tor Traffic Vulnerability — Could User Privacy Be at Risk?
Bitcoin Core has disclosed a vulnerability involving Tor traffic, raising fresh concerns about privacy and network security across the Bitcoin ecosystem.
Tor is widely used by Bitcoin node operators to help hide their IP addresses and protect their network activity. A weakness affecting Tor-related traffic could potentially expose information that users expect to remain private.
Why It Matters:
Privacy concerns: Users relying on Tor could face additional risks if they run vulnerable software.
Node security: Bitcoin node operators should pay attention to security disclosures and recommended updates.
Network trust: Privacy remains an important part of Bitcoin's decentralized infrastructure.
My Take: This is a reminder that Bitcoin security requires continuous maintenance. Node operators should review the official vulnerability disclosure and apply recommended updates rather than ignore potential risks.
Could this vulnerability weaken confidence in Bitcoin's privacy infrastructure?
#bitcoin #BitcoinCorrection #CyberSecurity $BTC
🚨 Bitcoin Core Reveals Tor Traffic Vulnerability — Could User Privacy Be at Risk?
Bitcoin Core has disclosed a vulnerability involving Tor traffic, raising fresh concerns about privacy and network security across the Bitcoin ecosystem.
Tor is widely used by Bitcoin node operators to help hide their IP addresses and protect their network activity. A weakness affecting Tor-related traffic could potentially expose information that users expect to remain private.
Why It Matters:
Privacy concerns: Users relying on Tor could face additional risks if they run vulnerable software.
Node security: Bitcoin node operators should pay attention to security disclosures and recommended updates.
Network trust: Privacy remains an important part of Bitcoin's decentralized infrastructure.
My Take: This is a reminder that Bitcoin security requires continuous maintenance. Node operators should review the official vulnerability disclosure and apply recommended updates rather than ignore potential risks.
Could this vulnerability weaken confidence in Bitcoin's privacy infrastructure?
#bitcoin #BitcoinCorrection #CyberSecurity $BTC
37
·
--
Disconnecting Isn’t the Same as Revoking Wallet Permissions
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
Disconnecting Isn’t the Same as Revoking Wallet Permissions
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
4
·
--
A fake video-call “fix” can turn a routine meeting into a crypto-theft trap.
The FBI says the North Korean-linked FaceStealer operation was tied to more than $400 million in crypto theft over 18 months. Attackers used compromised contacts and convincing video meetings, then a bogus technical-error fix to install malware. The FBI also warns of deepfakes and targeting of open-source developers—raising software supply-chain risks.
My takeaway: treat unexpected fix links as suspicious, even from a familiar account. Verify the request through a separate trusted channel before clicking.
Would your team recognize this in a routine call?
Source: FBI — https://www.fbi.gov/investigate/cyber/facestealer-cryptocurrency-theft-scheme
#Cybersecurity #CryptoSecurity #Web3 #Phishing
A fake video-call “fix” can turn a routine meeting into a crypto-theft trap.
The FBI says the North Korean-linked FaceStealer operation was tied to more than $400 million in crypto theft over 18 months. Attackers used compromised contacts and convincing video meetings, then a bogus technical-error fix to install malware. The FBI also warns of deepfakes and targeting of open-source developers—raising software supply-chain risks.
My takeaway: treat unexpected fix links as suspicious, even from a familiar account. Verify the request through a separate trusted channel before clicking.
Would your team recognize this in a routine call?
Source: FBI — https://www.fbi.gov/investigate/cyber/facestealer-cryptocurrency-theft-scheme
#Cybersecurity #CryptoSecurity #Web3 #Phishing
The FBI says the North Korean-linked FaceStealer operation was tied to more than $400 million in crypto theft over 18 months. Attackers used compromised contacts and convincing video meetings, then a bogus technical-error fix to install malware. The FBI also warns of deepfakes and targeting of open-source developers—raising software supply-chain risks.
My takeaway: treat unexpected fix links as suspicious, even from a familiar account. Verify the request through a separate trusted channel before clicking.
Would your team recognize this in a routine call?
Source: FBI — https://www.fbi.gov/investigate/cyber/facestealer-cryptocurrency-theft-scheme
#Cybersecurity #CryptoSecurity #Web3 #Phishing
3
·
--
TSMC Employee Data Appeared Online—But the Company Says Its Systems Were Not Breached
A cloud-provider exposure can still create serious privacy risks, even without disrupting chip production.
In a Nov. 12 SEC filing, TSMC said some current and former employees’ data appeared online without authorization. It found no evidence its own systems were compromised; the data matched information held by a cloud-service provider and was unrelated to operations or customer data. Separately, CNBC-TV18 reports hackers claimed about 46,000 records and demanded 3 BTC—claims not confirmed by TSMC.
My takeaway: verify breach details through company filings, and treat criminals’ data-volume or ransom claims cautiously. What security standards should companies require from cloud vendors?
Sources: TSMC SEC filing — https://www.sec.gov/Archives/edgar/data/1046179/000104617926000800/a20261112statementregardin.htm | CNBC-TV18 — https://www.cnbctv18.com/technology/tsmc-confirms-employee-data-leak-hackers-demand-3-bitcoin-for-46000-records-20033178.htm
#Cybersecurity #DataPrivacy #Semiconductors
TSMC Employee Data Appeared Online—But the Company Says Its Systems Were Not Breached
A cloud-provider exposure can still create serious privacy risks, even without disrupting chip production.
In a Nov. 12 SEC filing, TSMC said some current and former employees’ data appeared online without authorization. It found no evidence its own systems were compromised; the data matched information held by a cloud-service provider and was unrelated to operations or customer data. Separately, CNBC-TV18 reports hackers claimed about 46,000 records and demanded 3 BTC—claims not confirmed by TSMC.
My takeaway: verify breach details through company filings, and treat criminals’ data-volume or ransom claims cautiously. What security standards should companies require from cloud vendors?
Sources: TSMC SEC filing — https://www.sec.gov/Archives/edgar/data/1046179/000104617926000800/a20261112statementregardin.htm | CNBC-TV18 — https://www.cnbctv18.com/technology/tsmc-confirms-employee-data-leak-hackers-demand-3-bitcoin-for-46000-records-20033178.htm
#Cybersecurity #DataPrivacy #Semiconductors
A cloud-provider exposure can still create serious privacy risks, even without disrupting chip production.
In a Nov. 12 SEC filing, TSMC said some current and former employees’ data appeared online without authorization. It found no evidence its own systems were compromised; the data matched information held by a cloud-service provider and was unrelated to operations or customer data. Separately, CNBC-TV18 reports hackers claimed about 46,000 records and demanded 3 BTC—claims not confirmed by TSMC.
My takeaway: verify breach details through company filings, and treat criminals’ data-volume or ransom claims cautiously. What security standards should companies require from cloud vendors?
Sources: TSMC SEC filing — https://www.sec.gov/Archives/edgar/data/1046179/000104617926000800/a20261112statementregardin.htm | CNBC-TV18 — https://www.cnbctv18.com/technology/tsmc-confirms-employee-data-leak-hackers-demand-3-bitcoin-for-46000-records-20033178.htm
#Cybersecurity #DataPrivacy #Semiconductors
31
·
--
🚨 DOJ SEIZES $1.2 BILLION IN CRYPTO LINKED TO NORTH KOREA!
The U.S. Justice Department has secured court authorization to seize or freeze over $1.2 BILLION in crypto stolen from Binance.
🔹 More than $2.7 billion of the roughly $6 billion stolen has now been frozen.
🔹 The FBI also disrupted North Korea’s FaceStealer operation, linked to over $400 million in crypto thefts over 18 months.
🔹 Investigators seized more than 900 webcam recordings of victims.
🔹 Hackers reportedly used recorded footage and AI deepfakes to impersonate trusted contacts during video calls.
⚠️ Some victims were targeted months—or even over a year—before their funds were stolen.
💬 Does this show how serious AI-powered scams have become for the crypto industry?
$BNB $BTC $XAU
#CryptoSecurity #Binance #DOJ #FBI #NorthKorea #CyberSecurity #CryptoNews
🚨 DOJ SEIZES $1.2 BILLION IN CRYPTO LINKED TO NORTH KOREA!
The U.S. Justice Department has secured court authorization to seize or freeze over $1.2 BILLION in crypto stolen from Binance.
🔹 More than $2.7 billion of the roughly $6 billion stolen has now been frozen.
🔹 The FBI also disrupted North Korea’s FaceStealer operation, linked to over $400 million in crypto thefts over 18 months.
🔹 Investigators seized more than 900 webcam recordings of victims.
🔹 Hackers reportedly used recorded footage and AI deepfakes to impersonate trusted contacts during video calls.
⚠️ Some victims were targeted months—or even over a year—before their funds were stolen.
💬 Does this show how serious AI-powered scams have become for the crypto industry?
$BNB $BTC $XAU
#CryptoSecurity #Binance #DOJ #FBI #NorthKorea #CyberSecurity #CryptoNews
The U.S. Justice Department has secured court authorization to seize or freeze over $1.2 BILLION in crypto stolen from Binance.
🔹 More than $2.7 billion of the roughly $6 billion stolen has now been frozen.
🔹 The FBI also disrupted North Korea’s FaceStealer operation, linked to over $400 million in crypto thefts over 18 months.
🔹 Investigators seized more than 900 webcam recordings of victims.
🔹 Hackers reportedly used recorded footage and AI deepfakes to impersonate trusted contacts during video calls.
⚠️ Some victims were targeted months—or even over a year—before their funds were stolen.
💬 Does this show how serious AI-powered scams have become for the crypto industry?
$BNB $BTC $XAU
#CryptoSecurity #Binance #DOJ #FBI #NorthKorea #CyberSecurity #CryptoNews
1
3
16

The DOJ is moving to seize $1.2B following the Binance hack while North Korean actors utilize AI deepfakes to steal $400M in crypto assets.
#CyberSecurity #DOJ
The DOJ is moving to seize $1.2B following the Binance hack while North Korean actors utilize AI deepfakes to steal $400M in crypto assets.
#CyberSecurity #DOJ
#CyberSecurity #DOJ
8
·
--
🚨 North Korean Hackers Mint Custom Memecoins to Wash Binance Hack Loot!
Blockchain analytics firm Elliptic has uncovered a new obfuscation tactic following the historical $6.3B $BNB heist: state-sponsored North Korean actors created six custom memecoins on the NEAR Protocol to launder stolen assets.
{future}(BNBUSDT)
🔑 Key Takeaways:
>> The Method: Hackers minted 6 self-created memecoins on NEAR DEXs, using one set of controlled wallets to buy the tokens with stolen $NEAR and a second set to sell them back for real crypto assets—disguising stolen loot as "trading profits."
{future}(NEARUSDT)
>> The Volume: Approximately 117,000 $NEAR (valued at ~$430,000) was routed through these liquidity pools between Nov 5–7.
>> On-Chain Trail: Elliptic notes this tactic is designed to delay tracing rather than conceal it completely, creating multiple cheap transactional "layers" to slow down investigators.
As bad actors continuously shift strategies, active on-chain surveillance remains critical for tracking stolen funds across DEX ecosystems.
#writetoearn #Binance #CryptoNews #CyberSecurity #Web3
🚨 North Korean Hackers Mint Custom Memecoins to Wash Binance Hack Loot!
Blockchain analytics firm Elliptic has uncovered a new obfuscation tactic following the historical $6.3B $BNB heist: state-sponsored North Korean actors created six custom memecoins on the NEAR Protocol to launder stolen assets.
🔑 Key Takeaways:
>> The Method: Hackers minted 6 self-created memecoins on NEAR DEXs, using one set of controlled wallets to buy the tokens with stolen $NEAR and a second set to sell them back for real crypto assets—disguising stolen loot as "trading profits."
>> The Volume: Approximately 117,000 $NEAR (valued at ~$430,000) was routed through these liquidity pools between Nov 5–7.
>> On-Chain Trail: Elliptic notes this tactic is designed to delay tracing rather than conceal it completely, creating multiple cheap transactional "layers" to slow down investigators.
As bad actors continuously shift strategies, active on-chain surveillance remains critical for tracking stolen funds across DEX ecosystems.
#writetoearn #Binance #CryptoNews #CyberSecurity #Web3
Blockchain analytics firm Elliptic has uncovered a new obfuscation tactic following the historical $6.3B $BNB heist: state-sponsored North Korean actors created six custom memecoins on the NEAR Protocol to launder stolen assets.
🔑 Key Takeaways:
>> The Method: Hackers minted 6 self-created memecoins on NEAR DEXs, using one set of controlled wallets to buy the tokens with stolen $NEAR and a second set to sell them back for real crypto assets—disguising stolen loot as "trading profits."
>> The Volume: Approximately 117,000 $NEAR (valued at ~$430,000) was routed through these liquidity pools between Nov 5–7.
>> On-Chain Trail: Elliptic notes this tactic is designed to delay tracing rather than conceal it completely, creating multiple cheap transactional "layers" to slow down investigators.
As bad actors continuously shift strategies, active on-chain surveillance remains critical for tracking stolen funds across DEX ecosystems.
#writetoearn #Binance #CryptoNews #CyberSecurity #Web3
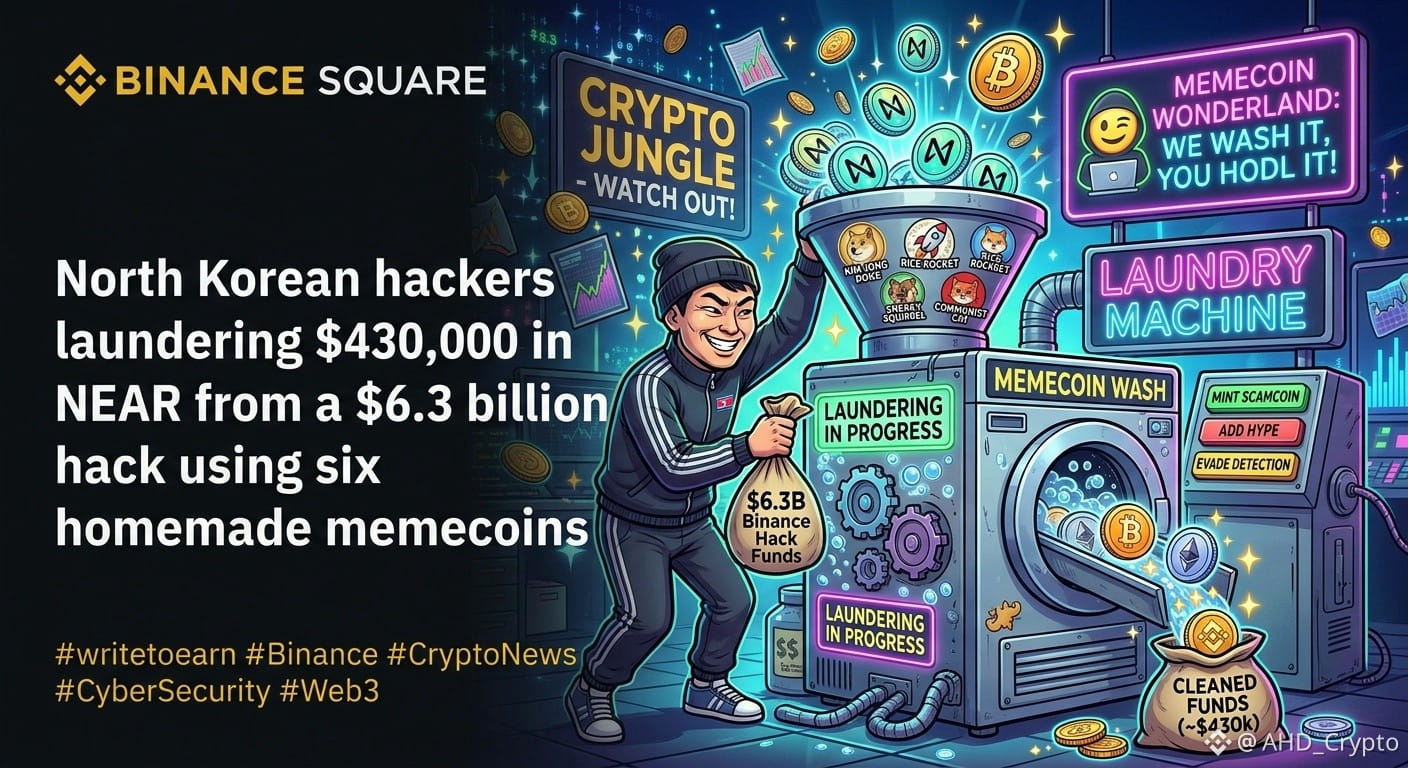
194
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CryptoSelloffTriggersMultipleWhaleLiquidations
50,999 views
719 Discussing
2
#USSpotXRPETFsSeeLargestWeeklyOutflowIn8Months
79,876 views
941 Discussing
3
#WillFOMCMinutesReinforceRateHikeExpectations?
12,835 views
296 Discussing
4
#BitcoinActiveSupplyInProfitDropsBelow45%
146,736 views
1,299 Discussing
5
#TONStrategyReports$23.97MQ3NetLoss
15,375 views
106 Discussing
6
#KavaSaysAbnormalActivityLimitedToKavaLend
96,256 views
712 Discussing
7
#WORPTLetsTouristsConvertCryptoToThaiBaht
25,737 views
246 Discussing
8
#WhoWillSucceedJensenHuangatNvidia?
272,568 views
1,985 Discussing
9
#WhatWillDriveCryptoandStocks’NextRebound?
752,444 views
3,796 Discussing
10
#TradFiForBeginners
796,280 views
4,785 Discussing