
#lukso
lukso
26,475 views
16 Discussing
Hot
Latest

·
--
Article
Email can recover your account, and it can also be used by someone else to take your money out of it.On the night of Nov 17 to Nov 18, about 1.4 million LYX were stolen from about 300 accounts on LUKSO. The attacker did not touch anyone's private keys, did not steal a single seed phrase, and the chain itself had no problems. The money went out through the "email account recovery" path.
LUKSO's Universal Profile is a smart contract account, and one account can have multiple keys with different permissions. To make it convenient for people who forget their passwords, LUKSO built an email recovery service; once the email verification passes, it can help you recover your account. On the night of Nov 17, the attacker exploited a vulnerability in the backend of this recovery service; LUKSO did not publicly disclose what kind it was. After obtaining the recovery service's own "recovery account," the attacker added one of their own control keys to each of about 300 users' accounts, with address 0xa2f8Fd85366d1B4A3B13C33A48CD959F6D1Ba3a7. Once the key was added, the money could be transferred out. The 1.4 million LYX were first bridged to Ethereum, then exchanged on decentralized exchanges like Uniswap for about 50 ETH, worth about $95,000. LUKSO released a post-incident report on Nov 18, saying the email recovery service has been shut down and is being retired.
Email can recover your account, and it can also be used by someone else to take your money out of it.
On the night of Nov 17 to Nov 18, about 1.4 million LYX were stolen from about 300 accounts on LUKSO. The attacker did not touch anyone's private keys, did not steal a single seed phrase, and the chain itself had no problems. The money went out through the "email account recovery" path.
LUKSO's Universal Profile is a smart contract account, and one account can have multiple keys with different permissions. To make it convenient for people who forget their passwords, LUKSO built an email recovery service; once the email verification passes, it can help you recover your account. On the night of Nov 17, the attacker exploited a vulnerability in the backend of this recovery service; LUKSO did not publicly disclose what kind it was. After obtaining the recovery service's own "recovery account," the attacker added one of their own control keys to each of about 300 users' accounts, with address 0xa2f8Fd85366d1B4A3B13C33A48CD959F6D1Ba3a7. Once the key was added, the money could be transferred out. The 1.4 million LYX were first bridged to Ethereum, then exchanged on decentralized exchanges like Uniswap for about 50 ETH, worth about $95,000. LUKSO released a post-incident report on Nov 18, saying the email recovery service has been shut down and is being retired.
LUKSO's Universal Profile is a smart contract account, and one account can have multiple keys with different permissions. To make it convenient for people who forget their passwords, LUKSO built an email recovery service; once the email verification passes, it can help you recover your account. On the night of Nov 17, the attacker exploited a vulnerability in the backend of this recovery service; LUKSO did not publicly disclose what kind it was. After obtaining the recovery service's own "recovery account," the attacker added one of their own control keys to each of about 300 users' accounts, with address 0xa2f8Fd85366d1B4A3B13C33A48CD959F6D1Ba3a7. Once the key was added, the money could be transferred out. The 1.4 million LYX were first bridged to Ethereum, then exchanged on decentralized exchanges like Uniswap for about 50 ETH, worth about $95,000. LUKSO released a post-incident report on Nov 18, saying the email recovery service has been shut down and is being retired.
16

·
--
【Market Alert】A vulnerability has been discovered in LUKSO’s email account recovery feature. Attackers exploited it to steal approximately 1.4 million LYX, affecting around 300 accounts. The stolen items were account profiles; the attackers’ keys remain in the accounts. The project team confirmed that the vulnerability was in the email recovery process and decided to disable the feature. Affected users must still manually remove the attackers’ keys, or their assets will remain at risk. Have you enabled email recovery?
$LYX $BTC $ETH
#币安广场 #安全 #LUKSO
(Source: TheDefiant)
⚠️Risk warning: The above is shared for market information only and does not constitute investment advice. Investing involves risks; exercise caution when entering the market.
【Market Alert】A vulnerability has been discovered in LUKSO’s email account recovery feature. Attackers exploited it to steal approximately 1.4 million LYX, affecting around 300 accounts. The stolen items were account profiles; the attackers’ keys remain in the accounts. The project team confirmed that the vulnerability was in the email recovery process and decided to disable the feature. Affected users must still manually remove the attackers’ keys, or their assets will remain at risk. Have you enabled email recovery?
$LYX $BTC $ETH
#币安广场 #安全 #LUKSO
(Source: TheDefiant)
⚠️Risk warning: The above is shared for market information only and does not constitute investment advice. Investing involves risks; exercise caution when entering the market.
$LYX $BTC $ETH
#币安广场 #安全 #LUKSO
(Source: TheDefiant)
⚠️Risk warning: The above is shared for market information only and does not constitute investment advice. Investing involves risks; exercise caution when entering the market.
4

·
--
LUKSO Urgent Alert: Some Universal Profiles Were Stuffed with Attacker Keys; Simply Revoking Permissions Is Not Enough
If you use a LUKSO Universal Profile (UP), pause for a moment: at 15:26 today (Hong Kong time), LUKSO officially issued an urgent security alert. An attacker used a malicious “recovery account” (recovery UP) to add a key they control to some UPs. The official notice specifically emphasized that simply revoking permissions is not enough; the entire controller must be removed.
This affects only “some” UP accounts, not the entire LUKSO network, and not all holders of LYX. The Defiant, citing on-chain indexing, said that as of 15:31, 278 different profiles had granted non-zero permissions to the attacker’s key; this number does not equal confirmed victims, let alone the amount stolen. As of 18:15, when quoted by Wu Shuo, the official had still not disclosed any asset losses.
The official remediation process has two steps: first, in the UP! mobile app, follow the instructions in the official post to remove the attacker’s controller key, even if it is not visible in the controller list; second, go to “Controllers” and delete that malicious recovery-up controller. Do not reverse the order, and removing only one does not count as done. For the operation address and key address, only trust the original post from LUKSO’s official X account; do not click “fix links” sent in DMs or comments.
Next, three things need to be confirmed: how the attacker’s malicious recovery account was added, whether any assets have already been transferred out, and whether the official will provide a batch detection tool.
How many controllers in your UP controller list do you currently recognize as your own?
Not investment advice.
Source: LUKSO official X (2026-11-18 15:26 Hong Kong time, https://x.com/LUKSO_io/status/2122954621253464215); The Defiant (https://thedefiant.io/news/security/lukso-urges-key-removal-after-universal-profile-attack); Wu Shuo (2026-11-18 18:15 Hong Kong time, https://x.com/wublockchain12/status/2122997140574155071) · 2026-11-18 Hong Kong time
#LUKSO #钱包安全 #夯B媒体 $LYX
LUKSO Urgent Alert: Some Universal Profiles Were Stuffed with Attacker Keys; Simply Revoking Permissions Is Not Enough
If you use a LUKSO Universal Profile (UP), pause for a moment: at 15:26 today (Hong Kong time), LUKSO officially issued an urgent security alert. An attacker used a malicious “recovery account” (recovery UP) to add a key they control to some UPs. The official notice specifically emphasized that simply revoking permissions is not enough; the entire controller must be removed.
This affects only “some” UP accounts, not the entire LUKSO network, and not all holders of LYX. The Defiant, citing on-chain indexing, said that as of 15:31, 278 different profiles had granted non-zero permissions to the attacker’s key; this number does not equal confirmed victims, let alone the amount stolen. As of 18:15, when quoted by Wu Shuo, the official had still not disclosed any asset losses.
The official remediation process has two steps: first, in the UP! mobile app, follow the instructions in the official post to remove the attacker’s controller key, even if it is not visible in the controller list; second, go to “Controllers” and delete that malicious recovery-up controller. Do not reverse the order, and removing only one does not count as done. For the operation address and key address, only trust the original post from LUKSO’s official X account; do not click “fix links” sent in DMs or comments.
Next, three things need to be confirmed: how the attacker’s malicious recovery account was added, whether any assets have already been transferred out, and whether the official will provide a batch detection tool.
How many controllers in your UP controller list do you currently recognize as your own?
Not investment advice.
Source: LUKSO official X (2026-11-18 15:26 Hong Kong time, https://x.com/LUKSO_io/status/2122954621253464215); The Defiant (https://thedefiant.io/news/security/lukso-urges-key-removal-after-universal-profile-attack); Wu Shuo (2026-11-18 18:15 Hong Kong time, https://x.com/wublockchain12/status/2122997140574155071) · 2026-11-18 Hong Kong time
#LUKSO #钱包安全 #夯B媒体 $LYX
If you use a LUKSO Universal Profile (UP), pause for a moment: at 15:26 today (Hong Kong time), LUKSO officially issued an urgent security alert. An attacker used a malicious “recovery account” (recovery UP) to add a key they control to some UPs. The official notice specifically emphasized that simply revoking permissions is not enough; the entire controller must be removed.
This affects only “some” UP accounts, not the entire LUKSO network, and not all holders of LYX. The Defiant, citing on-chain indexing, said that as of 15:31, 278 different profiles had granted non-zero permissions to the attacker’s key; this number does not equal confirmed victims, let alone the amount stolen. As of 18:15, when quoted by Wu Shuo, the official had still not disclosed any asset losses.
The official remediation process has two steps: first, in the UP! mobile app, follow the instructions in the official post to remove the attacker’s controller key, even if it is not visible in the controller list; second, go to “Controllers” and delete that malicious recovery-up controller. Do not reverse the order, and removing only one does not count as done. For the operation address and key address, only trust the original post from LUKSO’s official X account; do not click “fix links” sent in DMs or comments.
Next, three things need to be confirmed: how the attacker’s malicious recovery account was added, whether any assets have already been transferred out, and whether the official will provide a batch detection tool.
How many controllers in your UP controller list do you currently recognize as your own?
Not investment advice.
Source: LUKSO official X (2026-11-18 15:26 Hong Kong time, https://x.com/LUKSO_io/status/2122954621253464215); The Defiant (https://thedefiant.io/news/security/lukso-urges-key-removal-after-universal-profile-attack); Wu Shuo (2026-11-18 18:15 Hong Kong time, https://x.com/wublockchain12/status/2122997140574155071) · 2026-11-18 Hong Kong time
#LUKSO #钱包安全 #夯B媒体 $LYX
12

The most important thing to remember about this LUKSO hack is what the official announcement said: revoking permissions alone isn’t enough—you have to remove both controllers completely.
First, what’s been confirmed: At 07:26 UTC on 11/18, LUKSO officially issued an emergency announcement saying that an attacker used a malicious “recovery” Universal Profile to add keys they controlled to some users’ UP accounts. The official instructions are to first delete the attacker’s key—in case it doesn’t appear in the controller list—and then delete the malicious recovery controller.
There’s no official figure yet for the scale of the losses. Claims circulating in the community include “278 Profiles granted that key nonzero permissions,” “about 296 accounts hacked for around 1.5 million LYX,” and “over 1 million LYX bridged out via Hyperlane.” These figures don’t line up, so treat them as rumors for now. It also hasn’t been disclosed how the attacker got the malicious recovery UP attached to users’ accounts.
But the phrase “revoking permissions isn’t enough” explains the mechanism. Social recovery for a smart contract account is essentially a backdoor you leave for another address, allowing it to add keys to your account again. If you zero out the attacker key’s permissions, but leave the recovery controller in place, it can simply add the key back. Many people treat “recoverability” as a selling point that makes these wallets safer than private-key wallets. In reality, it adds another high-privilege access point—and it’s not obvious in everyday use, so no one checks it daily.
So if you use any smart wallet with a recovery/guardian mechanism—not just LUKSO—keep a checklist: How many controllers are there now? Who can add new controllers? Is there a delay before recovery takes effect? Recovery permissions without a timelock aren’t much different from giving someone a copy of your seed phrase.
#LUKSO #WalletSecurity
The most important thing to remember about this LUKSO hack is what the official announcement said: revoking permissions alone isn’t enough—you have to remove both controllers completely.
First, what’s been confirmed: At 07:26 UTC on 11/18, LUKSO officially issued an emergency announcement saying that an attacker used a malicious “recovery” Universal Profile to add keys they controlled to some users’ UP accounts. The official instructions are to first delete the attacker’s key—in case it doesn’t appear in the controller list—and then delete the malicious recovery controller.
There’s no official figure yet for the scale of the losses. Claims circulating in the community include “278 Profiles granted that key nonzero permissions,” “about 296 accounts hacked for around 1.5 million LYX,” and “over 1 million LYX bridged out via Hyperlane.” These figures don’t line up, so treat them as rumors for now. It also hasn’t been disclosed how the attacker got the malicious recovery UP attached to users’ accounts.
But the phrase “revoking permissions isn’t enough” explains the mechanism. Social recovery for a smart contract account is essentially a backdoor you leave for another address, allowing it to add keys to your account again. If you zero out the attacker key’s permissions, but leave the recovery controller in place, it can simply add the key back. Many people treat “recoverability” as a selling point that makes these wallets safer than private-key wallets. In reality, it adds another high-privilege access point—and it’s not obvious in everyday use, so no one checks it daily.
So if you use any smart wallet with a recovery/guardian mechanism—not just LUKSO—keep a checklist: How many controllers are there now? Who can add new controllers? Is there a delay before recovery takes effect? Recovery permissions without a timelock aren’t much different from giving someone a copy of your seed phrase.
#LUKSO #WalletSecurity
First, what’s been confirmed: At 07:26 UTC on 11/18, LUKSO officially issued an emergency announcement saying that an attacker used a malicious “recovery” Universal Profile to add keys they controlled to some users’ UP accounts. The official instructions are to first delete the attacker’s key—in case it doesn’t appear in the controller list—and then delete the malicious recovery controller.
There’s no official figure yet for the scale of the losses. Claims circulating in the community include “278 Profiles granted that key nonzero permissions,” “about 296 accounts hacked for around 1.5 million LYX,” and “over 1 million LYX bridged out via Hyperlane.” These figures don’t line up, so treat them as rumors for now. It also hasn’t been disclosed how the attacker got the malicious recovery UP attached to users’ accounts.
But the phrase “revoking permissions isn’t enough” explains the mechanism. Social recovery for a smart contract account is essentially a backdoor you leave for another address, allowing it to add keys to your account again. If you zero out the attacker key’s permissions, but leave the recovery controller in place, it can simply add the key back. Many people treat “recoverability” as a selling point that makes these wallets safer than private-key wallets. In reality, it adds another high-privilege access point—and it’s not obvious in everyday use, so no one checks it daily.
So if you use any smart wallet with a recovery/guardian mechanism—not just LUKSO—keep a checklist: How many controllers are there now? Who can add new controllers? Is there a delay before recovery takes effect? Recovery permissions without a timelock aren’t much different from giving someone a copy of your seed phrase.
#LUKSO #WalletSecurity
1

🚀 The Web3 Social Layer
Social networking shouldn't be limited to centralized platforms.
LUKSO is building around Universal Profiles, digital identity and onchain social experiences.
The next chapter of Web3 social could be interesting!
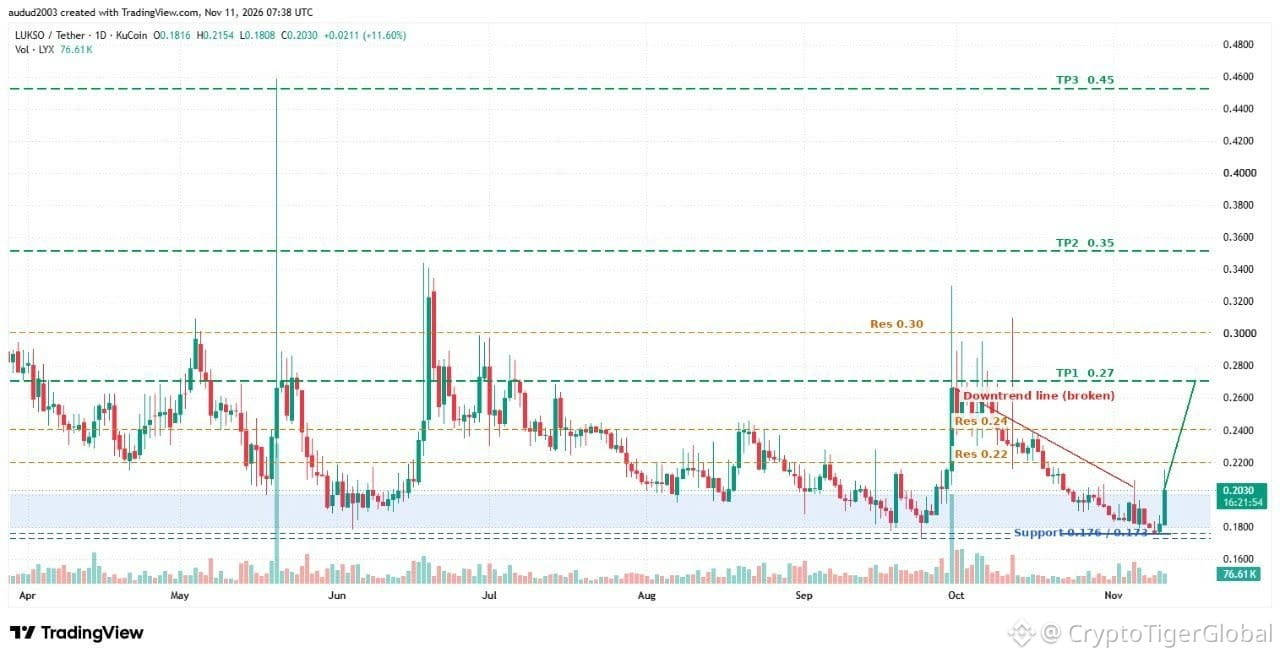
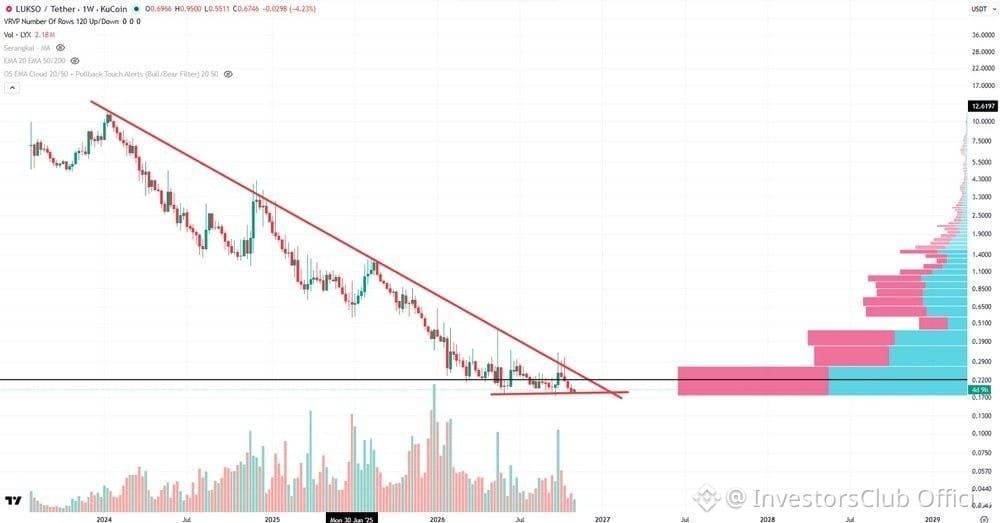
🎯 $LYX:
$0.23 → $0.27 → $0.35 → $0.42 → $0.55
@lukso_io @ERC725Account $LYX
#SocialFi Fi #Lukso
🚀 The Web3 Social Layer
Social networking shouldn't be limited to centralized platforms.
LUKSO is building around Universal Profiles, digital identity and onchain social experiences.
The next chapter of Web3 social could be interesting!
🎯 $LYX:
$0.23 → $0.27 → $0.35 → $0.42 → $0.55
@lukso_io @ERC725Account $LYX
#SocialFi Fi #Lukso
Social networking shouldn't be limited to centralized platforms.
LUKSO is building around Universal Profiles, digital identity and onchain social experiences.
The next chapter of Web3 social could be interesting!
🎯 $LYX:
$0.23 → $0.27 → $0.35 → $0.42 → $0.55
@lukso_io @ERC725Account $LYX
#SocialFi Fi #Lukso
143


🤖 The AI & Web3 Connection
AI is changing how we interact with technology.
Web3 identity and smart accounts could become important pieces of this evolution.
LUKSO is an ecosystem worth following in this space.
🎯 $LYX Price Targets:
$0.23 → $0.27 → $0.42 → $0.55
The future is getting interesting! 🚀
@lukso_io @ERC725Account $LYX
#AI #Web3 #LUKSO
🤖 The AI & Web3 Connection
AI is changing how we interact with technology.
Web3 identity and smart accounts could become important pieces of this evolution.
LUKSO is an ecosystem worth following in this space.
🎯 $LYX Price Targets:
$0.23 → $0.27 → $0.42 → $0.55
The future is getting interesting! 🚀
@lukso_io @ERC725Account $LYX
#AI #Web3 #LUKSO
AI is changing how we interact with technology.
Web3 identity and smart accounts could become important pieces of this evolution.
LUKSO is an ecosystem worth following in this space.
🎯 $LYX Price Targets:
$0.23 → $0.27 → $0.42 → $0.55
The future is getting interesting! 🚀
@lukso_io @ERC725Account $LYX
#AI #Web3 #LUKSO
201
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BTCReboundsAbove$60KAmidWhaleDipBuying
52,444 views
278 Discussing
2
#SolanaSets2027RoadmapToDoubleComputeCapacity
37,321 views
758 Discussing
3
#CaliforniaNvidiaProbeExaminesPotentialCriminalViolations
9,730 views
99 Discussing
4
#BlackRockLaunchesHKDollarDigitalLiquidityFund
30,240 views
588 Discussing
5
#NvidiaLoses$2.7TrillionInMonthAndAHalf
69,648 views
285 Discussing
6
#GlobalStocksFaceLongestLosingStreakSince2023
528,320 views
3,306 Discussing
7
#BlackRockIBITPostsRecord$541MSingleDayOutflow
86,392 views
176 Discussing
8
#AnthropicPlungesTowardIPOPriceonDay2
288,827 views
2,215 Discussing
9
#TwentyOneCapitalAdds172.25BTC
149,901 views
1,543 Discussing
10
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
17,220 views
100 Discussing