
#security
security
2M views
6,377 Discussing
Hot
Latest
·
--
🚨 Wrapped Monero crashes amid multi‑million $ exploit – $BTC & $ETH tumble
🚨 Wrapped Monero suffers a flash‑loan style exploit, draining millions from its liquidity pool in minutes.
📉 Immediate market reaction
• $WRXMR price plunged sharply, breaking key support levels.
• $BTC slipped about 6% to $57,988.58.
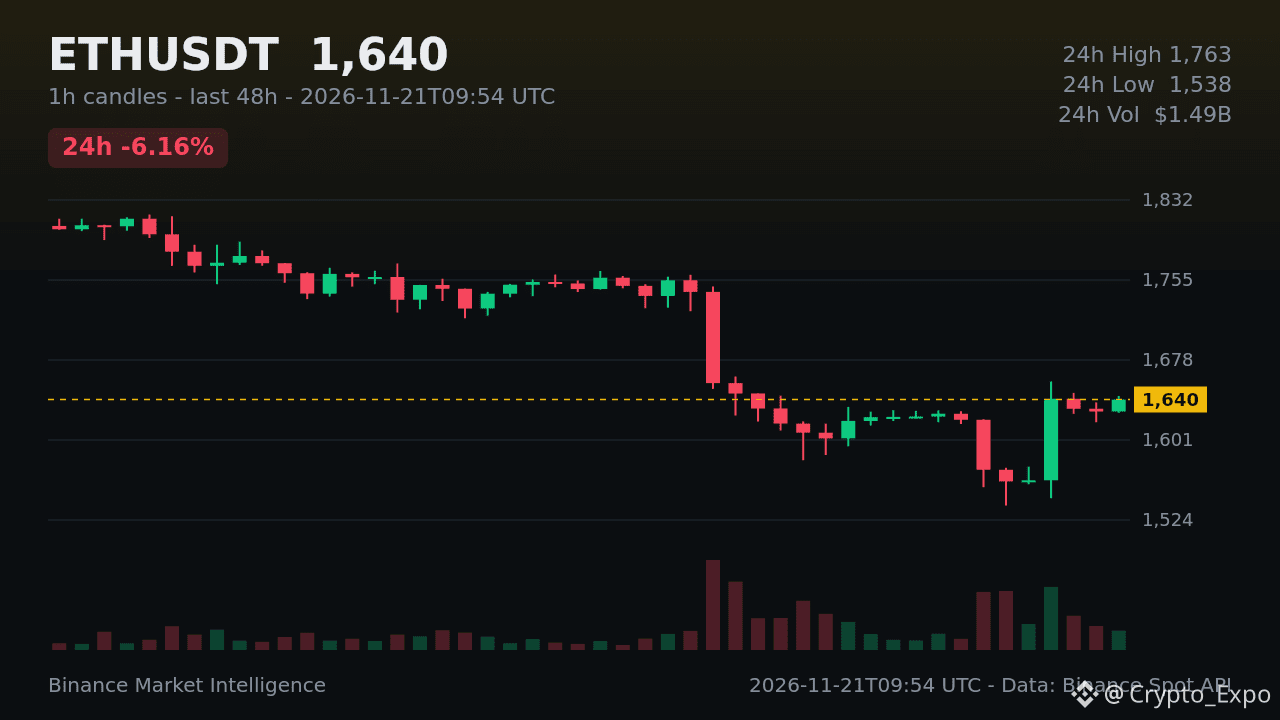
• $ETH dropped about 6% to $1,640.04.
• Fear & Greed Index sits at 12 (Extreme Fear), signaling heightened risk aversion.
⚠️ Risk note
The exploit highlights potential contract vulnerabilities. Keep position sizes small until a thorough audit is released.
💬 What’s your take – short‑term panic sell or long‑term opportunity? Share your thoughts below 👇
$WRXMR $BTC #Crypto #Security #Altcoins
🚨 Wrapped Monero crashes amid multi‑million $ exploit – $BTC & $ETH tumble
🚨 Wrapped Monero suffers a flash‑loan style exploit, draining millions from its liquidity pool in minutes.
📉 Immediate market reaction
• $WRXMR price plunged sharply, breaking key support levels.
• $BTC slipped about 6% to $57,988.58.
• $ETH dropped about 6% to $1,640.04.
• Fear & Greed Index sits at 12 (Extreme Fear), signaling heightened risk aversion.
⚠️ Risk note
The exploit highlights potential contract vulnerabilities. Keep position sizes small until a thorough audit is released.
💬 What’s your take – short‑term panic sell or long‑term opportunity? Share your thoughts below 👇
$WRXMR $BTC #Crypto #Security #Altcoins
🚨 Wrapped Monero suffers a flash‑loan style exploit, draining millions from its liquidity pool in minutes.
📉 Immediate market reaction
• $WRXMR price plunged sharply, breaking key support levels.
• $BTC slipped about 6% to $57,988.58.
• $ETH dropped about 6% to $1,640.04.
• Fear & Greed Index sits at 12 (Extreme Fear), signaling heightened risk aversion.
⚠️ Risk note
The exploit highlights potential contract vulnerabilities. Keep position sizes small until a thorough audit is released.
💬 What’s your take – short‑term panic sell or long‑term opportunity? Share your thoughts below 👇
$WRXMR $BTC #Crypto #Security #Altcoins
1
·
--
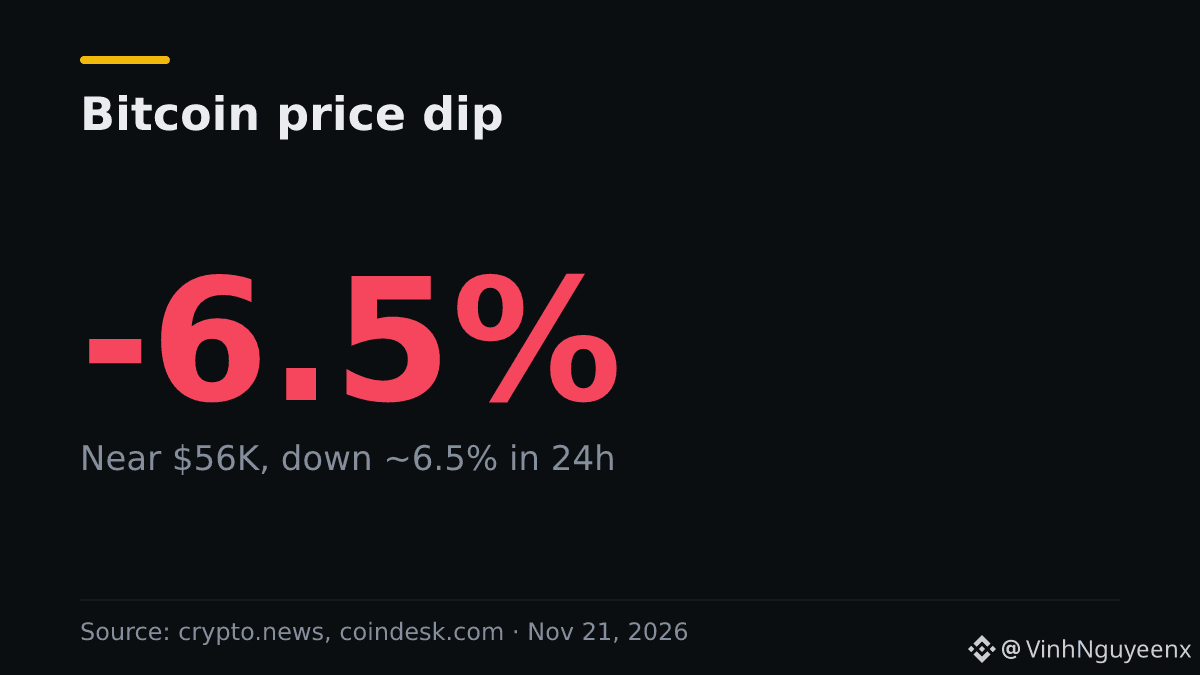
Bitcoin slipped under $56K as a critical node bug surfaced.
• Bitcoin fell to ~ $55,935, its lowest in over two years (crypto.news)
• An AI‑detected bug could stall nodes by repeating one ID 50,000 times (coindesk.com)
The convergence of market weakness and a technical vulnerability underscores the need for rigorous code audits and strong liquidity buffers.
Which risk worries you more?
A) Market sell‑offs
B) Software bugs
$BTC #Crypto #Security 🚀 🔒
⚠️ Not financial advice. DYOR.
Bitcoin slipped under $56K as a critical node bug surfaced.
• Bitcoin fell to ~ $55,935, its lowest in over two years (crypto.news)
• An AI‑detected bug could stall nodes by repeating one ID 50,000 times (coindesk.com)
The convergence of market weakness and a technical vulnerability underscores the need for rigorous code audits and strong liquidity buffers.
Which risk worries you more?
A) Market sell‑offs
B) Software bugs
$BTC #Crypto #Security 🚀 🔒
⚠️ Not financial advice. DYOR.
• Bitcoin fell to ~ $55,935, its lowest in over two years (crypto.news)
• An AI‑detected bug could stall nodes by repeating one ID 50,000 times (coindesk.com)
The convergence of market weakness and a technical vulnerability underscores the need for rigorous code audits and strong liquidity buffers.
Which risk worries you more?
A) Market sell‑offs
B) Software bugs
$BTC #Crypto #Security 🚀 🔒
⚠️ Not financial advice. DYOR.
34
·
--
Article
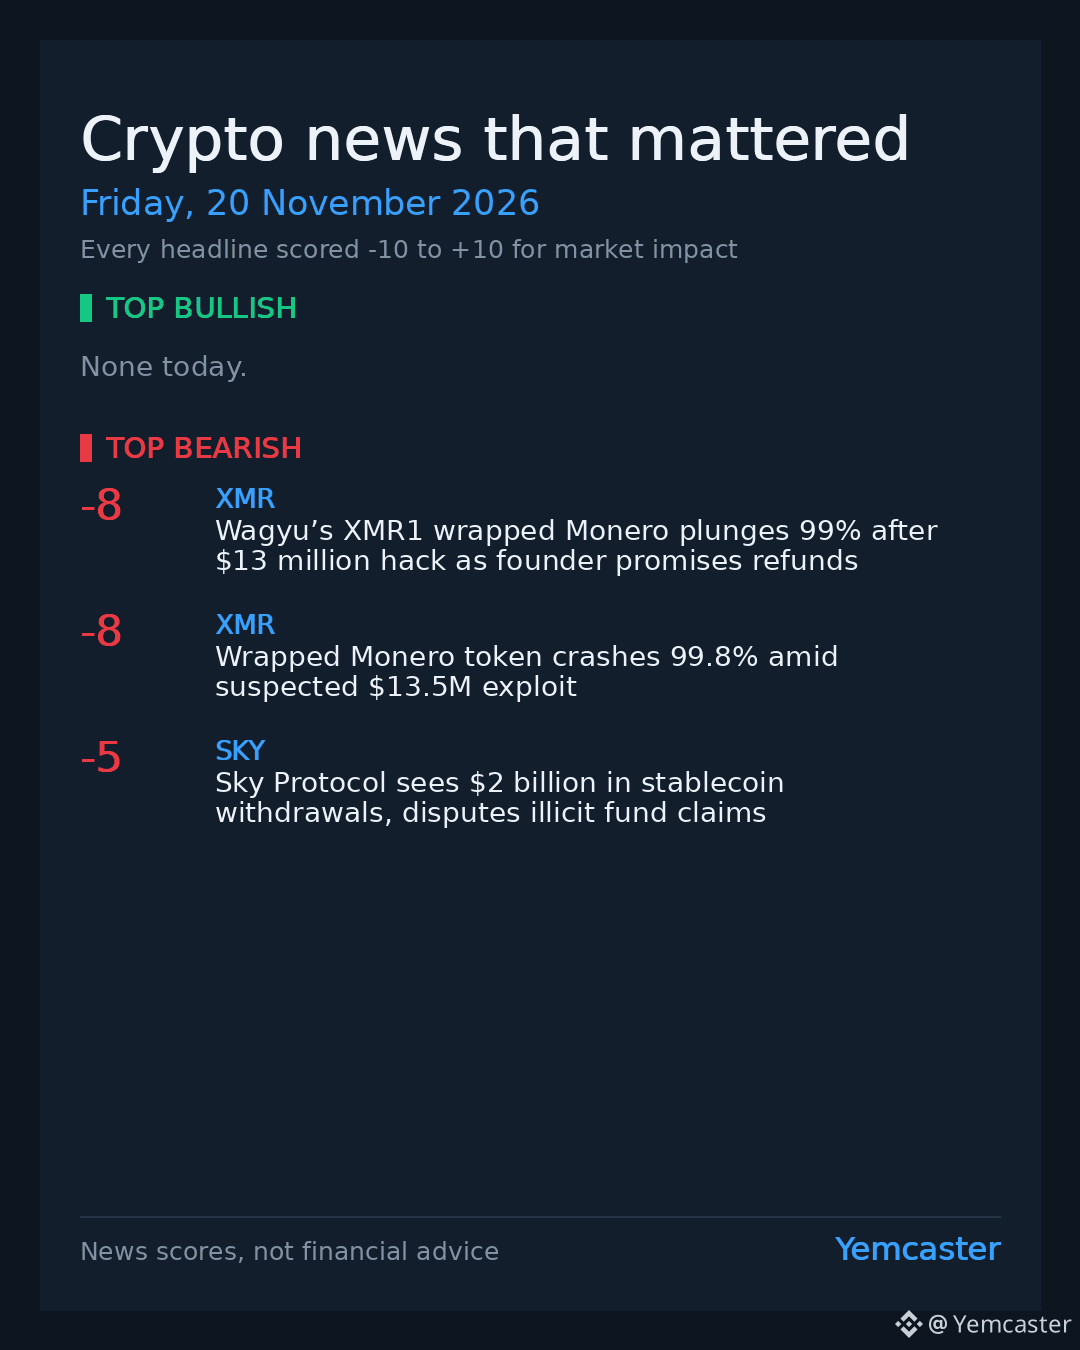
20 Nov: the crypto headlines that matteredSecurity exploits and capital movement weighed heavily on the broader crypto market yesterday, 20 Nov 2026.
Wrapped Monero dropped 99 percent following a 13 million USD hack, an event that carries a Yemcaster score of -8 as the project founder promises refunds to those affected.
A separate report highlighted a 99.8 percent crash in the Wrapped Monero token due to a suspected 13.5 million USD exploit, also receiving a score of -8.
The $SKY protocol faced challenges as 2 billion USD in stablecoin withdrawals occurred, with the team actively disputing allegations of illicit fund activity, resulting in a score of -5.
#CryptoNews #DeFi #Security
News scores, not financial advice.
20 Nov: the crypto headlines that mattered
Security exploits and capital movement weighed heavily on the broader crypto market yesterday, 20 Nov 2026.
Wrapped Monero dropped 99 percent following a 13 million USD hack, an event that carries a Yemcaster score of -8 as the project founder promises refunds to those affected.
A separate report highlighted a 99.8 percent crash in the Wrapped Monero token due to a suspected 13.5 million USD exploit, also receiving a score of -8.
The $SKY protocol faced challenges as 2 billion USD in stablecoin withdrawals occurred, with the team actively disputing allegations of illicit fund activity, resulting in a score of -5.
#CryptoNews #DeFi #Security
News scores, not financial advice.
Wrapped Monero dropped 99 percent following a 13 million USD hack, an event that carries a Yemcaster score of -8 as the project founder promises refunds to those affected.
A separate report highlighted a 99.8 percent crash in the Wrapped Monero token due to a suspected 13.5 million USD exploit, also receiving a score of -8.
The $SKY protocol faced challenges as 2 billion USD in stablecoin withdrawals occurred, with the team actively disputing allegations of illicit fund activity, resulting in a score of -5.
#CryptoNews #DeFi #Security
News scores, not financial advice.
270
·
--
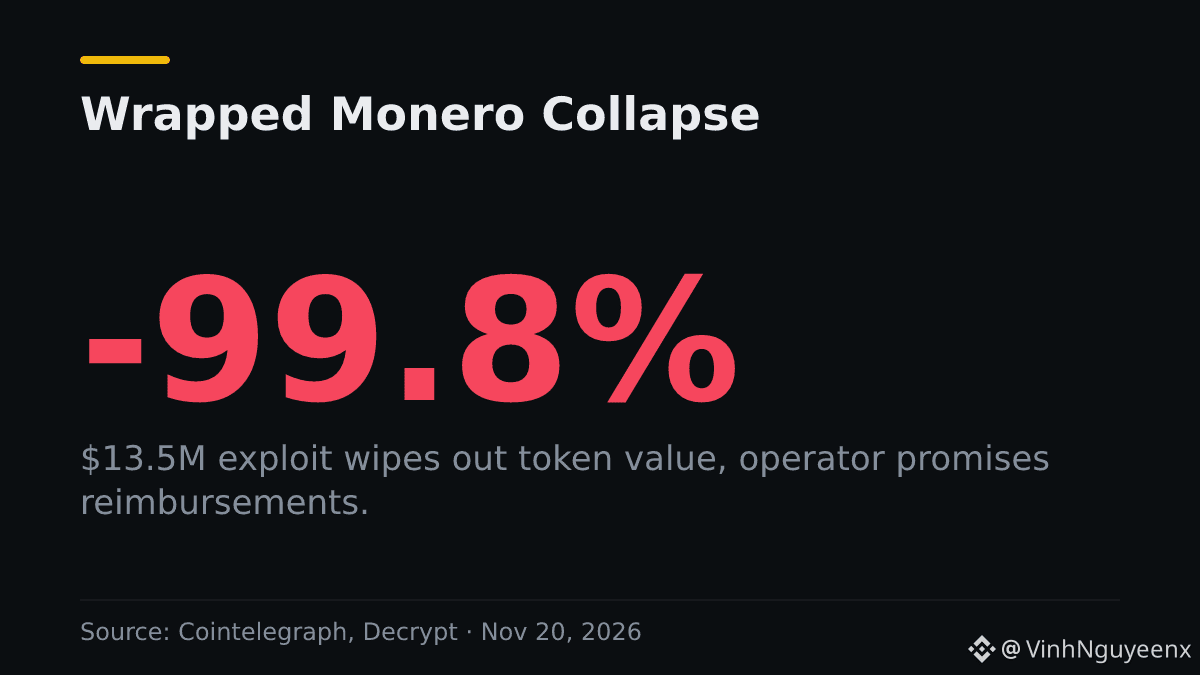
Wrapped Monero plunged 99.8% after a $13.5 million exploit.
• Token fell >99% as $13.5M was siphoned (cointelegraph.com)
• Operator blamed a security breach and vowed reimbursements (decrypt.co)
The crash underscores the fragility of wrapped assets and the urgency of rigorous audits.
How should the community respond?
A) Demand stricter audits
B) Accept risk of innovation
$XMR #WrappedToken #Security 🛡️
⚠️ Not financial advice. DYOR.
Wrapped Monero plunged 99.8% after a $13.5 million exploit.
• Token fell >99% as $13.5M was siphoned (cointelegraph.com)
• Operator blamed a security breach and vowed reimbursements (decrypt.co)
The crash underscores the fragility of wrapped assets and the urgency of rigorous audits.
How should the community respond?
A) Demand stricter audits
B) Accept risk of innovation
$XMR #WrappedToken #Security 🛡️
⚠️ Not financial advice. DYOR.
• Token fell >99% as $13.5M was siphoned (cointelegraph.com)
• Operator blamed a security breach and vowed reimbursements (decrypt.co)
The crash underscores the fragility of wrapped assets and the urgency of rigorous audits.
How should the community respond?
A) Demand stricter audits
B) Accept risk of innovation
$XMR #WrappedToken #Security 🛡️
⚠️ Not financial advice. DYOR.
23
·
--
Wrapped Monero token XMR1 crashes over 99% after hack
An attacker shifted 5.2 million XMR1 from its deployer account and sold a portion for roughly $13.5 M, per Decrypt. The token's price collapsed, leaving it almost valueless.
📌 Key points:
• XMR1 fell more than 99%
• 5.2 million tokens moved from deployer account
• $13.5 M worth sold
• Hack blamed on the web host
It shows how a single hosting flaw can devastate a wrapped asset, though I'm not sure how far the fallout will reach across DeFi.
For context, $BTC $58,481 (-6.05%) and $SOL $68.31 (-6.71%) right now.
Do you think wrapped tokens should require audited hosting providers?
#crypto #security #DeFi
Wrapped Monero token XMR1 crashes over 99% after hack
An attacker shifted 5.2 million XMR1 from its deployer account and sold a portion for roughly $13.5 M, per Decrypt. The token's price collapsed, leaving it almost valueless.
📌 Key points:
• XMR1 fell more than 99%
• 5.2 million tokens moved from deployer account
• $13.5 M worth sold
• Hack blamed on the web host
It shows how a single hosting flaw can devastate a wrapped asset, though I'm not sure how far the fallout will reach across DeFi.
For context, $BTC $58,481 (-6.05%) and $SOL $68.31 (-6.71%) right now.
Do you think wrapped tokens should require audited hosting providers?
#crypto #security #DeFi
An attacker shifted 5.2 million XMR1 from its deployer account and sold a portion for roughly $13.5 M, per Decrypt. The token's price collapsed, leaving it almost valueless.
📌 Key points:
• XMR1 fell more than 99%
• 5.2 million tokens moved from deployer account
• $13.5 M worth sold
• Hack blamed on the web host
It shows how a single hosting flaw can devastate a wrapped asset, though I'm not sure how far the fallout will reach across DeFi.
For context, $BTC $58,481 (-6.05%) and $SOL $68.31 (-6.71%) right now.
Do you think wrapped tokens should require audited hosting providers?
#crypto #security #DeFi
300

·
--
🚨 $BTC $ETH $SOL EXPOSED IN OPTIMIZELY security incident – 178 SITES COMPROMISED
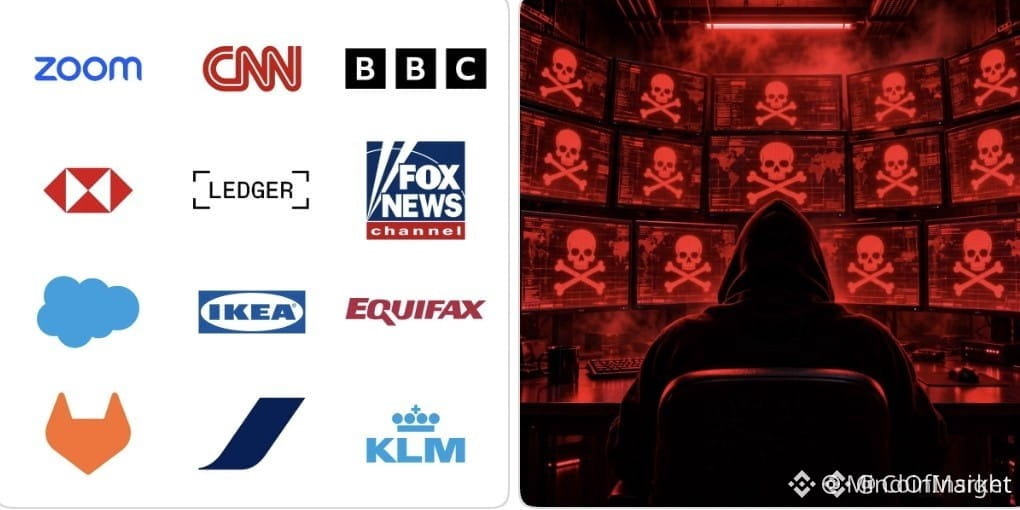
The recent Optimizely test‑environment breach injected malicious scripts across 178 high‑profile domains, from HSBC to BBC, siphoning crypto addresses and credential data. 📊
Smart‑money operators scan for these exposed addresses; the sudden influx of $BTC , $ETH and $SOL on a top‑tier exchange’s inbound flow often signals a liquidity sweep driven by compromised scripts. 🔍
Institutions must audit third‑party integrations and enforce zero‑trust token handling to prevent a single weak link from contaminating the broader ecosystem. 💡
💬 Have you revisited your address verification workflow after this wave?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ETH #SOL #Security #CryptoRisk
🦈 🔥
🚨 $BTC $ETH $SOL EXPOSED IN OPTIMIZELY security incident – 178 SITES COMPROMISED
The recent Optimizely test‑environment breach injected malicious scripts across 178 high‑profile domains, from HSBC to BBC, siphoning crypto addresses and credential data. 📊
Smart‑money operators scan for these exposed addresses; the sudden influx of $BTC , $ETH and $SOL on a top‑tier exchange’s inbound flow often signals a liquidity sweep driven by compromised scripts. 🔍
Institutions must audit third‑party integrations and enforce zero‑trust token handling to prevent a single weak link from contaminating the broader ecosystem. 💡
💬 Have you revisited your address verification workflow after this wave?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ETH #SOL #Security #CryptoRisk
🦈 🔥
The recent Optimizely test‑environment breach injected malicious scripts across 178 high‑profile domains, from HSBC to BBC, siphoning crypto addresses and credential data. 📊
Smart‑money operators scan for these exposed addresses; the sudden influx of $BTC , $ETH and $SOL on a top‑tier exchange’s inbound flow often signals a liquidity sweep driven by compromised scripts. 🔍
Institutions must audit third‑party integrations and enforce zero‑trust token handling to prevent a single weak link from contaminating the broader ecosystem. 💡
💬 Have you revisited your address verification workflow after this wave?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ETH #SOL #Security #CryptoRisk
🦈 🔥
5

🚨 178 ENTERPRISE WEBSITES COMPROMISED IN SILENT CLIPBOARD ATTACK TARGETING $BTC , $ETH , AND $SOL ! ⚠️
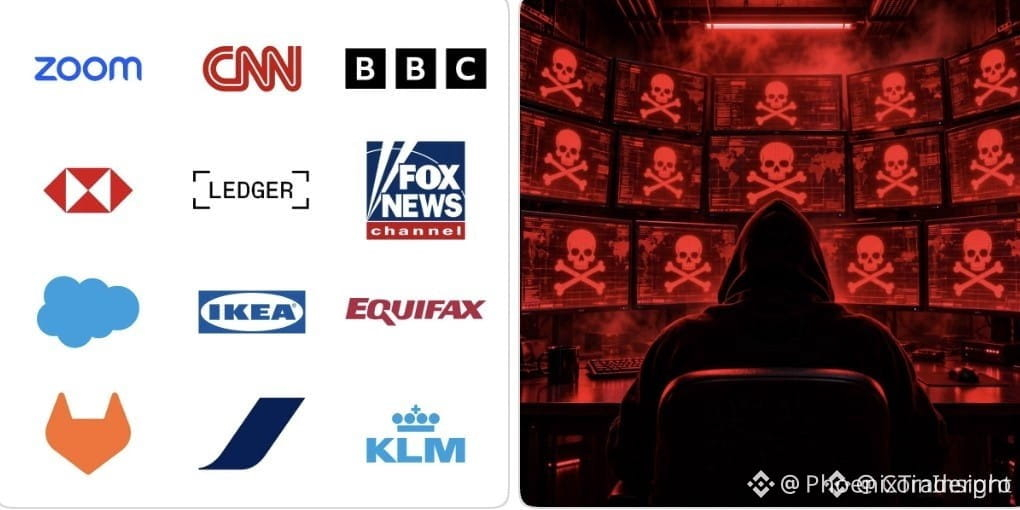
A silent malicious script just swept across 178 high-profile web portals, quietly rewriting destination addresses during $BTC , $ETH , and $SOL transfers. 🔍
When trusted digital infrastructure gets subverted, automated address swapping can intercept your capital before you even hit send. 💡 Always verify every single character on your hardware device display before clearing any transaction. 🛡️
💬 How meticulously do you verify destination addresses character by character during routine asset transfers? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #Crypto #Solana
🔥 💎
🚨 178 ENTERPRISE WEBSITES COMPROMISED IN SILENT CLIPBOARD ATTACK TARGETING $BTC , $ETH , AND $SOL ! ⚠️
A silent malicious script just swept across 178 high-profile web portals, quietly rewriting destination addresses during $BTC , $ETH , and $SOL transfers. 🔍
When trusted digital infrastructure gets subverted, automated address swapping can intercept your capital before you even hit send. 💡 Always verify every single character on your hardware device display before clearing any transaction. 🛡️
💬 How meticulously do you verify destination addresses character by character during routine asset transfers? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #Crypto #Solana
🔥 💎
A silent malicious script just swept across 178 high-profile web portals, quietly rewriting destination addresses during $BTC , $ETH , and $SOL transfers. 🔍
When trusted digital infrastructure gets subverted, automated address swapping can intercept your capital before you even hit send. 💡 Always verify every single character on your hardware device display before clearing any transaction. 🛡️
💬 How meticulously do you verify destination addresses character by character during routine asset transfers? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #Crypto #Solana
🔥 💎
9

·
--
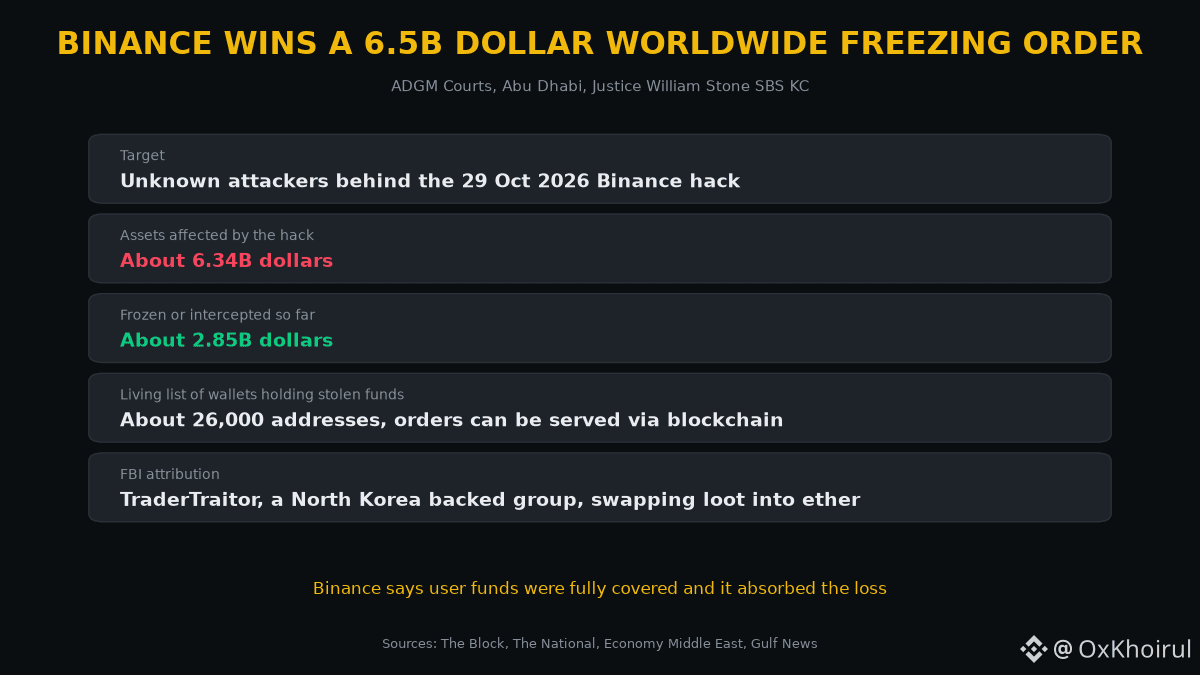
Binance just got a court to freeze up to 6.5 billion dollars worldwide against the people who hacked it, and lawyers are calling it maybe the biggest freezing order ever made.
The order came from the ADGM Courts in Abu Dhabi and targets the unknown attackers behind the Oct 29 hack.
What's confirmed so far:
About 6.34B dollars in assets were hit in the attack
About 2.85B of that has been frozen or intercepted
There's a living list of around 26,000 wallets holding stolen funds, and the orders can be served straight on chain
The FBI pinned it on TraderTraitor, a North Korea backed group, and says they've been swapping the loot into $ETH
The interesting part for me is the practical side. Some issuers and exchanges won't hand back frozen funds without a formal court order. Now there is one, so recovery could actually move faster. Binance also says users were fully covered and it ate the loss itself.
Market isn't celebrating though. $BTC is around 61.6K on Binance this morning, down almost 2% on the day.
Do you think court orders like this can really claw back hacked crypto, or is most of it gone for good?
#Binance #CryptoNews #Security
Binance just got a court to freeze up to 6.5 billion dollars worldwide against the people who hacked it, and lawyers are calling it maybe the biggest freezing order ever made.
The order came from the ADGM Courts in Abu Dhabi and targets the unknown attackers behind the Oct 29 hack.
What's confirmed so far:
About 6.34B dollars in assets were hit in the attack
About 2.85B of that has been frozen or intercepted
There's a living list of around 26,000 wallets holding stolen funds, and the orders can be served straight on chain
The FBI pinned it on TraderTraitor, a North Korea backed group, and says they've been swapping the loot into $ETH
The interesting part for me is the practical side. Some issuers and exchanges won't hand back frozen funds without a formal court order. Now there is one, so recovery could actually move faster. Binance also says users were fully covered and it ate the loss itself.
Market isn't celebrating though. $BTC is around 61.6K on Binance this morning, down almost 2% on the day.
Do you think court orders like this can really claw back hacked crypto, or is most of it gone for good?
#Binance #CryptoNews #Security
The order came from the ADGM Courts in Abu Dhabi and targets the unknown attackers behind the Oct 29 hack.
What's confirmed so far:
About 6.34B dollars in assets were hit in the attack
About 2.85B of that has been frozen or intercepted
There's a living list of around 26,000 wallets holding stolen funds, and the orders can be served straight on chain
The FBI pinned it on TraderTraitor, a North Korea backed group, and says they've been swapping the loot into $ETH
The interesting part for me is the practical side. Some issuers and exchanges won't hand back frozen funds without a formal court order. Now there is one, so recovery could actually move faster. Binance also says users were fully covered and it ate the loss itself.
Market isn't celebrating though. $BTC is around 61.6K on Binance this morning, down almost 2% on the day.
Do you think court orders like this can really claw back hacked crypto, or is most of it gone for good?
#Binance #CryptoNews #Security
1.4k

🚨 SUPPLY CHAIN INTERFERENCE TARGETING $BTC COLD STORAGE ACROSS BERLIN AND DUBAI! ⚠️
Institutional-grade security begins at the point of origin, where recent supply-chain vectors in Berlin and Dubai compromised physical hardware before unboxing. 🦈 Unscrupulous interception points are manipulating distribution channels to compromise recovery pathways, resulting in significant capital loss. 📊
Smart capital never compromises on custody integrity, reinforcing the absolute necessity of sourcing hardware exclusively through official direct channels. 🛡️
How do you verify the integrity of your cold storage before transferring major liquidity? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #ColdStorage #Crypto
🔒 ⚡
🚨 SUPPLY CHAIN INTERFERENCE TARGETING $BTC COLD STORAGE ACROSS BERLIN AND DUBAI! ⚠️
Institutional-grade security begins at the point of origin, where recent supply-chain vectors in Berlin and Dubai compromised physical hardware before unboxing. 🦈 Unscrupulous interception points are manipulating distribution channels to compromise recovery pathways, resulting in significant capital loss. 📊
Smart capital never compromises on custody integrity, reinforcing the absolute necessity of sourcing hardware exclusively through official direct channels. 🛡️
How do you verify the integrity of your cold storage before transferring major liquidity? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #ColdStorage #Crypto
🔒 ⚡
Institutional-grade security begins at the point of origin, where recent supply-chain vectors in Berlin and Dubai compromised physical hardware before unboxing. 🦈 Unscrupulous interception points are manipulating distribution channels to compromise recovery pathways, resulting in significant capital loss. 📊
Smart capital never compromises on custody integrity, reinforcing the absolute necessity of sourcing hardware exclusively through official direct channels. 🛡️
How do you verify the integrity of your cold storage before transferring major liquidity? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #ColdStorage #Crypto
🔒 ⚡
7

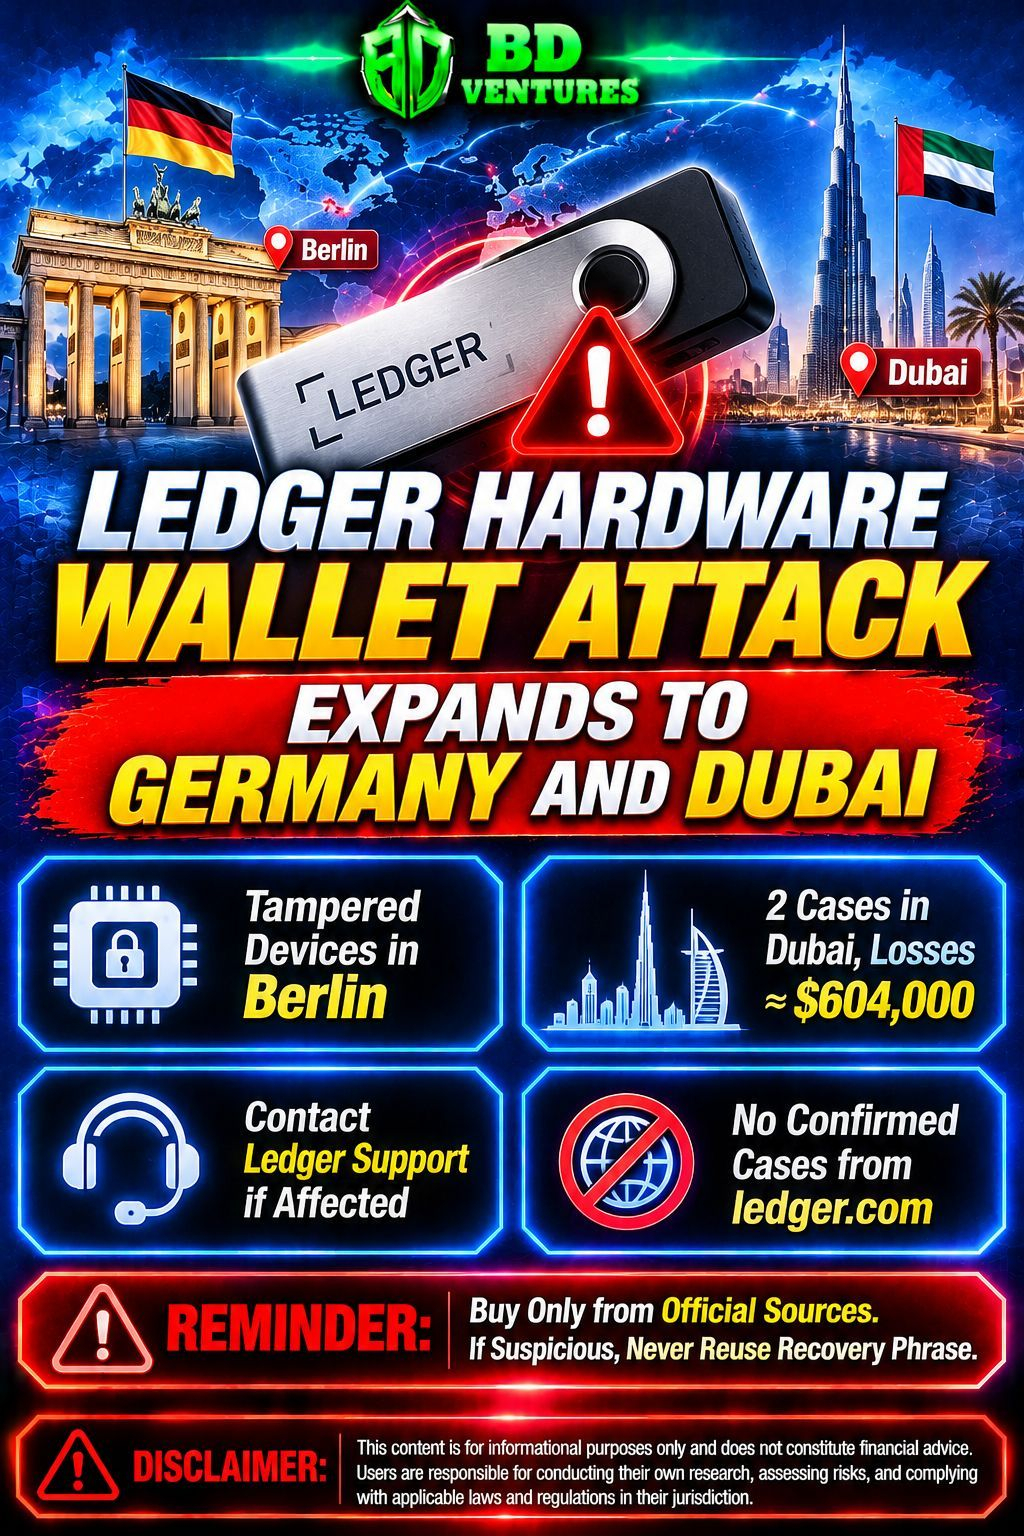
🚨 $BTC USERS ALERT: LEDGER HARDWARE COMPROMISE SPREADS TO GERMANY & DUBAI 🛡️
Ledger’s supply‑chain breach just jumped from Southeast Asia to Berlin and Dubai, hijacking devices before they ever hit a user’s desk. The hidden chip silently siphons recovery phrases during the initial setup, leaving wallets exposed before the first transaction.
Two Dubai investors felt the sting, losing over $600k combined, while Berlin users report similar thefts. Ledger stresses that devices bought from the official site remain clean, but the attack vector lives in the distribution chain, turning a trusted entry point into a liquidity trap for unsuspecting holders. 📊
If your Ledger wasn’t sourced directly, consider a full reset and move funds to a fresh cold‑storage address. 🛡️
💬 Are you certain your recovery phrase is still safe? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #Security #Crypto
🔥 💎
🚨 $BTC USERS ALERT: LEDGER HARDWARE COMPROMISE SPREADS TO GERMANY & DUBAI 🛡️
Ledger’s supply‑chain breach just jumped from Southeast Asia to Berlin and Dubai, hijacking devices before they ever hit a user’s desk. The hidden chip silently siphons recovery phrases during the initial setup, leaving wallets exposed before the first transaction.
Two Dubai investors felt the sting, losing over $600k combined, while Berlin users report similar thefts. Ledger stresses that devices bought from the official site remain clean, but the attack vector lives in the distribution chain, turning a trusted entry point into a liquidity trap for unsuspecting holders. 📊
If your Ledger wasn’t sourced directly, consider a full reset and move funds to a fresh cold‑storage address. 🛡️
💬 Are you certain your recovery phrase is still safe? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #Security #Crypto
🔥 💎
Ledger’s supply‑chain breach just jumped from Southeast Asia to Berlin and Dubai, hijacking devices before they ever hit a user’s desk. The hidden chip silently siphons recovery phrases during the initial setup, leaving wallets exposed before the first transaction.
Two Dubai investors felt the sting, losing over $600k combined, while Berlin users report similar thefts. Ledger stresses that devices bought from the official site remain clean, but the attack vector lives in the distribution chain, turning a trusted entry point into a liquidity trap for unsuspecting holders. 📊
If your Ledger wasn’t sourced directly, consider a full reset and move funds to a fresh cold‑storage address. 🛡️
💬 Are you certain your recovery phrase is still safe? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #Security #Crypto
🔥 💎
5
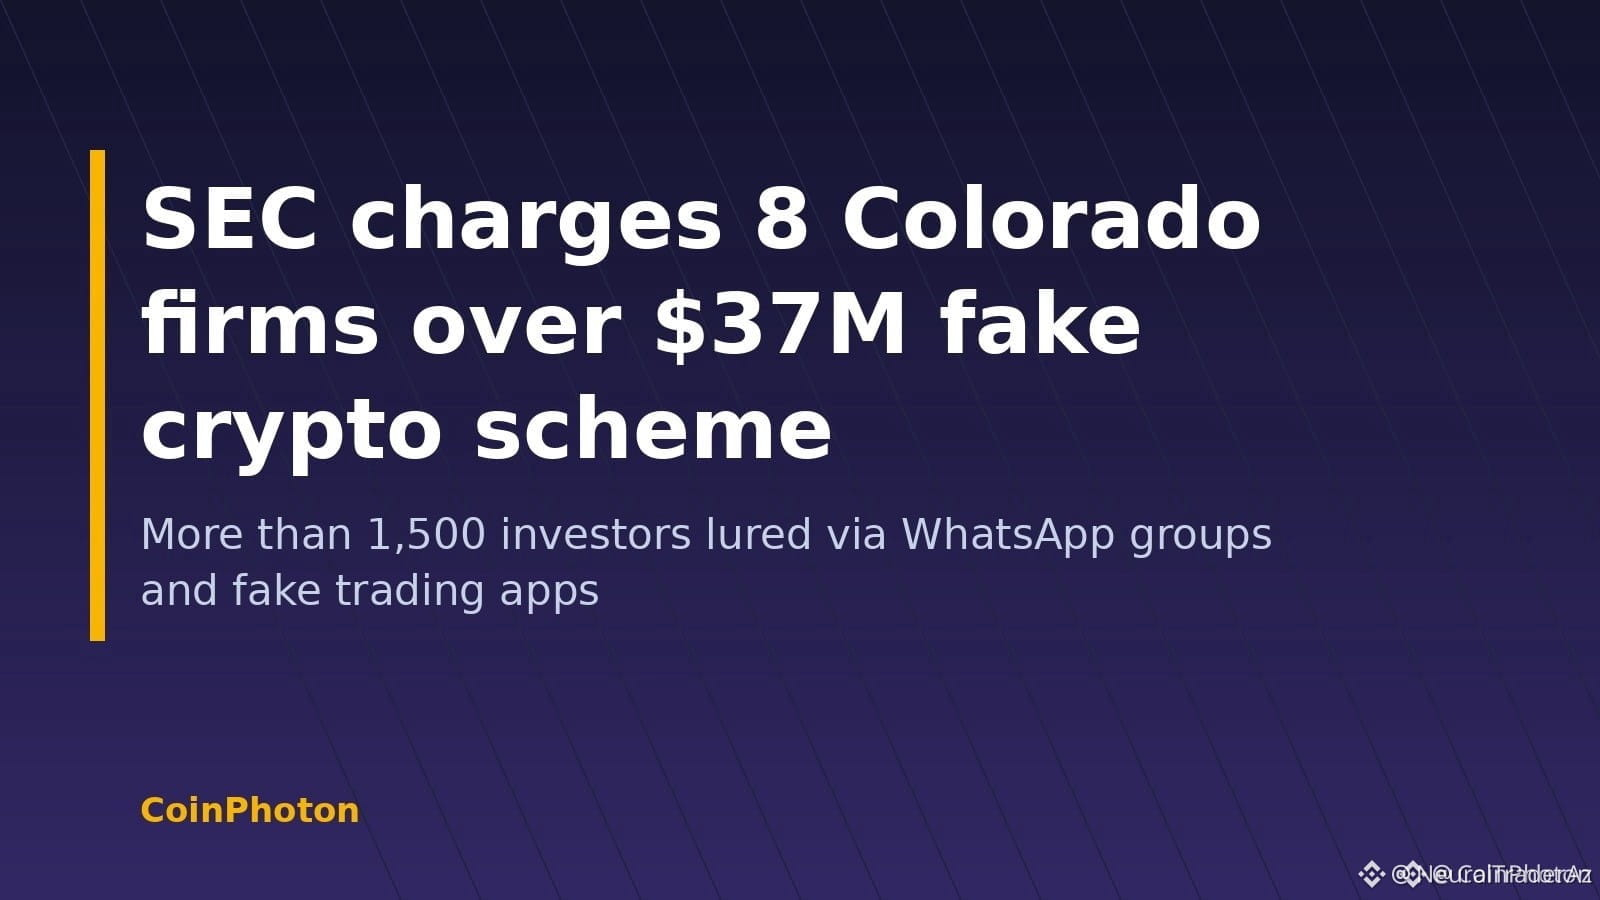
🚨 HOW A 37M FRAUD RING TARGETED $ETH HOLDERS THROUGH ILLUSIONARY APPS! ⚠️
Institutional-grade security isn't just about asset custody; it extends to rigorous counterparty verification. Recent regulatory actions exposed a predatory ring orchestrating fake platforms that harvested millions from unsuspecting participants using fabricated returns and locked withdrawals. 🔍
Smart money operates strictly within transparent environments with verifiable liquidity footprints. If an external entity promises unrealistic yields while routing traffic through off-chain messaging, structural danger is imminent. 🛡️
💡 How do you independently verify the structural integrity of a venue before deploying capital? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #RiskManagement #CryptoSafety
🛡️ 📊
🚨 HOW A 37M FRAUD RING TARGETED $ETH HOLDERS THROUGH ILLUSIONARY APPS! ⚠️
Institutional-grade security isn't just about asset custody; it extends to rigorous counterparty verification. Recent regulatory actions exposed a predatory ring orchestrating fake platforms that harvested millions from unsuspecting participants using fabricated returns and locked withdrawals. 🔍
Smart money operates strictly within transparent environments with verifiable liquidity footprints. If an external entity promises unrealistic yields while routing traffic through off-chain messaging, structural danger is imminent. 🛡️
💡 How do you independently verify the structural integrity of a venue before deploying capital? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #RiskManagement #CryptoSafety
🛡️ 📊
Institutional-grade security isn't just about asset custody; it extends to rigorous counterparty verification. Recent regulatory actions exposed a predatory ring orchestrating fake platforms that harvested millions from unsuspecting participants using fabricated returns and locked withdrawals. 🔍
Smart money operates strictly within transparent environments with verifiable liquidity footprints. If an external entity promises unrealistic yields while routing traffic through off-chain messaging, structural danger is imminent. 🛡️
💡 How do you independently verify the structural integrity of a venue before deploying capital? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #RiskManagement #CryptoSafety
🛡️ 📊
11
·
--
⚠️ Hackers Planted Crypto-Stealing Code on 178 Major Sites — Including Ledger
A flaw in Optimizely's signup flow let attackers inject malicious code into 178 organisations' websites — BBC, CNN, HSBC, Zoom, Salesforce, and hardware wallet maker Ledger.
The code swapped crypto wallet addresses (BTC, ETH, SOL, TRON + 5 more) so payments were redirected to the attacker, skimmed card details from on-page forms, and targeted older iPhones. About $7,040 was traced to attacker wallets so far.
Optimizely fixed the flaw and removed the code on Nov 16–17, but the incident is still listed as unresolved. Always verify the wallet address before you send.
Not financial advice.
#Crypto #Security #Ledger #Bitcoin
⚠️ Hackers Planted Crypto-Stealing Code on 178 Major Sites — Including Ledger
A flaw in Optimizely's signup flow let attackers inject malicious code into 178 organisations' websites — BBC, CNN, HSBC, Zoom, Salesforce, and hardware wallet maker Ledger.
The code swapped crypto wallet addresses (BTC, ETH, SOL, TRON + 5 more) so payments were redirected to the attacker, skimmed card details from on-page forms, and targeted older iPhones. About $7,040 was traced to attacker wallets so far.
Optimizely fixed the flaw and removed the code on Nov 16–17, but the incident is still listed as unresolved. Always verify the wallet address before you send.
Not financial advice.
#Crypto #Security #Ledger #Bitcoin
A flaw in Optimizely's signup flow let attackers inject malicious code into 178 organisations' websites — BBC, CNN, HSBC, Zoom, Salesforce, and hardware wallet maker Ledger.
The code swapped crypto wallet addresses (BTC, ETH, SOL, TRON + 5 more) so payments were redirected to the attacker, skimmed card details from on-page forms, and targeted older iPhones. About $7,040 was traced to attacker wallets so far.
Optimizely fixed the flaw and removed the code on Nov 16–17, but the incident is still listed as unresolved. Always verify the wallet address before you send.
Not financial advice.
#Crypto #Security #Ledger #Bitcoin
4

Security Risks Emerge as Illicit Funds Linked to Sky Ecosystem
Recent investigations have traced $518 million in illicit activity to a reserve backing stablecoins like DAI and USDS.
This activity involves funds allegedly used by North Korean hackers in high-profile events, including the 2025 Bybit hack.
The findings place the Sky stablecoin protocol under intense scrutiny regarding its institutional finance ambitions and decentralized design.
WHY IT MATTERS: Security vulnerabilities within stablecoin reserves pose a systemic risk to the stability and regulatory acceptance of decentralized finance platforms.
MARKET IMPACT: Bearish, as security breaches and links to illicit activity often cause temporary instability for affected protocols and tokens.
How important is security auditing when you choose which stablecoins to hold?
#Security #DeFi #Stablecoins
Security Risks Emerge as Illicit Funds Linked to Sky Ecosystem
Recent investigations have traced $518 million in illicit activity to a reserve backing stablecoins like DAI and USDS.
This activity involves funds allegedly used by North Korean hackers in high-profile events, including the 2025 Bybit hack.
The findings place the Sky stablecoin protocol under intense scrutiny regarding its institutional finance ambitions and decentralized design.
WHY IT MATTERS: Security vulnerabilities within stablecoin reserves pose a systemic risk to the stability and regulatory acceptance of decentralized finance platforms.
MARKET IMPACT: Bearish, as security breaches and links to illicit activity often cause temporary instability for affected protocols and tokens.
How important is security auditing when you choose which stablecoins to hold?
#Security #DeFi #Stablecoins
Recent investigations have traced $518 million in illicit activity to a reserve backing stablecoins like DAI and USDS.
This activity involves funds allegedly used by North Korean hackers in high-profile events, including the 2025 Bybit hack.
The findings place the Sky stablecoin protocol under intense scrutiny regarding its institutional finance ambitions and decentralized design.
WHY IT MATTERS: Security vulnerabilities within stablecoin reserves pose a systemic risk to the stability and regulatory acceptance of decentralized finance platforms.
MARKET IMPACT: Bearish, as security breaches and links to illicit activity often cause temporary instability for affected protocols and tokens.
How important is security auditing when you choose which stablecoins to hold?
#Security #DeFi #Stablecoins
1
320
🚨 $NAORIS EYEING SUPPLY-CHAIN SECURITY NARRATIVES AS TRADITIONAL FINANCE FACES VENDOR BREACHES
Recent legacy banking infrastructure vulnerabilities highlight the urgent demand for decentralized cryptographic verification across third-party networks. 📊 As institutional capital reassesses systemic counterparty exposure, on-chain security protocols are stepping into the spotlight.
Assets like $YB and $LUNC are also catching structural attention as market participants re-evaluate network integrity and data handling standards. 💡 The macroeconomic shift toward robust cybersecurity solutions creates an evolving liquidity footprint for specialized decentralized layers.
How is your portfolio positioned to capture capital rotation into infrastructure security plays? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NAORIS #Security #MarketStructure #Crypto
🔥
🚨 $NAORIS EYEING SUPPLY-CHAIN SECURITY NARRATIVES AS TRADITIONAL FINANCE FACES VENDOR BREACHES
Recent legacy banking infrastructure vulnerabilities highlight the urgent demand for decentralized cryptographic verification across third-party networks. 📊 As institutional capital reassesses systemic counterparty exposure, on-chain security protocols are stepping into the spotlight.
Assets like $YB and $LUNC are also catching structural attention as market participants re-evaluate network integrity and data handling standards. 💡 The macroeconomic shift toward robust cybersecurity solutions creates an evolving liquidity footprint for specialized decentralized layers.
How is your portfolio positioned to capture capital rotation into infrastructure security plays? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NAORIS #Security #MarketStructure #Crypto
🔥
Recent legacy banking infrastructure vulnerabilities highlight the urgent demand for decentralized cryptographic verification across third-party networks. 📊 As institutional capital reassesses systemic counterparty exposure, on-chain security protocols are stepping into the spotlight.
Assets like $YB and $LUNC are also catching structural attention as market participants re-evaluate network integrity and data handling standards. 💡 The macroeconomic shift toward robust cybersecurity solutions creates an evolving liquidity footprint for specialized decentralized layers.
How is your portfolio positioned to capture capital rotation into infrastructure security plays? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NAORIS #Security #MarketStructure #Crypto
🔥
6

·
--
Traders on X are sounding the alarm, and this one is worth your attention. 🚨
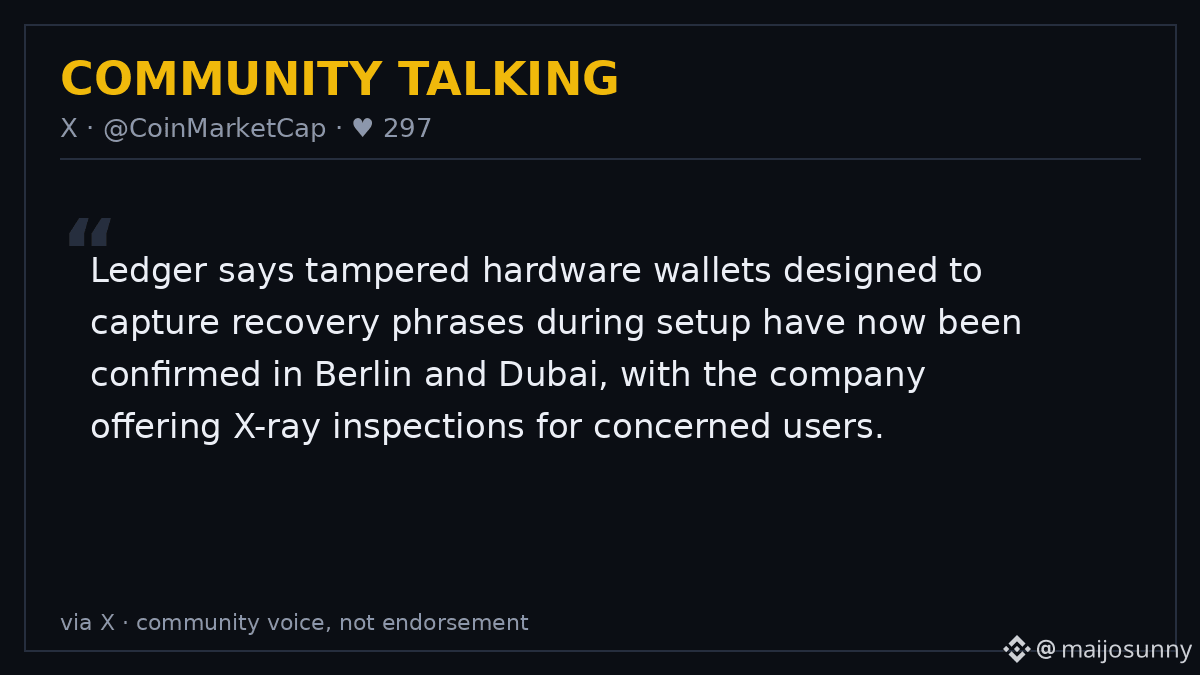
Ledger just confirmed tampered hardware wallets in Berlin, and it is investigating two more suspected units in Dubai. Every confirmed device carries the same physical modification, built to capture your 24-word recovery phrase during setup. On-chain investigators have traced a suspected ~$87M drain linked to the implants.
Ledger says there is no flaw in its chip or OS, and no confirmed case involves a device bought on ledger.com. Every tampered unit so far came through a third-party reseller.
Why it matters: this started as a Southeast Asia incident in October. Now it is in Europe, and Ledger expects more units to surface.
Action Required:
• Bought a Ledger in Berlin since Jan 2026? Contact Ledger Support
• Never set up or restore a wallet on a suspect device
• Move funds to a fresh wallet with a brand-new recovery phrase
• Free X-ray inspections at Ledger's Vierzon, France factory, for a limited time
Ledger will never ask for your 24 words. Anyone who does is a scammer.
Is your $BTC sitting on a Ledger bought from a reseller, or straight from ledger.com? 👇
Not financial advice. DYOR.
#crypto #Ledger #Security
Traders on X are sounding the alarm, and this one is worth your attention. 🚨
Ledger just confirmed tampered hardware wallets in Berlin, and it is investigating two more suspected units in Dubai. Every confirmed device carries the same physical modification, built to capture your 24-word recovery phrase during setup. On-chain investigators have traced a suspected ~$87M drain linked to the implants.
Ledger says there is no flaw in its chip or OS, and no confirmed case involves a device bought on ledger.com. Every tampered unit so far came through a third-party reseller.
Why it matters: this started as a Southeast Asia incident in October. Now it is in Europe, and Ledger expects more units to surface.
Action Required:
• Bought a Ledger in Berlin since Jan 2026? Contact Ledger Support
• Never set up or restore a wallet on a suspect device
• Move funds to a fresh wallet with a brand-new recovery phrase
• Free X-ray inspections at Ledger's Vierzon, France factory, for a limited time
Ledger will never ask for your 24 words. Anyone who does is a scammer.
Is your $BTC sitting on a Ledger bought from a reseller, or straight from ledger.com? 👇
Not financial advice. DYOR.
#crypto #Ledger #Security
Ledger just confirmed tampered hardware wallets in Berlin, and it is investigating two more suspected units in Dubai. Every confirmed device carries the same physical modification, built to capture your 24-word recovery phrase during setup. On-chain investigators have traced a suspected ~$87M drain linked to the implants.
Ledger says there is no flaw in its chip or OS, and no confirmed case involves a device bought on ledger.com. Every tampered unit so far came through a third-party reseller.
Why it matters: this started as a Southeast Asia incident in October. Now it is in Europe, and Ledger expects more units to surface.
Action Required:
• Bought a Ledger in Berlin since Jan 2026? Contact Ledger Support
• Never set up or restore a wallet on a suspect device
• Move funds to a fresh wallet with a brand-new recovery phrase
• Free X-ray inspections at Ledger's Vierzon, France factory, for a limited time
Ledger will never ask for your 24 words. Anyone who does is a scammer.
Is your $BTC sitting on a Ledger bought from a reseller, or straight from ledger.com? 👇
Not financial advice. DYOR.
#crypto #Ledger #Security
16

·
--
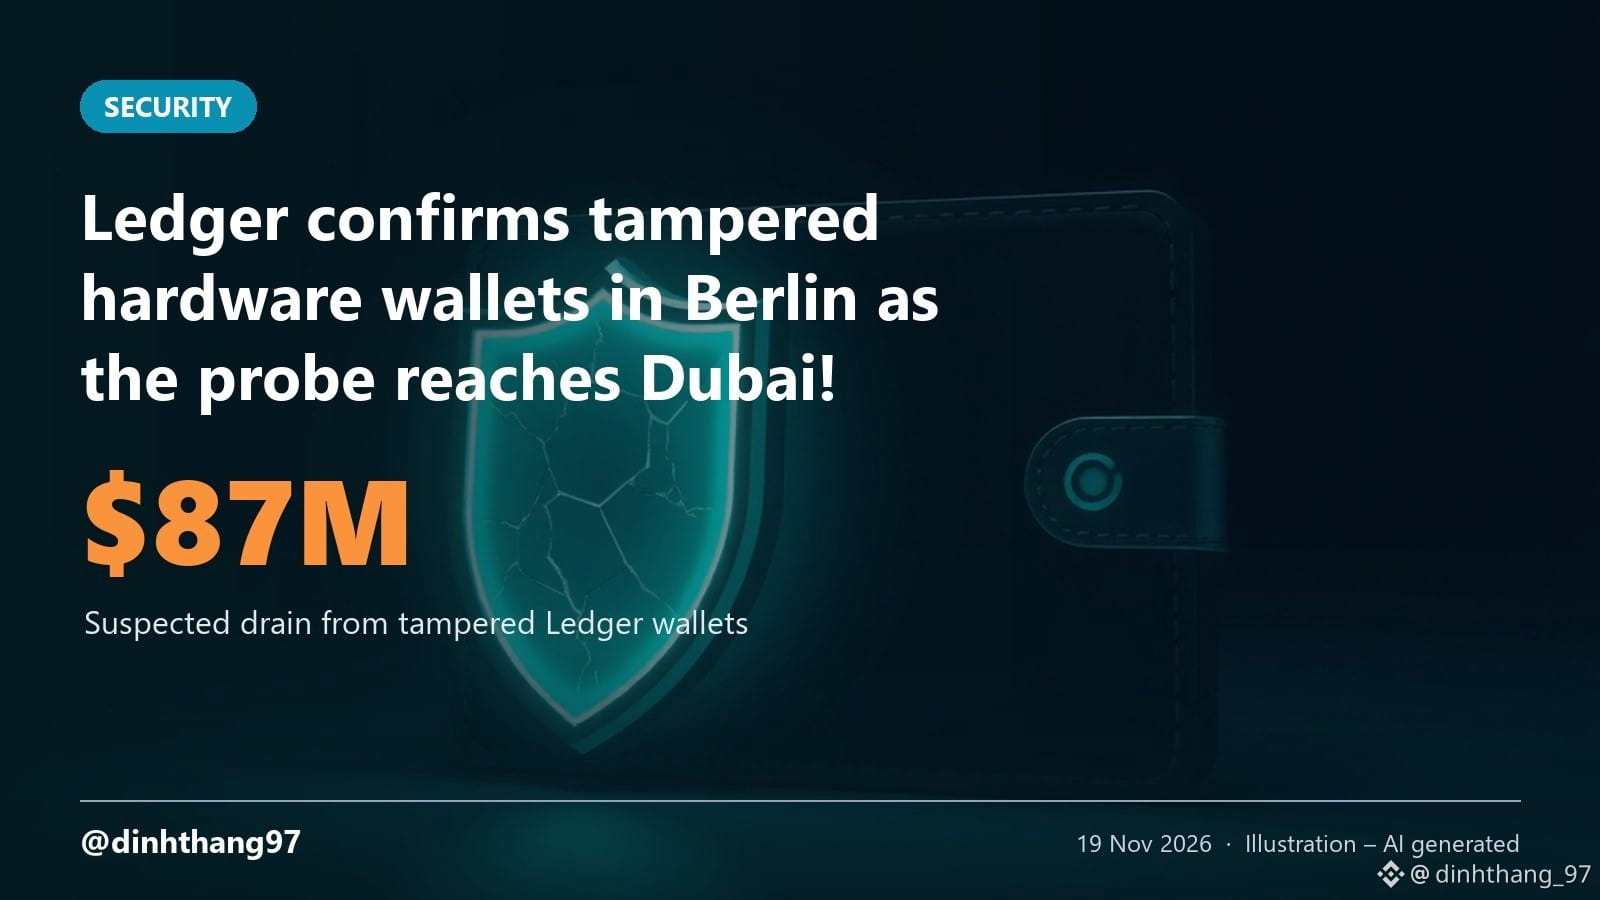
Ledger confirms tampered hardware wallets in Berlin as the probe reaches Dubai!
According to Decrypt, Cointelegraph and The Defiant, the modified devices are built to capture the recovery phrase during setup:
🔴 About $87M suspected drained from hundreds of victim wallets
🔸 Berlin: buyers since January 2026 should contact support
🔸 Dubai: two suspect units from a retail store
🔸 One user reported a $320,000 loss after a Berlin purchase
Here's what caught my attention: Ledger says its secure chip and OS are not flawed, and no confirmed case involves ledger.com purchases.
Of course, Ledger also expects more affected devices to surface.
Only buy hardware wallets direct from the maker and never share your recovery phrase.
Not financial advice, DYOR.
#Ledger #Security
Ledger confirms tampered hardware wallets in Berlin as the probe reaches Dubai!
According to Decrypt, Cointelegraph and The Defiant, the modified devices are built to capture the recovery phrase during setup:
🔴 About $87M suspected drained from hundreds of victim wallets
🔸 Berlin: buyers since January 2026 should contact support
🔸 Dubai: two suspect units from a retail store
🔸 One user reported a $320,000 loss after a Berlin purchase
Here's what caught my attention: Ledger says its secure chip and OS are not flawed, and no confirmed case involves ledger.com purchases.
Of course, Ledger also expects more affected devices to surface.
Only buy hardware wallets direct from the maker and never share your recovery phrase.
Not financial advice, DYOR.
#Ledger #Security
According to Decrypt, Cointelegraph and The Defiant, the modified devices are built to capture the recovery phrase during setup:
🔴 About $87M suspected drained from hundreds of victim wallets
🔸 Berlin: buyers since January 2026 should contact support
🔸 Dubai: two suspect units from a retail store
🔸 One user reported a $320,000 loss after a Berlin purchase
Here's what caught my attention: Ledger says its secure chip and OS are not flawed, and no confirmed case involves ledger.com purchases.
Of course, Ledger also expects more affected devices to surface.
Only buy hardware wallets direct from the maker and never share your recovery phrase.
Not financial advice, DYOR.
#Ledger #Security
138
Article
Trezor Hit by Third Data Breach in 2023: Shipping Partners BlamedTrezor users are facing new risks after another major data breach linked to a third-party shipping partner, raising big questions about supply chain security in the crypto space.
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
Trezor Hit by Third Data Breach in 2023: Shipping Partners Blamed
Trezor users are facing new risks after another major data breach linked to a third-party shipping partner, raising big questions about supply chain security in the crypto space.
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
95

The recent K3 Capital exploit highlights a critical vulnerability in how block builders prioritize transactions. With over half of the stolen $3.4 million in the sBOLD vault hack flowing directly to MEV-boosted builders, it underscores how automation and gas bidding wars can facilitate malicious activity on-chain. This incident serves as a stark reminder that the current block construction process remains a double-edged sword for network integrity. Security in DeFi is truly paramount. $ETH #Ethereum #DeFi #Security
The recent K3 Capital exploit highlights a critical vulnerability in how block builders prioritize transactions. With over half of the stolen $3.4 million in the sBOLD vault hack flowing directly to MEV-boosted builders, it underscores how automation and gas bidding wars can facilitate malicious activity on-chain. This incident serves as a stark reminder that the current block construction process remains a double-edged sword for network integrity. Security in DeFi is truly paramount. $ETH #Ethereum #DeFi #Security
12
With online fraud losses hitting staggering highs in 2025, regulatory pressure is shifting toward aggressive intervention. The new administration's dedicated center targeting scam payments could reshape compliance across the board. While this aims to protect everyday users, it also means traditional rails and digital assets alike will face heightened scrutiny. Expect stricter oversight on cross-border transactions as authorities try to cut off illicit flows at the source. #CryptoRegulation #Security #FraudPrevention
With online fraud losses hitting staggering highs in 2025, regulatory pressure is shifting toward aggressive intervention. The new administration's dedicated center targeting scam payments could reshape compliance across the board. While this aims to protect everyday users, it also means traditional rails and digital assets alike will face heightened scrutiny. Expect stricter oversight on cross-border transactions as authorities try to cut off illicit flows at the source. #CryptoRegulation #Security #FraudPrevention
3
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanBTCReboundAfterFallingBelow60K?
365,279 views
1,540 Discussing
2
#GlobalStocksFaceLongestLosingStreakSince2023
120,655 views
1,088 Discussing
3
#BlackRockIBITPostsRecord$541MSingleDayOutflow
648 views
17 Discussing
4
#AnthropicPlungesTowardIPOPriceonDay2
58,891 views
593 Discussing
5
#TwentyOneCapitalAdds172.25BTC
10,865 views
161 Discussing
6
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
924 views
14 Discussing
7
#BNBDropsBelow540USDTWith8.46%DailyDecline
32,204 views
273 Discussing
8
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,033 views
14 Discussing
9
#BitMineFaces$10.1BUnrealizedETHLoss
1,985 views
18 Discussing
10
#StrategyReports$35BNetReserves
1,867 views
18 Discussing