
#hardwarewallet
hardwarewallet
145,580 views
459 Discussing
Hot
Latest

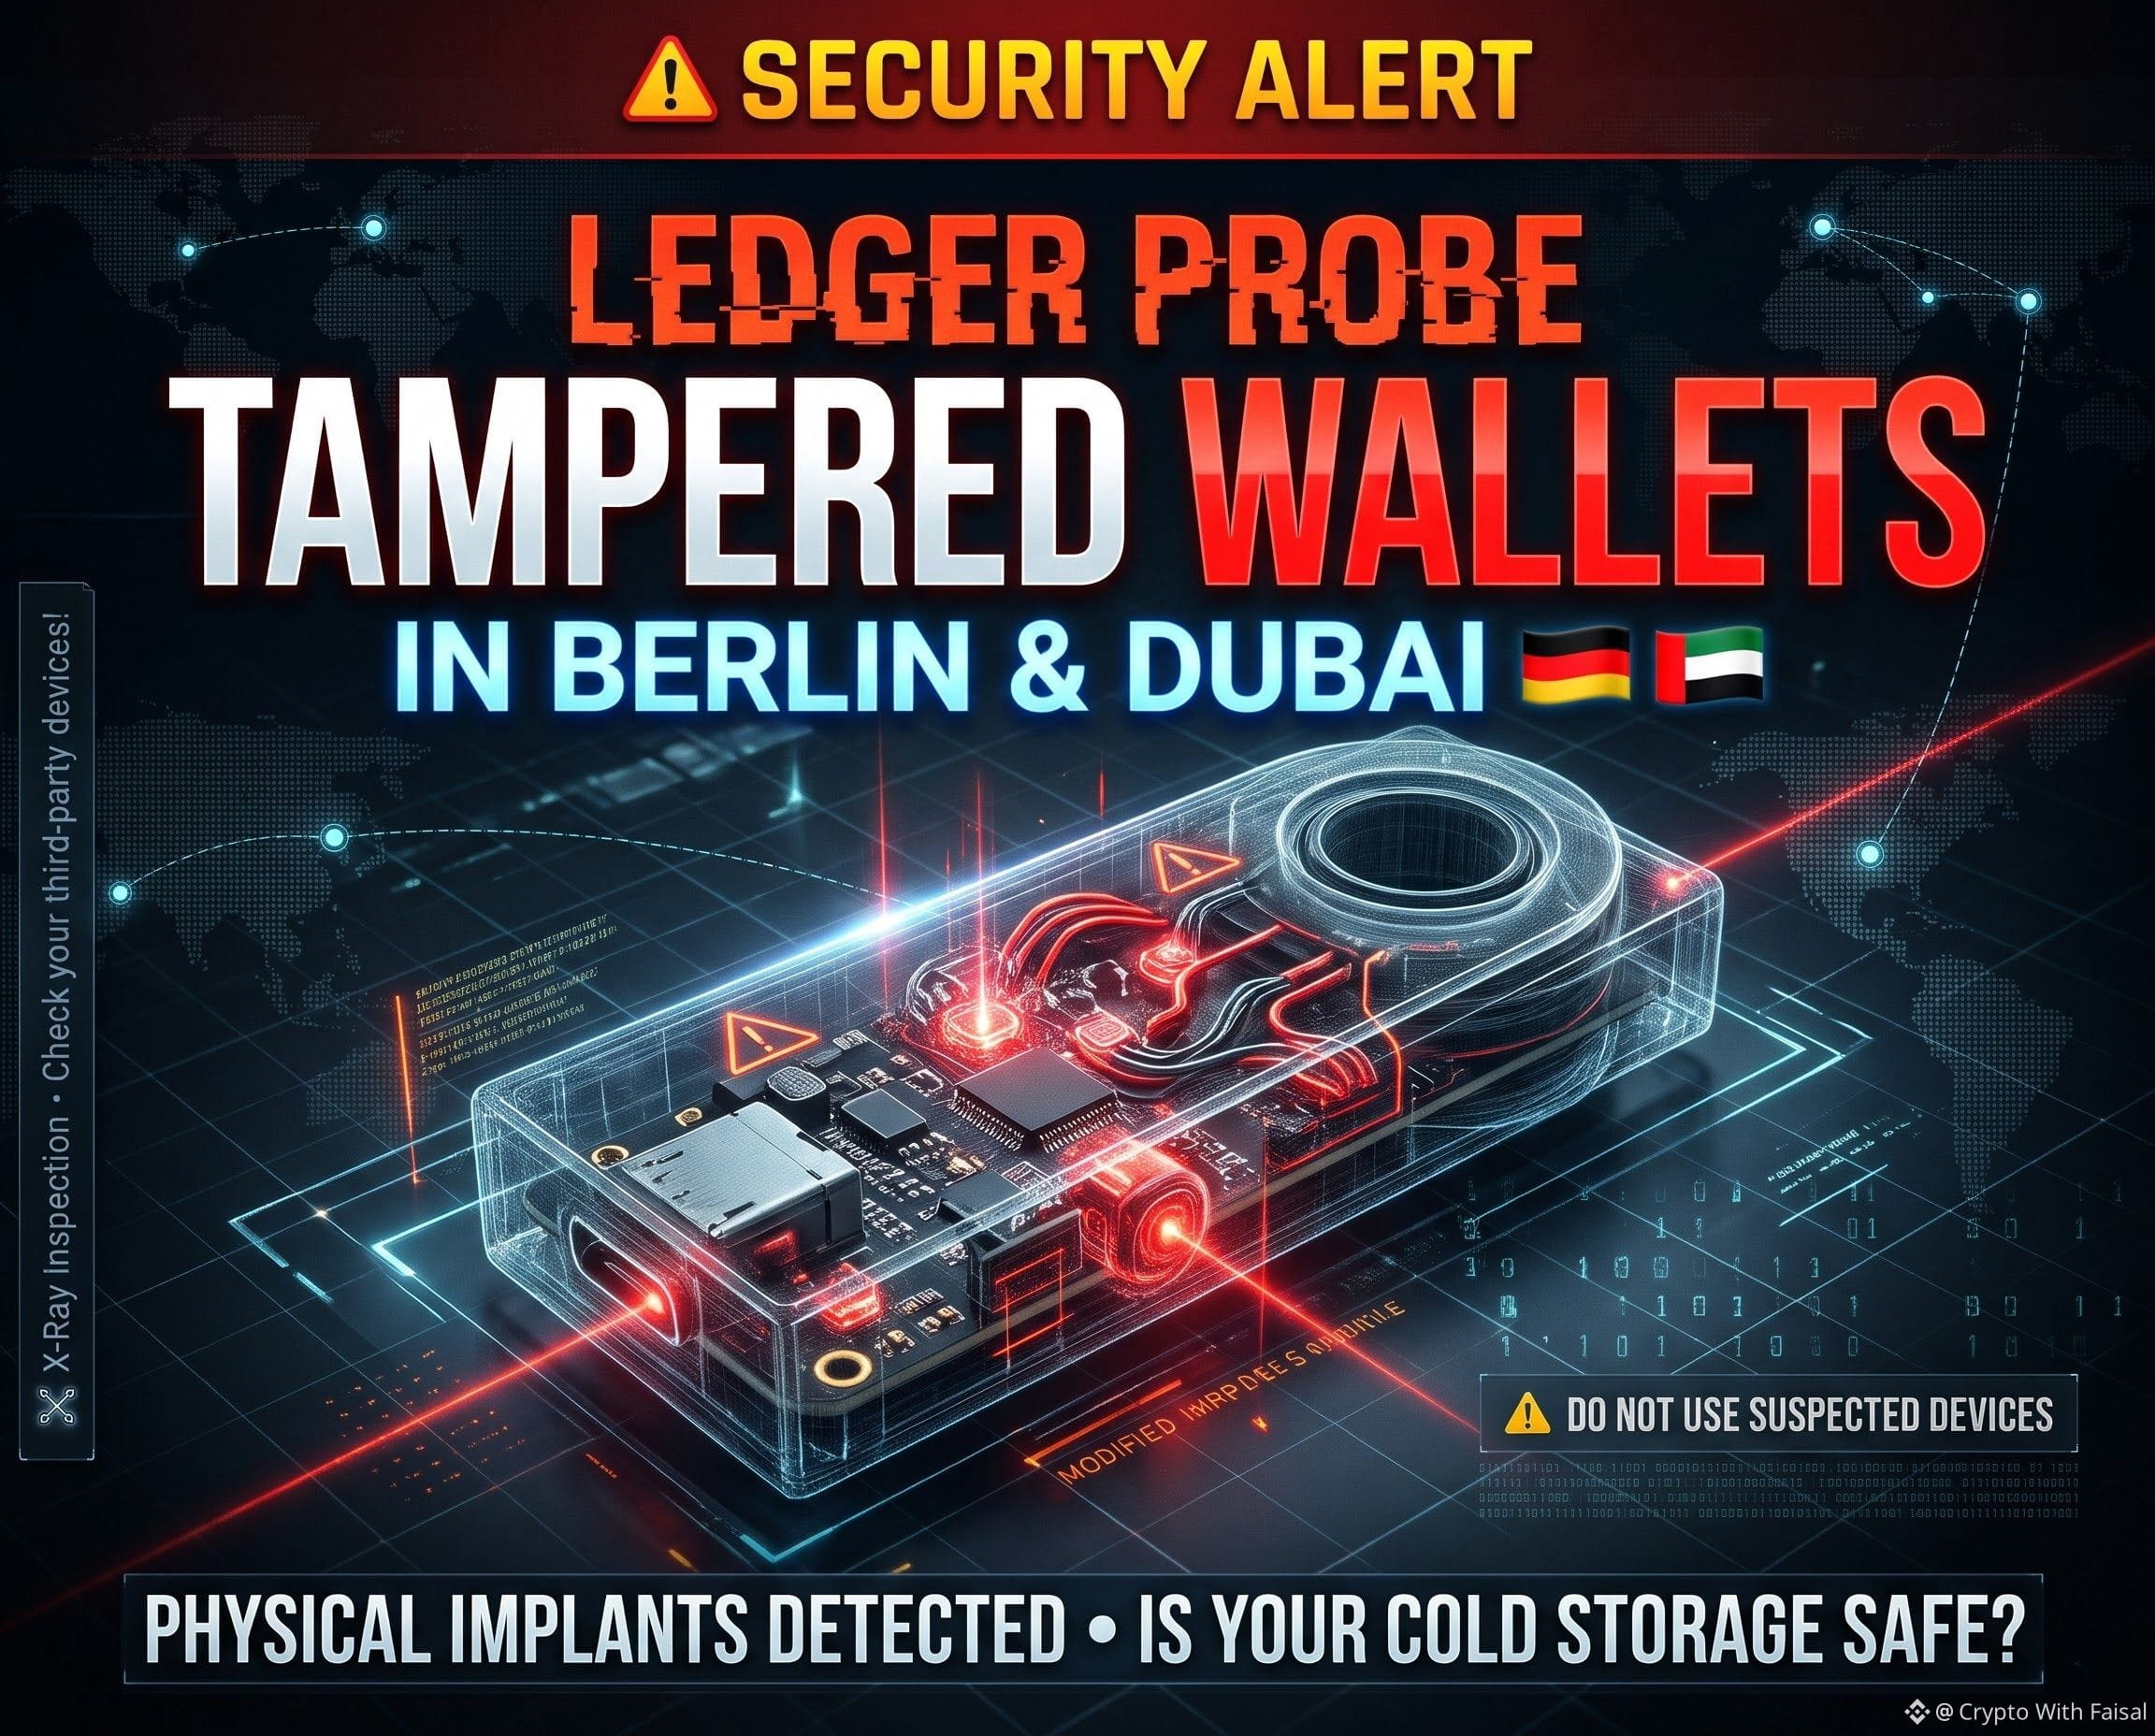
🚨 Security Alert: Ledger confirmed physically tampered hardware wallets in Berlin and is probing two suspected units in Dubai.
Key facts every trader needs to know:
🔹 The Threat: Affected units carry a physical implant built to steal your recovery phrase during setup—part of the same third-party reseller incident uncovered in Southeast Asia in October.
🔹 What Is Safe: Ledger confirmed zero flaws in its secure chip or OS, and zero cases tied to devices bought directly from ledger.com.
🔹 Next Steps: Bitquery estimates ~$1.68M was drained across 16 wallets in both cities. If you bought a Ledger in Berlin since Jan 2026 or from a third party in Dubai, stop using it immediately. Contact Ledger Support for a factory X-ray check in France and move funds to a fresh wallet.
Never buy cold storage from middlemen. Do you buy hardware wallets direct only, or through resellers? 👇
$BTC $ETH $EVAA
{future}(EVAAUSDT)
{future}(BTCUSDT)
{future}(ETHUSDT)
#ledgerprobestamperedwalletsinberlinanddubai #CryptoSecurity #SelfCustody #HardwareWallet
🚨 Security Alert: Ledger confirmed physically tampered hardware wallets in Berlin and is probing two suspected units in Dubai.
Key facts every trader needs to know:
🔹 The Threat: Affected units carry a physical implant built to steal your recovery phrase during setup—part of the same third-party reseller incident uncovered in Southeast Asia in October.
🔹 What Is Safe: Ledger confirmed zero flaws in its secure chip or OS, and zero cases tied to devices bought directly from ledger.com.
🔹 Next Steps: Bitquery estimates ~$1.68M was drained across 16 wallets in both cities. If you bought a Ledger in Berlin since Jan 2026 or from a third party in Dubai, stop using it immediately. Contact Ledger Support for a factory X-ray check in France and move funds to a fresh wallet.
Never buy cold storage from middlemen. Do you buy hardware wallets direct only, or through resellers? 👇
$BTC $ETH $EVAA
#ledgerprobestamperedwalletsinberlinanddubai #CryptoSecurity #SelfCustody #HardwareWallet
Key facts every trader needs to know:
🔹 The Threat: Affected units carry a physical implant built to steal your recovery phrase during setup—part of the same third-party reseller incident uncovered in Southeast Asia in October.
🔹 What Is Safe: Ledger confirmed zero flaws in its secure chip or OS, and zero cases tied to devices bought directly from ledger.com.
🔹 Next Steps: Bitquery estimates ~$1.68M was drained across 16 wallets in both cities. If you bought a Ledger in Berlin since Jan 2026 or from a third party in Dubai, stop using it immediately. Contact Ledger Support for a factory X-ray check in France and move funds to a fresh wallet.
Never buy cold storage from middlemen. Do you buy hardware wallets direct only, or through resellers? 👇
$BTC $ETH $EVAA
#ledgerprobestamperedwalletsinberlinanddubai #CryptoSecurity #SelfCustody #HardwareWallet
4
3.4k

🚨 $BTC USERS ALERT: LEDGER HARDWARE COMPROMISE SPREADS TO GERMANY & DUBAI 🛡️
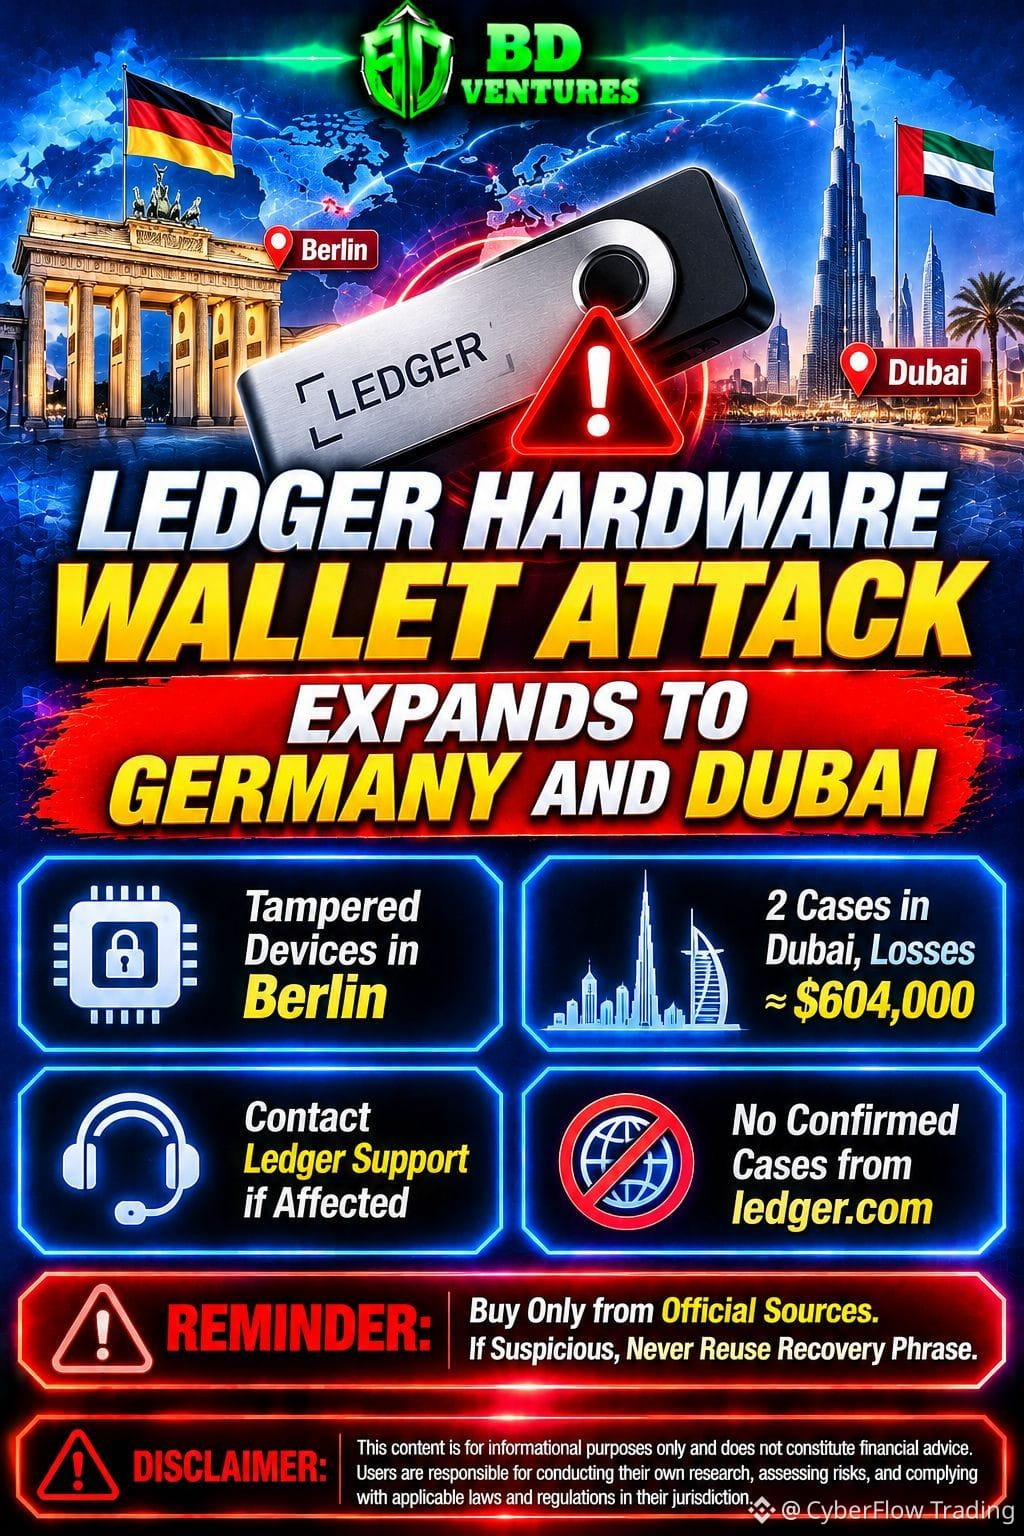
Ledger’s supply‑chain breach just jumped from Southeast Asia to Berlin and Dubai, hijacking devices before they ever hit a user’s desk. The hidden chip silently siphons recovery phrases during the initial setup, leaving wallets exposed before the first transaction.
Two Dubai investors felt the sting, losing over $600k combined, while Berlin users report similar thefts. Ledger stresses that devices bought from the official site remain clean, but the attack vector lives in the distribution chain, turning a trusted entry point into a liquidity trap for unsuspecting holders. 📊
If your Ledger wasn’t sourced directly, consider a full reset and move funds to a fresh cold‑storage address. 🛡️
💬 Are you certain your recovery phrase is still safe? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #Security #Crypto
🔥 💎
🚨 $BTC USERS ALERT: LEDGER HARDWARE COMPROMISE SPREADS TO GERMANY & DUBAI 🛡️
Ledger’s supply‑chain breach just jumped from Southeast Asia to Berlin and Dubai, hijacking devices before they ever hit a user’s desk. The hidden chip silently siphons recovery phrases during the initial setup, leaving wallets exposed before the first transaction.
Two Dubai investors felt the sting, losing over $600k combined, while Berlin users report similar thefts. Ledger stresses that devices bought from the official site remain clean, but the attack vector lives in the distribution chain, turning a trusted entry point into a liquidity trap for unsuspecting holders. 📊
If your Ledger wasn’t sourced directly, consider a full reset and move funds to a fresh cold‑storage address. 🛡️
💬 Are you certain your recovery phrase is still safe? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #Security #Crypto
🔥 💎
Ledger’s supply‑chain breach just jumped from Southeast Asia to Berlin and Dubai, hijacking devices before they ever hit a user’s desk. The hidden chip silently siphons recovery phrases during the initial setup, leaving wallets exposed before the first transaction.
Two Dubai investors felt the sting, losing over $600k combined, while Berlin users report similar thefts. Ledger stresses that devices bought from the official site remain clean, but the attack vector lives in the distribution chain, turning a trusted entry point into a liquidity trap for unsuspecting holders. 📊
If your Ledger wasn’t sourced directly, consider a full reset and move funds to a fresh cold‑storage address. 🛡️
💬 Are you certain your recovery phrase is still safe? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #Security #Crypto
🔥 💎
5

·
--
🚨 $BTC ALERT: LEDGER HARDWARE COMPROMISED IN BERLIN & DUBAI 🦈
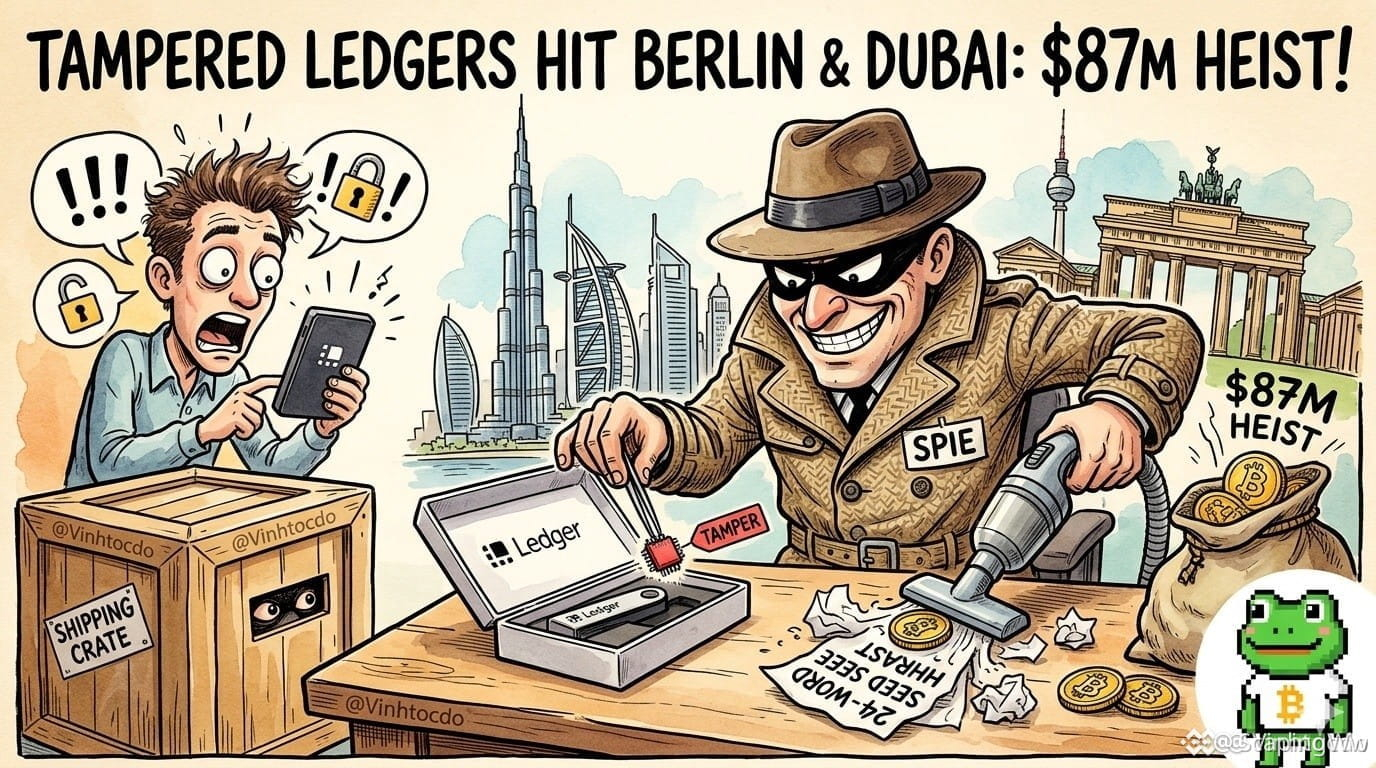
📊 The supply‑chain breach rippled from Southeast Asia to Europe, with tampered chips siphoning 24 recovery seeds the moment a device boots. Ledger insists factory chips are clean, but the physical meddling proves that a rogue insider can turn a trusted vault into a back‑door.
💡 Traders, treat any Ledger purchased off‑exchange or through gray‑market channels as compromised. If you bought a device in Berlin after Jan 1, migrate assets to a fresh wallet on a verified source ASAP. 🛡️
💬 How are you securing your cold storage after this news? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #CryptoSecurity #Ledger #CryptoNews
🔥 💎
🚨 $BTC ALERT: LEDGER HARDWARE COMPROMISED IN BERLIN & DUBAI 🦈
📊 The supply‑chain breach rippled from Southeast Asia to Europe, with tampered chips siphoning 24 recovery seeds the moment a device boots. Ledger insists factory chips are clean, but the physical meddling proves that a rogue insider can turn a trusted vault into a back‑door.
💡 Traders, treat any Ledger purchased off‑exchange or through gray‑market channels as compromised. If you bought a device in Berlin after Jan 1, migrate assets to a fresh wallet on a verified source ASAP. 🛡️
💬 How are you securing your cold storage after this news? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #CryptoSecurity #Ledger #CryptoNews
🔥 💎
📊 The supply‑chain breach rippled from Southeast Asia to Europe, with tampered chips siphoning 24 recovery seeds the moment a device boots. Ledger insists factory chips are clean, but the physical meddling proves that a rogue insider can turn a trusted vault into a back‑door.
💡 Traders, treat any Ledger purchased off‑exchange or through gray‑market channels as compromised. If you bought a device in Berlin after Jan 1, migrate assets to a fresh wallet on a verified source ASAP. 🛡️
💬 How are you securing your cold storage after this news? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #HardwareWallet #CryptoSecurity #Ledger #CryptoNews
🔥 💎
5

Security concerns are escalating globally as Ledger-related device tampering reports spread from Dubai to Berlin. While the company is offering urgent factory inspections and advising affected users to migrate funds immediately, this incident highlights a glaring vulnerability in hardware supply chains. Physical security is just as critical as seed phrase management in crypto. If you bought a device recently, double-check your hardware integrity and stay vigilant against sophisticated physical exploits. #CryptoSecurity #Ledger #HardwareWallet
Security concerns are escalating globally as Ledger-related device tampering reports spread from Dubai to Berlin. While the company is offering urgent factory inspections and advising affected users to migrate funds immediately, this incident highlights a glaring vulnerability in hardware supply chains. Physical security is just as critical as seed phrase management in crypto. If you bought a device recently, double-check your hardware integrity and stay vigilant against sophisticated physical exploits. #CryptoSecurity #Ledger #HardwareWallet
1
3
🔥Ledger Hardware Wallet Security Alert: Tampered Devices Found in Berlin, Dubai Probe Underway
A major security warning has emerged for crypto investors as Ledger expands its investigation into tampered hardware wallets.
According to Ledger's November 18 update, the company has confirmed modified hardware wallets in Berlin, Germany, and is investigating two suspected devices in Dubai, UAE.
The attackers allegedly installed hidden components inside genuine Ledger devices designed to capture users' 24-word recovery phrases during wallet setup.
Two Dubai users have reportedly lost a combined $604,000 in cryptocurrency. However, these losses have not been officially confirmed by Ledger.
Ledger says its Secure Element chip and operating system have no identified vulnerabilities, and no affected devices purchased directly from its official website have been confirmed.
What Users Should Know:
- Avoid purchasing hardware wallets from unverified sellers.
- Contact Ledger Support if you purchased a device in Berlin since January 2026 or in Dubai.
- Never share your 24-word recovery phrase.
- Stop using any device you suspect has been tampered with.
My Take:
This incident highlights an important reality: even hardware wallets can face supply-chain security risks. Protecting crypto is not just about choosing the right wallet; it is also about verifying where your device comes from.
Security must always come before convenience.
#Ledger #Bitcoin #HardwareWallet
$BTC
{spot}(BTCUSDT)
🔥Ledger Hardware Wallet Security Alert: Tampered Devices Found in Berlin, Dubai Probe Underway
A major security warning has emerged for crypto investors as Ledger expands its investigation into tampered hardware wallets.
According to Ledger's November 18 update, the company has confirmed modified hardware wallets in Berlin, Germany, and is investigating two suspected devices in Dubai, UAE.
The attackers allegedly installed hidden components inside genuine Ledger devices designed to capture users' 24-word recovery phrases during wallet setup.
Two Dubai users have reportedly lost a combined $604,000 in cryptocurrency. However, these losses have not been officially confirmed by Ledger.
Ledger says its Secure Element chip and operating system have no identified vulnerabilities, and no affected devices purchased directly from its official website have been confirmed.
What Users Should Know:
- Avoid purchasing hardware wallets from unverified sellers.
- Contact Ledger Support if you purchased a device in Berlin since January 2026 or in Dubai.
- Never share your 24-word recovery phrase.
- Stop using any device you suspect has been tampered with.
My Take:
This incident highlights an important reality: even hardware wallets can face supply-chain security risks. Protecting crypto is not just about choosing the right wallet; it is also about verifying where your device comes from.
Security must always come before convenience.
#Ledger #Bitcoin #HardwareWallet
$BTC
A major security warning has emerged for crypto investors as Ledger expands its investigation into tampered hardware wallets.
According to Ledger's November 18 update, the company has confirmed modified hardware wallets in Berlin, Germany, and is investigating two suspected devices in Dubai, UAE.
The attackers allegedly installed hidden components inside genuine Ledger devices designed to capture users' 24-word recovery phrases during wallet setup.
Two Dubai users have reportedly lost a combined $604,000 in cryptocurrency. However, these losses have not been officially confirmed by Ledger.
Ledger says its Secure Element chip and operating system have no identified vulnerabilities, and no affected devices purchased directly from its official website have been confirmed.
What Users Should Know:
- Avoid purchasing hardware wallets from unverified sellers.
- Contact Ledger Support if you purchased a device in Berlin since January 2026 or in Dubai.
- Never share your 24-word recovery phrase.
- Stop using any device you suspect has been tampered with.
My Take:
This incident highlights an important reality: even hardware wallets can face supply-chain security risks. Protecting crypto is not just about choosing the right wallet; it is also about verifying where your device comes from.
Security must always come before convenience.
#Ledger #Bitcoin #HardwareWallet
$BTC
1
57

·
--
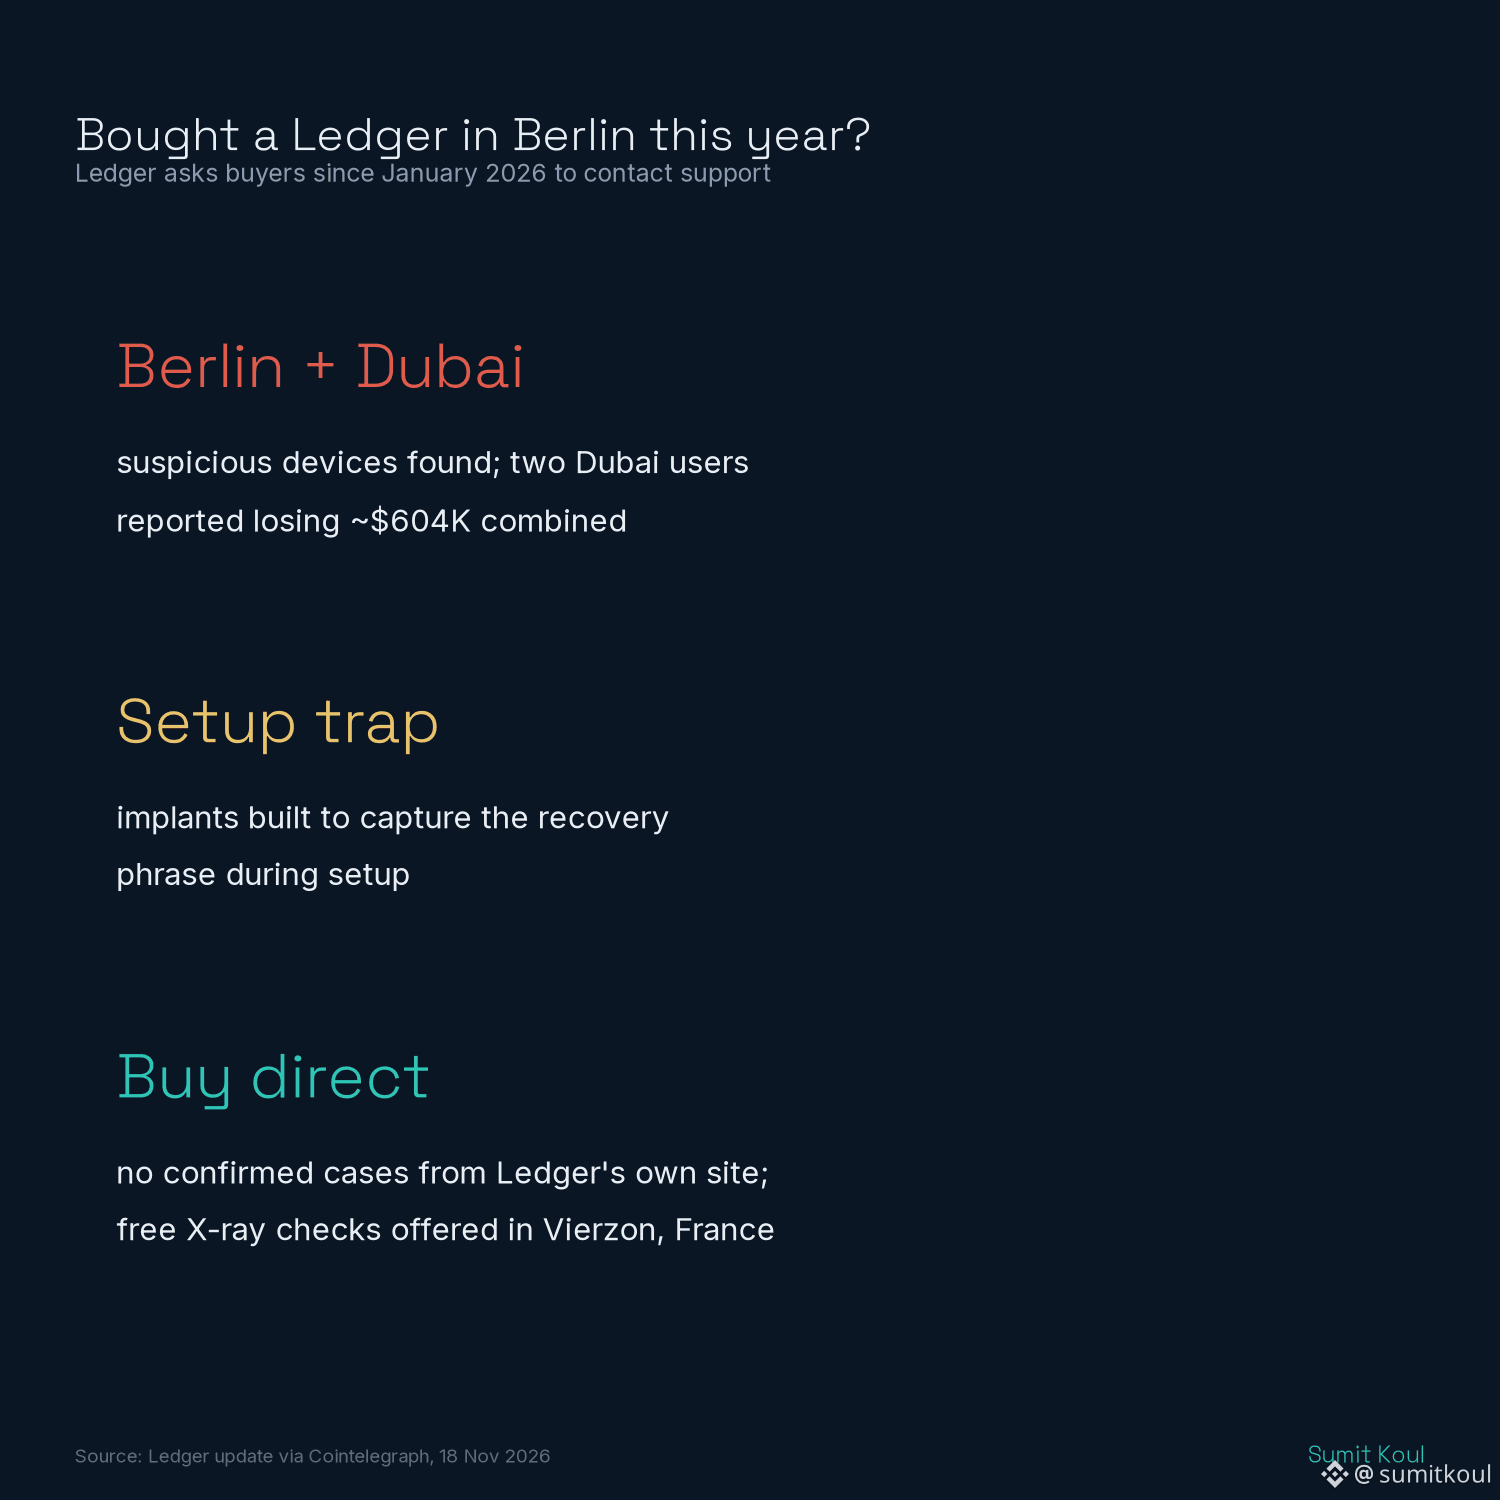
Bought a Ledger in Berlin this year? Read this before you load it. 🔐
Ledger's 18 Nov update:
• Suspicious tampered devices found in Berlin. Buyers since January 2026 should contact support
• Tampered devices also reported in Dubai. Two users said they lost ~$604K combined
• The implants are built to steal the recovery phrase during setup
Ledger says its chip and software weren't hacked, and no cases involve devices bought from its own website. It's offering free X-ray checks in France.
Buy hardware wallets only from the maker. Never use a pre-filled seed card. Send this to anyone holding $BTC on a new device. 👇
#Ledger #CryptoSecurity #HardwareWallet
Bought a Ledger in Berlin this year? Read this before you load it. 🔐
Ledger's 18 Nov update:
• Suspicious tampered devices found in Berlin. Buyers since January 2026 should contact support
• Tampered devices also reported in Dubai. Two users said they lost ~$604K combined
• The implants are built to steal the recovery phrase during setup
Ledger says its chip and software weren't hacked, and no cases involve devices bought from its own website. It's offering free X-ray checks in France.
Buy hardware wallets only from the maker. Never use a pre-filled seed card. Send this to anyone holding $BTC on a new device. 👇
#Ledger #CryptoSecurity #HardwareWallet
Ledger's 18 Nov update:
• Suspicious tampered devices found in Berlin. Buyers since January 2026 should contact support
• Tampered devices also reported in Dubai. Two users said they lost ~$604K combined
• The implants are built to steal the recovery phrase during setup
Ledger says its chip and software weren't hacked, and no cases involve devices bought from its own website. It's offering free X-ray checks in France.
Buy hardware wallets only from the maker. Never use a pre-filled seed card. Send this to anyone holding $BTC on a new device. 👇
#Ledger #CryptoSecurity #HardwareWallet
1
36
·
--
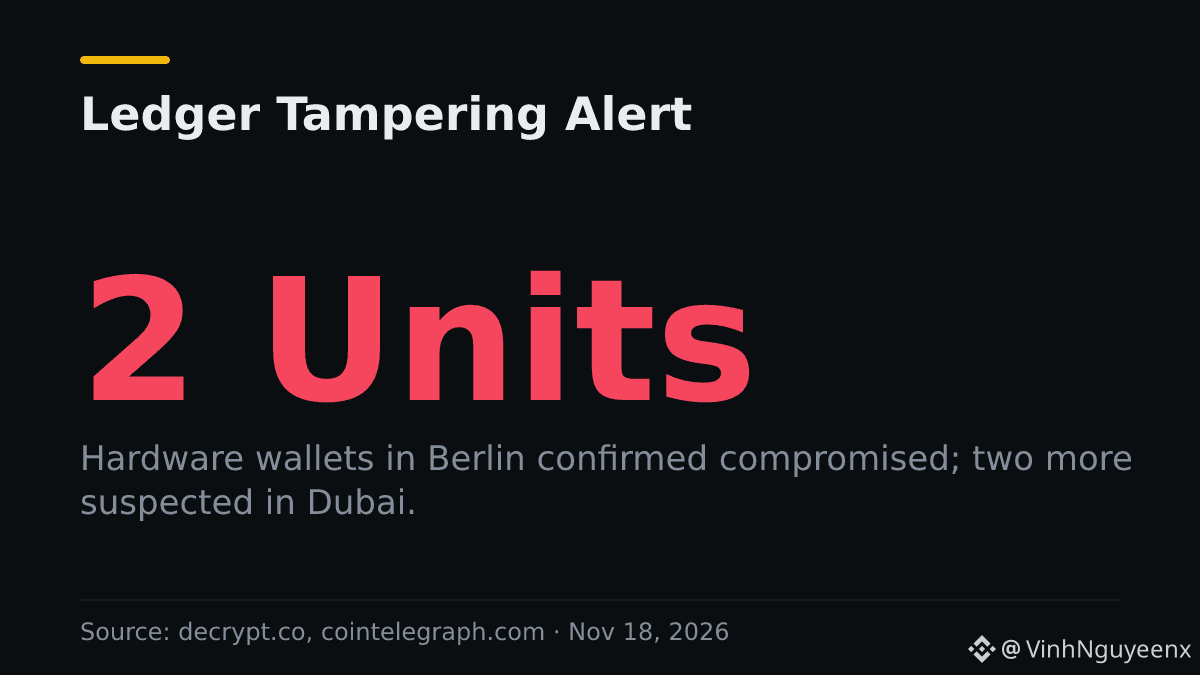
Ledger flagged two suspected compromised wallets in Dubai while confirming tampering in Berlin.
• Ledger confirmed hardware implants in Berlin‑purchased wallets (decrypt.co)
• The investigation now includes two suspected tampered units in Dubai (cointelegraph.com)
• Affected users are urged to contact support and halt transactions (decrypt.co)
The breach underscores a physical attack vector on crypto custody, urging stricter supply‑chain audits.
What’s your next move?
A) Update firmware immediately
B) Switch to a different hardware wallet
C) Keep using but monitor support
$BTC #Ledger #HardwareWallet #Security 🔐
⚠️ Not financial advice. DYOR.
Ledger flagged two suspected compromised wallets in Dubai while confirming tampering in Berlin.
• Ledger confirmed hardware implants in Berlin‑purchased wallets (decrypt.co)
• The investigation now includes two suspected tampered units in Dubai (cointelegraph.com)
• Affected users are urged to contact support and halt transactions (decrypt.co)
The breach underscores a physical attack vector on crypto custody, urging stricter supply‑chain audits.
What’s your next move?
A) Update firmware immediately
B) Switch to a different hardware wallet
C) Keep using but monitor support
$BTC #Ledger #HardwareWallet #Security 🔐
⚠️ Not financial advice. DYOR.
• Ledger confirmed hardware implants in Berlin‑purchased wallets (decrypt.co)
• The investigation now includes two suspected tampered units in Dubai (cointelegraph.com)
• Affected users are urged to contact support and halt transactions (decrypt.co)
The breach underscores a physical attack vector on crypto custody, urging stricter supply‑chain audits.
What’s your next move?
A) Update firmware immediately
B) Switch to a different hardware wallet
C) Keep using but monitor support
$BTC #Ledger #HardwareWallet #Security 🔐
⚠️ Not financial advice. DYOR.
1
30


·
--
🔐 Ledger warns Berlin buyers as its device-tampering probe widens
Ledger told customers who bought hardware wallets in Berlin since January 2026 to contact support after it found several suspicious devices in the city. It also acknowledged tampered devices in Dubai, where two customers recently reported losing a combined $604,000 in crypto. Ledger says all confirmed cases share physical modifications built to capture recovery phrases during setup, tied to the same distribution-channel campaign it began probing in Southeast Asia in October. The company found no flaw in its secure chip or OS and no confirmed cases from devices bought directly on its website.
⭐ Supply-chain attacks can bypass even strong hardware security, making official purchase channels more important than ever.
#Ledger #Security #HardwareWallet #CryptoNews
🔐 Ledger warns Berlin buyers as its device-tampering probe widens
Ledger told customers who bought hardware wallets in Berlin since January 2026 to contact support after it found several suspicious devices in the city. It also acknowledged tampered devices in Dubai, where two customers recently reported losing a combined $604,000 in crypto. Ledger says all confirmed cases share physical modifications built to capture recovery phrases during setup, tied to the same distribution-channel campaign it began probing in Southeast Asia in October. The company found no flaw in its secure chip or OS and no confirmed cases from devices bought directly on its website.
⭐ Supply-chain attacks can bypass even strong hardware security, making official purchase channels more important than ever.
#Ledger #Security #HardwareWallet #CryptoNews
Ledger told customers who bought hardware wallets in Berlin since January 2026 to contact support after it found several suspicious devices in the city. It also acknowledged tampered devices in Dubai, where two customers recently reported losing a combined $604,000 in crypto. Ledger says all confirmed cases share physical modifications built to capture recovery phrases during setup, tied to the same distribution-channel campaign it began probing in Southeast Asia in October. The company found no flaw in its secure chip or OS and no confirmed cases from devices bought directly on its website.
⭐ Supply-chain attacks can bypass even strong hardware security, making official purchase channels more important than ever.
#Ledger #Security #HardwareWallet #CryptoNews
1
854

·
--
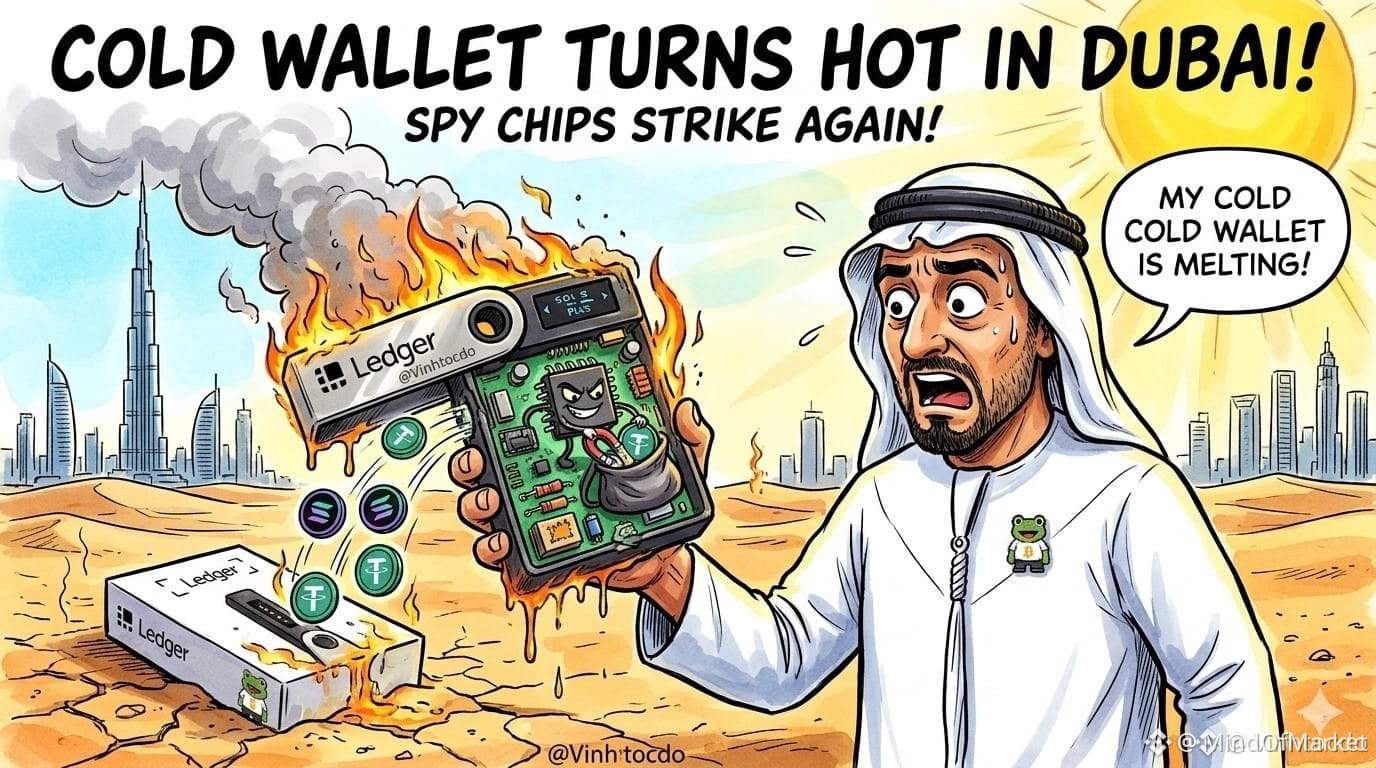
🚨 SUPPLY CHAIN COMPROMISE HITS $SOL HARDWARE STORAGE ACROSS PREMIUM RETAIL OUTLETS! ⚠️
Institutional-grade security starts at the distribution layer, where recent supply chain intrusions in Dubai have exposed vulnerable hardware units. 🔍 Unsuspecting participants are watching significant capital drain even on freshly unboxed devices.
Protect your structural capital by sourcing directly from verified manufacturers and implementing an additional passphrase layer for structural redundancy. 💡 Never rely solely on factory defaults when safeguarding large digital asset allocations.
💬 How are you auditing your offline storage security protocols right now? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #HardwareWallet #Web3Safety
🦈 🔒
🚨 SUPPLY CHAIN COMPROMISE HITS $SOL HARDWARE STORAGE ACROSS PREMIUM RETAIL OUTLETS! ⚠️
Institutional-grade security starts at the distribution layer, where recent supply chain intrusions in Dubai have exposed vulnerable hardware units. 🔍 Unsuspecting participants are watching significant capital drain even on freshly unboxed devices.
Protect your structural capital by sourcing directly from verified manufacturers and implementing an additional passphrase layer for structural redundancy. 💡 Never rely solely on factory defaults when safeguarding large digital asset allocations.
💬 How are you auditing your offline storage security protocols right now? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #HardwareWallet #Web3Safety
🦈 🔒
Institutional-grade security starts at the distribution layer, where recent supply chain intrusions in Dubai have exposed vulnerable hardware units. 🔍 Unsuspecting participants are watching significant capital drain even on freshly unboxed devices.
Protect your structural capital by sourcing directly from verified manufacturers and implementing an additional passphrase layer for structural redundancy. 💡 Never rely solely on factory defaults when safeguarding large digital asset allocations.
💬 How are you auditing your offline storage security protocols right now? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #HardwareWallet #Web3Safety
🦈 🔒
12
·
--
Bearish
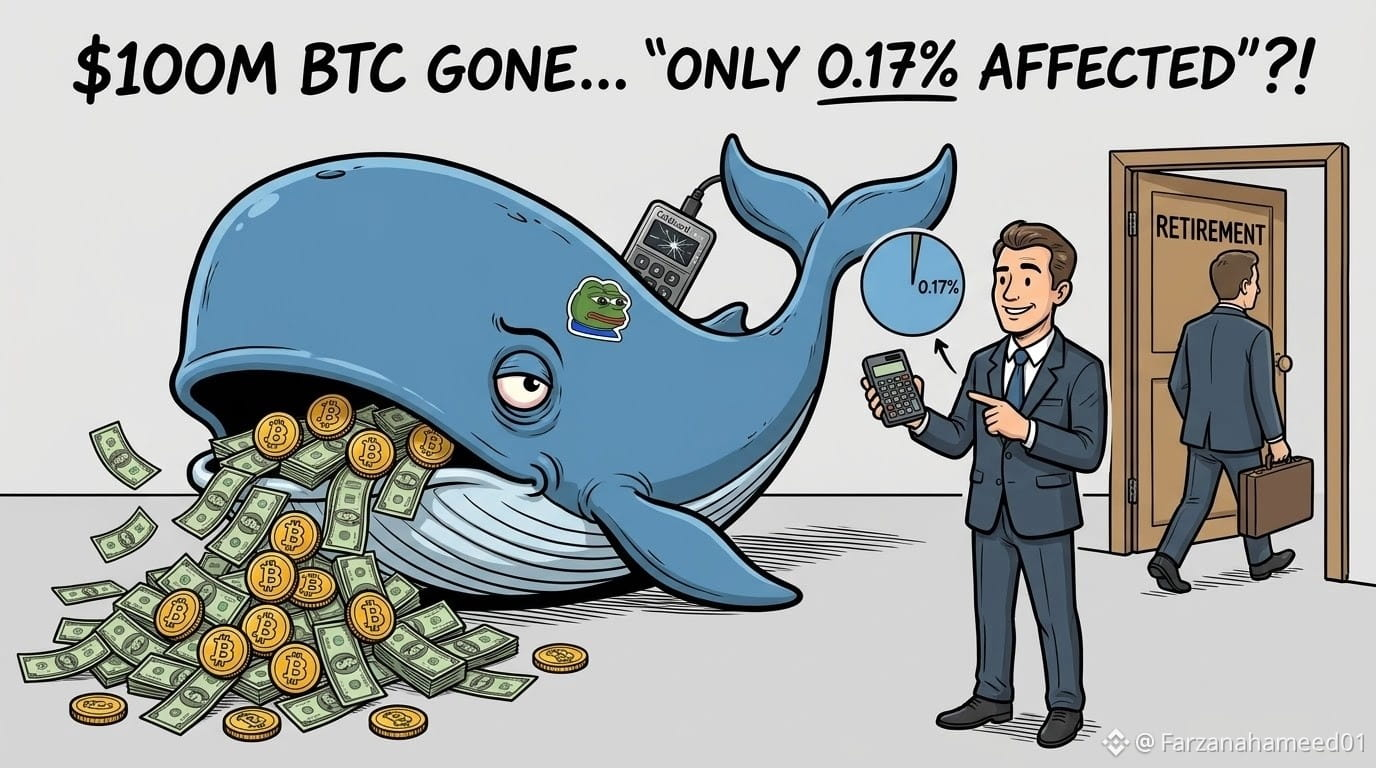
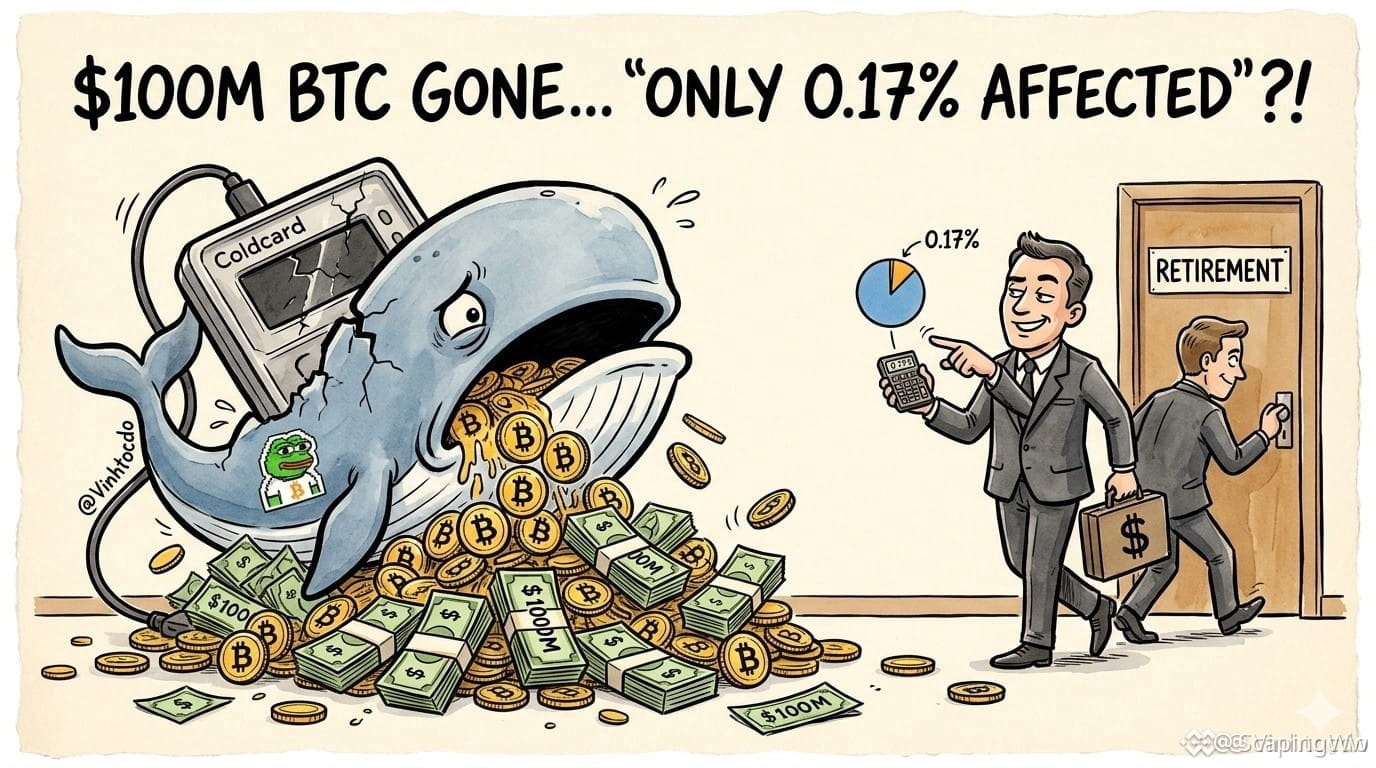
😱 OVER $100 MILLION IN BTC LOST, AND YOU SAY IT'S ONLY 0.17% OF USERS? WHAT KIND OF MATH IS THAT? 🧮
After five waves of attacks wiped out 1,830 BTC (over $100 million) from 9,200 addresses, the CEO of Coin kite calmly concluded that only about 0.17% of Cold card users were affected, then announced he was "retiring into seclusion"!
Guess those 0.17% are all "mega whales" carrying the percentage for the entire ecosystem, folks!
💡 What should traders do?
Don't let your guard down with cold wallets! If you use Cold card, update to the latest firmware, create a completely new seed phrase, and spread your assets across several other reputable wallets to avoid "putting all your eggs in one basket."
⚠️ This is not financial advice.
This is for learning and sharing only.
$BTC | $BNB | $BREV
#Coldcard #Bitcoin #CryptoSecurity #HardwareWallet #LedgerHardwareImplantReportsExtendToDubai
✨𝐅𝐀𝐑𝐙𝐀𝐍𝐀 𝐇𝐀𝐌𝐄𝐄𝐃 𝐎𝐅𝐅𝐈𝐂𝐈𝐀𝐋 • 🦋
😱 OVER $100 MILLION IN BTC LOST, AND YOU SAY IT'S ONLY 0.17% OF USERS? WHAT KIND OF MATH IS THAT? 🧮
After five waves of attacks wiped out 1,830 BTC (over $100 million) from 9,200 addresses, the CEO of Coin kite calmly concluded that only about 0.17% of Cold card users were affected, then announced he was "retiring into seclusion"!
Guess those 0.17% are all "mega whales" carrying the percentage for the entire ecosystem, folks!
💡 What should traders do?
Don't let your guard down with cold wallets! If you use Cold card, update to the latest firmware, create a completely new seed phrase, and spread your assets across several other reputable wallets to avoid "putting all your eggs in one basket."
⚠️ This is not financial advice.
This is for learning and sharing only.
$BTC | $BNB | $BREV
#Coldcard #Bitcoin #CryptoSecurity #HardwareWallet #LedgerHardwareImplantReportsExtendToDubai
✨𝐅𝐀𝐑𝐙𝐀𝐍𝐀 𝐇𝐀𝐌𝐄𝐄𝐃 𝐎𝐅𝐅𝐈𝐂𝐈𝐀𝐋 • 🦋
After five waves of attacks wiped out 1,830 BTC (over $100 million) from 9,200 addresses, the CEO of Coin kite calmly concluded that only about 0.17% of Cold card users were affected, then announced he was "retiring into seclusion"!
Guess those 0.17% are all "mega whales" carrying the percentage for the entire ecosystem, folks!
💡 What should traders do?
Don't let your guard down with cold wallets! If you use Cold card, update to the latest firmware, create a completely new seed phrase, and spread your assets across several other reputable wallets to avoid "putting all your eggs in one basket."
⚠️ This is not financial advice.
This is for learning and sharing only.
$BTC | $BNB | $BREV
#Coldcard #Bitcoin #CryptoSecurity #HardwareWallet #LedgerHardwareImplantReportsExtendToDubai
✨𝐅𝐀𝐑𝐙𝐀𝐍𝐀 𝐇𝐀𝐌𝐄𝐄𝐃 𝐎𝐅𝐅𝐈𝐂𝐈𝐀𝐋 • 🦋
Vinhtocdo:
🌹🌹🌹
4
5
320
·
--
🚨 ONE HUNDRED MILLION IN $BTC SWEPT FROM HARDWARE STORAGE AS SECURITY CRACKS EXPOSED! 🛡️
When over eighteen hundred coins vanish from cold storage across thousands of addresses, dismissing it as a minor statistical anomaly is pure negligence. 🦈
Institutional-grade custody starts with elite hygiene, meaning immediate firmware upgrades and dispersing master backups across isolated physical locations rather than leaving a single point of failure. 💡
Are you auditing your hardware security protocols today or waiting for a liquidity event to test your defenses? 💬 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #HardwareWallet #Crypto
🔥 💎
🚨 ONE HUNDRED MILLION IN $BTC SWEPT FROM HARDWARE STORAGE AS SECURITY CRACKS EXPOSED! 🛡️
When over eighteen hundred coins vanish from cold storage across thousands of addresses, dismissing it as a minor statistical anomaly is pure negligence. 🦈
Institutional-grade custody starts with elite hygiene, meaning immediate firmware upgrades and dispersing master backups across isolated physical locations rather than leaving a single point of failure. 💡
Are you auditing your hardware security protocols today or waiting for a liquidity event to test your defenses? 💬 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #HardwareWallet #Crypto
🔥 💎
When over eighteen hundred coins vanish from cold storage across thousands of addresses, dismissing it as a minor statistical anomaly is pure negligence. 🦈
Institutional-grade custody starts with elite hygiene, meaning immediate firmware upgrades and dispersing master backups across isolated physical locations rather than leaving a single point of failure. 💡
Are you auditing your hardware security protocols today or waiting for a liquidity event to test your defenses? 💬 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #HardwareWallet #Crypto
🔥 💎
8

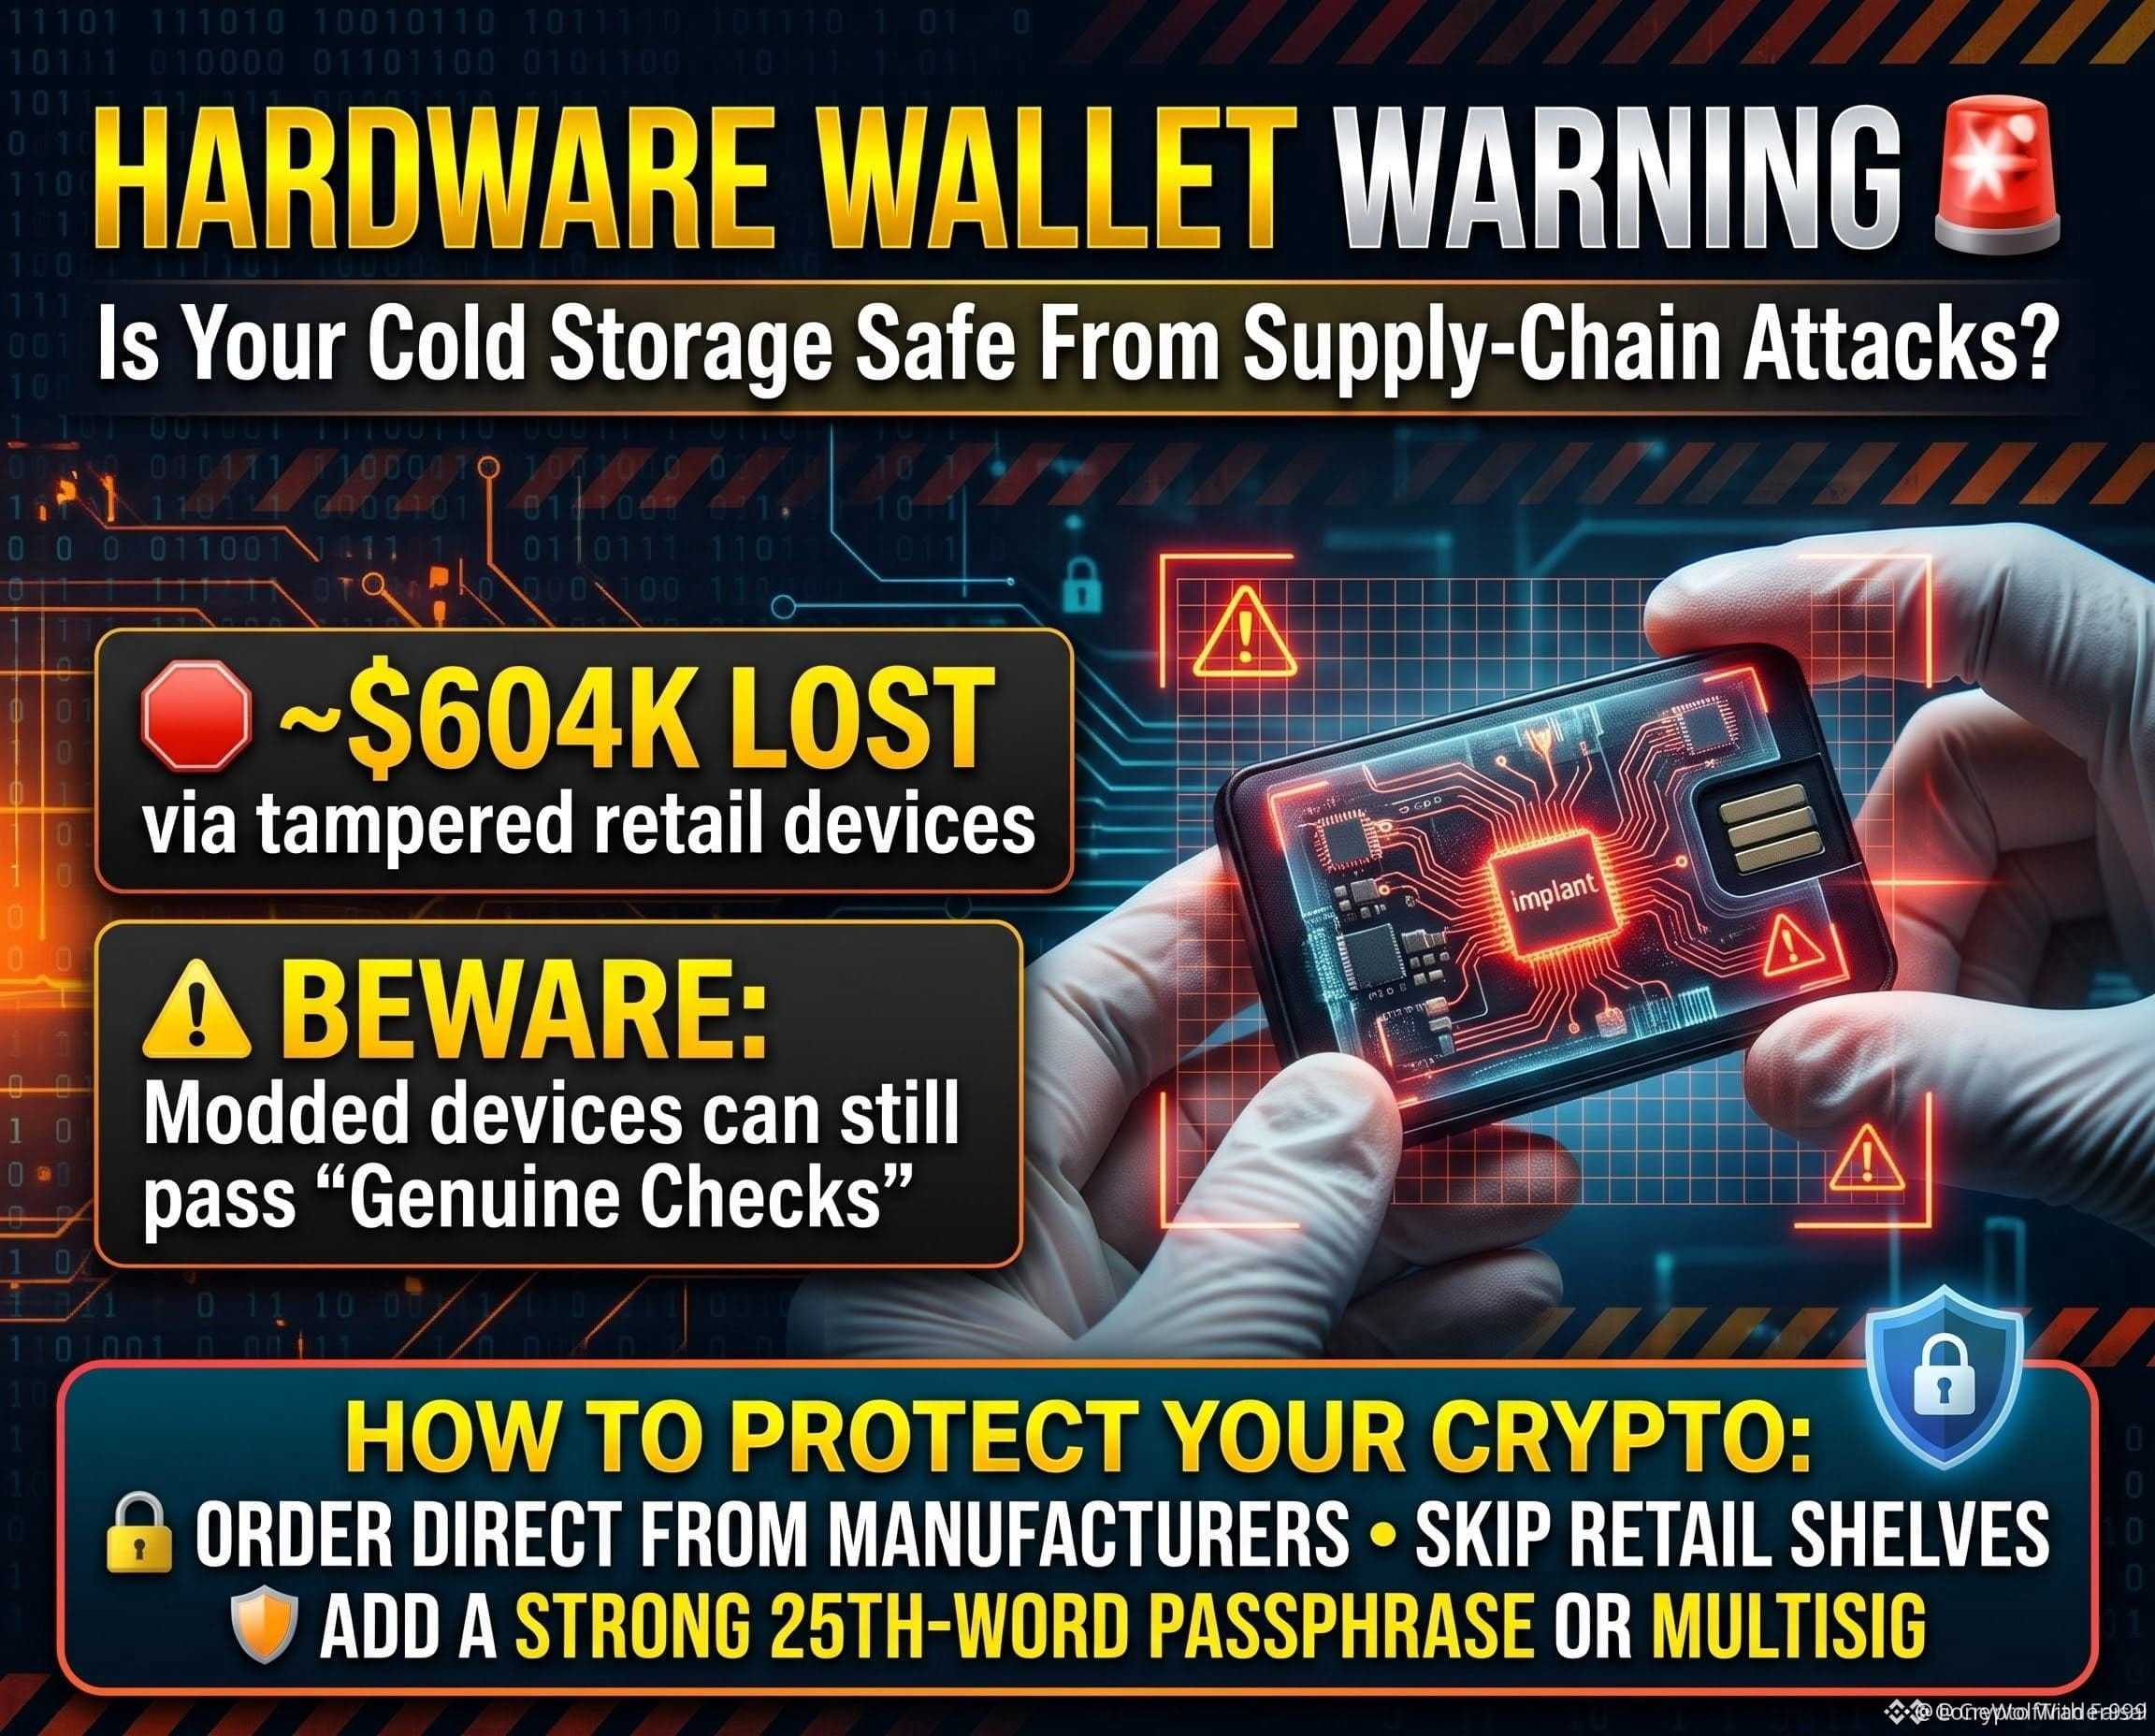
🚨 SILENT DRAINERS IN THE SUPPLY CHAIN ARE TARGETING YOUR $SOL BAGS! 🦈
When physical hardware gets intercepted before reaching your desk, standard cryptographic verification checks are completely bypassed. Rogue circuits can harvest your recovery credentials right off the screen without altering core device security. 🔍
Protecting your stack requires absolute paranoia when sourcing storage gear. Never trust retail middlemen or third-party storefronts when direct manufacturer delivery ensures uncompromised custody. 🛡️
Are you still taking chances buying hardware wallets off retail shelves, or strictly ordering direct from the source now? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #SelfCustody #HardwareWallet
🔥 🔒
🚨 SILENT DRAINERS IN THE SUPPLY CHAIN ARE TARGETING YOUR $SOL BAGS! 🦈
When physical hardware gets intercepted before reaching your desk, standard cryptographic verification checks are completely bypassed. Rogue circuits can harvest your recovery credentials right off the screen without altering core device security. 🔍
Protecting your stack requires absolute paranoia when sourcing storage gear. Never trust retail middlemen or third-party storefronts when direct manufacturer delivery ensures uncompromised custody. 🛡️
Are you still taking chances buying hardware wallets off retail shelves, or strictly ordering direct from the source now? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #SelfCustody #HardwareWallet
🔥 🔒
When physical hardware gets intercepted before reaching your desk, standard cryptographic verification checks are completely bypassed. Rogue circuits can harvest your recovery credentials right off the screen without altering core device security. 🔍
Protecting your stack requires absolute paranoia when sourcing storage gear. Never trust retail middlemen or third-party storefronts when direct manufacturer delivery ensures uncompromised custody. 🛡️
Are you still taking chances buying hardware wallets off retail shelves, or strictly ordering direct from the source now? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #SelfCustody #HardwareWallet
🔥 🔒
6

🚨 WHY YOUR BRAND NEW $SOL HARDWARE WALLET MIGHT ALREADY BE COMPROMISED ⚠️
Supply chain vectors are the silent assassins of crypto portfolios, proving that even factory-sealed boxes can harbor malicious hardware tampering in major retail hubs like Dubai. 🔍
When malicious actors intercept distribution channels to alter microchips before retail shelves, your cold storage becomes a vulnerable point draining funds instantly. ⚡
Protect your capital by verifying direct manufacturer shipments, enforcing a strict passphrase layer, and diversifying custody channels across the board. 💡 💬 Are you auditing your hardware storage security setup today or waiting for a costly wake-up call? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #HardwareWallet #Web3Safety
🛡️ 🔒
🚨 WHY YOUR BRAND NEW $SOL HARDWARE WALLET MIGHT ALREADY BE COMPROMISED ⚠️
Supply chain vectors are the silent assassins of crypto portfolios, proving that even factory-sealed boxes can harbor malicious hardware tampering in major retail hubs like Dubai. 🔍
When malicious actors intercept distribution channels to alter microchips before retail shelves, your cold storage becomes a vulnerable point draining funds instantly. ⚡
Protect your capital by verifying direct manufacturer shipments, enforcing a strict passphrase layer, and diversifying custody channels across the board. 💡 💬 Are you auditing your hardware storage security setup today or waiting for a costly wake-up call? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #HardwareWallet #Web3Safety
🛡️ 🔒
Supply chain vectors are the silent assassins of crypto portfolios, proving that even factory-sealed boxes can harbor malicious hardware tampering in major retail hubs like Dubai. 🔍
When malicious actors intercept distribution channels to alter microchips before retail shelves, your cold storage becomes a vulnerable point draining funds instantly. ⚡
Protect your capital by verifying direct manufacturer shipments, enforcing a strict passphrase layer, and diversifying custody channels across the board. 💡 💬 Are you auditing your hardware storage security setup today or waiting for a costly wake-up call? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #CryptoSecurity #HardwareWallet #Web3Safety
🛡️ 🔒
5

·
--
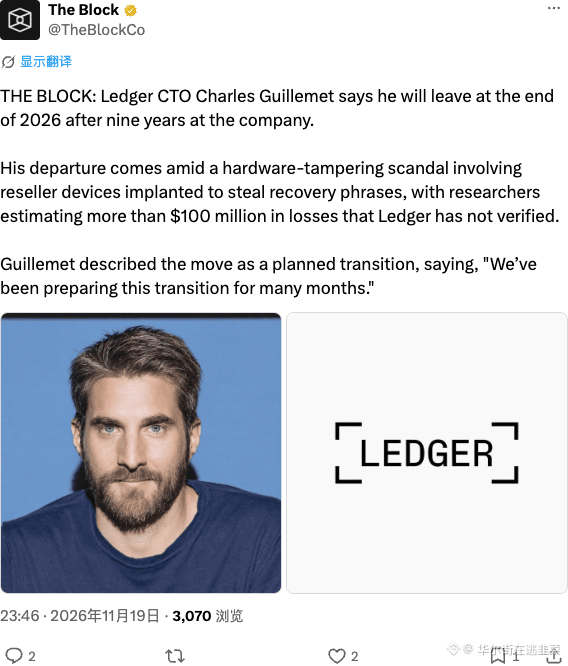
Ledger’s CTO officially announced he’ll leave at the end of 2026, following the hardware-tampering scandal that caused over $100 million in losses—a scandal the company still hasn’t acknowledged. After nine years of sticking it out, this “planned transition” sounds an awful lot like waiting for the whole thing to blow over.
$LEDR #Ledger #HardwareWallet
Ledger’s CTO officially announced he’ll leave at the end of 2026, following the hardware-tampering scandal that caused over $100 million in losses—a scandal the company still hasn’t acknowledged. After nine years of sticking it out, this “planned transition” sounds an awful lot like waiting for the whole thing to blow over.
$LEDR #Ledger #HardwareWallet
$LEDR #Ledger #HardwareWallet
30

·
--
Ledger spy chip confirmed in Berlin; hardware wallet supply-chain trust crisis spreads across Europe
The foundation of trust in hardware wallets is being pushed from the software layer to the physical layer. Ledger has officially confirmed that its investigation into a hardware implant incident has found a tampered device in Berlin. It is also examining two devices suspected of containing spy chips, as the investigation expands from Asia to Europe.
According to Decrypt, Ledger said its investigation has confirmed the presence of a tampered device in Berlin and that it is currently examining two devices suspected of containing spy chips. This is the most concrete publicly reported hardware-level supply-chain security incident to date, forming a “hardware + software” narrative alongside recent software-only hijacking attacks involving Optimizely, Luxor, and others.
Why this warrants concern. For years, hardware wallets have been considered a relatively reliable option for cold storage: private keys stay offline and are generated without an internet connection. But the crux of this incident is that the issue may not be limited to software hijacking while the wallet is in use; it could involve physical tampering during manufacturing, shipping, or distribution. If the hardware itself has been compromised, users’ assets could still be bypassed even when they follow proper procedures.
On the fundamentals, the risks hinge on several undisclosed variables: the specific wallet models affected, the technical method used to implant the chips, and who is responsible for the incident. None of these details have been made public, so any current assessment should remain cautious.
How might the market react? Hardware wallets are directly tied to the secure storage of crypto assets. If trust is damaged, expectations for demand across the entire hardware wallet category could be affected, potentially implicating other brands and triggering industry-wide panic. However, it is worth noting that supply-chain security incidents of this kind tend to affect trust and sentiment. Their direct impact on the prices of major assets such as BTC and ETH is usually limited; the effects are more structural and slow-moving.
A counterpoint is that the investigation is ongoing, and neither the actual scope of the impact nor whether any assets have truly been lost has been confirmed. It is also worth watching for duplicated information or overlapping narratives with recent reports about the Optimizely/Trezor hardware hijacking incidents.
What to watch next. Three signals matter most: the list of affected wallet models, the technical method used to implant the chips, and whether the incident develops from an isolated case into an industry-wide trust crisis. From a trading perspective, these events have a limited impact on the prices of major assets. If you are watching related assets, it is better to wait for confirmation of actual losses and the scope of the impact rather than price them in prematurely.
#Ledger #CryptoSecurity #HardwareWallet
The above is a summary of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any important developments.
Ledger spy chip confirmed in Berlin; hardware wallet supply-chain trust crisis spreads across Europe
The foundation of trust in hardware wallets is being pushed from the software layer to the physical layer. Ledger has officially confirmed that its investigation into a hardware implant incident has found a tampered device in Berlin. It is also examining two devices suspected of containing spy chips, as the investigation expands from Asia to Europe.
According to Decrypt, Ledger said its investigation has confirmed the presence of a tampered device in Berlin and that it is currently examining two devices suspected of containing spy chips. This is the most concrete publicly reported hardware-level supply-chain security incident to date, forming a “hardware + software” narrative alongside recent software-only hijacking attacks involving Optimizely, Luxor, and others.
Why this warrants concern. For years, hardware wallets have been considered a relatively reliable option for cold storage: private keys stay offline and are generated without an internet connection. But the crux of this incident is that the issue may not be limited to software hijacking while the wallet is in use; it could involve physical tampering during manufacturing, shipping, or distribution. If the hardware itself has been compromised, users’ assets could still be bypassed even when they follow proper procedures.
On the fundamentals, the risks hinge on several undisclosed variables: the specific wallet models affected, the technical method used to implant the chips, and who is responsible for the incident. None of these details have been made public, so any current assessment should remain cautious.
How might the market react? Hardware wallets are directly tied to the secure storage of crypto assets. If trust is damaged, expectations for demand across the entire hardware wallet category could be affected, potentially implicating other brands and triggering industry-wide panic. However, it is worth noting that supply-chain security incidents of this kind tend to affect trust and sentiment. Their direct impact on the prices of major assets such as BTC and ETH is usually limited; the effects are more structural and slow-moving.
A counterpoint is that the investigation is ongoing, and neither the actual scope of the impact nor whether any assets have truly been lost has been confirmed. It is also worth watching for duplicated information or overlapping narratives with recent reports about the Optimizely/Trezor hardware hijacking incidents.
What to watch next. Three signals matter most: the list of affected wallet models, the technical method used to implant the chips, and whether the incident develops from an isolated case into an industry-wide trust crisis. From a trading perspective, these events have a limited impact on the prices of major assets. If you are watching related assets, it is better to wait for confirmation of actual losses and the scope of the impact rather than price them in prematurely.
#Ledger #CryptoSecurity #HardwareWallet
The above is a summary of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any important developments.
The foundation of trust in hardware wallets is being pushed from the software layer to the physical layer. Ledger has officially confirmed that its investigation into a hardware implant incident has found a tampered device in Berlin. It is also examining two devices suspected of containing spy chips, as the investigation expands from Asia to Europe.
According to Decrypt, Ledger said its investigation has confirmed the presence of a tampered device in Berlin and that it is currently examining two devices suspected of containing spy chips. This is the most concrete publicly reported hardware-level supply-chain security incident to date, forming a “hardware + software” narrative alongside recent software-only hijacking attacks involving Optimizely, Luxor, and others.
Why this warrants concern. For years, hardware wallets have been considered a relatively reliable option for cold storage: private keys stay offline and are generated without an internet connection. But the crux of this incident is that the issue may not be limited to software hijacking while the wallet is in use; it could involve physical tampering during manufacturing, shipping, or distribution. If the hardware itself has been compromised, users’ assets could still be bypassed even when they follow proper procedures.
On the fundamentals, the risks hinge on several undisclosed variables: the specific wallet models affected, the technical method used to implant the chips, and who is responsible for the incident. None of these details have been made public, so any current assessment should remain cautious.
How might the market react? Hardware wallets are directly tied to the secure storage of crypto assets. If trust is damaged, expectations for demand across the entire hardware wallet category could be affected, potentially implicating other brands and triggering industry-wide panic. However, it is worth noting that supply-chain security incidents of this kind tend to affect trust and sentiment. Their direct impact on the prices of major assets such as BTC and ETH is usually limited; the effects are more structural and slow-moving.
A counterpoint is that the investigation is ongoing, and neither the actual scope of the impact nor whether any assets have truly been lost has been confirmed. It is also worth watching for duplicated information or overlapping narratives with recent reports about the Optimizely/Trezor hardware hijacking incidents.
What to watch next. Three signals matter most: the list of affected wallet models, the technical method used to implant the chips, and whether the incident develops from an isolated case into an industry-wide trust crisis. From a trading perspective, these events have a limited impact on the prices of major assets. If you are watching related assets, it is better to wait for confirmation of actual losses and the scope of the impact rather than price them in prematurely.
#Ledger #CryptoSecurity #HardwareWallet
The above is a summary of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any important developments.
57
·
--
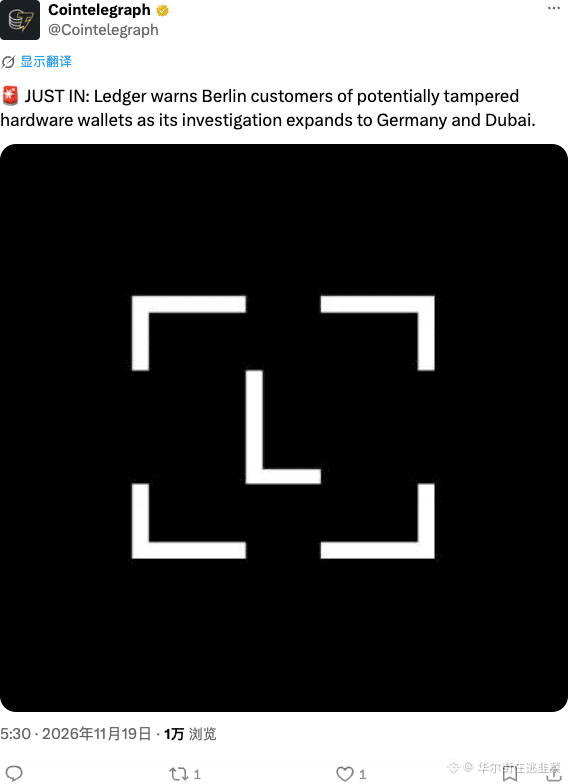
Ledger customers in Berlin received unsolicited mobile games, and the investigation has now expanded to Dubai.
This time, the security myth surrounding hardware wallets has been completely shattered.
Even physical access can be exploited, and offline storage has vulnerabilities too.
A reminder for onlookers: Don’t put all your eggs in cold wallets; keeping multiple backups is the real rule.
Ledger
#LedgerSecurity #HardwareWallet #CryptoNews
Ledger customers in Berlin received unsolicited mobile games, and the investigation has now expanded to Dubai.
This time, the security myth surrounding hardware wallets has been completely shattered.
Even physical access can be exploited, and offline storage has vulnerabilities too.
A reminder for onlookers: Don’t put all your eggs in cold wallets; keeping multiple backups is the real rule.
Ledger
#LedgerSecurity #HardwareWallet #CryptoNews
This time, the security myth surrounding hardware wallets has been completely shattered.
Even physical access can be exploited, and offline storage has vulnerabilities too.
A reminder for onlookers: Don’t put all your eggs in cold wallets; keeping multiple backups is the real rule.
Ledger
#LedgerSecurity #HardwareWallet #CryptoNews
5
·
--
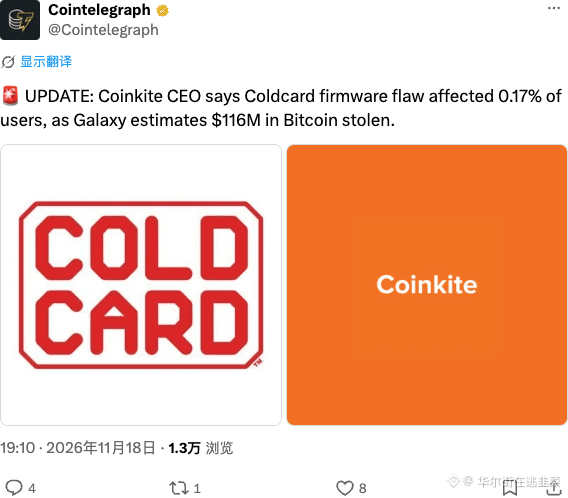
A 0.17% exposure put 116 million at risk, shattering the myth of hardware wallets. Coinkite acknowledged the vulnerability, but the supply chain black hole runs deeper than imagined. Don’t put all your eggs in the hardware basket: private key management is what matters; physical protection is just psychological comfort.
#Coldcard #Bitcoin #HardwareWallet
A 0.17% exposure put 116 million at risk, shattering the myth of hardware wallets. Coinkite acknowledged the vulnerability, but the supply chain black hole runs deeper than imagined. Don’t put all your eggs in the hardware basket: private key management is what matters; physical protection is just psychological comfort.
#Coldcard #Bitcoin #HardwareWallet
#Coldcard #Bitcoin #HardwareWallet
5
·
--
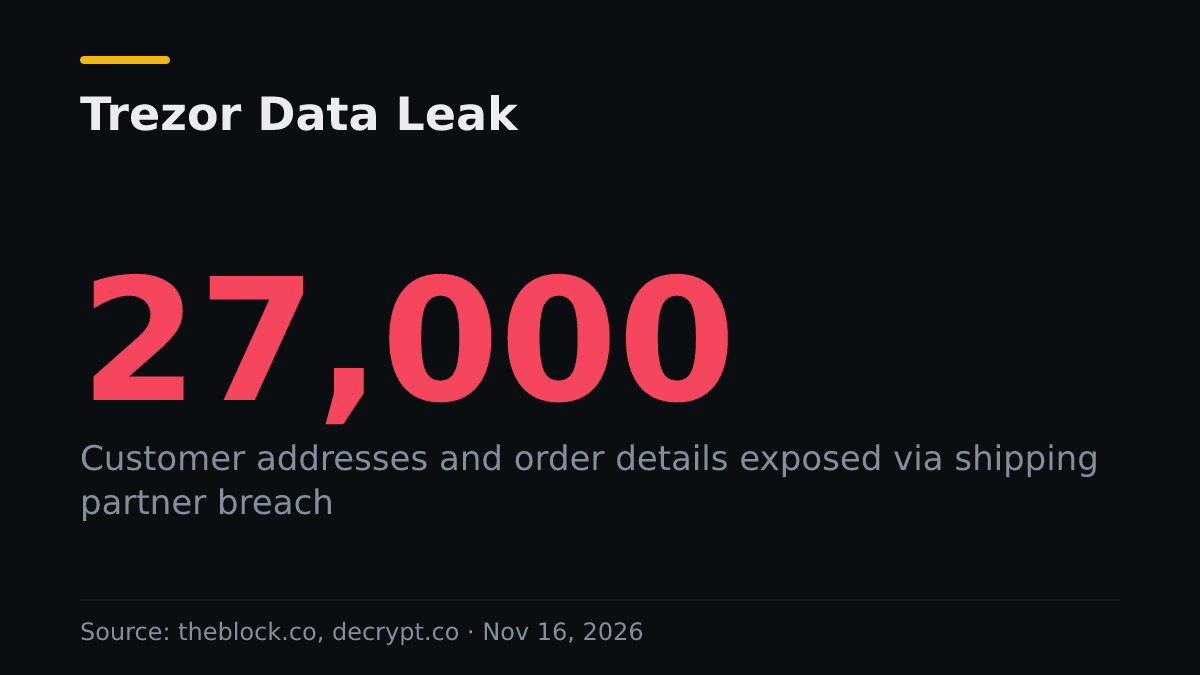
27,000 Trezor orders exposed in a fresh data leak.
• Trezor disclosed a breach at a shipping partner affecting ~27,000 orders (theblock.co)
• A second partner leak revealed customer addresses and order details, prompting scam call warnings (decrypt.co)
• The incidents raise fresh concerns over physical security and supply‑chain risks for hardware wallets (theblock.co)
These breaches highlight that even offline‑first wallets can be vulnerable through their logistics chain, urging users to monitor for phishing.
What’s your next step to protect your crypto assets?
A) Review wallet address exposure
B) Switch to a different hardware wallet
C) Strengthen phishing defenses
$BTC #Security #HardwareWallet 🔐
⚠️ Not financial advice. DYOR.
27,000 Trezor orders exposed in a fresh data leak.
• Trezor disclosed a breach at a shipping partner affecting ~27,000 orders (theblock.co)
• A second partner leak revealed customer addresses and order details, prompting scam call warnings (decrypt.co)
• The incidents raise fresh concerns over physical security and supply‑chain risks for hardware wallets (theblock.co)
These breaches highlight that even offline‑first wallets can be vulnerable through their logistics chain, urging users to monitor for phishing.
What’s your next step to protect your crypto assets?
A) Review wallet address exposure
B) Switch to a different hardware wallet
C) Strengthen phishing defenses
$BTC #Security #HardwareWallet 🔐
⚠️ Not financial advice. DYOR.
• Trezor disclosed a breach at a shipping partner affecting ~27,000 orders (theblock.co)
• A second partner leak revealed customer addresses and order details, prompting scam call warnings (decrypt.co)
• The incidents raise fresh concerns over physical security and supply‑chain risks for hardware wallets (theblock.co)
These breaches highlight that even offline‑first wallets can be vulnerable through their logistics chain, urging users to monitor for phishing.
What’s your next step to protect your crypto assets?
A) Review wallet address exposure
B) Switch to a different hardware wallet
C) Strengthen phishing defenses
$BTC #Security #HardwareWallet 🔐
⚠️ Not financial advice. DYOR.
21

·
--
Trezor’s Logistics Breached for the Second Time: Hardware Wallet Supply Chain Security Raises Red Flags Again
Hardware wallet maker Trezor has suffered a breach at a second logistics provider within three months, exposing buyers’ addresses and order details once again. Supply chain risks are escalating from isolated incidents into a systemic vulnerability.
According to Decrypt, Trezor confirmed that a second logistics partner was breached within three months, exposing data such as buyers’ addresses and order details. This is the company’s second data breach involving a logistics channel in a relatively short period, suggesting that attackers’ points of access have expanded beyond the product itself to the intermediate stages of package delivery.
This incident merits scrutiny from both a financial and institutional perspective because the user base for hardware wallets is closely tied to market liquidity. Early holders and institutional investors are often more inclined to use cold storage, and a supply chain data breach could undermine their trust in hardware wallets. If that trust begins to erode, the potential impact may not be immediate selling pressure, but rather whether incoming capital remains willing to entrust assets to this kind of infrastructure.
Technically, the vulnerability lies not in the wallet firmware itself, but in the logistics chain. An attacker only needs to breach one logistics provider to obtain information such as buyers’ addresses and order details—data that should otherwise be kept isolated. For institutions, this means the security perimeter is expanding: product security, warehouse security, and logistics security are linked into a fragile chain, and a breach at any point could affect the whole system.
The market’s likely reaction currently appears neutral to slightly bearish, but there is no direct basis to expect selling. This is a risk-warning event, not a major market shock, and is unlikely to trigger large-scale asset transfers in the short term. What matters most is whether this incident combines with other recent security events to fuel systemic doubts about the hardware wallet sector.
A counterpoint is that a single logistics breach does not mean the wallet itself has failed. Users’ assets remain protected by their private keys, and there is a clear distinction between data exposure and asset theft. That said, a second logistics provider being breached within three months suggests this is not an isolated incident, but a recurring weak point in the supply chain.
What to watch next: Trezor’s security response and any compensation measures, as well as marginal changes in market confidence in the company. If incidents of this kind continue to escalate, the valuation logic for the hardware wallet sector may face reassessment.
#Trezor #HardwareWallet #CryptoSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any significant developments.
Trezor’s Logistics Breached for the Second Time: Hardware Wallet Supply Chain Security Raises Red Flags Again
Hardware wallet maker Trezor has suffered a breach at a second logistics provider within three months, exposing buyers’ addresses and order details once again. Supply chain risks are escalating from isolated incidents into a systemic vulnerability.
According to Decrypt, Trezor confirmed that a second logistics partner was breached within three months, exposing data such as buyers’ addresses and order details. This is the company’s second data breach involving a logistics channel in a relatively short period, suggesting that attackers’ points of access have expanded beyond the product itself to the intermediate stages of package delivery.
This incident merits scrutiny from both a financial and institutional perspective because the user base for hardware wallets is closely tied to market liquidity. Early holders and institutional investors are often more inclined to use cold storage, and a supply chain data breach could undermine their trust in hardware wallets. If that trust begins to erode, the potential impact may not be immediate selling pressure, but rather whether incoming capital remains willing to entrust assets to this kind of infrastructure.
Technically, the vulnerability lies not in the wallet firmware itself, but in the logistics chain. An attacker only needs to breach one logistics provider to obtain information such as buyers’ addresses and order details—data that should otherwise be kept isolated. For institutions, this means the security perimeter is expanding: product security, warehouse security, and logistics security are linked into a fragile chain, and a breach at any point could affect the whole system.
The market’s likely reaction currently appears neutral to slightly bearish, but there is no direct basis to expect selling. This is a risk-warning event, not a major market shock, and is unlikely to trigger large-scale asset transfers in the short term. What matters most is whether this incident combines with other recent security events to fuel systemic doubts about the hardware wallet sector.
A counterpoint is that a single logistics breach does not mean the wallet itself has failed. Users’ assets remain protected by their private keys, and there is a clear distinction between data exposure and asset theft. That said, a second logistics provider being breached within three months suggests this is not an isolated incident, but a recurring weak point in the supply chain.
What to watch next: Trezor’s security response and any compensation measures, as well as marginal changes in market confidence in the company. If incidents of this kind continue to escalate, the valuation logic for the hardware wallet sector may face reassessment.
#Trezor #HardwareWallet #CryptoSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any significant developments.
Hardware wallet maker Trezor has suffered a breach at a second logistics provider within three months, exposing buyers’ addresses and order details once again. Supply chain risks are escalating from isolated incidents into a systemic vulnerability.
According to Decrypt, Trezor confirmed that a second logistics partner was breached within three months, exposing data such as buyers’ addresses and order details. This is the company’s second data breach involving a logistics channel in a relatively short period, suggesting that attackers’ points of access have expanded beyond the product itself to the intermediate stages of package delivery.
This incident merits scrutiny from both a financial and institutional perspective because the user base for hardware wallets is closely tied to market liquidity. Early holders and institutional investors are often more inclined to use cold storage, and a supply chain data breach could undermine their trust in hardware wallets. If that trust begins to erode, the potential impact may not be immediate selling pressure, but rather whether incoming capital remains willing to entrust assets to this kind of infrastructure.
Technically, the vulnerability lies not in the wallet firmware itself, but in the logistics chain. An attacker only needs to breach one logistics provider to obtain information such as buyers’ addresses and order details—data that should otherwise be kept isolated. For institutions, this means the security perimeter is expanding: product security, warehouse security, and logistics security are linked into a fragile chain, and a breach at any point could affect the whole system.
The market’s likely reaction currently appears neutral to slightly bearish, but there is no direct basis to expect selling. This is a risk-warning event, not a major market shock, and is unlikely to trigger large-scale asset transfers in the short term. What matters most is whether this incident combines with other recent security events to fuel systemic doubts about the hardware wallet sector.
A counterpoint is that a single logistics breach does not mean the wallet itself has failed. Users’ assets remain protected by their private keys, and there is a clear distinction between data exposure and asset theft. That said, a second logistics provider being breached within three months suggests this is not an isolated incident, but a recurring weak point in the supply chain.
What to watch next: Trezor’s security response and any compensation measures, as well as marginal changes in market confidence in the company. If incidents of this kind continue to escalate, the valuation logic for the hardware wallet sector may face reassessment.
#Trezor #HardwareWallet #CryptoSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any significant developments.
5
·
--
Trezor Hit by Third Logistics Provider Breach, Data of 27,000 Customers Leaked
The security perimeter of hardware wallets is quietly being breached through an inconspicuous link in the logistics chain.
According to Cointelegraph, Trezor has officially warned that an attacker was able to access the names, phone numbers, and shipping addresses of 27,000 customers. This is the third logistics partner to be compromised this year, meaning attackers have repeatedly exploited the same weak link in the supply chain.
Why is this incident cause for concern? In recent months, logistics operations at hardware wallet companies have been exposed more than once. The impact of the first and second breaches was relatively limited, but this time the number of affected customers has risen significantly—and it is the third incident in just three months. This pattern of repeated breaches is more telling than a single incident: logistics information itself may have become the biggest data vulnerability for hardware wallets.
There are two key figures in this leak: the logistics provider has been breached three times, and 27,000 customers were affected. It is worth noting that the leaked information was primarily personal data such as names, phone numbers, and addresses—not sensitive information that directly controls assets, such as private keys or seed phrases. This is therefore more a breach of user privacy than a direct risk of asset theft.
How might the market react? Since Trezor operates in the hardware infrastructure layer and no private keys were involved, the direct impact on crypto asset prices may be limited. However, the incident exposes a weak link in the hardware wallet chain of trust and could, over the long term, affect some users’ confidence in hardware wallet security.
One mitigating factor is that the leak was limited to logistics information, and the attackers cannot directly access on-chain assets. The real risk may be that the leaked personal information could be used for targeted phishing, paving the way for subsequent social engineering attacks.
What remains to be seen is whether Trezor will disclose more details about the scope of the breach and its response, and whether phishing attacks using the leaked information will follow. This supply chain security front is worth monitoring closely.
#Trezor #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow and provide updates if there are any significant developments.
Trezor Hit by Third Logistics Provider Breach, Data of 27,000 Customers Leaked
The security perimeter of hardware wallets is quietly being breached through an inconspicuous link in the logistics chain.
According to Cointelegraph, Trezor has officially warned that an attacker was able to access the names, phone numbers, and shipping addresses of 27,000 customers. This is the third logistics partner to be compromised this year, meaning attackers have repeatedly exploited the same weak link in the supply chain.
Why is this incident cause for concern? In recent months, logistics operations at hardware wallet companies have been exposed more than once. The impact of the first and second breaches was relatively limited, but this time the number of affected customers has risen significantly—and it is the third incident in just three months. This pattern of repeated breaches is more telling than a single incident: logistics information itself may have become the biggest data vulnerability for hardware wallets.
There are two key figures in this leak: the logistics provider has been breached three times, and 27,000 customers were affected. It is worth noting that the leaked information was primarily personal data such as names, phone numbers, and addresses—not sensitive information that directly controls assets, such as private keys or seed phrases. This is therefore more a breach of user privacy than a direct risk of asset theft.
How might the market react? Since Trezor operates in the hardware infrastructure layer and no private keys were involved, the direct impact on crypto asset prices may be limited. However, the incident exposes a weak link in the hardware wallet chain of trust and could, over the long term, affect some users’ confidence in hardware wallet security.
One mitigating factor is that the leak was limited to logistics information, and the attackers cannot directly access on-chain assets. The real risk may be that the leaked personal information could be used for targeted phishing, paving the way for subsequent social engineering attacks.
What remains to be seen is whether Trezor will disclose more details about the scope of the breach and its response, and whether phishing attacks using the leaked information will follow. This supply chain security front is worth monitoring closely.
#Trezor #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow and provide updates if there are any significant developments.
The security perimeter of hardware wallets is quietly being breached through an inconspicuous link in the logistics chain.
According to Cointelegraph, Trezor has officially warned that an attacker was able to access the names, phone numbers, and shipping addresses of 27,000 customers. This is the third logistics partner to be compromised this year, meaning attackers have repeatedly exploited the same weak link in the supply chain.
Why is this incident cause for concern? In recent months, logistics operations at hardware wallet companies have been exposed more than once. The impact of the first and second breaches was relatively limited, but this time the number of affected customers has risen significantly—and it is the third incident in just three months. This pattern of repeated breaches is more telling than a single incident: logistics information itself may have become the biggest data vulnerability for hardware wallets.
There are two key figures in this leak: the logistics provider has been breached three times, and 27,000 customers were affected. It is worth noting that the leaked information was primarily personal data such as names, phone numbers, and addresses—not sensitive information that directly controls assets, such as private keys or seed phrases. This is therefore more a breach of user privacy than a direct risk of asset theft.
How might the market react? Since Trezor operates in the hardware infrastructure layer and no private keys were involved, the direct impact on crypto asset prices may be limited. However, the incident exposes a weak link in the hardware wallet chain of trust and could, over the long term, affect some users’ confidence in hardware wallet security.
One mitigating factor is that the leak was limited to logistics information, and the attackers cannot directly access on-chain assets. The real risk may be that the leaked personal information could be used for targeted phishing, paving the way for subsequent social engineering attacks.
What remains to be seen is whether Trezor will disclose more details about the scope of the breach and its response, and whether phishing attacks using the leaked information will follow. This supply chain security front is worth monitoring closely.
#Trezor #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow and provide updates if there are any significant developments.
4
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinCorePatchesAIDiscoveredVulnerability
7 views
34 Discussing
2
#CanBTCReboundAfterFallingBelow60K?
448,740 views
1,951 Discussing
3
#GlobalStocksFaceLongestLosingStreakSince2023
152,117 views
1,358 Discussing
4
#BlackRockIBITPostsRecord$541MSingleDayOutflow
5,295 views
42 Discussing
5
#AnthropicPlungesTowardIPOPriceonDay2
73,269 views
767 Discussing
6
#TwentyOneCapitalAdds172.25BTC
23,984 views
305 Discussing
7
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
2,671 views
31 Discussing
8
#BNBDropsBelow540USDTWith8.46%DailyDecline
42,673 views
373 Discussing
9
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,500 views
20 Discussing
10
#BitMineFaces$10.1BUnrealizedETHLoss
2,750 views
25 Discussing