
#cybersecurity
cybersecurity
1.6M views
3,941 Discussing
Hot
Latest

🚨 AI JUST UNLOCKED A RARE ZERO-DAY FLAW THAT COULD FREEZE $BTC NODES! 💥
Silicon intelligence is now stress-testing network architecture, exposing vulnerabilities long before manual audits catch them. 📊 Project Loupe just flagged an AI-discovered exploit where a single transaction ID spammed fifty thousand times could temporarily freeze unpatched $BTC nodes. ⚡
Bitcoin Core moved swiftly to ship fixes in versions thirty point five and thirty-one point three, neutralizing the threat before bad actors could weaponize it at scale. 💡 Node operators must upgrade immediately to protect exchange deposits and ensure uninterrupted ledger synchronization. 📌
Are you running an updated node version, or are you still vulnerable to automated network stress tests? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
🚨 AI JUST UNLOCKED A RARE ZERO-DAY FLAW THAT COULD FREEZE $BTC NODES! 💥
Silicon intelligence is now stress-testing network architecture, exposing vulnerabilities long before manual audits catch them. 📊 Project Loupe just flagged an AI-discovered exploit where a single transaction ID spammed fifty thousand times could temporarily freeze unpatched $BTC nodes. ⚡
Bitcoin Core moved swiftly to ship fixes in versions thirty point five and thirty-one point three, neutralizing the threat before bad actors could weaponize it at scale. 💡 Node operators must upgrade immediately to protect exchange deposits and ensure uninterrupted ledger synchronization. 📌
Are you running an updated node version, or are you still vulnerable to automated network stress tests? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
Silicon intelligence is now stress-testing network architecture, exposing vulnerabilities long before manual audits catch them. 📊 Project Loupe just flagged an AI-discovered exploit where a single transaction ID spammed fifty thousand times could temporarily freeze unpatched $BTC nodes. ⚡
Bitcoin Core moved swiftly to ship fixes in versions thirty point five and thirty-one point three, neutralizing the threat before bad actors could weaponize it at scale. 💡 Node operators must upgrade immediately to protect exchange deposits and ensure uninterrupted ledger synchronization. 📌
Are you running an updated node version, or are you still vulnerable to automated network stress tests? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #BitcoinCore #CyberSecurity #Crypto
🔥 💎
7
·
--
🚨 China Trips Come With Serious Security Rules for US Officials! 🇺🇸🇨🇳
A visit to China is clearly not an ordinary overseas trip for American officials.
Reports say US officials are required to leave their personal phones behind and use temporary security-issued devices during the visit. These devices are reportedly destroyed afterward to reduce the risk of sensitive information being compromised.
Even food security is taken seriously, with President Trump reportedly avoiding food provided by foreign governments.
Officials also face additional security checks when they return home.
In today's world, cybersecurity and national security go far beyond what we can see. One simple phone or meal can become a potential security concern. 👀
#Trump #China #USGovernment #CyberSecurity #WorldNews
🚨 China Trips Come With Serious Security Rules for US Officials! 🇺🇸🇨🇳
A visit to China is clearly not an ordinary overseas trip for American officials.
Reports say US officials are required to leave their personal phones behind and use temporary security-issued devices during the visit. These devices are reportedly destroyed afterward to reduce the risk of sensitive information being compromised.
Even food security is taken seriously, with President Trump reportedly avoiding food provided by foreign governments.
Officials also face additional security checks when they return home.
In today's world, cybersecurity and national security go far beyond what we can see. One simple phone or meal can become a potential security concern. 👀
#Trump #China #USGovernment #CyberSecurity #WorldNews
A visit to China is clearly not an ordinary overseas trip for American officials.
Reports say US officials are required to leave their personal phones behind and use temporary security-issued devices during the visit. These devices are reportedly destroyed afterward to reduce the risk of sensitive information being compromised.
Even food security is taken seriously, with President Trump reportedly avoiding food provided by foreign governments.
Officials also face additional security checks when they return home.
In today's world, cybersecurity and national security go far beyond what we can see. One simple phone or meal can become a potential security concern. 👀
#Trump #China #USGovernment #CyberSecurity #WorldNews
Life is Race
·
--
$DGB Claim A Big Gift here 🎁🎁🎁🎁🎁🧧🧧🧧🧧🧧✅✅✅✅✅✅✅
730

Google just brought Gemini's computer-use feature to Mac, letting the AI navigate apps and files. While convenience is peaking, Google's own warnings highlight serious prompt injection vulnerabilities. As AI agents gain deep OS access, security will become the ultimate bottleneck for mainstream adoption. Watch how this narrative impacts decentralized security and AI utility tokens moving forward. #BinanceSquare #ArtificialIntelligence #CyberSecurity
Google just brought Gemini's computer-use feature to Mac, letting the AI navigate apps and files. While convenience is peaking, Google's own warnings highlight serious prompt injection vulnerabilities. As AI agents gain deep OS access, security will become the ultimate bottleneck for mainstream adoption. Watch how this narrative impacts decentralized security and AI utility tokens moving forward. #BinanceSquare #ArtificialIntelligence #CyberSecurity
GOOGL-1.83%
GOOGUS-0.84%
135

JUST IN: 🇺🇸🇨🇳 US TREASURY SECRETARY WARNS ABOUT AI CYBERSECURITY RISKS!
US Treasury Secretary Scott Bessent has reportedly described Chinese AI models dangerous raising concerns about their potential use in cyberattacks.
⚠️ Key concerns:
- AI-powered cyber threats
- Growing global cybersecurity risks
- National security concerns
- Increasing competition in artificial intelligence
🤖 As AI technology advances cybersecurity is becoming an increasingly important global issue.
🔥 Could AI become the next major battleground in global technology?
#CyberSecurity #USA #china #Crypto
JUST IN: 🇺🇸🇨🇳 US TREASURY SECRETARY WARNS ABOUT AI CYBERSECURITY RISKS!
US Treasury Secretary Scott Bessent has reportedly described Chinese AI models dangerous raising concerns about their potential use in cyberattacks.
⚠️ Key concerns:
- AI-powered cyber threats
- Growing global cybersecurity risks
- National security concerns
- Increasing competition in artificial intelligence
🤖 As AI technology advances cybersecurity is becoming an increasingly important global issue.
🔥 Could AI become the next major battleground in global technology?
#CyberSecurity #USA #china #Crypto
US Treasury Secretary Scott Bessent has reportedly described Chinese AI models dangerous raising concerns about their potential use in cyberattacks.
⚠️ Key concerns:
- AI-powered cyber threats
- Growing global cybersecurity risks
- National security concerns
- Increasing competition in artificial intelligence
🤖 As AI technology advances cybersecurity is becoming an increasingly important global issue.
🔥 Could AI become the next major battleground in global technology?
#CyberSecurity #USA #china #Crypto
31

Your LLM gateway is now on CISA's Known Exploited Vulnerabilities list.
On 18 Nov, CISA added CVE-2026-40217 (BerriAI LiteLLM) to KEV, along with three other CVEs. KEV means exploitation was observed in the wild. Per the BerriAI advisory, code can escape a custom-code sandbox and run inside the proxy process.
Why it matters: a gateway may hold your provider API keys. By default the endpoint needs proxy-admin credentials, so this is not "every gateway is owned." Risk depends on your version, configuration and who can reach it.
This is not about $BNB or price. It is about the plumbing under your AI tools.
Do now:
• Upgrade to 1.83.11 or later
• Can't yet? Block POST /guardrails/test_custom_code at your proxy
• Restrict access to it and review logs for unexpected requests
Verdict: PROVEN, confidence high. That covers the KEV listing, not your own exposure.
Watchpoint: 2 Dec 2026 is CISA's deadline for US federal agencies. It is an administrative date, not a patch date.
If one gateway holds every key you own, is it still just a gateway? Do you know where yours is exposed?
#CISA #LLMSecurity #CyberSecurity
Your LLM gateway is now on CISA's Known Exploited Vulnerabilities list.
On 18 Nov, CISA added CVE-2026-40217 (BerriAI LiteLLM) to KEV, along with three other CVEs. KEV means exploitation was observed in the wild. Per the BerriAI advisory, code can escape a custom-code sandbox and run inside the proxy process.
Why it matters: a gateway may hold your provider API keys. By default the endpoint needs proxy-admin credentials, so this is not "every gateway is owned." Risk depends on your version, configuration and who can reach it.
This is not about $BNB or price. It is about the plumbing under your AI tools.
Do now:
• Upgrade to 1.83.11 or later
• Can't yet? Block POST /guardrails/test_custom_code at your proxy
• Restrict access to it and review logs for unexpected requests
Verdict: PROVEN, confidence high. That covers the KEV listing, not your own exposure.
Watchpoint: 2 Dec 2026 is CISA's deadline for US federal agencies. It is an administrative date, not a patch date.
If one gateway holds every key you own, is it still just a gateway? Do you know where yours is exposed?
#CISA #LLMSecurity #CyberSecurity
On 18 Nov, CISA added CVE-2026-40217 (BerriAI LiteLLM) to KEV, along with three other CVEs. KEV means exploitation was observed in the wild. Per the BerriAI advisory, code can escape a custom-code sandbox and run inside the proxy process.
Why it matters: a gateway may hold your provider API keys. By default the endpoint needs proxy-admin credentials, so this is not "every gateway is owned." Risk depends on your version, configuration and who can reach it.
This is not about $BNB or price. It is about the plumbing under your AI tools.
Do now:
• Upgrade to 1.83.11 or later
• Can't yet? Block POST /guardrails/test_custom_code at your proxy
• Restrict access to it and review logs for unexpected requests
Verdict: PROVEN, confidence high. That covers the KEV listing, not your own exposure.
Watchpoint: 2 Dec 2026 is CISA's deadline for US federal agencies. It is an administrative date, not a patch date.
If one gateway holds every key you own, is it still just a gateway? Do you know where yours is exposed?
#CISA #LLMSecurity #CyberSecurity
77

Instantaneous Asset Drainage via Private Key Exposure
Automated bot activity triggered immediate liquidation of assets following the accidental exposure of private keys.
#BitcoinSecurity #Cybersecurity
Instantaneous Asset Drainage via Private Key Exposure
Automated bot activity triggered immediate liquidation of assets following the accidental exposure of private keys.
#BitcoinSecurity #Cybersecurity
Automated bot activity triggered immediate liquidation of assets following the accidental exposure of private keys.
#BitcoinSecurity #Cybersecurity
4

🔌 Are we already living through an active cyber war? 🛡️⚡
🏦 The pattern is getting impossible to ignore.
✈️ ▸ Financial giants hit via third-party provider breaches
▸ Massive data leaks exposing millions of user records
▸ Major cloud infrastructure facing full-day outages
When centralized trust breaks down across tradfi and tech simultaneously, the vulnerability isn't just code — it's single points of failure. 🚨
Every security incident reinforces a brutal market truth: if you don't control your keys and architecture, someone else does. Self-custody and decentralized verification aren't just narrative tropes; they are structural risk management. 🔐💥
#CyberSecurity #CryptoSecurity #AICSH #BinanceAlpha #AICryptoSpotHunter .
🔌 Are we already living through an active cyber war? 🛡️⚡
🏦 The pattern is getting impossible to ignore.
✈️ ▸ Financial giants hit via third-party provider breaches
▸ Massive data leaks exposing millions of user records
▸ Major cloud infrastructure facing full-day outages
When centralized trust breaks down across tradfi and tech simultaneously, the vulnerability isn't just code — it's single points of failure. 🚨
Every security incident reinforces a brutal market truth: if you don't control your keys and architecture, someone else does. Self-custody and decentralized verification aren't just narrative tropes; they are structural risk management. 🔐💥
#CyberSecurity #CryptoSecurity #AICSH #BinanceAlpha #AICryptoSpotHunter .
🏦 The pattern is getting impossible to ignore.
✈️ ▸ Financial giants hit via third-party provider breaches
▸ Massive data leaks exposing millions of user records
▸ Major cloud infrastructure facing full-day outages
When centralized trust breaks down across tradfi and tech simultaneously, the vulnerability isn't just code — it's single points of failure. 🚨
Every security incident reinforces a brutal market truth: if you don't control your keys and architecture, someone else does. Self-custody and decentralized verification aren't just narrative tropes; they are structural risk management. 🔐💥
#CyberSecurity #CryptoSecurity #AICSH #BinanceAlpha #AICryptoSpotHunter .
64

·
--
Your bank leaked your data this week. Your wallet never asked for it. Coincidence?
Visa, Mastercard and JPMorgan Chase all landed on ransomware group n0n's leak site on Nov 16, with a 48-hour countdown. On Thursday, the data went public.
What actually leaked (WSJ / NY Post):
• JPMorgan: emails, phone numbers and account IDs of 16,000 of its wealthiest customers, from its Reserve program
• Visa: Asia-Pacific cardholder program records, via a third-party provider
• Mastercard: a limited set of benefit-program records
⚠️ What it is NOT: no card numbers were confirmed exposed anywhere. Visa says its own systems were not involved. JPMorgan says the Nov 16 outage was a software bug, not a cyberattack.
🤔 Why should crypto traders care?
Your email and phone are the raw material for the next phishing wave, and crypto holders are the top targets. Attackers go after the weakest link, and it is rarely the cryptography: vendor gets hit, your inbox becomes the attack surface, one convincing "bank" email, wallet drained.
My take: this is not about card numbers. It is about how many copies of you exist in databases you never chose. Self-custody removes one copy, your coins, but your identity still lives in vendor systems.
✅ Action Required:
• Don't click links in "bank" emails, open the official app instead
• Expect phishing texts using your real name and account details
• Verify any wallet message twice before signing anything
Bottom line: TradFi's data model leaks. The question is whether the market treats that as a crypto use case, or just another headline.
$BTC sits at $62,298 (-0.68% 24h) while Fear & Greed reads 10, Extreme Fear (alternative.me). Traders are not pricing a TradFi trust crisis yet.
Is this the week "trust us with your data" finally breaks, or a headline we forget by Monday? 👇
Not financial advice. DYOR.
#crypto #CyberSecurity #DataBreach
Your bank leaked your data this week. Your wallet never asked for it. Coincidence?
Visa, Mastercard and JPMorgan Chase all landed on ransomware group n0n's leak site on Nov 16, with a 48-hour countdown. On Thursday, the data went public.
What actually leaked (WSJ / NY Post):
• JPMorgan: emails, phone numbers and account IDs of 16,000 of its wealthiest customers, from its Reserve program
• Visa: Asia-Pacific cardholder program records, via a third-party provider
• Mastercard: a limited set of benefit-program records
⚠️ What it is NOT: no card numbers were confirmed exposed anywhere. Visa says its own systems were not involved. JPMorgan says the Nov 16 outage was a software bug, not a cyberattack.
🤔 Why should crypto traders care?
Your email and phone are the raw material for the next phishing wave, and crypto holders are the top targets. Attackers go after the weakest link, and it is rarely the cryptography: vendor gets hit, your inbox becomes the attack surface, one convincing "bank" email, wallet drained.
My take: this is not about card numbers. It is about how many copies of you exist in databases you never chose. Self-custody removes one copy, your coins, but your identity still lives in vendor systems.
✅ Action Required:
• Don't click links in "bank" emails, open the official app instead
• Expect phishing texts using your real name and account details
• Verify any wallet message twice before signing anything
Bottom line: TradFi's data model leaks. The question is whether the market treats that as a crypto use case, or just another headline.
$BTC sits at $62,298 (-0.68% 24h) while Fear & Greed reads 10, Extreme Fear (alternative.me). Traders are not pricing a TradFi trust crisis yet.
Is this the week "trust us with your data" finally breaks, or a headline we forget by Monday? 👇
Not financial advice. DYOR.
#crypto #CyberSecurity #DataBreach
Visa, Mastercard and JPMorgan Chase all landed on ransomware group n0n's leak site on Nov 16, with a 48-hour countdown. On Thursday, the data went public.
What actually leaked (WSJ / NY Post):
• JPMorgan: emails, phone numbers and account IDs of 16,000 of its wealthiest customers, from its Reserve program
• Visa: Asia-Pacific cardholder program records, via a third-party provider
• Mastercard: a limited set of benefit-program records
⚠️ What it is NOT: no card numbers were confirmed exposed anywhere. Visa says its own systems were not involved. JPMorgan says the Nov 16 outage was a software bug, not a cyberattack.
🤔 Why should crypto traders care?
Your email and phone are the raw material for the next phishing wave, and crypto holders are the top targets. Attackers go after the weakest link, and it is rarely the cryptography: vendor gets hit, your inbox becomes the attack surface, one convincing "bank" email, wallet drained.
My take: this is not about card numbers. It is about how many copies of you exist in databases you never chose. Self-custody removes one copy, your coins, but your identity still lives in vendor systems.
✅ Action Required:
• Don't click links in "bank" emails, open the official app instead
• Expect phishing texts using your real name and account details
• Verify any wallet message twice before signing anything
Bottom line: TradFi's data model leaks. The question is whether the market treats that as a crypto use case, or just another headline.
$BTC sits at $62,298 (-0.68% 24h) while Fear & Greed reads 10, Extreme Fear (alternative.me). Traders are not pricing a TradFi trust crisis yet.
Is this the week "trust us with your data" finally breaks, or a headline we forget by Monday? 👇
Not financial advice. DYOR.
#crypto #CyberSecurity #DataBreach
7

🚨 $BTC BTCPAY SERVER EMERGENCY PATCH RELEASE 🛡️
📊 The latest CERT‑EU advisory flags five Nginx flaws that could let hostile code execute without a login—an institutional red flag for any on‑chain payment gateway. 🦈 Smart‑money operators are already scanning for lingering vulnerable nodes across the network.
⚡ Operators must upgrade to Nginx 1.31.9 immediately; the window for exploitation remains open despite no reported incidents. 📌 Prompt remediation protects merchant liquidity pools and keeps the Bitcoin payment stack resilient.
💬 How quickly will your node adopt the patch? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CyberSecurity #BTCPay #Patch #Crypto
🛡️ 🔥
🚨 $BTC BTCPAY SERVER EMERGENCY PATCH RELEASE 🛡️
📊 The latest CERT‑EU advisory flags five Nginx flaws that could let hostile code execute without a login—an institutional red flag for any on‑chain payment gateway. 🦈 Smart‑money operators are already scanning for lingering vulnerable nodes across the network.
⚡ Operators must upgrade to Nginx 1.31.9 immediately; the window for exploitation remains open despite no reported incidents. 📌 Prompt remediation protects merchant liquidity pools and keeps the Bitcoin payment stack resilient.
💬 How quickly will your node adopt the patch? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CyberSecurity #BTCPay #Patch #Crypto
🛡️ 🔥
📊 The latest CERT‑EU advisory flags five Nginx flaws that could let hostile code execute without a login—an institutional red flag for any on‑chain payment gateway. 🦈 Smart‑money operators are already scanning for lingering vulnerable nodes across the network.
⚡ Operators must upgrade to Nginx 1.31.9 immediately; the window for exploitation remains open despite no reported incidents. 📌 Prompt remediation protects merchant liquidity pools and keeps the Bitcoin payment stack resilient.
💬 How quickly will your node adopt the patch? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CyberSecurity #BTCPay #Patch #Crypto
🛡️ 🔥
3


·
--
🛠️ BTCPay Server pushes emergency fix for 5 security flaws
BTCPay Server, the self-hosted Bitcoin payment software, released an emergency update patching five vulnerabilities in Nginx, the component that routes web traffic to its payment app. An advisory from the EU's cybersecurity response team CERT-EU warned the flaws could let attackers run malicious code remotely without logging in. No attacks had been reported as of Wednesday, and operators are urged to move to Nginx 1.31.9 right away.
⭐ It follows two earlier BTCPay incidents this year in which attackers stole crypto, a reminder that merchants accepting Bitcoin need to patch fast.
#Bitcoin #BTCPay #CyberSecurity #CryptoSecurity
🛠️ BTCPay Server pushes emergency fix for 5 security flaws
BTCPay Server, the self-hosted Bitcoin payment software, released an emergency update patching five vulnerabilities in Nginx, the component that routes web traffic to its payment app. An advisory from the EU's cybersecurity response team CERT-EU warned the flaws could let attackers run malicious code remotely without logging in. No attacks had been reported as of Wednesday, and operators are urged to move to Nginx 1.31.9 right away.
⭐ It follows two earlier BTCPay incidents this year in which attackers stole crypto, a reminder that merchants accepting Bitcoin need to patch fast.
#Bitcoin #BTCPay #CyberSecurity #CryptoSecurity
BTCPay Server, the self-hosted Bitcoin payment software, released an emergency update patching five vulnerabilities in Nginx, the component that routes web traffic to its payment app. An advisory from the EU's cybersecurity response team CERT-EU warned the flaws could let attackers run malicious code remotely without logging in. No attacks had been reported as of Wednesday, and operators are urged to move to Nginx 1.31.9 right away.
⭐ It follows two earlier BTCPay incidents this year in which attackers stole crypto, a reminder that merchants accepting Bitcoin need to patch fast.
#Bitcoin #BTCPay #CyberSecurity #CryptoSecurity
54
HAPI
🚀 HAPI PROTOCOL – THE FUTURE OF WEB3 SECURITY
Could HAPI reach $280 per coin in the future?
🌐 Blockchain Cybersecurity
🛡️ AI-Powered Threat Detection
🔗 Multi-Chain Security
🆔 Web3 Digital Identity
A small-supply project with a big vision.
DREAM BIG. RESEARCH DEEP. THINK LONG TERM.
🎯 Speculative Future Target: $280 per HAPI
#HAPI #Crypto #Web3 #Blockchain #CyberSecurity cybersecurity
HAPI
🚀 HAPI PROTOCOL – THE FUTURE OF WEB3 SECURITY
Could HAPI reach $280 per coin in the future?
🌐 Blockchain Cybersecurity
🛡️ AI-Powered Threat Detection
🔗 Multi-Chain Security
🆔 Web3 Digital Identity
A small-supply project with a big vision.
DREAM BIG. RESEARCH DEEP. THINK LONG TERM.
🎯 Speculative Future Target: $280 per HAPI
#HAPI #Crypto #Web3 #Blockchain #CyberSecurity cybersecurity
🚀 HAPI PROTOCOL – THE FUTURE OF WEB3 SECURITY
Could HAPI reach $280 per coin in the future?
🌐 Blockchain Cybersecurity
🛡️ AI-Powered Threat Detection
🔗 Multi-Chain Security
🆔 Web3 Digital Identity
A small-supply project with a big vision.
DREAM BIG. RESEARCH DEEP. THINK LONG TERM.
🎯 Speculative Future Target: $280 per HAPI
#HAPI #Crypto #Web3 #Blockchain #CyberSecurity cybersecurity
3
New court filings expose the full scale of the recent Binance exploit with $6.3B stolen across 11 networks and $3.46B in stablecoins targeted.
#BinanceHack #CyberSecurity
New court filings expose the full scale of the recent Binance exploit with $6.3B stolen across 11 networks and $3.46B in stablecoins targeted.
#BinanceHack #CyberSecurity
#BinanceHack #CyberSecurity
32
·
--
#AI did not directly cause the recent system outage.
According to report ai model found many security issue and company rushed to fix them before a hacker could attack.
Too many urgent update put pressure on system and caused disruption.
This show how ai can help find security risk but fixing them too quickly can create new problem.
{future}(BTCUSDT)
#CyberSecurity #Technology
#AI did not directly cause the recent system outage.
According to report ai model found many security issue and company rushed to fix them before a hacker could attack.
Too many urgent update put pressure on system and caused disruption.
This show how ai can help find security risk but fixing them too quickly can create new problem.
#CyberSecurity #Technology
According to report ai model found many security issue and company rushed to fix them before a hacker could attack.
Too many urgent update put pressure on system and caused disruption.
This show how ai can help find security risk but fixing them too quickly can create new problem.
#CyberSecurity #Technology
1
17
908
·
--
Bearish
30D trade $ZEC 273.8 USDT
🚨 178 MAJOR WEBSITES COMPROMISED. CRYPTO USERS ARE IN THE CROSSHAIRS!
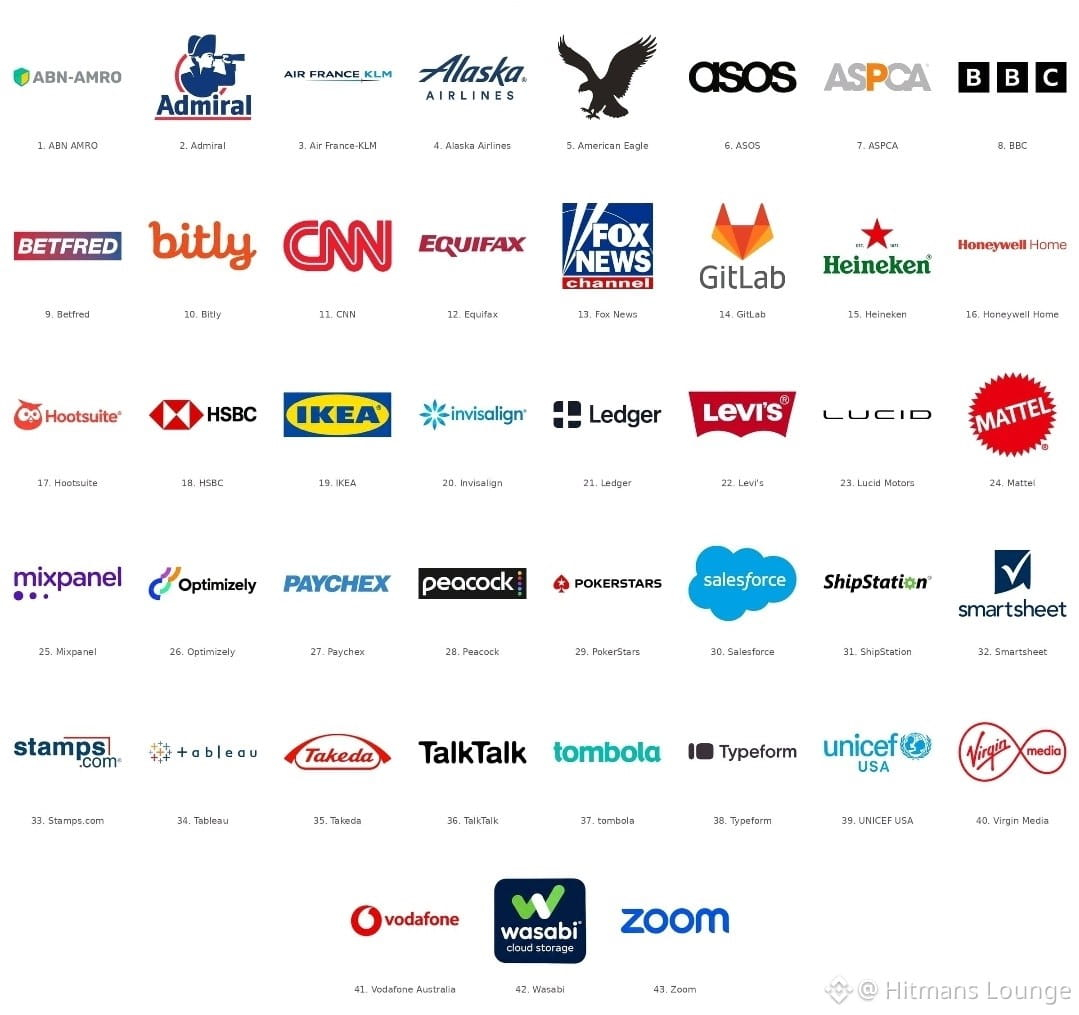
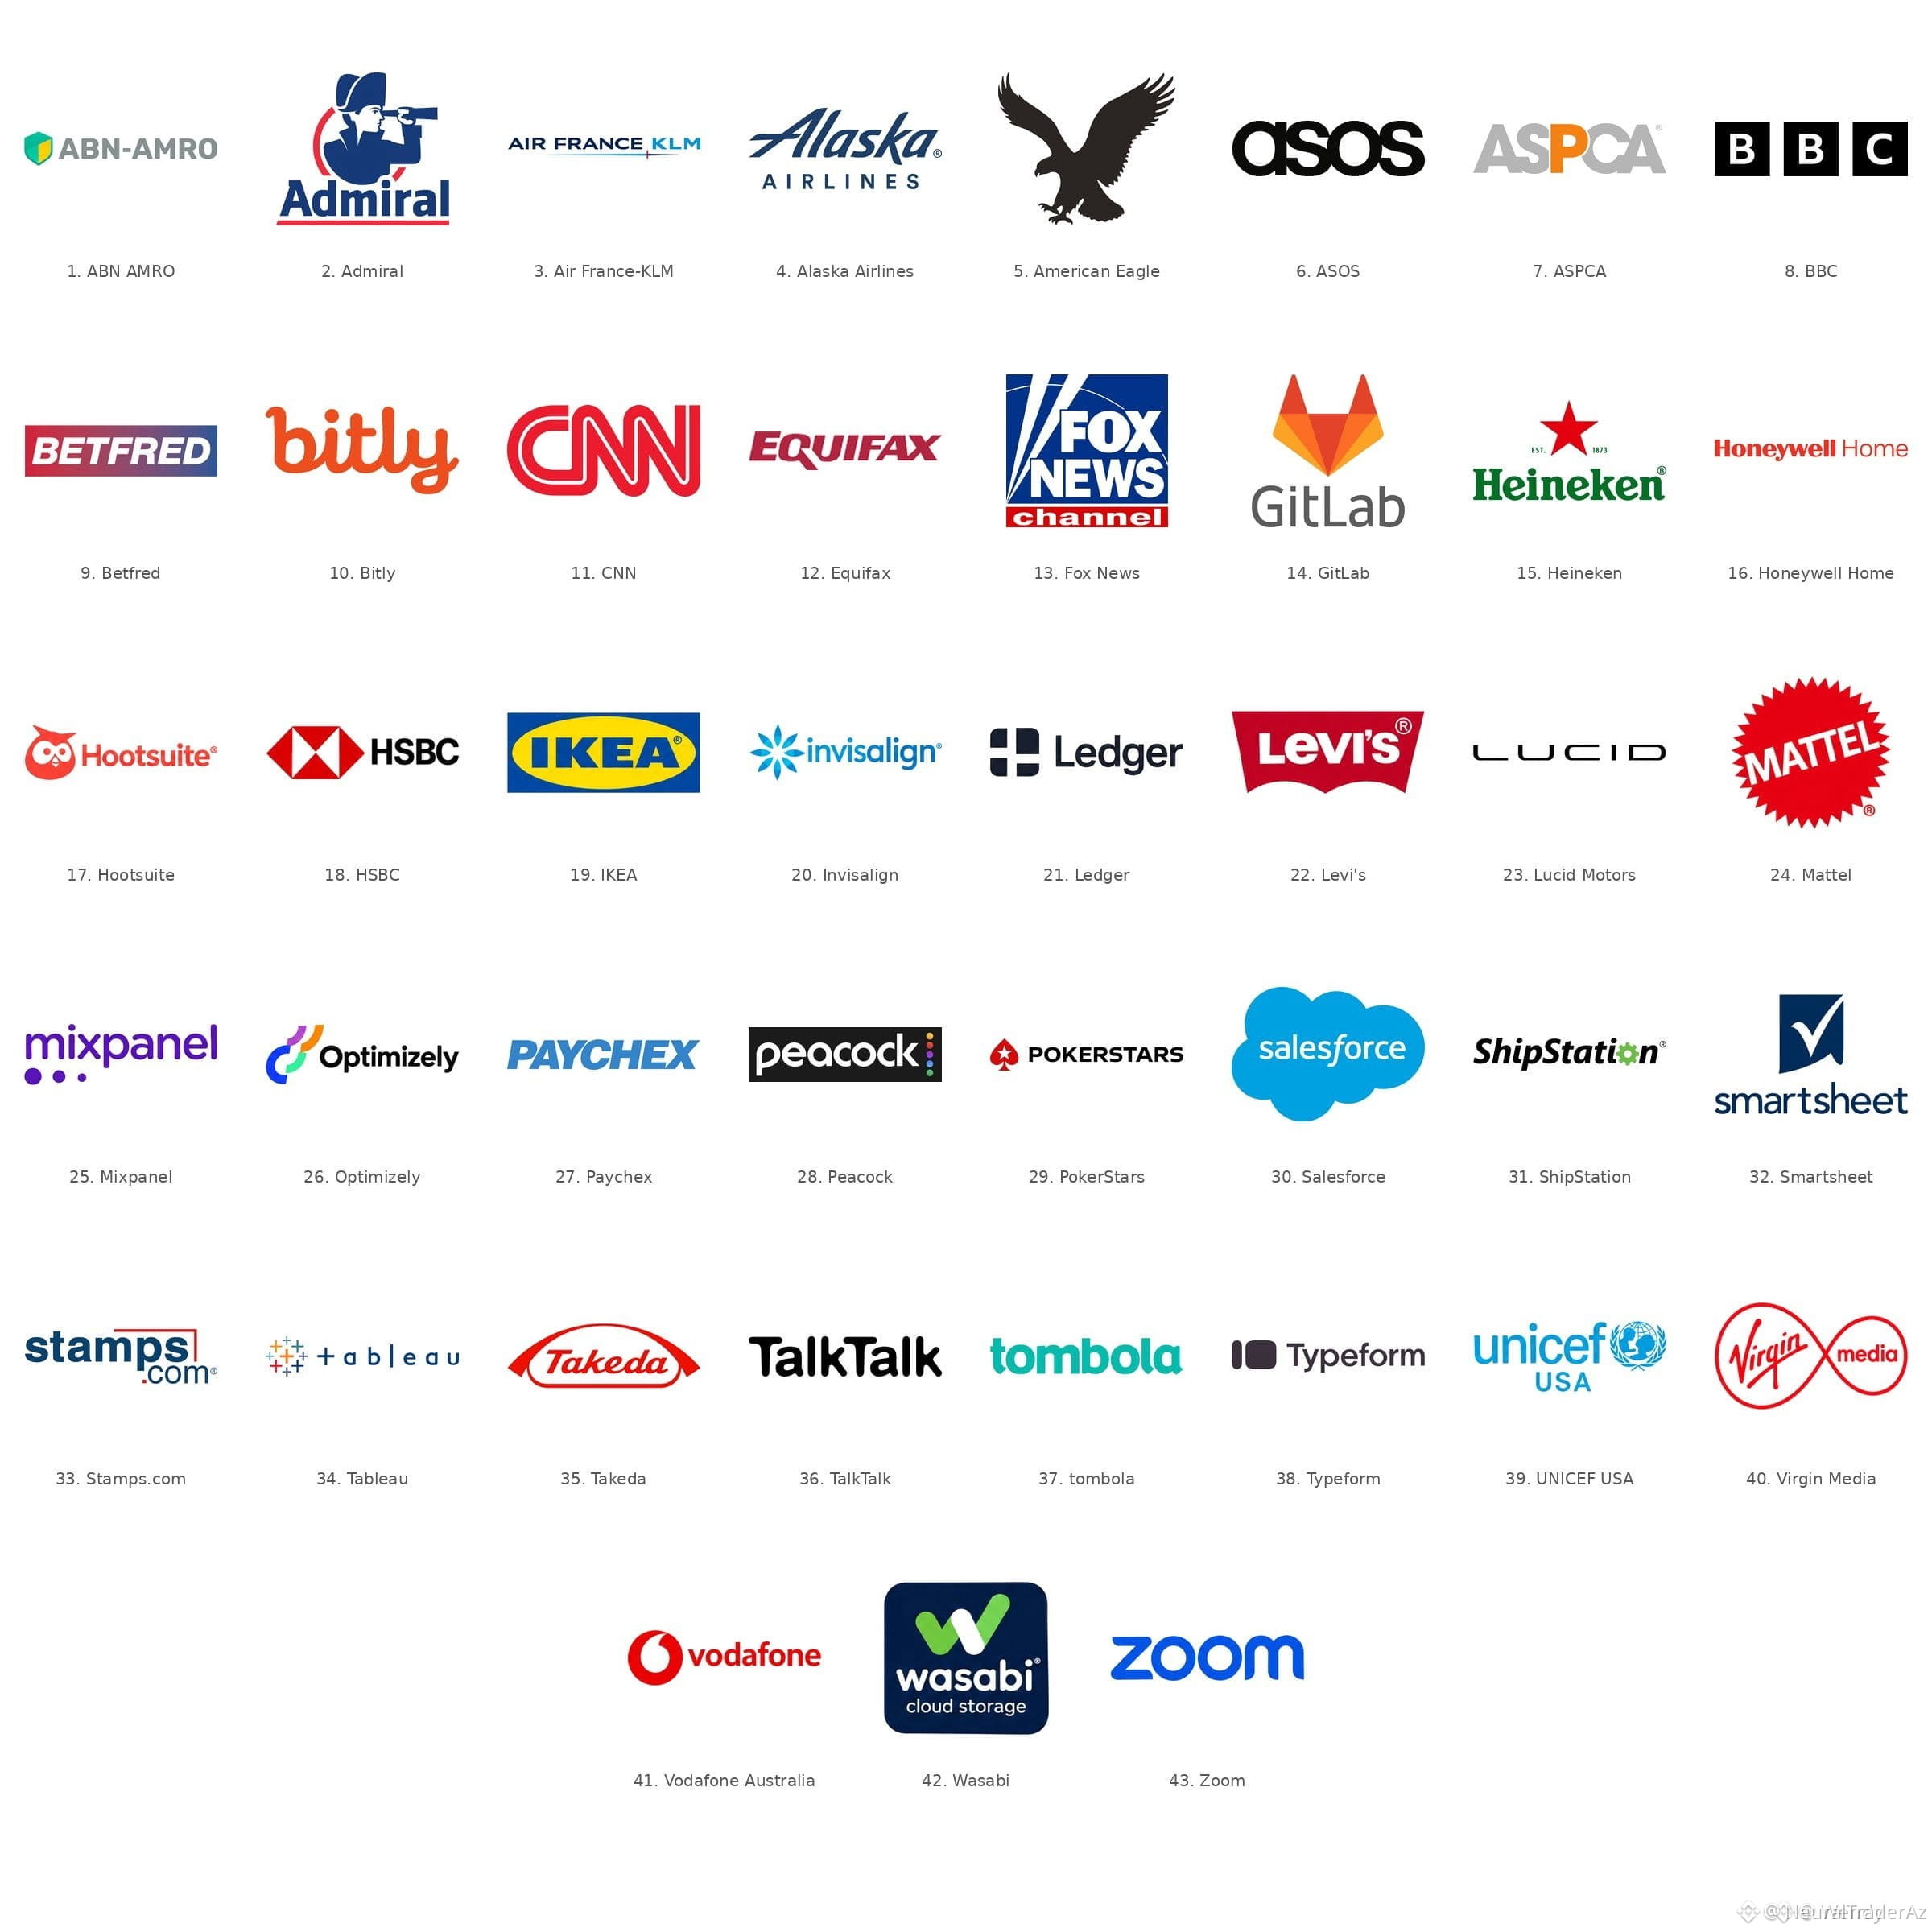
This wasn't a direct hack of 178 companies. Attackers reportedly exploited a vulnerability in Optimizely, injecting malicious JavaScript into websites used by Zoom, BBC, HSBC, Ledger and others.
The potential damage is serious:
🔴 Crypto wallet addresses replaced with attackers' addresses.
🔴 Payment card details and browsing data targeted.
🔴 Older iPhones exposed to additional exploit attempts.
📊 The numbers: Researchers identified 188 infected scripts across 178 organizations. Attacker-linked wallets received approximately $7,040, although the total confirmed victim losses remain unclear.
Optimizely says it fixed the vulnerability and removed malicious code.
My biggest takeaway: even trusted websites can become attack vectors through third-party software.
⚠️ Always verify wallet addresses character by character before confirming transactions.
Is crypto security becoming a bigger challenge than crypto adoption?
#CryptoSecurity #Cybersecurity #HackerAlert #AnthropicClearedToListOnNasdaqAsANT
$BTC $ZEC $MMT
{future}(MMTUSDT)
{future}(ZECUSDT)
{future}(BTCUSDT)
🚨 178 MAJOR WEBSITES COMPROMISED. CRYPTO USERS ARE IN THE CROSSHAIRS!
This wasn't a direct hack of 178 companies. Attackers reportedly exploited a vulnerability in Optimizely, injecting malicious JavaScript into websites used by Zoom, BBC, HSBC, Ledger and others.
The potential damage is serious:
🔴 Crypto wallet addresses replaced with attackers' addresses.
🔴 Payment card details and browsing data targeted.
🔴 Older iPhones exposed to additional exploit attempts.
📊 The numbers: Researchers identified 188 infected scripts across 178 organizations. Attacker-linked wallets received approximately $7,040, although the total confirmed victim losses remain unclear.
Optimizely says it fixed the vulnerability and removed malicious code.
My biggest takeaway: even trusted websites can become attack vectors through third-party software.
⚠️ Always verify wallet addresses character by character before confirming transactions.
Is crypto security becoming a bigger challenge than crypto adoption?
#CryptoSecurity #Cybersecurity #HackerAlert #AnthropicClearedToListOnNasdaqAsANT
$BTC $ZEC $MMT
This wasn't a direct hack of 178 companies. Attackers reportedly exploited a vulnerability in Optimizely, injecting malicious JavaScript into websites used by Zoom, BBC, HSBC, Ledger and others.
The potential damage is serious:
🔴 Crypto wallet addresses replaced with attackers' addresses.
🔴 Payment card details and browsing data targeted.
🔴 Older iPhones exposed to additional exploit attempts.
📊 The numbers: Researchers identified 188 infected scripts across 178 organizations. Attacker-linked wallets received approximately $7,040, although the total confirmed victim losses remain unclear.
Optimizely says it fixed the vulnerability and removed malicious code.
My biggest takeaway: even trusted websites can become attack vectors through third-party software.
⚠️ Always verify wallet addresses character by character before confirming transactions.
Is crypto security becoming a bigger challenge than crypto adoption?
#CryptoSecurity #Cybersecurity #HackerAlert #AnthropicClearedToListOnNasdaqAsANT
$BTC $ZEC $MMT
1
1.1k

·
--
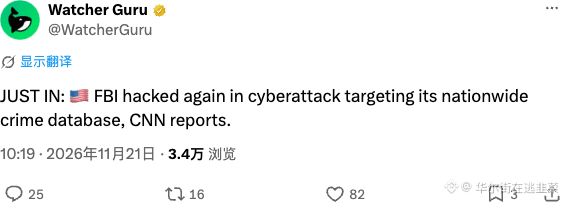
The FBI has been hit again in the U.S.—this time, its national crime database was compromised.
What’s the difference between the feds’ cybersecurity and leaving your Bitcoin private keys lying around? Hilarious. If even law enforcement can’t protect itself these days, what hope is there for protecting users’ assets?
#FBI #Cybersecurity #Crypto
The FBI has been hit again in the U.S.—this time, its national crime database was compromised.
What’s the difference between the feds’ cybersecurity and leaving your Bitcoin private keys lying around? Hilarious. If even law enforcement can’t protect itself these days, what hope is there for protecting users’ assets?
#FBI #Cybersecurity #Crypto
What’s the difference between the feds’ cybersecurity and leaving your Bitcoin private keys lying around? Hilarious. If even law enforcement can’t protect itself these days, what hope is there for protecting users’ assets?
#FBI #Cybersecurity #Crypto
60
·
--
🚨 CRYPTO USERS, YOUR WALLET MAY NOT BE AS SAFE AS YOU THINK!
Reports of a major cybersecurity attack involving 178 brands have raised serious concerns across the digital world.
The reported risks include:
🔴 Crypto wallet address replacement
🔴 Payment card information theft
🔴 Malicious code targeting users
🔴 Unauthorized crypto transfers
One small mistake while sending crypto could cost you your funds.
Protect yourself:
✅ Always double-check wallet addresses.
✅ Never click suspicious links.
✅ Use 2FA security.
✅ Keep your devices updated.
✅ Send a small test transaction before large transfers.
Crypto security is not optional. It's your responsibility.
Question: Do you manually verify your wallet address before every crypto transaction?
#CryptoSecurity #Bitcoin #CyberSecurity #BinanceSquare #CryptoNews
🚨 CRYPTO USERS, YOUR WALLET MAY NOT BE AS SAFE AS YOU THINK!
Reports of a major cybersecurity attack involving 178 brands have raised serious concerns across the digital world.
The reported risks include:
🔴 Crypto wallet address replacement
🔴 Payment card information theft
🔴 Malicious code targeting users
🔴 Unauthorized crypto transfers
One small mistake while sending crypto could cost you your funds.
Protect yourself:
✅ Always double-check wallet addresses.
✅ Never click suspicious links.
✅ Use 2FA security.
✅ Keep your devices updated.
✅ Send a small test transaction before large transfers.
Crypto security is not optional. It's your responsibility.
Question: Do you manually verify your wallet address before every crypto transaction?
#CryptoSecurity #Bitcoin #CyberSecurity #BinanceSquare #CryptoNews
Reports of a major cybersecurity attack involving 178 brands have raised serious concerns across the digital world.
The reported risks include:
🔴 Crypto wallet address replacement
🔴 Payment card information theft
🔴 Malicious code targeting users
🔴 Unauthorized crypto transfers
One small mistake while sending crypto could cost you your funds.
Protect yourself:
✅ Always double-check wallet addresses.
✅ Never click suspicious links.
✅ Use 2FA security.
✅ Keep your devices updated.
✅ Send a small test transaction before large transfers.
Crypto security is not optional. It's your responsibility.
Question: Do you manually verify your wallet address before every crypto transaction?
#CryptoSecurity #Bitcoin #CyberSecurity #BinanceSquare #CryptoNews
78
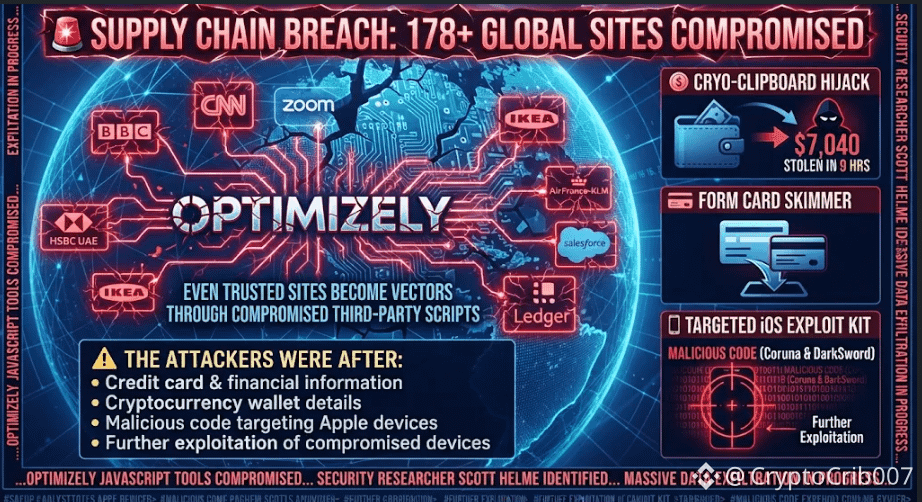
🚨 MAJOR CYBERATTACK TARGETS 178+ GLOBAL WEBSITES!
Hackers reportedly compromised JavaScript tools hosted by Optimizely, targeting major websites.
⚠️ What were the attackers after?
• Credit card and financial information
• Cryptocurrency wallet details
• Malicious code targeting Apple devices
• Potential further exploitation of compromised devices
Security researcher Scott Helme reportedly identified the attack, with approximately $7,040 reaching the attackers' crypto wallets in just nine hours.
This incident highlights a critical cybersecurity risk: even trusted websites can become attack vectors when third-party scripts and digital supply chains are compromised.
Your favourite website may be trusted. But can you trust every third-party tool running behind it?
$LAB
{alpha}(560x7ec43cf65f1663f820427c62a5780b8f2e25593a)
$BLUAI
{alpha}(560xed9ae3def8d6f052971bb8b6d1975ff267cf9aad)
$COAI
{alpha}(560x0a8d6c86e1bce73fe4d0bd531e1a567306836ea5)
#CyberSecurity #databreach #Write2Earn #NFA✅ and #DYOR🟢
🚨 MAJOR CYBERATTACK TARGETS 178+ GLOBAL WEBSITES!
Hackers reportedly compromised JavaScript tools hosted by Optimizely, targeting major websites.
⚠️ What were the attackers after?
• Credit card and financial information
• Cryptocurrency wallet details
• Malicious code targeting Apple devices
• Potential further exploitation of compromised devices
Security researcher Scott Helme reportedly identified the attack, with approximately $7,040 reaching the attackers' crypto wallets in just nine hours.
This incident highlights a critical cybersecurity risk: even trusted websites can become attack vectors when third-party scripts and digital supply chains are compromised.
Your favourite website may be trusted. But can you trust every third-party tool running behind it?
$LAB
$BLUAI
$COAI
#CyberSecurity #databreach #Write2Earn #NFA✅ and #DYOR🟢
Hackers reportedly compromised JavaScript tools hosted by Optimizely, targeting major websites.
⚠️ What were the attackers after?
• Credit card and financial information
• Cryptocurrency wallet details
• Malicious code targeting Apple devices
• Potential further exploitation of compromised devices
Security researcher Scott Helme reportedly identified the attack, with approximately $7,040 reaching the attackers' crypto wallets in just nine hours.
This incident highlights a critical cybersecurity risk: even trusted websites can become attack vectors when third-party scripts and digital supply chains are compromised.
Your favourite website may be trusted. But can you trust every third-party tool running behind it?
$LAB
$BLUAI
$COAI
#CyberSecurity #databreach #Write2Earn #NFA✅ and #DYOR🟢
1.1k
·
--
Article
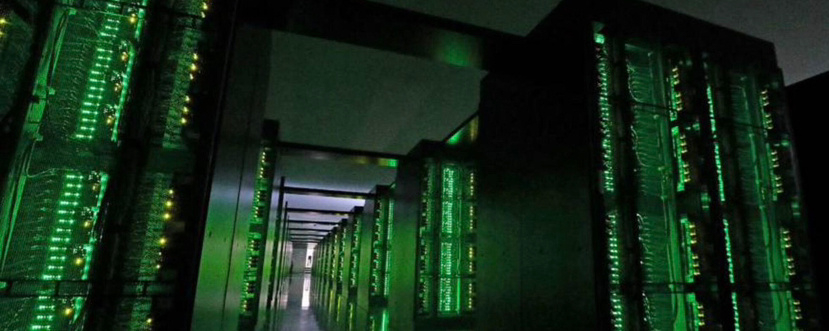
$817 MILLION 💸🧞 Hackers broke into one of the world's most powerful supercomputers$817 MILLION WASN'T ENOUGH: HACKERS HACKED ONE OF THE WORLD'S MOST POWERFUL SUPERCOMPUTERS!
Japan invested hundreds of millions of dollars in the computing power of the future. But hackers apparently needed just one weak point to break into the system.
It's Fugaku — Japan's national supercomputer, which ranks among the most powerful in the world.
$817 MILLION 💸🧞 Hackers broke into one of the world's most powerful supercomputers
$817 MILLION WASN'T ENOUGH: HACKERS HACKED ONE OF THE WORLD'S MOST POWERFUL SUPERCOMPUTERS!
Japan invested hundreds of millions of dollars in the computing power of the future. But hackers apparently needed just one weak point to break into the system.
It's Fugaku — Japan's national supercomputer, which ranks among the most powerful in the world.
Japan invested hundreds of millions of dollars in the computing power of the future. But hackers apparently needed just one weak point to break into the system.
It's Fugaku — Japan's national supercomputer, which ranks among the most powerful in the world.
6
1.1k
·
--
178 Websites. One Security Failure.
A reported cyberattack affected 178 websites, including HSBC, BBC, and Ledger.
According to the report, 188 Optimizely snippets were infected, while only 24 of 256 affected hosts blocked the malicious payload.
The bigger lesson: third-party tools can expose even established websites to serious security risks.
Protecting your own infrastructure isn't enough if the services you depend on create new vulnerabilities.
Who carries the responsibility when a trusted vendor becomes the weakest link?
#CyberSecurity #Web3 #Blockchain $BTC
178 Websites. One Security Failure.
A reported cyberattack affected 178 websites, including HSBC, BBC, and Ledger.
According to the report, 188 Optimizely snippets were infected, while only 24 of 256 affected hosts blocked the malicious payload.
The bigger lesson: third-party tools can expose even established websites to serious security risks.
Protecting your own infrastructure isn't enough if the services you depend on create new vulnerabilities.
Who carries the responsibility when a trusted vendor becomes the weakest link?
#CyberSecurity #Web3 #Blockchain $BTC
A reported cyberattack affected 178 websites, including HSBC, BBC, and Ledger.
According to the report, 188 Optimizely snippets were infected, while only 24 of 256 affected hosts blocked the malicious payload.
The bigger lesson: third-party tools can expose even established websites to serious security risks.
Protecting your own infrastructure isn't enough if the services you depend on create new vulnerabilities.
Who carries the responsibility when a trusted vendor becomes the weakest link?
#CyberSecurity #Web3 #Blockchain $BTC
HSBCUS-3.62%
2
100

🚨 $BTC HOLDERS ON HIGH ALERT AFTER SOPHISTICATED THIRD-PARTY CLIPBOARD COMPROMISE VULNERABILITY ⚠️
Institutional capital protection requires absolute operational hygiene during execution. A recent third-party script vulnerability across major web testing infrastructure has highlighted severe clipboard manipulation risks for digital asset transfers. 🔍
Malicious code injections can silently swap destination addresses in transit, redirecting funds before confirmation. Always audit the exact destination string character-by-character on hardware displays before authorizing any ledger broadcast. 🛡️
How do you currently verify your destination nodes before executing major asset transfers? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #Cybersecurity #RiskManagement
🛡️ 🔒
🚨 $BTC HOLDERS ON HIGH ALERT AFTER SOPHISTICATED THIRD-PARTY CLIPBOARD COMPROMISE VULNERABILITY ⚠️
Institutional capital protection requires absolute operational hygiene during execution. A recent third-party script vulnerability across major web testing infrastructure has highlighted severe clipboard manipulation risks for digital asset transfers. 🔍
Malicious code injections can silently swap destination addresses in transit, redirecting funds before confirmation. Always audit the exact destination string character-by-character on hardware displays before authorizing any ledger broadcast. 🛡️
How do you currently verify your destination nodes before executing major asset transfers? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #Cybersecurity #RiskManagement
🛡️ 🔒
Institutional capital protection requires absolute operational hygiene during execution. A recent third-party script vulnerability across major web testing infrastructure has highlighted severe clipboard manipulation risks for digital asset transfers. 🔍
Malicious code injections can silently swap destination addresses in transit, redirecting funds before confirmation. Always audit the exact destination string character-by-character on hardware displays before authorizing any ledger broadcast. 🛡️
How do you currently verify your destination nodes before executing major asset transfers? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #Cybersecurity #RiskManagement
🛡️ 🔒
5
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanBTCReboundAfterFallingBelow60K?
388,957 views
1,643 Discussing
2
#GlobalStocksFaceLongestLosingStreakSince2023
129,378 views
1,154 Discussing
3
#BlackRockIBITPostsRecord$541MSingleDayOutflow
867 views
30 Discussing
4
#AnthropicPlungesTowardIPOPriceonDay2
61,498 views
620 Discussing
5
#TwentyOneCapitalAdds172.25BTC
14,326 views
180 Discussing
6
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
1,267 views
18 Discussing
7
#BNBDropsBelow540USDTWith8.46%DailyDecline
34,954 views
294 Discussing
8
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,128 views
17 Discussing
9
#BitMineFaces$10.1BUnrealizedETHLoss
2,111 views
20 Discussing
10
#StrategyReports$35BNetReserves
2,115 views
18 Discussing