
#cisa
cisa
527 views
9 Discussing
Hot
Latest

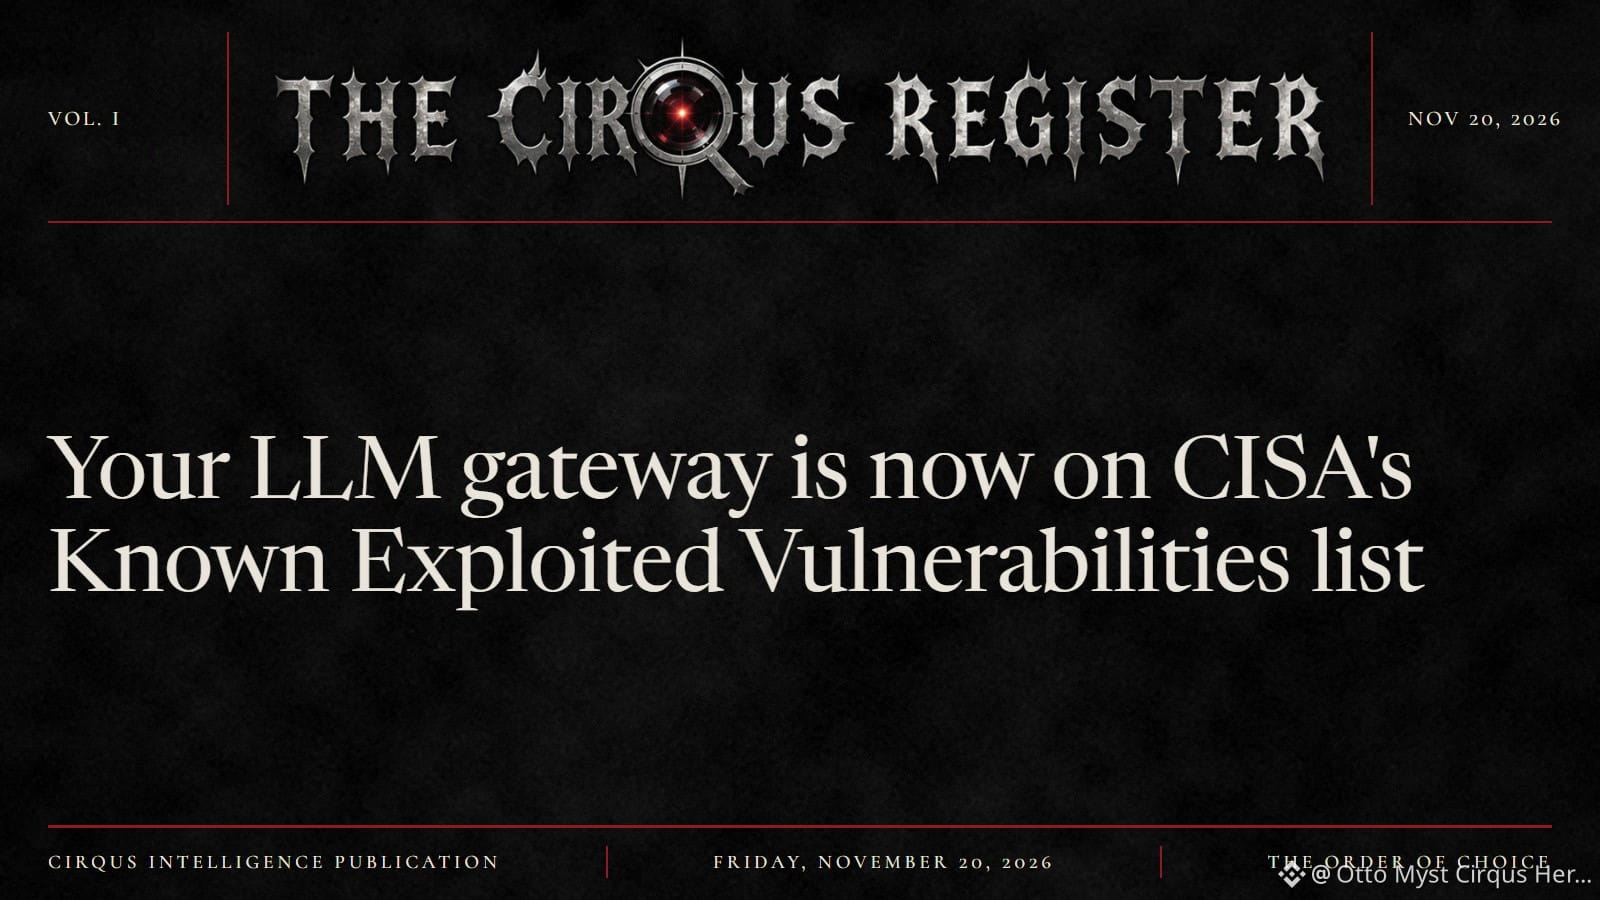
Your LLM gateway is now on CISA's Known Exploited Vulnerabilities list.
On 18 Nov, CISA added CVE-2026-40217 (BerriAI LiteLLM) to KEV, along with three other CVEs. KEV means exploitation was observed in the wild. Per the BerriAI advisory, code can escape a custom-code sandbox and run inside the proxy process.
Why it matters: a gateway may hold your provider API keys. By default the endpoint needs proxy-admin credentials, so this is not "every gateway is owned." Risk depends on your version, configuration and who can reach it.
This is not about $BNB or price. It is about the plumbing under your AI tools.
Do now:
• Upgrade to 1.83.11 or later
• Can't yet? Block POST /guardrails/test_custom_code at your proxy
• Restrict access to it and review logs for unexpected requests
Verdict: PROVEN, confidence high. That covers the KEV listing, not your own exposure.
Watchpoint: 2 Dec 2026 is CISA's deadline for US federal agencies. It is an administrative date, not a patch date.
If one gateway holds every key you own, is it still just a gateway? Do you know where yours is exposed?
#CISA #LLMSecurity #CyberSecurity
Your LLM gateway is now on CISA's Known Exploited Vulnerabilities list.
On 18 Nov, CISA added CVE-2026-40217 (BerriAI LiteLLM) to KEV, along with three other CVEs. KEV means exploitation was observed in the wild. Per the BerriAI advisory, code can escape a custom-code sandbox and run inside the proxy process.
Why it matters: a gateway may hold your provider API keys. By default the endpoint needs proxy-admin credentials, so this is not "every gateway is owned." Risk depends on your version, configuration and who can reach it.
This is not about $BNB or price. It is about the plumbing under your AI tools.
Do now:
• Upgrade to 1.83.11 or later
• Can't yet? Block POST /guardrails/test_custom_code at your proxy
• Restrict access to it and review logs for unexpected requests
Verdict: PROVEN, confidence high. That covers the KEV listing, not your own exposure.
Watchpoint: 2 Dec 2026 is CISA's deadline for US federal agencies. It is an administrative date, not a patch date.
If one gateway holds every key you own, is it still just a gateway? Do you know where yours is exposed?
#CISA #LLMSecurity #CyberSecurity
On 18 Nov, CISA added CVE-2026-40217 (BerriAI LiteLLM) to KEV, along with three other CVEs. KEV means exploitation was observed in the wild. Per the BerriAI advisory, code can escape a custom-code sandbox and run inside the proxy process.
Why it matters: a gateway may hold your provider API keys. By default the endpoint needs proxy-admin credentials, so this is not "every gateway is owned." Risk depends on your version, configuration and who can reach it.
This is not about $BNB or price. It is about the plumbing under your AI tools.
Do now:
• Upgrade to 1.83.11 or later
• Can't yet? Block POST /guardrails/test_custom_code at your proxy
• Restrict access to it and review logs for unexpected requests
Verdict: PROVEN, confidence high. That covers the KEV listing, not your own exposure.
Watchpoint: 2 Dec 2026 is CISA's deadline for US federal agencies. It is an administrative date, not a patch date.
If one gateway holds every key you own, is it still just a gateway? Do you know where yours is exposed?
#CISA #LLMSecurity #CyberSecurity
77

·
--
The U.S. government has also started using AI to look for code vulnerabilities. Anthropic is doing work for CISA, scanning federal systems
This is one step earlier than even the encryption community. Over here, our audits still rely on outsourced teams manually scanning with AI assistance, but having AI directly probe the core codebase? If something goes wrong, who’s responsible?
Once on-chain code is deployed, it becomes an iron rule. If AI vulnerability hunting really takes off, it will either help hackers or help auditors—it's a double-edged sword taken to the extreme. #AI #CISA $BTC
{future}(BTCUSDT)
The U.S. government has also started using AI to look for code vulnerabilities. Anthropic is doing work for CISA, scanning federal systems
This is one step earlier than even the encryption community. Over here, our audits still rely on outsourced teams manually scanning with AI assistance, but having AI directly probe the core codebase? If something goes wrong, who’s responsible?
Once on-chain code is deployed, it becomes an iron rule. If AI vulnerability hunting really takes off, it will either help hackers or help auditors—it's a double-edged sword taken to the extreme. #AI #CISA $BTC
This is one step earlier than even the encryption community. Over here, our audits still rely on outsourced teams manually scanning with AI assistance, but having AI directly probe the core codebase? If something goes wrong, who’s responsible?
Once on-chain code is deployed, it becomes an iron rule. If AI vulnerability hunting really takes off, it will either help hackers or help auditors—it's a double-edged sword taken to the extreme. #AI #CISA $BTC
190
·
--
CISA adds actively exploited vulnerabilities from $Cisco, $PaloAltoNetworks
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #CISA
CISA adds actively exploited vulnerabilities from $Cisco, $PaloAltoNetworks
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #CISA
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #CISA
50
·
--
Cyberattack on water services in Minnesota (July 26-27)
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #CISA
Cyberattack on water services in Minnesota (July 26-27)
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #CISA
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #CISA
80
·
--
🚨 APPLE LAUNCHES EMERGENCY PATCH AFTER "ZERO-CLICK" VULNERABILITY IN COREGRAPHICS 🍏🛡️
Apple responds with critical security updates to close a zero-day gap that allowed remote code execution without any user interaction 📊
Key points from the cybersecurity report:
⚠️ "Zero-Click" Threat: The flaw in CoreGraphics allowed malicious code execution simply by processing an infected file, with no screen tap required.
📱 Affected devices: The update applies to the iPhone 11 and later, compatible iPads, and Mac computers.
🏛️ CISA Alert: The U.S. agency gave federal institutions a maximum of 3 days to patch their systems and audit their infrastructure.
Do you think the growing sophistication of zero-click attacks will accelerate the adoption of decentralized systems and military-grade encryption to protect sensitive data.
💬👇 I’m reading your comments!
#Cybersecurity #CoreGraphics #TechNews #CISA #CryptoCommunity
$AAPLB
{spot}(AAPLBUSDT)
$BTC
{spot}(BTCUSDT)
$ETH
{spot}(ETHUSDT)
🚨 APPLE LAUNCHES EMERGENCY PATCH AFTER "ZERO-CLICK" VULNERABILITY IN COREGRAPHICS 🍏🛡️
Apple responds with critical security updates to close a zero-day gap that allowed remote code execution without any user interaction 📊
Key points from the cybersecurity report:
⚠️ "Zero-Click" Threat: The flaw in CoreGraphics allowed malicious code execution simply by processing an infected file, with no screen tap required.
📱 Affected devices: The update applies to the iPhone 11 and later, compatible iPads, and Mac computers.
🏛️ CISA Alert: The U.S. agency gave federal institutions a maximum of 3 days to patch their systems and audit their infrastructure.
Do you think the growing sophistication of zero-click attacks will accelerate the adoption of decentralized systems and military-grade encryption to protect sensitive data.
💬👇 I’m reading your comments!
#Cybersecurity #CoreGraphics #TechNews #CISA #CryptoCommunity
$AAPLB
$BTC
$ETH
Apple responds with critical security updates to close a zero-day gap that allowed remote code execution without any user interaction 📊
Key points from the cybersecurity report:
⚠️ "Zero-Click" Threat: The flaw in CoreGraphics allowed malicious code execution simply by processing an infected file, with no screen tap required.
📱 Affected devices: The update applies to the iPhone 11 and later, compatible iPads, and Mac computers.
🏛️ CISA Alert: The U.S. agency gave federal institutions a maximum of 3 days to patch their systems and audit their infrastructure.
Do you think the growing sophistication of zero-click attacks will accelerate the adoption of decentralized systems and military-grade encryption to protect sensitive data.
💬👇 I’m reading your comments!
#Cybersecurity #CoreGraphics #TechNews #CISA #CryptoCommunity
$AAPLB
$BTC
$ETH
82

🚨 CISA Agency Adds 7 New Security Vulnerabilities to the Exploited Risks List
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced the addition of seven new security vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog. This addition comes after the exploitation of these vulnerabilities was observed by malicious actors to deploy malware such as cryptocurrency-mining tools and reverse-access components.
━━━━━━━━━━━━━━
📊 Impact: 📊 Medium
🏷️ OTHER
#Cybersecurity #CISA #Vulnerabilities #Security #Malware
📰 Source: thehackernews.com
🚨 CISA Agency Adds 7 New Security Vulnerabilities to the Exploited Risks List
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced the addition of seven new security vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog. This addition comes after the exploitation of these vulnerabilities was observed by malicious actors to deploy malware such as cryptocurrency-mining tools and reverse-access components.
━━━━━━━━━━━━━━
📊 Impact: 📊 Medium
🏷️ OTHER
#Cybersecurity #CISA #Vulnerabilities #Security #Malware
📰 Source: thehackernews.com
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced the addition of seven new security vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog. This addition comes after the exploitation of these vulnerabilities was observed by malicious actors to deploy malware such as cryptocurrency-mining tools and reverse-access components.
━━━━━━━━━━━━━━
📊 Impact: 📊 Medium
🏷️ OTHER
#Cybersecurity #CISA #Vulnerabilities #Security #Malware
📰 Source: thehackernews.com
14
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaLoses$2.7TrillionInMonthAndAHalf
18,753 views
118 Discussing
2
#CanBTCReboundAfterFallingBelow60K?
762,868 views
2,974 Discussing
3
#GlobalStocksFaceLongestLosingStreakSince2023
275,478 views
1,983 Discussing
4
#BlackRockIBITPostsRecord$541MSingleDayOutflow
32,865 views
90 Discussing
5
#AnthropicPlungesTowardIPOPriceonDay2
141,817 views
1,208 Discussing
6
#TwentyOneCapitalAdds172.25BTC
64,345 views
660 Discussing
7
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
8,181 views
50 Discussing
8
#BNBDropsBelow540USDTWith8.46%DailyDecline
77,451 views
649 Discussing
9
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
2,590 views
22 Discussing
10
#BitMineFaces$10.1BUnrealizedETHLoss
5,462 views
28 Discussing