
#exploit
exploit
109,914 views
416 Discussing
Hot
Latest
Wrapped Monero token dropped ninety nine point eight percent after suspected thirteen million dollar exploit in market today and now
📉 #Monero #Exploit
$BTC
Wrapped Monero token dropped ninety nine point eight percent after suspected thirteen million dollar exploit in market today and now
📉 #Monero #Exploit
$BTC
📉 #Monero #Exploit
$BTC
60

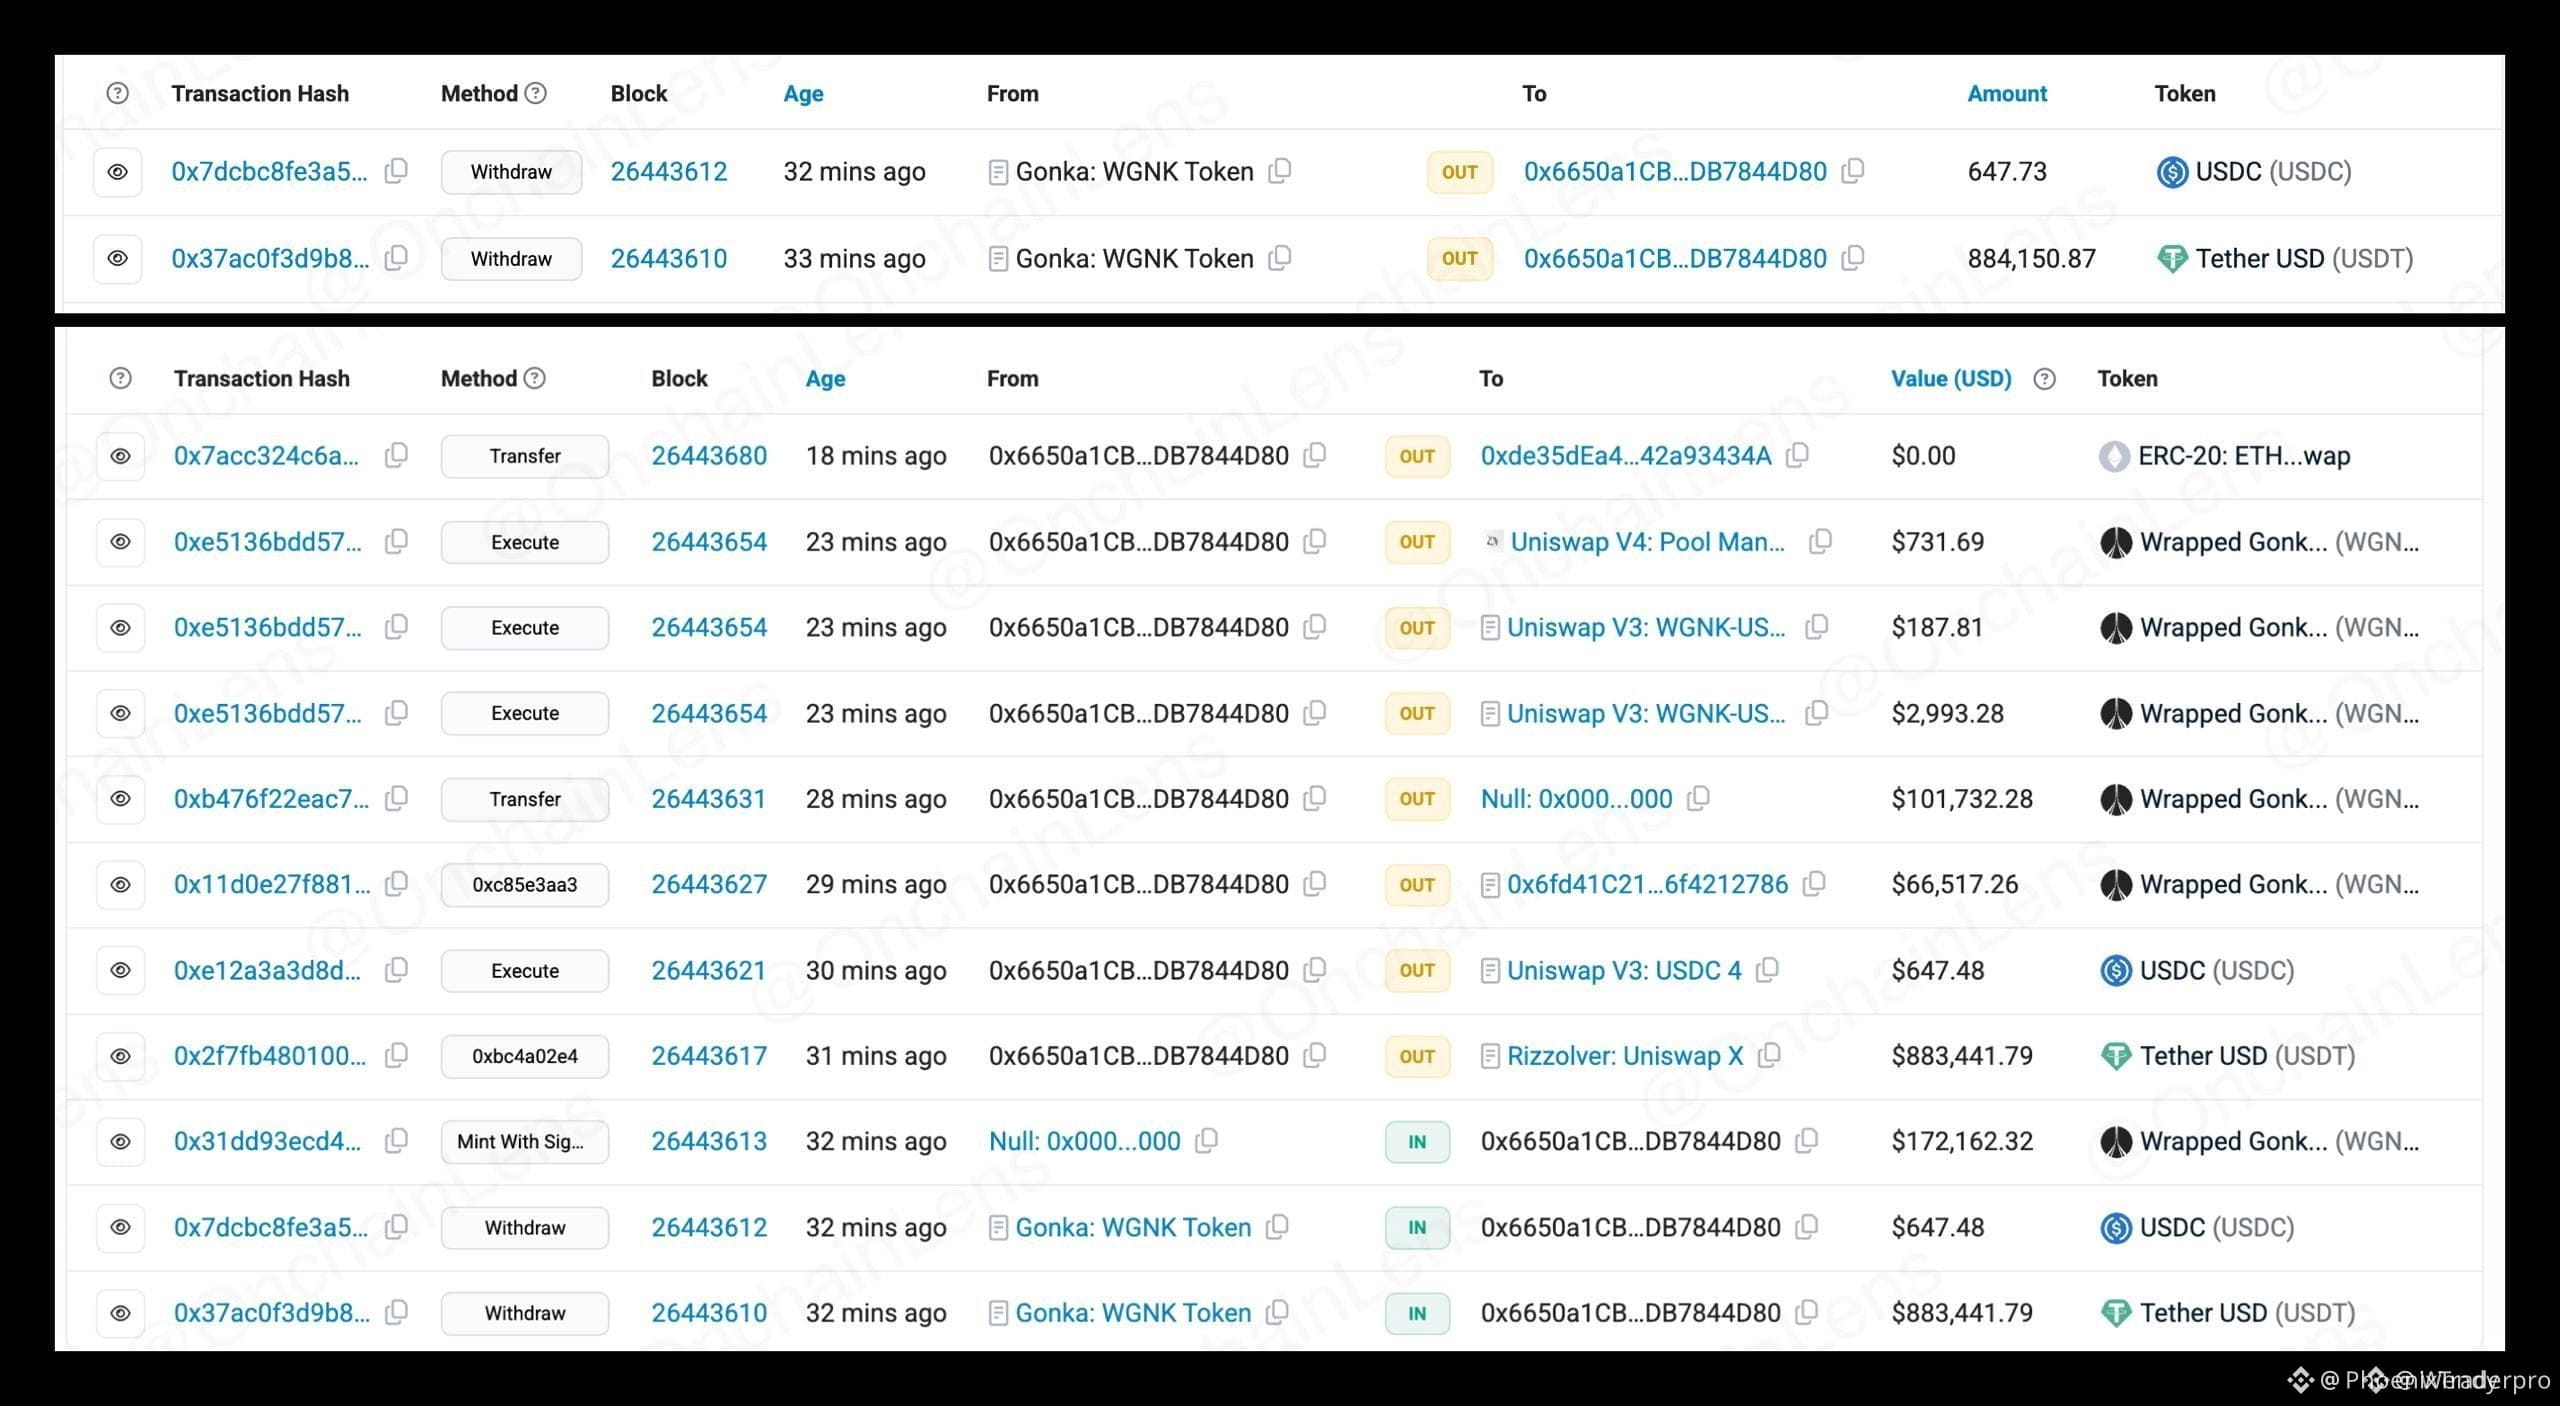
🚨 $ETH EXPLOIT UNVEILS $1M BRIDGE BREACH! 🦈
On‑chain forensics show a compromised bridge BLS group key at Gonka AI, letting an attacker siphon ~ $884.8K USDT/USDC and mint $172K unbacked WGNK. 📊
The flow hit Uniswap and bounced across multiple wallets, a classic liquidity sweep that lets whales clean the floor before the dust settles. 🦈⚡
While the breach isn’t independently verified yet, the sheer volume flags a red alert for any $ETH ‑linked exposure. 💬 What defensive moves are you taking to shield your positions?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #Exploit #Crypto
🚀 ⚡
🚨 $ETH EXPLOIT UNVEILS $1M BRIDGE BREACH! 🦈
On‑chain forensics show a compromised bridge BLS group key at Gonka AI, letting an attacker siphon ~ $884.8K USDT/USDC and mint $172K unbacked WGNK. 📊
The flow hit Uniswap and bounced across multiple wallets, a classic liquidity sweep that lets whales clean the floor before the dust settles. 🦈⚡
While the breach isn’t independently verified yet, the sheer volume flags a red alert for any $ETH ‑linked exposure. 💬 What defensive moves are you taking to shield your positions?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #Exploit #Crypto
🚀 ⚡
On‑chain forensics show a compromised bridge BLS group key at Gonka AI, letting an attacker siphon ~ $884.8K USDT/USDC and mint $172K unbacked WGNK. 📊
The flow hit Uniswap and bounced across multiple wallets, a classic liquidity sweep that lets whales clean the floor before the dust settles. 🦈⚡
While the breach isn’t independently verified yet, the sheer volume flags a red alert for any $ETH ‑linked exposure. 💬 What defensive moves are you taking to shield your positions?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #Exploit #Crypto
🚀 ⚡
13
A stablecoin nobody has minted since 2023 just drained a lending protocol.
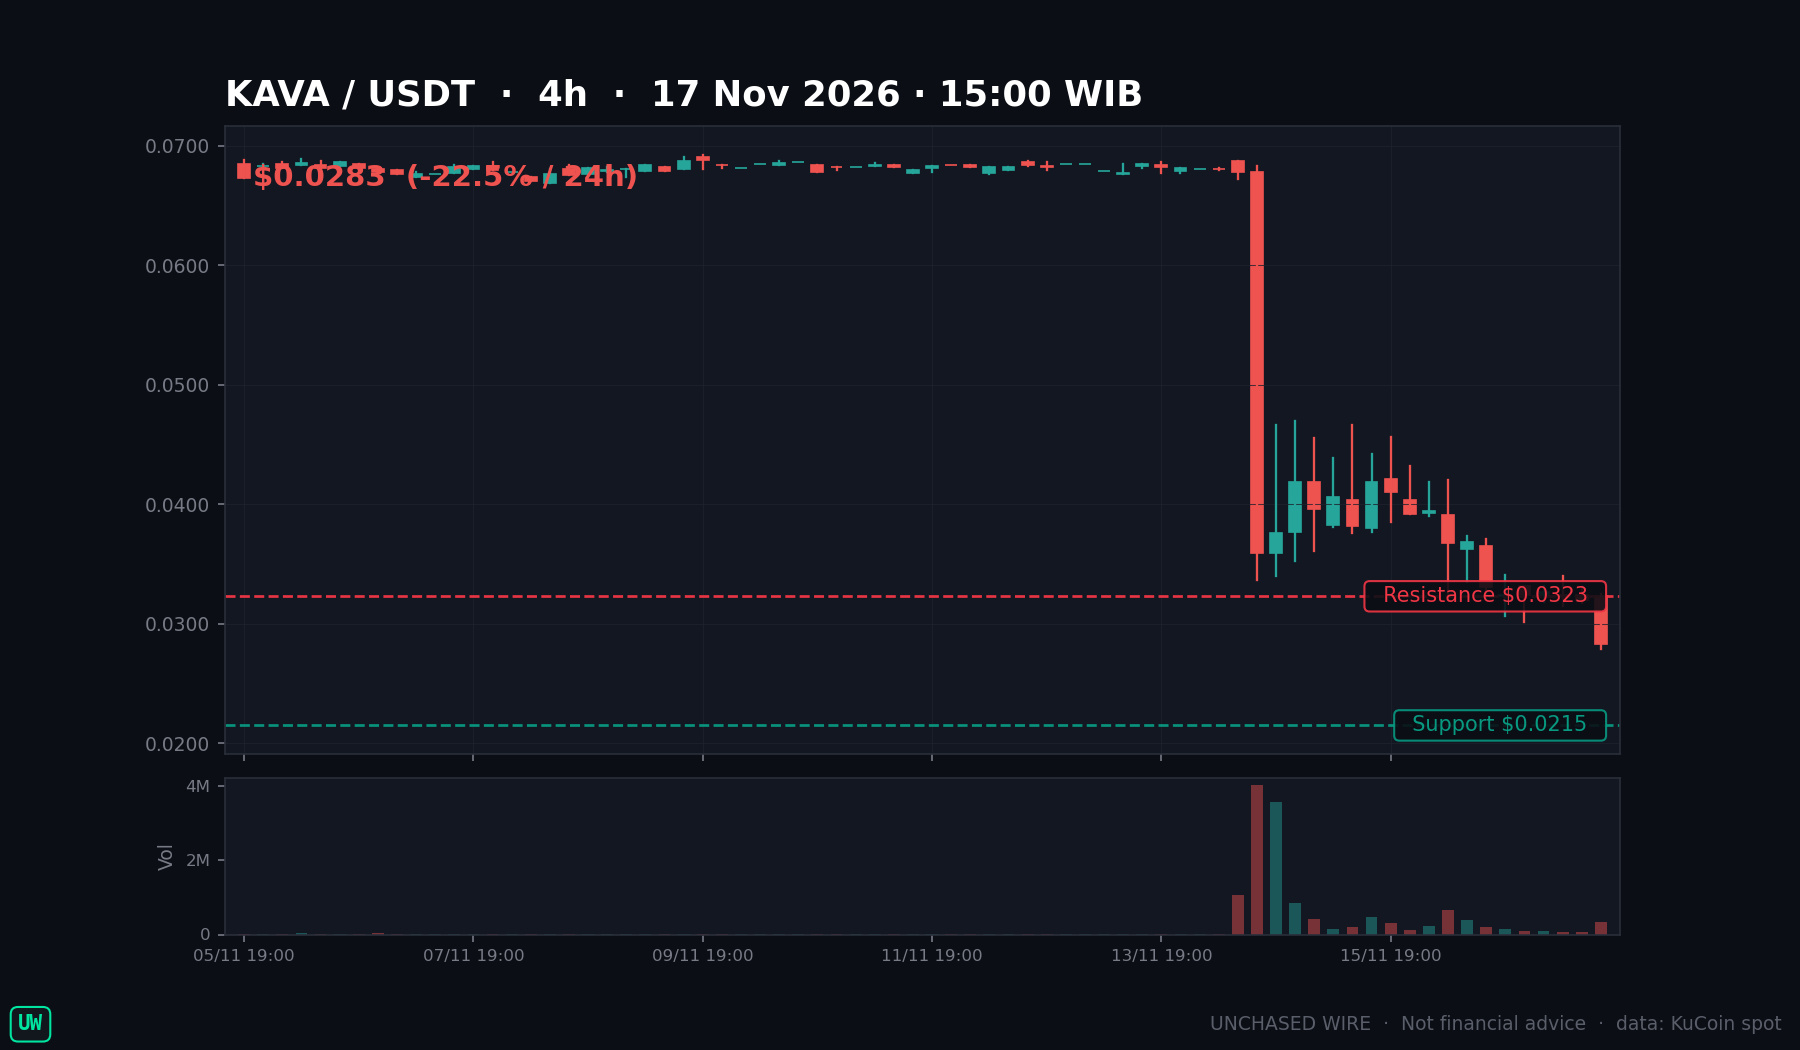
I've watched $KAVA since Friday: Kava Lend lost about 54 million KAVA, roughly $3.8 million, after an attacker pushed a dormant BUSD market's supply to two hundred-millionths of a dollar and borrowed 127 times against the phantom collateral in 98 minutes. Kava confirmed it Monday; a Korean exchange watchlisted the token for delisting, due December 14–18.
The chart is the crime scene: flat near $0.068 for a week, one candle to $0.033, a bounce to $0.047, then a fade to $0.028 — 59% below the pre-attack price.
Support $0.0215. Resistance $0.0323, the ceiling the bounce keeps failing. A 4-hour close under $0.0215 reopens the air below; above $0.0323, the exploit is priced in.
What keeps me uneasy: the stolen coins were bridged and sold within an hour, and a delisting decision hangs over the token until mid-December.
$0.0323 reclaim, or $0.0215 gives way — which print comes first?
NFA, DYOR.
$KAVA $BTC #Kava #DeFi #Exploit #Crypto
A stablecoin nobody has minted since 2023 just drained a lending protocol.
I've watched $KAVA since Friday: Kava Lend lost about 54 million KAVA, roughly $3.8 million, after an attacker pushed a dormant BUSD market's supply to two hundred-millionths of a dollar and borrowed 127 times against the phantom collateral in 98 minutes. Kava confirmed it Monday; a Korean exchange watchlisted the token for delisting, due December 14–18.
The chart is the crime scene: flat near $0.068 for a week, one candle to $0.033, a bounce to $0.047, then a fade to $0.028 — 59% below the pre-attack price.
Support $0.0215. Resistance $0.0323, the ceiling the bounce keeps failing. A 4-hour close under $0.0215 reopens the air below; above $0.0323, the exploit is priced in.
What keeps me uneasy: the stolen coins were bridged and sold within an hour, and a delisting decision hangs over the token until mid-December.
$0.0323 reclaim, or $0.0215 gives way — which print comes first?
NFA, DYOR.
$KAVA $BTC #Kava #DeFi #Exploit #Crypto
I've watched $KAVA since Friday: Kava Lend lost about 54 million KAVA, roughly $3.8 million, after an attacker pushed a dormant BUSD market's supply to two hundred-millionths of a dollar and borrowed 127 times against the phantom collateral in 98 minutes. Kava confirmed it Monday; a Korean exchange watchlisted the token for delisting, due December 14–18.
The chart is the crime scene: flat near $0.068 for a week, one candle to $0.033, a bounce to $0.047, then a fade to $0.028 — 59% below the pre-attack price.
Support $0.0215. Resistance $0.0323, the ceiling the bounce keeps failing. A 4-hour close under $0.0215 reopens the air below; above $0.0323, the exploit is priced in.
What keeps me uneasy: the stolen coins were bridged and sold within an hour, and a delisting decision hangs over the token until mid-December.
$0.0323 reclaim, or $0.0215 gives way — which print comes first?
NFA, DYOR.
$KAVA $BTC #Kava #DeFi #Exploit #Crypto
10
·
--
Sanidul Islam:
okay bro 👍
1
1
186

Another day, another reminder that API key security is the weakest link in crypto trading. Lighter halting withdrawals following a $10.4M exploit highlights how crucial operational hygiene is, even when smart contracts hold up. Tracking stolen funds to destinations like Hyperliquid shows the speed of modern on-chain forensics, but prevention beats recovery every single time. Traders must stay vigilant with permissions. #CryptoSecurity #DeFi #Exploit
Another day, another reminder that API key security is the weakest link in crypto trading. Lighter halting withdrawals following a $10.4M exploit highlights how crucial operational hygiene is, even when smart contracts hold up. Tracking stolen funds to destinations like Hyperliquid shows the speed of modern on-chain forensics, but prevention beats recovery every single time. Traders must stay vigilant with permissions. #CryptoSecurity #DeFi #Exploit
2
Exploit Alert: Kava Lend Drained, $KAVA Crashes ~39%
What happened: An attacker drained about 55.2M $KAVA (~$3.76M at pre-attack prices) from Kava Lend, the chain's native lending protocol, late Friday. The exploit reportedly centered on a dormant BUSD market.
Why the market is pricing it now: Holders are reacting to the drained supply hitting the market and protocol risk. $KAVA fell ~39% in 24H.
Officially confirmed: The incident is visible in on-chain data reviewed by The Block, and Kava's X account addressed it on Nov 14. A full post-mortem has not been seen yet.
What to watch next: post-mortem, fund recovery or bounty talks, and any exchange actions on KAVA deposits/withdrawals.
#KAVA #DeFi #Exploit #CryptoSecurity
Exploit Alert: Kava Lend Drained, $KAVA Crashes ~39%
What happened: An attacker drained about 55.2M $KAVA (~$3.76M at pre-attack prices) from Kava Lend, the chain's native lending protocol, late Friday. The exploit reportedly centered on a dormant BUSD market.
Why the market is pricing it now: Holders are reacting to the drained supply hitting the market and protocol risk. $KAVA fell ~39% in 24H.
Officially confirmed: The incident is visible in on-chain data reviewed by The Block, and Kava's X account addressed it on Nov 14. A full post-mortem has not been seen yet.
What to watch next: post-mortem, fund recovery or bounty talks, and any exchange actions on KAVA deposits/withdrawals.
#KAVA #DeFi #Exploit #CryptoSecurity
What happened: An attacker drained about 55.2M $KAVA (~$3.76M at pre-attack prices) from Kava Lend, the chain's native lending protocol, late Friday. The exploit reportedly centered on a dormant BUSD market.
Why the market is pricing it now: Holders are reacting to the drained supply hitting the market and protocol risk. $KAVA fell ~39% in 24H.
Officially confirmed: The incident is visible in on-chain data reviewed by The Block, and Kava's X account addressed it on Nov 14. A full post-mortem has not been seen yet.
What to watch next: post-mortem, fund recovery or bounty talks, and any exchange actions on KAVA deposits/withdrawals.
#KAVA #DeFi #Exploit #CryptoSecurity
190
·
--
#Kava said it was speeding up $HARD Lend's planned wind-down after the Nov. 14 #exploit and would seek a governance vote to permanently disable new lending and borrowing. In an incident report, the team said it had blocked the exploit and frozen some funds. It put the amount stolen at about 53.9 million KAVA.@kava
#Kava said it was speeding up $HARD Lend's planned wind-down after the Nov. 14 #exploit and would seek a governance vote to permanently disable new lending and borrowing. In an incident report, the team said it had blocked the exploit and frozen some funds. It put the amount stolen at about 53.9 million KAVA.@kava
396
·
--
Article
DOJ moves to seize $1.2 billion from Binance hack, disrupts North Korean deepfake schemeThe DOJ received court approval to seize more than $1.2 billion stolen from Binance and shut down systems used in a separate North Korean scheme involving fake video calls.
The U.S. Department of Justice has obtained court approval to seize or restrain more than $1.2 billion stolen from crypto exchange Binance and disrupted a separate North Korean scheme that used fake video calls to steal crypto.
The Binance funds are part of more than $2.7 billion frozen through efforts by U.S. authorities and private companies, the DOJ said Thursday. Investigators are still tracing stolen assets as the hackers move them through crypto bridges, mixers and exchanges, the department said.
The DOJ attributed the Binance hack to North Korean military hackers known as TraderTraitor. The group stole more than $6 billion from the exchange around Oct. 29, according to the department.
"North Korea's government bankrolls its rogue regime and illicit weapons program through cryptocurrency theft," said Principal Deputy Assistant Attorney General for National Security M. Scott Proctor. "The National Security Division will use every tool at its disposal to seize and return North Korea's ill-gotten gains."
Binance previously put its losses at about $6.3 billion and set aside $6.34 billion in company funds to cover them. Earlier Thursday, Binance said it has completed coverage of assets impacted in the hack and published a new proof of reserves snapshot.
DOJ seizes FaceStealer deepfake video-call infrastructure
Separately, the DOJ said it seized cloud infrastructure used in a North Korean campaign the FBI calls FaceStealer. The scheme has led to more than $400 million in crypto theft over the past 18 months, the department said.
Hackers used stolen accounts to invite victims to video calls, where they played recordings or deepfakes of familiar people. They then faked technical problems and tricked victims into installing malware that could steal crypto or access other systems, the DOJ said.
"It exploits our trust in ubiquitous video conference platforms and valued personal relationships," said Patrick Grandy, assistant director in charge of the FBI's Los Angeles Field Office. "If you can't imagine a scenario where you might fall prey to it, you are not thinking creatively enough."
In some cases, the theft and takeover of communication accounts happened months to more than a year after the computer was first compromised, the department said.
Hackers also used stolen contacts and accounts to target more people, including open-source software developers, potentially to carry out attacks through their software. The FBI seized more than 900 webcam videos of FaceStealer victims and issued guidance for those affected, the DOJ said.
#exploit #Binance
DOJ moves to seize $1.2 billion from Binance hack, disrupts North Korean deepfake scheme
The DOJ received court approval to seize more than $1.2 billion stolen from Binance and shut down systems used in a separate North Korean scheme involving fake video calls.
The U.S. Department of Justice has obtained court approval to seize or restrain more than $1.2 billion stolen from crypto exchange Binance and disrupted a separate North Korean scheme that used fake video calls to steal crypto.
The Binance funds are part of more than $2.7 billion frozen through efforts by U.S. authorities and private companies, the DOJ said Thursday. Investigators are still tracing stolen assets as the hackers move them through crypto bridges, mixers and exchanges, the department said.
The DOJ attributed the Binance hack to North Korean military hackers known as TraderTraitor. The group stole more than $6 billion from the exchange around Oct. 29, according to the department.
"North Korea's government bankrolls its rogue regime and illicit weapons program through cryptocurrency theft," said Principal Deputy Assistant Attorney General for National Security M. Scott Proctor. "The National Security Division will use every tool at its disposal to seize and return North Korea's ill-gotten gains."
Binance previously put its losses at about $6.3 billion and set aside $6.34 billion in company funds to cover them. Earlier Thursday, Binance said it has completed coverage of assets impacted in the hack and published a new proof of reserves snapshot.
DOJ seizes FaceStealer deepfake video-call infrastructure
Separately, the DOJ said it seized cloud infrastructure used in a North Korean campaign the FBI calls FaceStealer. The scheme has led to more than $400 million in crypto theft over the past 18 months, the department said.
Hackers used stolen accounts to invite victims to video calls, where they played recordings or deepfakes of familiar people. They then faked technical problems and tricked victims into installing malware that could steal crypto or access other systems, the DOJ said.
"It exploits our trust in ubiquitous video conference platforms and valued personal relationships," said Patrick Grandy, assistant director in charge of the FBI's Los Angeles Field Office. "If you can't imagine a scenario where you might fall prey to it, you are not thinking creatively enough."
In some cases, the theft and takeover of communication accounts happened months to more than a year after the computer was first compromised, the department said.
Hackers also used stolen contacts and accounts to target more people, including open-source software developers, potentially to carry out attacks through their software. The FBI seized more than 900 webcam videos of FaceStealer victims and issued guidance for those affected, the DOJ said.
#exploit #Binance
The U.S. Department of Justice has obtained court approval to seize or restrain more than $1.2 billion stolen from crypto exchange Binance and disrupted a separate North Korean scheme that used fake video calls to steal crypto.
The Binance funds are part of more than $2.7 billion frozen through efforts by U.S. authorities and private companies, the DOJ said Thursday. Investigators are still tracing stolen assets as the hackers move them through crypto bridges, mixers and exchanges, the department said.
The DOJ attributed the Binance hack to North Korean military hackers known as TraderTraitor. The group stole more than $6 billion from the exchange around Oct. 29, according to the department.
"North Korea's government bankrolls its rogue regime and illicit weapons program through cryptocurrency theft," said Principal Deputy Assistant Attorney General for National Security M. Scott Proctor. "The National Security Division will use every tool at its disposal to seize and return North Korea's ill-gotten gains."
Binance previously put its losses at about $6.3 billion and set aside $6.34 billion in company funds to cover them. Earlier Thursday, Binance said it has completed coverage of assets impacted in the hack and published a new proof of reserves snapshot.
DOJ seizes FaceStealer deepfake video-call infrastructure
Separately, the DOJ said it seized cloud infrastructure used in a North Korean campaign the FBI calls FaceStealer. The scheme has led to more than $400 million in crypto theft over the past 18 months, the department said.
Hackers used stolen accounts to invite victims to video calls, where they played recordings or deepfakes of familiar people. They then faked technical problems and tricked victims into installing malware that could steal crypto or access other systems, the DOJ said.
"It exploits our trust in ubiquitous video conference platforms and valued personal relationships," said Patrick Grandy, assistant director in charge of the FBI's Los Angeles Field Office. "If you can't imagine a scenario where you might fall prey to it, you are not thinking creatively enough."
In some cases, the theft and takeover of communication accounts happened months to more than a year after the computer was first compromised, the department said.
Hackers also used stolen contacts and accounts to target more people, including open-source software developers, potentially to carry out attacks through their software. The FBI seized more than 900 webcam videos of FaceStealer victims and issued guidance for those affected, the DOJ said.
#exploit #Binance
66
I'm noticing something unusual with $INIT: its chain has been halted since Tuesday — and the token doubled anyway.
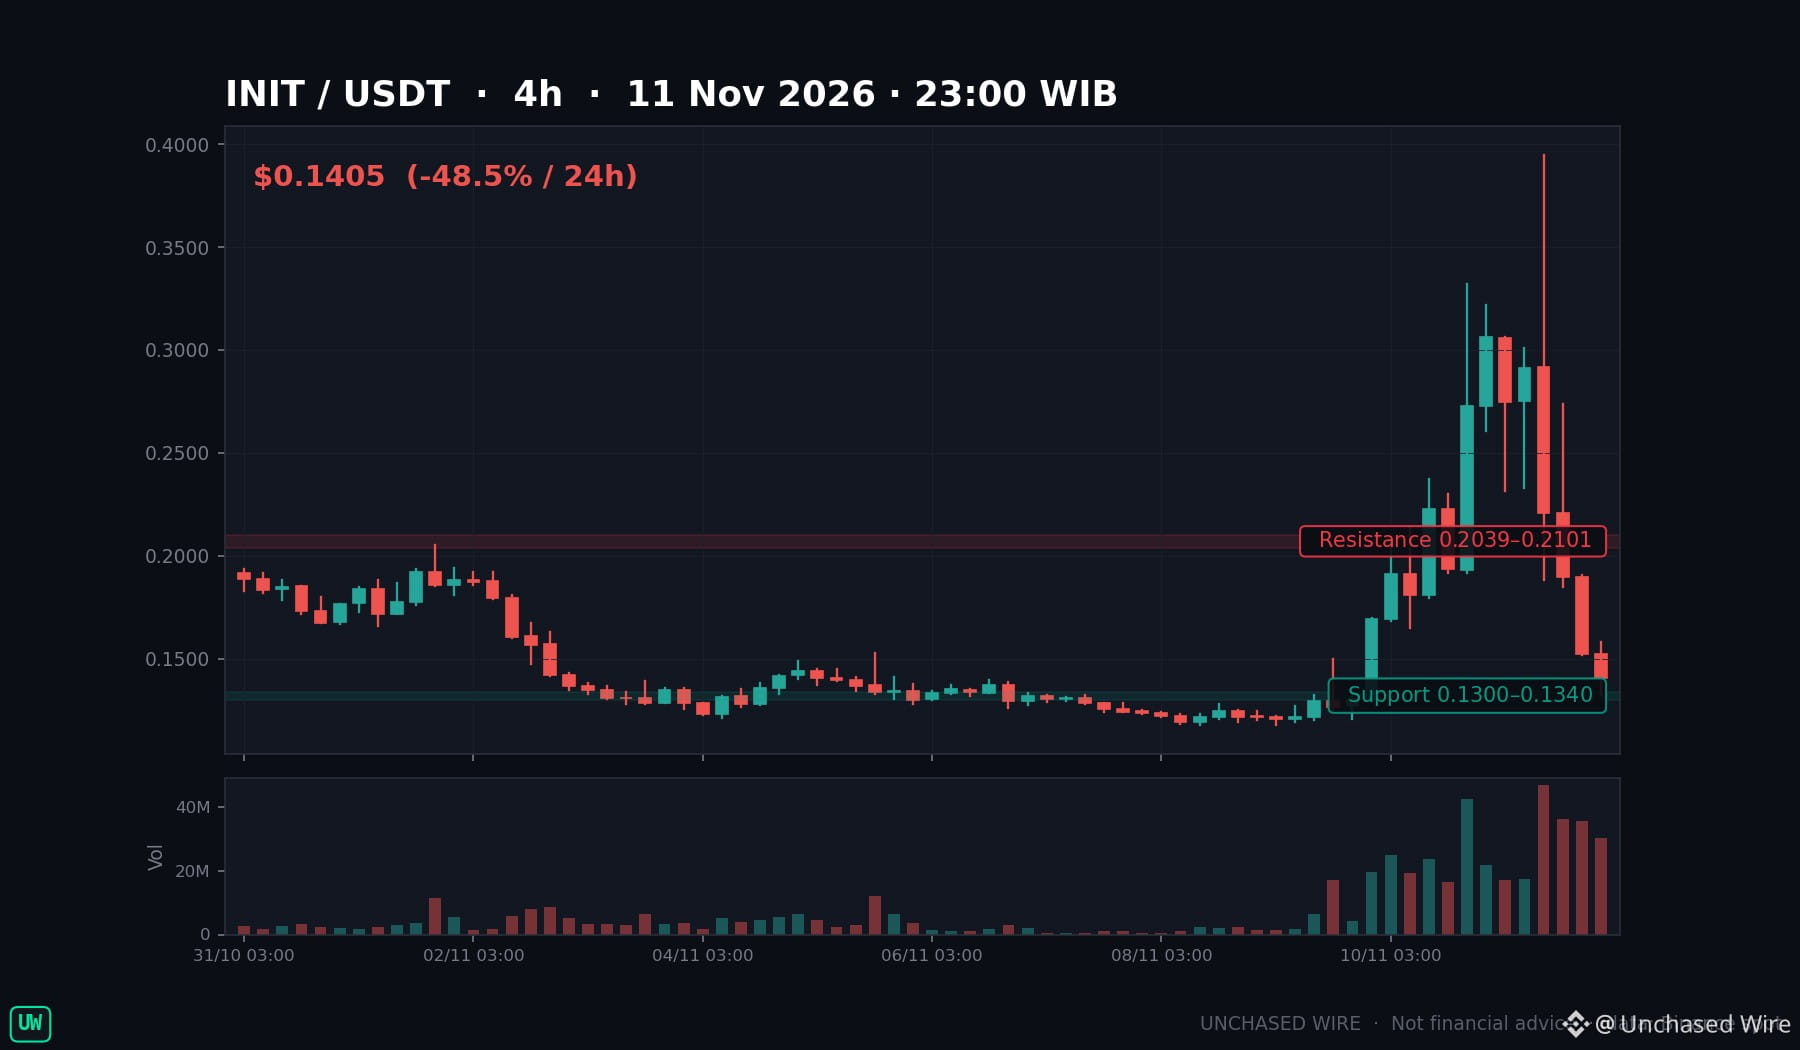
Round trip, in receipts. November 8 close: $0.12. November 10, hours after the halt: $0.27 close, $0.33 high. November 11: a $0.395 spike, then a close at $0.14 — the whole pump, gone in a day.
This is the second halt in three weeks. The October 23 exploit took about $2.7 million. This one moved about $3.27 million through forged withdrawals, with $2.16 million stuck on the paused chain. No restart date has been set.
Spot volume ran $42 million in 24 hours — more than the token's $31 million market cap. Until the chain restarts, the price trades on contracts, not a working network.
My lines: support $0.132, then $0.12. Resistance $0.207, then $0.275. A daily close under $0.12 breaks the pre-pump base; above $0.207, the pump story gets a second hearing.
Caught at the top near $0.39, riding it up from $0.12, or watching from the sidelines until the chain restarts — which one are you?
NFA, DYOR.
$INIT #Initia #CryptoNews #Exploit
I'm noticing something unusual with $INIT : its chain has been halted since Tuesday — and the token doubled anyway.
Round trip, in receipts. November 8 close: $0.12. November 10, hours after the halt: $0.27 close, $0.33 high. November 11: a $0.395 spike, then a close at $0.14 — the whole pump, gone in a day.
This is the second halt in three weeks. The October 23 exploit took about $2.7 million. This one moved about $3.27 million through forged withdrawals, with $2.16 million stuck on the paused chain. No restart date has been set.
Spot volume ran $42 million in 24 hours — more than the token's $31 million market cap. Until the chain restarts, the price trades on contracts, not a working network.
My lines: support $0.132, then $0.12. Resistance $0.207, then $0.275. A daily close under $0.12 breaks the pre-pump base; above $0.207, the pump story gets a second hearing.
Caught at the top near $0.39, riding it up from $0.12, or watching from the sidelines until the chain restarts — which one are you?
NFA, DYOR.
$INIT #Initia #CryptoNews #Exploit
Round trip, in receipts. November 8 close: $0.12. November 10, hours after the halt: $0.27 close, $0.33 high. November 11: a $0.395 spike, then a close at $0.14 — the whole pump, gone in a day.
This is the second halt in three weeks. The October 23 exploit took about $2.7 million. This one moved about $3.27 million through forged withdrawals, with $2.16 million stuck on the paused chain. No restart date has been set.
Spot volume ran $42 million in 24 hours — more than the token's $31 million market cap. Until the chain restarts, the price trades on contracts, not a working network.
My lines: support $0.132, then $0.12. Resistance $0.207, then $0.275. A daily close under $0.12 breaks the pre-pump base; above $0.207, the pump story gets a second hearing.
Caught at the top near $0.39, riding it up from $0.12, or watching from the sidelines until the chain restarts — which one are you?
NFA, DYOR.
$INIT #Initia #CryptoNews #Exploit
9

·
--
🚨 $SAND BLOWOUT: OVER 500 MILLION TOKENS ILLEGALLY MINTED IN CRITICAL EXPLOIT! 🩸
Smart contract exploit on Base allowed an attacker address to trigger an infinite mint, flooding supply with over 500M illegally created $SAND tokens. 🚨 Panic selling hit instantly, knocking price down by double digits as the market digested the massive dilution threat.
🔍 This vulnerability exposes severe risk vectors during multi-chain expansions when core minting rights are compromised. 💡 Smart money is stepping back to watch whether team response can contain the fallout or if contract permissions are permanently broken.
💬 Are you holding through the chaos or dumping your exposure until security audits confirm a fix? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAND #Exploit #CryptoSecurity #DeFi
🚨 📉
🚨 $SAND BLOWOUT: OVER 500 MILLION TOKENS ILLEGALLY MINTED IN CRITICAL EXPLOIT! 🩸
Smart contract exploit on Base allowed an attacker address to trigger an infinite mint, flooding supply with over 500M illegally created $SAND tokens. 🚨 Panic selling hit instantly, knocking price down by double digits as the market digested the massive dilution threat.
🔍 This vulnerability exposes severe risk vectors during multi-chain expansions when core minting rights are compromised. 💡 Smart money is stepping back to watch whether team response can contain the fallout or if contract permissions are permanently broken.
💬 Are you holding through the chaos or dumping your exposure until security audits confirm a fix? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAND #Exploit #CryptoSecurity #DeFi
🚨 📉
Smart contract exploit on Base allowed an attacker address to trigger an infinite mint, flooding supply with over 500M illegally created $SAND tokens. 🚨 Panic selling hit instantly, knocking price down by double digits as the market digested the massive dilution threat.
🔍 This vulnerability exposes severe risk vectors during multi-chain expansions when core minting rights are compromised. 💡 Smart money is stepping back to watch whether team response can contain the fallout or if contract permissions are permanently broken.
💬 Are you holding through the chaos or dumping your exposure until security audits confirm a fix? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAND #Exploit #CryptoSecurity #DeFi
🚨 📉
15
𝙏𝙃𝙀 𝘽𝙄𝙂𝙂𝙀𝙎𝙏 𝙃𝙀𝙄𝙎𝙏 𝙄𝙉 𝙏𝙃𝙀 𝙃𝙄𝙎𝙏𝙊𝙍𝙔 𝙊𝙁 𝘽𝙄𝙉𝘼𝙉𝘾𝙀 💥🦈
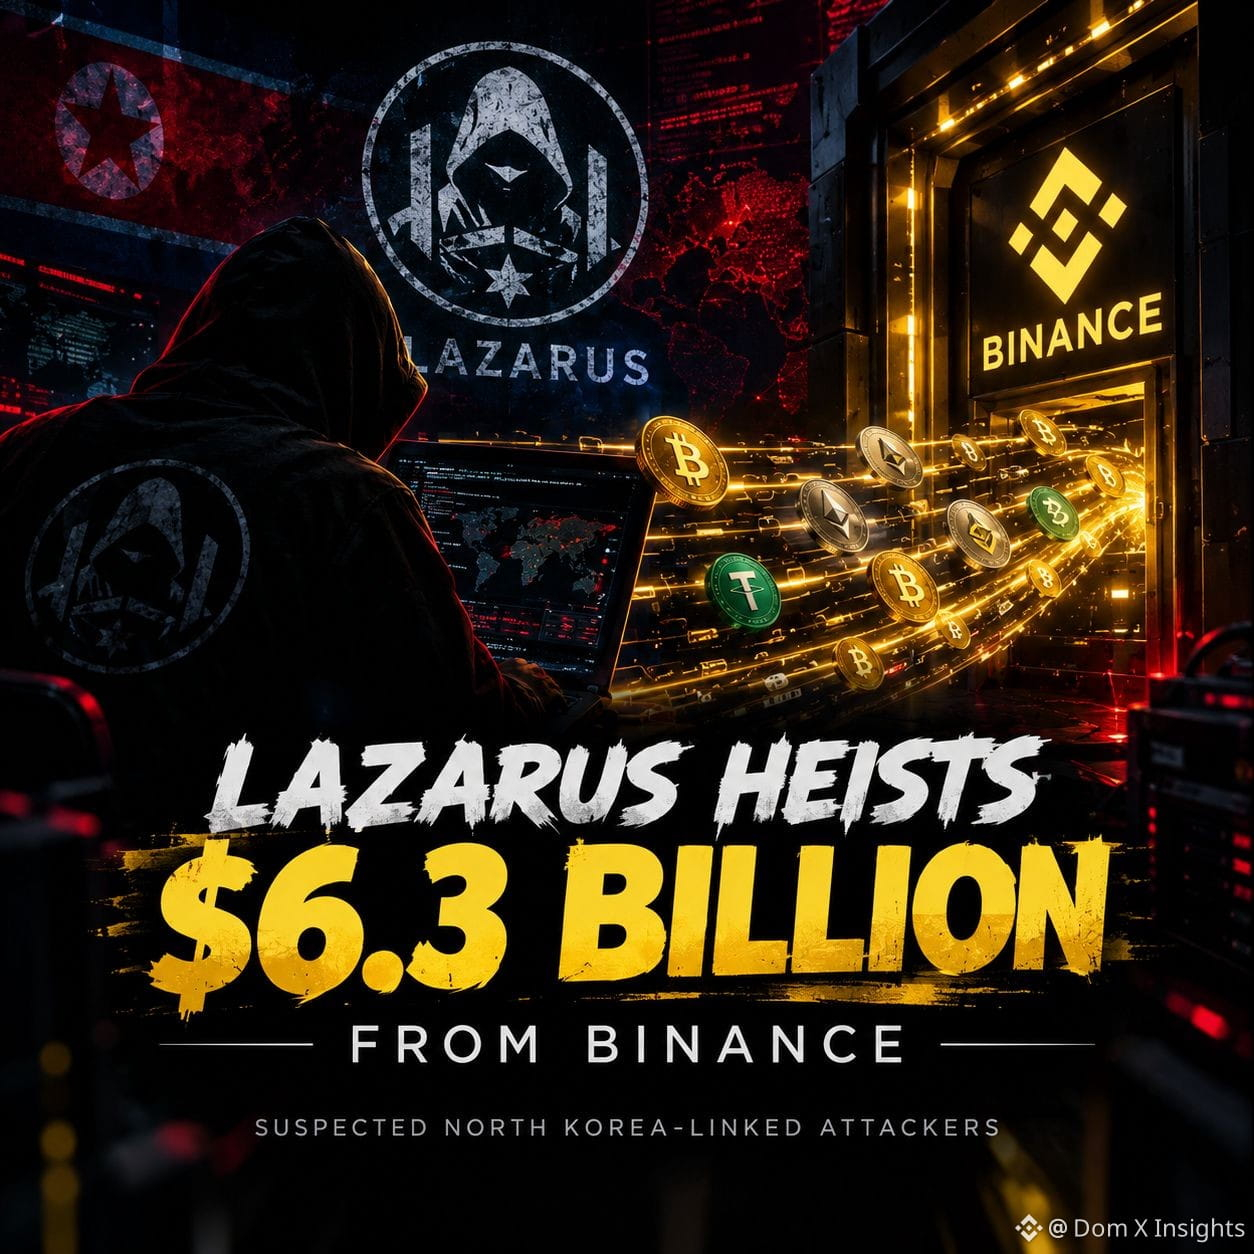
The crypto industry was shaken to its core when North Korea’s state-backed Lazarus Group pulled off a $6.3 billion breach against Binance, marking the largest cryptocurrency heist in history.
What began as a quiet intrusion escalated into a high-stakes, 20-minute operational nightmare. Armed with access gained through a compromised Binance DevOps engineer's device, the attackers targeted transaction-signing infrastructure across 10 blockchains to initiate rapid withdrawals.
Before security teams could fully react, billions vanished from hot wallets into non-custodial networks. The response from the broader crypto ecosystem was immediate: major stablecoin issuers Tether and Circle, along with chain security partners, raced to freeze nearly $3 billion of the stolen assets directly on-chain. However, over $2.4 billion in Bitcoin and Ethereum remains under the attacker's control and is actively moving through mixers like Tornado Cash.
To mitigate market panic, Binance leadership halted global withdrawals and committed to covering 100% of affected user funds using its SAFU emergency reserve, reassuring traders that internal systems and balances are being fully secured.
#exploit #Binance #TwoAddressesHoldingAbout1.28BUSDTFrozen
#HackerAlert
𝙏𝙃𝙀 𝘽𝙄𝙂𝙂𝙀𝙎𝙏 𝙃𝙀𝙄𝙎𝙏 𝙄𝙉 𝙏𝙃𝙀 𝙃𝙄𝙎𝙏𝙊𝙍𝙔 𝙊𝙁 𝘽𝙄𝙉𝘼𝙉𝘾𝙀 💥🦈
The crypto industry was shaken to its core when North Korea’s state-backed Lazarus Group pulled off a $6.3 billion breach against Binance, marking the largest cryptocurrency heist in history.
What began as a quiet intrusion escalated into a high-stakes, 20-minute operational nightmare. Armed with access gained through a compromised Binance DevOps engineer's device, the attackers targeted transaction-signing infrastructure across 10 blockchains to initiate rapid withdrawals.
Before security teams could fully react, billions vanished from hot wallets into non-custodial networks. The response from the broader crypto ecosystem was immediate: major stablecoin issuers Tether and Circle, along with chain security partners, raced to freeze nearly $3 billion of the stolen assets directly on-chain. However, over $2.4 billion in Bitcoin and Ethereum remains under the attacker's control and is actively moving through mixers like Tornado Cash.
To mitigate market panic, Binance leadership halted global withdrawals and committed to covering 100% of affected user funds using its SAFU emergency reserve, reassuring traders that internal systems and balances are being fully secured.
#exploit #Binance #TwoAddressesHoldingAbout1.28BUSDTFrozen
#HackerAlert
The crypto industry was shaken to its core when North Korea’s state-backed Lazarus Group pulled off a $6.3 billion breach against Binance, marking the largest cryptocurrency heist in history.
What began as a quiet intrusion escalated into a high-stakes, 20-minute operational nightmare. Armed with access gained through a compromised Binance DevOps engineer's device, the attackers targeted transaction-signing infrastructure across 10 blockchains to initiate rapid withdrawals.
Before security teams could fully react, billions vanished from hot wallets into non-custodial networks. The response from the broader crypto ecosystem was immediate: major stablecoin issuers Tether and Circle, along with chain security partners, raced to freeze nearly $3 billion of the stolen assets directly on-chain. However, over $2.4 billion in Bitcoin and Ethereum remains under the attacker's control and is actively moving through mixers like Tornado Cash.
To mitigate market panic, Binance leadership halted global withdrawals and committed to covering 100% of affected user funds using its SAFU emergency reserve, reassuring traders that internal systems and balances are being fully secured.
#exploit #Binance #TwoAddressesHoldingAbout1.28BUSDTFrozen
#HackerAlert
5
3
736
·
--
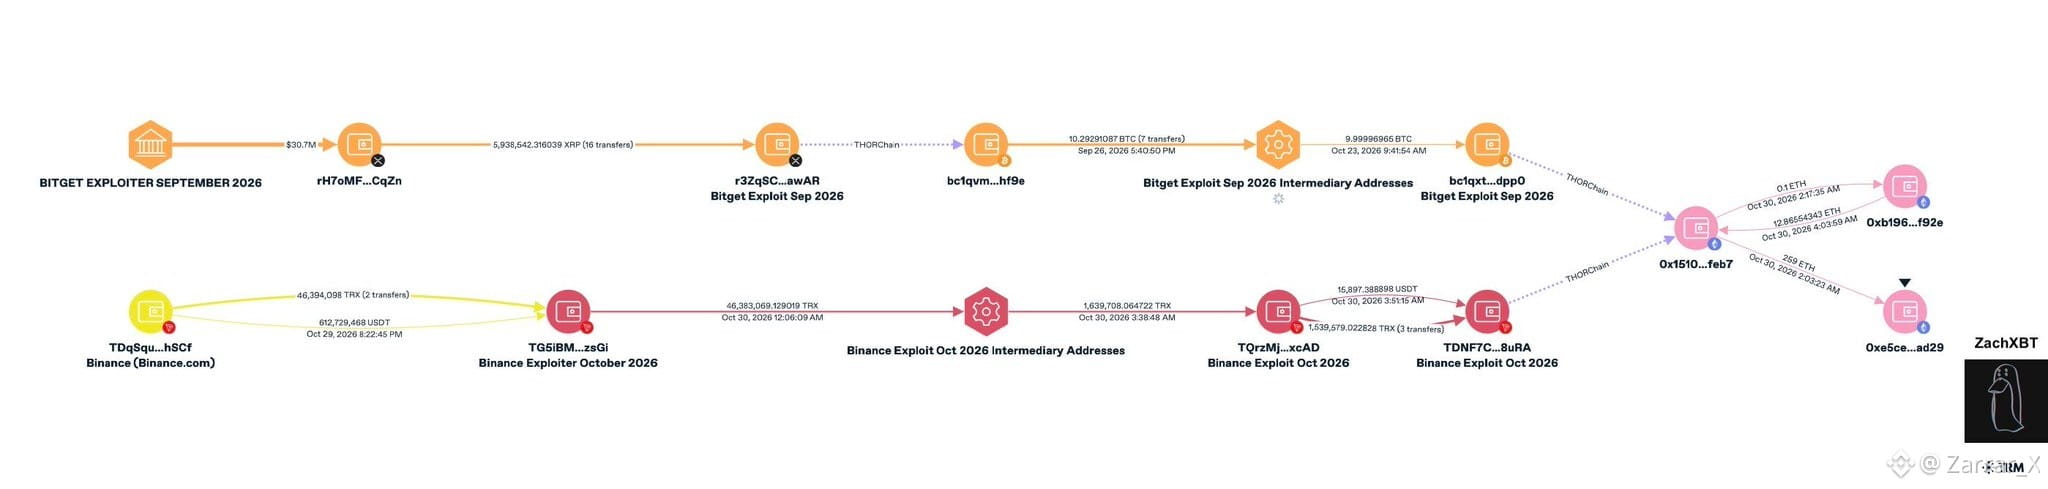
🚨 ZachXBT Links TraderTraitor to $6.3B Binance Hack.
Blockchain investigator ZachXBT says North Korea-linked hacking group TraderTraitor, previously associated with the $388 million Bitget exploit, may also be behind the reported $6.3 billion Binance hack.
The key connection is that funds stolen in both incidents reportedly ended up at the same blockchain address, raising suspicions of a shared attacker or laundering network.
If the attribution is confirmed, it would point to a much broader operation involving North Korean-linked cybercrime. However, a shared destination address alone does not conclusively establish that the same group carried out both attacks.
$LINK #exploit
{spot}(LINKUSDT)
🚨 ZachXBT Links TraderTraitor to $6.3B Binance Hack.
Blockchain investigator ZachXBT says North Korea-linked hacking group TraderTraitor, previously associated with the $388 million Bitget exploit, may also be behind the reported $6.3 billion Binance hack.
The key connection is that funds stolen in both incidents reportedly ended up at the same blockchain address, raising suspicions of a shared attacker or laundering network.
If the attribution is confirmed, it would point to a much broader operation involving North Korean-linked cybercrime. However, a shared destination address alone does not conclusively establish that the same group carried out both attacks.
$LINK #exploit
Blockchain investigator ZachXBT says North Korea-linked hacking group TraderTraitor, previously associated with the $388 million Bitget exploit, may also be behind the reported $6.3 billion Binance hack.
The key connection is that funds stolen in both incidents reportedly ended up at the same blockchain address, raising suspicions of a shared attacker or laundering network.
If the attribution is confirmed, it would point to a much broader operation involving North Korean-linked cybercrime. However, a shared destination address alone does not conclusively establish that the same group carried out both attacks.
$LINK #exploit
127
Governance, bought in a single transaction — that is what happened to X100 on Saturday evening, and I keep coming back to how little stood in the attackers' way.
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
Governance, bought in a single transaction — that is what happened to X100 on Saturday evening, and I keep coming back to how little stood in the attackers' way.
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
5
·
--

Article
Let Me Calm You Down About $GUA: Why Yesterday's 75% Drop Is a Hidden Gem and a Gift for Buyers!Yesterday, the community held its breath as they watched the SUPERFORTUNE (GUA) token cascade down to an extreme bottom around $0.2630. Many panicked, but those who know how to read charts and analyze on-chain data understood: this was a classic force majeure that opened up the perfect entry point.
- Right now, the price has already bounced back above $0.61, confidently securing its position above key moving averages! Let's break down why this project is fundamentally strong and why the panic is officially over.
👇🚨 Incident Breakdown: What Actually Happened?
- The brutal sell-off was not caused by a team rug pull or a vulnerability in the app's smart contract. It was a simple human error (an exploit during a multisig transaction): the project accidentally sent an airdrop to an address that was hijacked by a hacker.
- The attacker had no intention of holding the asset and immediately market-dumped all the tokens straight into the order book. The result: the hacker completely emptied their wallets, the panic selling pressure vanished, and diamond hands alongside market makers instantly started scooping up the token back. The main product remains completely secure!
🧠 Fundamentals: Why SUPERFORTUNE Is an InfoFi Giant.
The project operates in a highly lucrative and wildly popular niche at the intersection of Web3, AI, and Chinese metaphysics (AI-powered astrology and Feng Shui forecasts).
- Market Potential: In Asia, this market is valued at over $390 billion! The app already boasts a massive active user base.
- Powerful Incubation: The project was launched and is fully backed by the Manta Labs team (creators of Manta Network). They provide substantial budgets, liquidity, and top-tier crypto industry connections.
🗺️ Roadmap & Tight Tokenomics: Only Growth Ahead.
Many were worried about sell pressure, but let’s look at the facts:
1. Dump Protection: The global token unlock for the team and major investors is locked until the end of May 2027! The current circulating supply is strictly controlled.
2. Super App & Deflation: The team is preparing for the full launch of their mobile Super App with Apple Pay integration. A portion of the GUA tokens spent inside for AI reports will be permanently burned.
3. Tier-1 Listings: Given the direct connection to Manta, the project is actively preparing to launch on major first-tier exchanges, including Binance and Bybit.
📈 Technical Analysis: The Bottom Is In.
Take a look at the 15-minute chart right now:
- The price has confidently broken above MA(7) [$0.5732] and MA(30) [$0.4031] from the bottom up.
- The $0.2633 level is protected by a thick wall of buyers.
- The YTD (Year-to-Date) return sits at +401%, confirming its status as one of the strongest AI assets on the BNB Chain.
Conclusion: The panic surrounding the transaction mistake has been completely neutralized. The project has proven its resilience. Such sudden drops in strong projects are always an opportunity you shouldn't miss. Let's watch the development and wait for the march toward $1.00! 🚀
#gua #SUPERFORTUNE #exploit
$GUA
{future}(GUAUSDT)
$BTC
{future}(BTCUSDT)
$BNB
{future}(BNBUSDT)
Let Me Calm You Down About $GUA: Why Yesterday's 75% Drop Is a Hidden Gem and a Gift for Buyers!
Yesterday, the community held its breath as they watched the SUPERFORTUNE (GUA) token cascade down to an extreme bottom around $0.2630. Many panicked, but those who know how to read charts and analyze on-chain data understood: this was a classic force majeure that opened up the perfect entry point.
- Right now, the price has already bounced back above $0.61, confidently securing its position above key moving averages! Let's break down why this project is fundamentally strong and why the panic is officially over.
👇🚨 Incident Breakdown: What Actually Happened?
- The brutal sell-off was not caused by a team rug pull or a vulnerability in the app's smart contract. It was a simple human error (an exploit during a multisig transaction): the project accidentally sent an airdrop to an address that was hijacked by a hacker.
- The attacker had no intention of holding the asset and immediately market-dumped all the tokens straight into the order book. The result: the hacker completely emptied their wallets, the panic selling pressure vanished, and diamond hands alongside market makers instantly started scooping up the token back. The main product remains completely secure!
🧠 Fundamentals: Why SUPERFORTUNE Is an InfoFi Giant.
The project operates in a highly lucrative and wildly popular niche at the intersection of Web3, AI, and Chinese metaphysics (AI-powered astrology and Feng Shui forecasts).
- Market Potential: In Asia, this market is valued at over $390 billion! The app already boasts a massive active user base.
- Powerful Incubation: The project was launched and is fully backed by the Manta Labs team (creators of Manta Network). They provide substantial budgets, liquidity, and top-tier crypto industry connections.
🗺️ Roadmap & Tight Tokenomics: Only Growth Ahead.
Many were worried about sell pressure, but let’s look at the facts:
1. Dump Protection: The global token unlock for the team and major investors is locked until the end of May 2027! The current circulating supply is strictly controlled.
2. Super App & Deflation: The team is preparing for the full launch of their mobile Super App with Apple Pay integration. A portion of the GUA tokens spent inside for AI reports will be permanently burned.
3. Tier-1 Listings: Given the direct connection to Manta, the project is actively preparing to launch on major first-tier exchanges, including Binance and Bybit.
📈 Technical Analysis: The Bottom Is In.
Take a look at the 15-minute chart right now:
- The price has confidently broken above MA(7) [$0.5732] and MA(30) [$0.4031] from the bottom up.
- The $0.2633 level is protected by a thick wall of buyers.
- The YTD (Year-to-Date) return sits at +401%, confirming its status as one of the strongest AI assets on the BNB Chain.
Conclusion: The panic surrounding the transaction mistake has been completely neutralized. The project has proven its resilience. Such sudden drops in strong projects are always an opportunity you shouldn't miss. Let's watch the development and wait for the march toward $1.00! 🚀
#gua #SUPERFORTUNE #exploit
$GUA
$BTC
$BNB
- Right now, the price has already bounced back above $0.61, confidently securing its position above key moving averages! Let's break down why this project is fundamentally strong and why the panic is officially over.
👇🚨 Incident Breakdown: What Actually Happened?
- The brutal sell-off was not caused by a team rug pull or a vulnerability in the app's smart contract. It was a simple human error (an exploit during a multisig transaction): the project accidentally sent an airdrop to an address that was hijacked by a hacker.
- The attacker had no intention of holding the asset and immediately market-dumped all the tokens straight into the order book. The result: the hacker completely emptied their wallets, the panic selling pressure vanished, and diamond hands alongside market makers instantly started scooping up the token back. The main product remains completely secure!
🧠 Fundamentals: Why SUPERFORTUNE Is an InfoFi Giant.
The project operates in a highly lucrative and wildly popular niche at the intersection of Web3, AI, and Chinese metaphysics (AI-powered astrology and Feng Shui forecasts).
- Market Potential: In Asia, this market is valued at over $390 billion! The app already boasts a massive active user base.
- Powerful Incubation: The project was launched and is fully backed by the Manta Labs team (creators of Manta Network). They provide substantial budgets, liquidity, and top-tier crypto industry connections.
🗺️ Roadmap & Tight Tokenomics: Only Growth Ahead.
Many were worried about sell pressure, but let’s look at the facts:
1. Dump Protection: The global token unlock for the team and major investors is locked until the end of May 2027! The current circulating supply is strictly controlled.
2. Super App & Deflation: The team is preparing for the full launch of their mobile Super App with Apple Pay integration. A portion of the GUA tokens spent inside for AI reports will be permanently burned.
3. Tier-1 Listings: Given the direct connection to Manta, the project is actively preparing to launch on major first-tier exchanges, including Binance and Bybit.
📈 Technical Analysis: The Bottom Is In.
Take a look at the 15-minute chart right now:
- The price has confidently broken above MA(7) [$0.5732] and MA(30) [$0.4031] from the bottom up.
- The $0.2633 level is protected by a thick wall of buyers.
- The YTD (Year-to-Date) return sits at +401%, confirming its status as one of the strongest AI assets on the BNB Chain.
Conclusion: The panic surrounding the transaction mistake has been completely neutralized. The project has proven its resilience. Such sudden drops in strong projects are always an opportunity you shouldn't miss. Let's watch the development and wait for the march toward $1.00! 🚀
#gua #SUPERFORTUNE #exploit
$GUA
$BTC
$BNB
2
507
·
--
Thetanuts Finance was exploited on June 15 after an attacker targeted a legacy Ethereum vault and drained assets valued at about $2.1 million.
According to Blockaid, ExVul, and PeckShield, the attack exploited a low-supply accounting flaw in the vault's minting and redemption calculations. The attacker used flash-loaned capital to reduce token supply to an extremely low level, then reminted tokens at a discounted rate due to rounding behavior in the contract logic.
ExVul's analysis found that the vault's redemption formula became vulnerable when the total supply approached near-zero levels. This allowed the attacker to generate inflated redemption values and repeatedly execute mint-and-claim transactions that withdrew more assets than were deposited.
Initial estimates placed losses near $105,500 in USDC. A later analysis by PeckShield reported a total impact of $2.1 million.
PeckShield also stated that about $2 million worth of option tokens were secured by whitehat actors. The attacker converted about $105,000 in USDC into ETH and continued to hold additional assets linked to the exploit.
Thetanuts Finance said the affected vault was a deprecated product that had been migrated years ago and was not connected to any current contracts or active products. The team plans to release a full post-mortem after completing its investigation.
The incident serves as another reminder that legacy DeFi infrastructure can remain vulnerable even after protocols migrate users to newer systems.
#exploit #SecurityAlert #Thetanuts #CryptoNews #CryptocurrencyNews
Thetanuts Finance was exploited on June 15 after an attacker targeted a legacy Ethereum vault and drained assets valued at about $2.1 million.
According to Blockaid, ExVul, and PeckShield, the attack exploited a low-supply accounting flaw in the vault's minting and redemption calculations. The attacker used flash-loaned capital to reduce token supply to an extremely low level, then reminted tokens at a discounted rate due to rounding behavior in the contract logic.
ExVul's analysis found that the vault's redemption formula became vulnerable when the total supply approached near-zero levels. This allowed the attacker to generate inflated redemption values and repeatedly execute mint-and-claim transactions that withdrew more assets than were deposited.
Initial estimates placed losses near $105,500 in USDC. A later analysis by PeckShield reported a total impact of $2.1 million.
PeckShield also stated that about $2 million worth of option tokens were secured by whitehat actors. The attacker converted about $105,000 in USDC into ETH and continued to hold additional assets linked to the exploit.
Thetanuts Finance said the affected vault was a deprecated product that had been migrated years ago and was not connected to any current contracts or active products. The team plans to release a full post-mortem after completing its investigation.
The incident serves as another reminder that legacy DeFi infrastructure can remain vulnerable even after protocols migrate users to newer systems.
#exploit #SecurityAlert #Thetanuts #CryptoNews #CryptocurrencyNews
According to Blockaid, ExVul, and PeckShield, the attack exploited a low-supply accounting flaw in the vault's minting and redemption calculations. The attacker used flash-loaned capital to reduce token supply to an extremely low level, then reminted tokens at a discounted rate due to rounding behavior in the contract logic.
ExVul's analysis found that the vault's redemption formula became vulnerable when the total supply approached near-zero levels. This allowed the attacker to generate inflated redemption values and repeatedly execute mint-and-claim transactions that withdrew more assets than were deposited.
Initial estimates placed losses near $105,500 in USDC. A later analysis by PeckShield reported a total impact of $2.1 million.
PeckShield also stated that about $2 million worth of option tokens were secured by whitehat actors. The attacker converted about $105,000 in USDC into ETH and continued to hold additional assets linked to the exploit.
Thetanuts Finance said the affected vault was a deprecated product that had been migrated years ago and was not connected to any current contracts or active products. The team plans to release a full post-mortem after completing its investigation.
The incident serves as another reminder that legacy DeFi infrastructure can remain vulnerable even after protocols migrate users to newer systems.
#exploit #SecurityAlert #Thetanuts #CryptoNews #CryptocurrencyNews
99

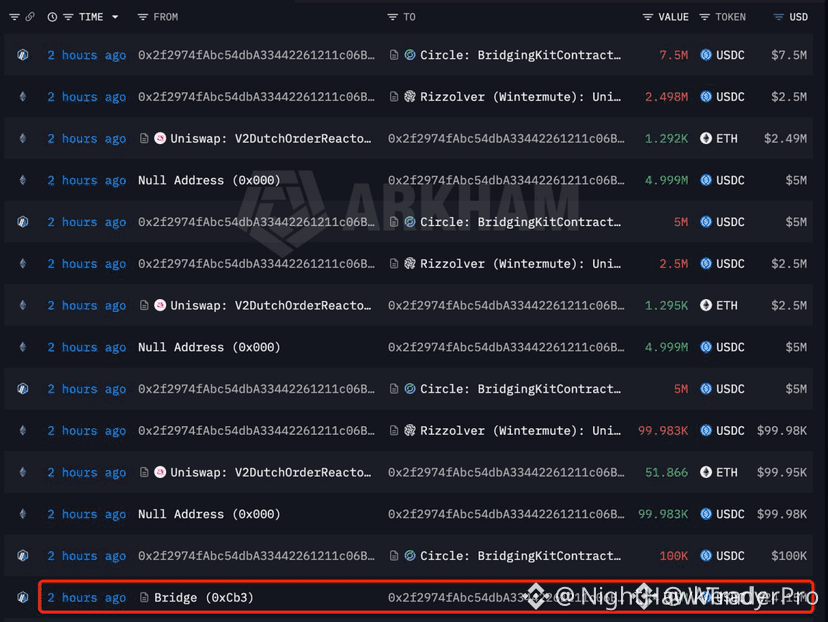
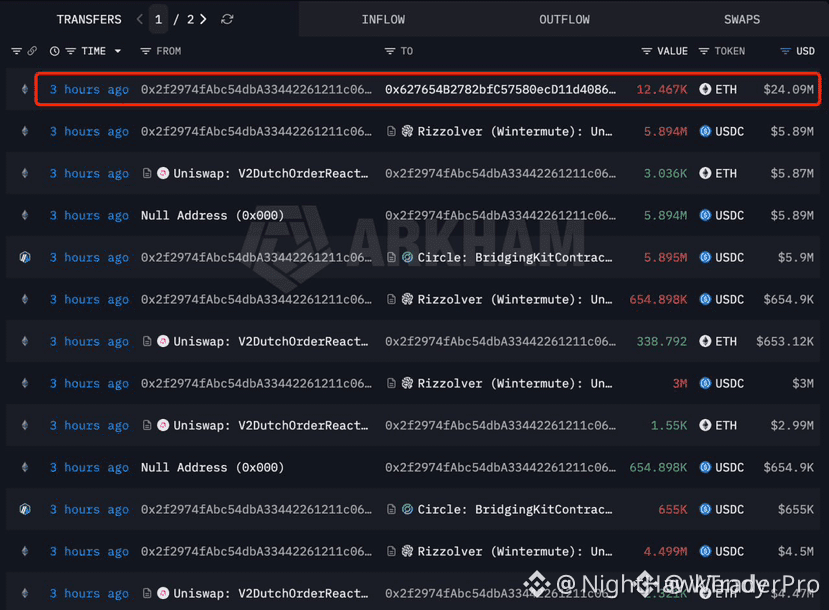
🚨 $AFX EXPLOIT – $24M DRAINED, ATTACKER FLOODS ETH WITH FRESH LIQUIDITY! 💣
📌 AFX Trade just got gutted for 24.15M USDC – attacker bridged it straight to Ethereum and swapped into 12,467 ETH at $1,937 average. This isn't random – it's a classic exit play 💡
💥 The moment those USDC hit the order books, buyer pressure on ETH spiked. Smart money? No – this is forced demand from stolen capital. The same pattern we've seen after every major DeFi heist – sell the stablecoins, buy the blue chip token of choice, then wash out through mixers or CEXs. 📊
⚠️ No official recovery update yet. If the attacker dumps those ETH in chunks, we could see local resistance near $1,950 get tested. But for now, ETH is absorbing a 24M injection. 💬 Do you think this buy pressure gets absorbed cleanly or does the hacker unwind it into a cascade? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AFX #ETH #DeFi #Exploit #Crypto
🛡️ 🔍
🚨 $AFX EXPLOIT – $24M DRAINED, ATTACKER FLOODS ETH WITH FRESH LIQUIDITY! 💣
📌 AFX Trade just got gutted for 24.15M USDC – attacker bridged it straight to Ethereum and swapped into 12,467 ETH at $1,937 average. This isn't random – it's a classic exit play 💡
💥 The moment those USDC hit the order books, buyer pressure on ETH spiked. Smart money? No – this is forced demand from stolen capital. The same pattern we've seen after every major DeFi heist – sell the stablecoins, buy the blue chip token of choice, then wash out through mixers or CEXs. 📊
⚠️ No official recovery update yet. If the attacker dumps those ETH in chunks, we could see local resistance near $1,950 get tested. But for now, ETH is absorbing a 24M injection. 💬 Do you think this buy pressure gets absorbed cleanly or does the hacker unwind it into a cascade? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AFX #ETH #DeFi #Exploit #Crypto
🛡️ 🔍
📌 AFX Trade just got gutted for 24.15M USDC – attacker bridged it straight to Ethereum and swapped into 12,467 ETH at $1,937 average. This isn't random – it's a classic exit play 💡
💥 The moment those USDC hit the order books, buyer pressure on ETH spiked. Smart money? No – this is forced demand from stolen capital. The same pattern we've seen after every major DeFi heist – sell the stablecoins, buy the blue chip token of choice, then wash out through mixers or CEXs. 📊
⚠️ No official recovery update yet. If the attacker dumps those ETH in chunks, we could see local resistance near $1,950 get tested. But for now, ETH is absorbing a 24M injection. 💬 Do you think this buy pressure gets absorbed cleanly or does the hacker unwind it into a cascade? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AFX #ETH #DeFi #Exploit #Crypto
🛡️ 🔍
1
900
·
--
⚠️ DEFI SUMMERFI PROTOCOL ANNOUNCES ITS CLOSURE AFTER A MASSIVE EXPLOIT 🛑📉
💥 Impact and Final Shutdown
The decentralized finance protocol SummerFi (formerly known as Oasis.app) formally announced that it will begin the process of winding down and gradually liquidating its services (sunsetting) after failing to recover from the impact caused by a critical security exploit in its smart contracts.
🛡️ Withdrawals and Liquidation
The development team urged all users and investors to immediately withdraw their liquidity and close their leveraged positions through the official interface before the platform’s final disconnection to avoid capital losses.
📊 Impact on the DeFi Ecosystem
SummerFi’s exit serves as another reminder of the security risks in smart contracts and DeFi infrastructure, adding volatility to the lending and decentralized yield management sector.
#SummerFi #DeFi #Exploit #CryptoNews #BinanceSquare
$SUN
{spot}(SUNUSDT)
$BTC
{spot}(BTCUSDT)
$ETH
{spot}(ETHUSDT)
⚠️ DEFI SUMMERFI PROTOCOL ANNOUNCES ITS CLOSURE AFTER A MASSIVE EXPLOIT 🛑📉
💥 Impact and Final Shutdown
The decentralized finance protocol SummerFi (formerly known as Oasis.app) formally announced that it will begin the process of winding down and gradually liquidating its services (sunsetting) after failing to recover from the impact caused by a critical security exploit in its smart contracts.
🛡️ Withdrawals and Liquidation
The development team urged all users and investors to immediately withdraw their liquidity and close their leveraged positions through the official interface before the platform’s final disconnection to avoid capital losses.
📊 Impact on the DeFi Ecosystem
SummerFi’s exit serves as another reminder of the security risks in smart contracts and DeFi infrastructure, adding volatility to the lending and decentralized yield management sector.
#SummerFi #DeFi #Exploit #CryptoNews #BinanceSquare
$SUN
$BTC
$ETH
💥 Impact and Final Shutdown
The decentralized finance protocol SummerFi (formerly known as Oasis.app) formally announced that it will begin the process of winding down and gradually liquidating its services (sunsetting) after failing to recover from the impact caused by a critical security exploit in its smart contracts.
🛡️ Withdrawals and Liquidation
The development team urged all users and investors to immediately withdraw their liquidity and close their leveraged positions through the official interface before the platform’s final disconnection to avoid capital losses.
📊 Impact on the DeFi Ecosystem
SummerFi’s exit serves as another reminder of the security risks in smart contracts and DeFi infrastructure, adding volatility to the lending and decentralized yield management sector.
#SummerFi #DeFi #Exploit #CryptoNews #BinanceSquare
$SUN
$BTC
$ETH
81
·
--
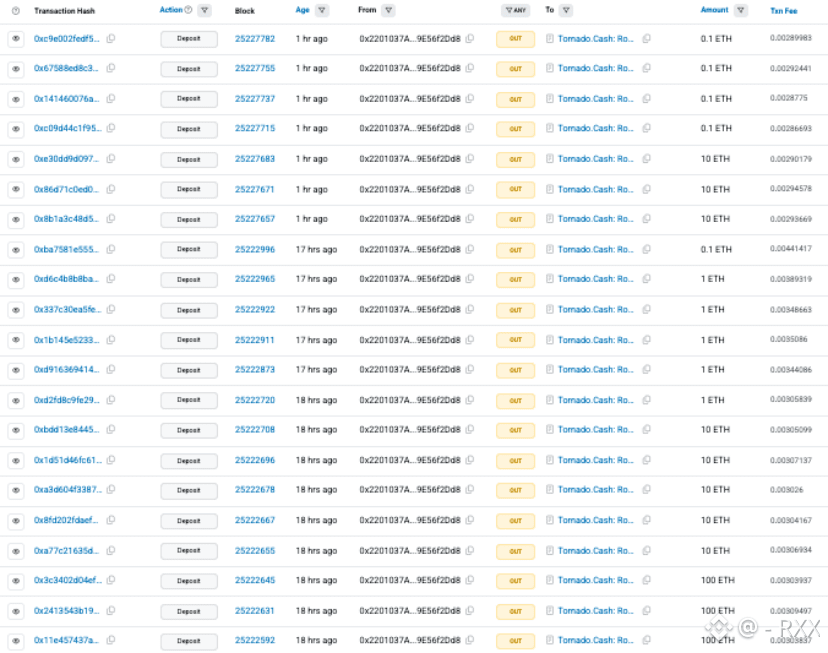
🚨 ANOTHER CRYPTO TOKEN JUST GOT NUKED TO ZERO 🩸😱
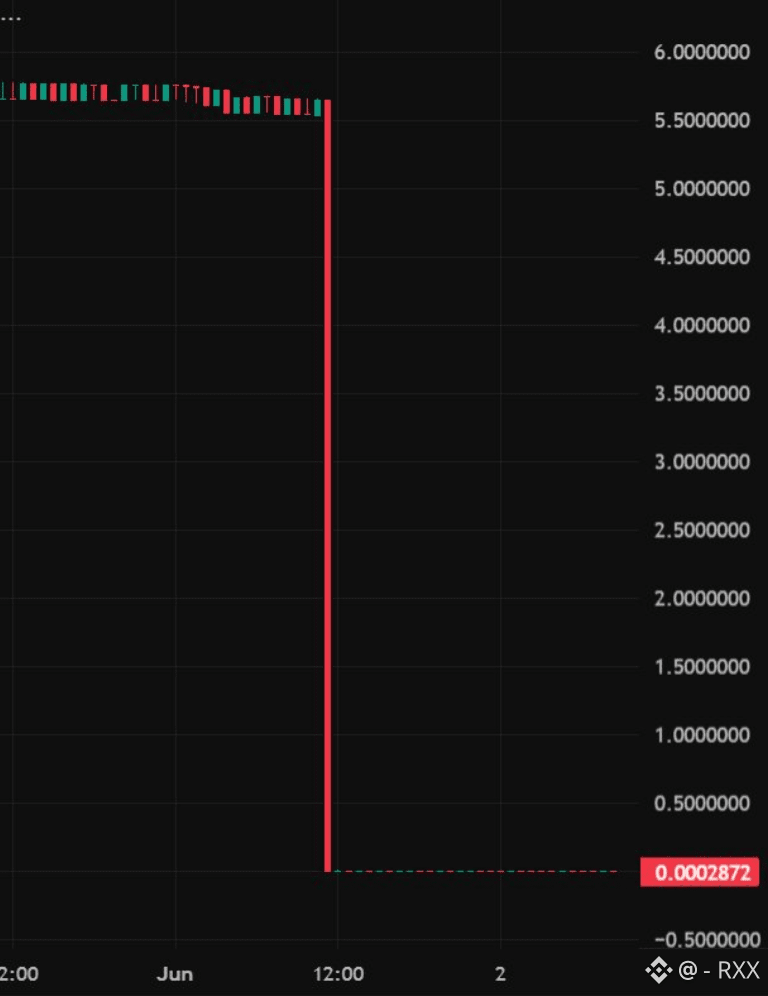
$TSR/USDT collapsed nearly 100% in a single day, crashing to around $0.0002 after a reported exploit on $BNB Chain. 👀
Here’s what allegedly happened:
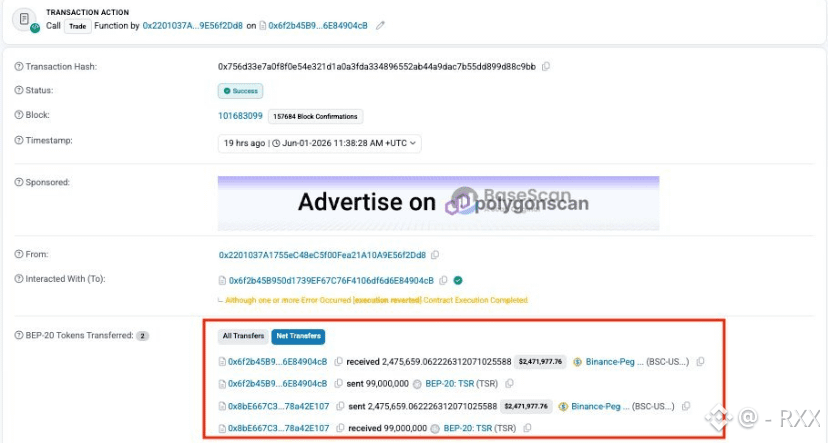
⚠️ An exploiter minted 99 MILLION $TSR
⚠️ Dumped the tokens on the market
⚠️ Extracted roughly $2.5M in $USDT
⚠️ Bridged funds to Ethereum
⚠️ Moved 1,285+ $ETH through Tornado Cash
The result?
📉 Price destruction
📉 Liquidity wiped out
📉 Holders left devastated
This is a brutal reminder of one of crypto’s biggest risks:
A project can look strong…
Until a smart contract vulnerability, exploit, or token mint issue turns everything upside down overnight. 🔥
In just hours:
💸 Millions disappeared
💸 Confidence vanished
💸 A token was effectively wiped out
The harsh reality?
In crypto, risk management matters more than chasing the next 100x.
Because sometimes one exploit is all it takes to erase an entire market. 👀
Stay safe.
Verify projects.
And never underestimate smart contract risk. ⚠️
$BNB
#Crypto #BNBChain #Exploit #Trading
{future}(BNBUSDT)
🚨 ANOTHER CRYPTO TOKEN JUST GOT NUKED TO ZERO 🩸😱
$TSR/USDT collapsed nearly 100% in a single day, crashing to around $0.0002 after a reported exploit on $BNB Chain. 👀
Here’s what allegedly happened:
⚠️ An exploiter minted 99 MILLION $TSR
⚠️ Dumped the tokens on the market
⚠️ Extracted roughly $2.5M in $USDT
⚠️ Bridged funds to Ethereum
⚠️ Moved 1,285+ $ETH through Tornado Cash
The result?
📉 Price destruction
📉 Liquidity wiped out
📉 Holders left devastated
This is a brutal reminder of one of crypto’s biggest risks:
A project can look strong…
Until a smart contract vulnerability, exploit, or token mint issue turns everything upside down overnight. 🔥
In just hours:
💸 Millions disappeared
💸 Confidence vanished
💸 A token was effectively wiped out
The harsh reality?
In crypto, risk management matters more than chasing the next 100x.
Because sometimes one exploit is all it takes to erase an entire market. 👀
Stay safe.
Verify projects.
And never underestimate smart contract risk. ⚠️
$BNB
#Crypto #BNBChain #Exploit #Trading
$TSR/USDT collapsed nearly 100% in a single day, crashing to around $0.0002 after a reported exploit on $BNB Chain. 👀
Here’s what allegedly happened:
⚠️ An exploiter minted 99 MILLION $TSR
⚠️ Dumped the tokens on the market
⚠️ Extracted roughly $2.5M in $USDT
⚠️ Bridged funds to Ethereum
⚠️ Moved 1,285+ $ETH through Tornado Cash
The result?
📉 Price destruction
📉 Liquidity wiped out
📉 Holders left devastated
This is a brutal reminder of one of crypto’s biggest risks:
A project can look strong…
Until a smart contract vulnerability, exploit, or token mint issue turns everything upside down overnight. 🔥
In just hours:
💸 Millions disappeared
💸 Confidence vanished
💸 A token was effectively wiped out
The harsh reality?
In crypto, risk management matters more than chasing the next 100x.
Because sometimes one exploit is all it takes to erase an entire market. 👀
Stay safe.
Verify projects.
And never underestimate smart contract risk. ⚠️
$BNB
#Crypto #BNBChain #Exploit #Trading
1
144
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanBTCReboundAfterFallingBelow60K?
369,886 views
1,555 Discussing
2
#GlobalStocksFaceLongestLosingStreakSince2023
123,905 views
1,098 Discussing
3
#BlackRockIBITPostsRecord$541MSingleDayOutflow
721 views
17 Discussing
4
#AnthropicPlungesTowardIPOPriceonDay2
59,580 views
598 Discussing
5
#TwentyOneCapitalAdds172.25BTC
12,105 views
162 Discussing
6
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
1,017 views
14 Discussing
7
#BNBDropsBelow540USDTWith8.46%DailyDecline
32,808 views
278 Discussing
8
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,079 views
14 Discussing
9
#BitMineFaces$10.1BUnrealizedETHLoss
2,028 views
18 Discussing
10
#StrategyReports$35BNetReserves
2,046 views
18 Discussing