
#safe
safe
326,656 views
1,667 Discussing
Hot
Latest
·
--
Article
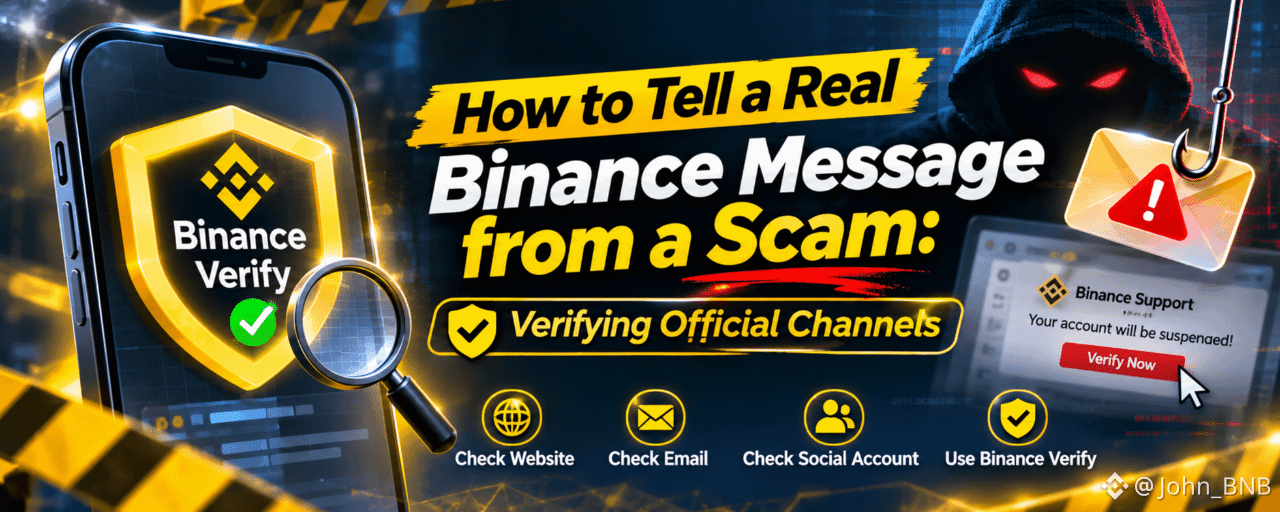
How to Tell a Real Binance Message from a Scam: Verifying Official ChannelsBinance Security Guide | Account Protection | Anti-Phishing
In the crypto world, not every message that looks official comes from the real source.
Scammers frequently impersonate trusted crypto platforms, especially after major security incidents or breaking news. They use fake emails, cloned websites, fraudulent social media accounts, and impersonated customer support agents to trick users into revealing sensitive information or transferring funds.
A message may carry the Binance logo, use professional language, and even appear to come from a familiar account. But appearances are not proof of authenticity.
The good news is that users have a way to check.
This guide explains how to verify whether a website, email, social media account, or other communication genuinely belongs to Binance, how to recognize common scam tactics, and what to do when something feels suspicious.
1. Use Binance Verify Before Trusting a Message
One of the simplest ways to check whether a communication is legitimate is Binance Verify.
Binance Verify is an official verification tool that allows users to check whether a website address, email address, phone number, or social media account is associated with Binance's official channels.
Instead of trusting a message because it looks professional, independently verify its source.
How to use it:
Visit [Binance Verify](https://www.binance.com/en/official-verification)Copy the website URL, email address, phone number, or social media account you want to check.Enter the information into the verification tool.Review the result to determine whether the source is officially recognized.If the source cannot be verified, do not interact with it until you confirm through Binance's official channels.
Important: Always access Binance Verify by typing the official Binance website address yourself or using a trusted bookmark. Avoid clicking verification links sent by suspicious accounts.
2. Check Every Channel, Not Just the Logo
Scammers can imitate almost anything. Knowing where legitimate Binance communications originate is an important part of account security.
Here are the main channels to check:
A. Websites and URLs
Always check the domain name before entering login credentials.Watch for misspellings, extra characters, unusual extensions, and misleading subdomains.Avoid shortened URLs from unknown sources.Access Binance by typing its official address directly: binance.com
B. Social media accounts
Check the account handle and verification status.Be careful with accounts using similar usernames, copied profile pictures, and Binance branding.Verify the social media handle through Binance Verify.Never trust someone simply because they claim to be a Binance employee or Angel.
C. Emails
Inspect the complete sender address, not just the display name.Check your personal Anti-Phishing Code.Avoid opening unexpected attachments or clicking suspicious links.Remember that email sender addresses can be spoofed.
D. Customer Support
Start conversations through Binance's official app or website.Do not trust unsolicited messages from people claiming to be support agents.Never install remote-access software or share your screen because someone claiming to be support asks you to.
3. Recognize the Warning Signs of a Scam
Most impersonation scams follow a familiar pattern: create fear, establish false trust, and push the victim into making a quick decision.
Watch for these common warning signs:
Warning sign
What scammers might say
Urgency
"Your account will be suspended in 30 minutes!"
Security threats
"We detected suspicious activity. Verify immediately."
Fake rewards
"Claim your exclusive Binance bonus here."
Account recovery
"Send your verification code to restore access."
Fake support
"I am your assigned Binance security officer."
Fund transfers
"Move your assets to this secure wallet."
Suspicious links
"Click here to unlock your account."
One particularly important lesson:
Urgency combined with a request for credentials is one of the clearest signs of a scam.
Legitimate security notifications may inform you about account activity, but you should independently open Binance and investigate rather than following instructions from an unexpected message.
4. Understand the Power of Your Anti-Phishing Code
Binance provides an additional security feature called the Anti-Phishing Code.
It allows users to create a unique personal code that appears in genuine Binance emails.
When enabled, you can use this code to distinguish legitimate Binance emails from many phishing attempts.
How to enable it:
Log in through the official Binance app or website.Navigate to your account's Security settings.Find Anti-Phishing Code.Create a unique code that is difficult for others to guess.Save your settings.
Whenever you receive an email claiming to come from Binance, check whether your personal code is displayed.
If it is missing or incorrect, treat the email as suspicious and verify it independently.
Remember: This feature helps authenticate emails, not every SMS, phone call, or social media message. It should be used alongside Binance Verify.
5. What Binance Will Never Ask You to Do
This is perhaps the most important section for every crypto user.
Scammers often pretend to help users protect their accounts, but their real objective is to gain access to their funds.
Keep these rules in mind:
Never share your account password.Never disclose your 2FA or verification codes.Never share your wallet seed phrase or private keys.Never transfer cryptocurrency to a stranger claiming it is necessary to secure your account.Never scan an unknown QR code to log in or authorize access.Never install remote-access applications at the request of an unverified support agent.Never provide screenshots or sensitive account information to strangers.
Your credentials belong to you. No legitimate support conversation should require you to hand over your password, 2FA codes, or private keys.
6. What Should You Do If You Receive a Suspicious Message?
If you receive a suspicious message claiming to be from Binance, don't panic. Follow these steps:
Stop: Don't click links, download files, reply, or share information.Verify: Check the sender, URL, email, or social account through Binance Verify.Report: Report suspicious impersonation through official Binance Support.Secure: If you have interacted with a suspicious website or disclosed information, change your password through the official platform and review your security settings.Act immediately: If you suspect unauthorized access, contact Binance Support through the official app or website and follow its instructions to secure or disable your account.
Also review your account activity, login history, and withdrawal records for anything you don't recognize.
The sooner you respond, the better your chances of limiting potential damage.
7. Security Is a Shared Responsibility
Binance provides security tools and official verification channels, but users also play an important role in protecting their assets.
A strong password, 2FA, Anti-Phishing Code, and regular security checks can help reduce risks. However, the most valuable habit is learning to question unexpected communications before taking action.
Scammers don't necessarily need to break through a platform's security systems if they can convince users to give away their credentials.
The next time someone sends you an urgent message claiming to be from Binance, remember three simple words:
STOP. VERIFY. PROTECT.
Don't trust appearances. Verify the source before you trust the message.
Frequently Asked Questions
1. How can I verify whether a Binance employee is real?
Use Binance Verify to check their email address, phone number, or social media handle. If you cannot verify their identity, do not proceed with their requests.
2. Does Binance Verify check Telegram accounts?
Yes. You can enter Telegram usernames and other supported social media handles to check whether they are officially recognized.
3. What if Binance Verify says an account is verified, but the message still looks suspicious?
Remain cautious. Email and SMS sender information can be spoofed. Contact Binance Support independently if you have doubts.
4. Does Binance Support ever ask for my password or 2FA code?
You should never disclose your password, 2FA codes, seed phrase, or private keys to anyone claiming to be support.
5. Where can I report a fake Binance account?
Use the official Binance Support portal to report suspicious accounts, messages, and phishing websites.
Official Security Resources
[Binance Verify – Official Verification Tool](https://www.binance.com/en/official-verification)[How to Identify and Avoid Binance Imposters](https://www.binance.com/blog/security/299010416215875222?ref=CPA_0037NAK6ST)[How to Identify Phishing Emails](https://www.binance.com/en/support/faq/detail/360002070252?utm_source=new_share&ref=CPA_0037NAK6ST)[How to Prevent Phishing Attacks](https://www.binance.com/en/support/faq/detail/360020819031?utm_source=new_share&ref=CPA_0037NAK6ST)
#Binance #security #SAFE #safu
How to Tell a Real Binance Message from a Scam: Verifying Official Channels
Binance Security Guide | Account Protection | Anti-Phishing
In the crypto world, not every message that looks official comes from the real source.
Scammers frequently impersonate trusted crypto platforms, especially after major security incidents or breaking news. They use fake emails, cloned websites, fraudulent social media accounts, and impersonated customer support agents to trick users into revealing sensitive information or transferring funds.
A message may carry the Binance logo, use professional language, and even appear to come from a familiar account. But appearances are not proof of authenticity.
The good news is that users have a way to check.
This guide explains how to verify whether a website, email, social media account, or other communication genuinely belongs to Binance, how to recognize common scam tactics, and what to do when something feels suspicious.
1. Use Binance Verify Before Trusting a Message
One of the simplest ways to check whether a communication is legitimate is Binance Verify.
Binance Verify is an official verification tool that allows users to check whether a website address, email address, phone number, or social media account is associated with Binance's official channels.
Instead of trusting a message because it looks professional, independently verify its source.
How to use it:
Visit Binance VerifyCopy the website URL, email address, phone number, or social media account you want to check.Enter the information into the verification tool.Review the result to determine whether the source is officially recognized.If the source cannot be verified, do not interact with it until you confirm through Binance's official channels.
Important: Always access Binance Verify by typing the official Binance website address yourself or using a trusted bookmark. Avoid clicking verification links sent by suspicious accounts.
2. Check Every Channel, Not Just the Logo
Scammers can imitate almost anything. Knowing where legitimate Binance communications originate is an important part of account security.
Here are the main channels to check:
A. Websites and URLs
Always check the domain name before entering login credentials.Watch for misspellings, extra characters, unusual extensions, and misleading subdomains.Avoid shortened URLs from unknown sources.Access Binance by typing its official address directly: binance.com
B. Social media accounts
Check the account handle and verification status.Be careful with accounts using similar usernames, copied profile pictures, and Binance branding.Verify the social media handle through Binance Verify.Never trust someone simply because they claim to be a Binance employee or Angel.
C. Emails
Inspect the complete sender address, not just the display name.Check your personal Anti-Phishing Code.Avoid opening unexpected attachments or clicking suspicious links.Remember that email sender addresses can be spoofed.
D. Customer Support
Start conversations through Binance's official app or website.Do not trust unsolicited messages from people claiming to be support agents.Never install remote-access software or share your screen because someone claiming to be support asks you to.
3. Recognize the Warning Signs of a Scam
Most impersonation scams follow a familiar pattern: create fear, establish false trust, and push the victim into making a quick decision.
Watch for these common warning signs:
Warning sign
What scammers might say
Urgency
"Your account will be suspended in 30 minutes!"
Security threats
"We detected suspicious activity. Verify immediately."
Fake rewards
"Claim your exclusive Binance bonus here."
Account recovery
"Send your verification code to restore access."
Fake support
"I am your assigned Binance security officer."
Fund transfers
"Move your assets to this secure wallet."
Suspicious links
"Click here to unlock your account."
One particularly important lesson:
Urgency combined with a request for credentials is one of the clearest signs of a scam.
Legitimate security notifications may inform you about account activity, but you should independently open Binance and investigate rather than following instructions from an unexpected message.
4. Understand the Power of Your Anti-Phishing Code
Binance provides an additional security feature called the Anti-Phishing Code.
It allows users to create a unique personal code that appears in genuine Binance emails.
When enabled, you can use this code to distinguish legitimate Binance emails from many phishing attempts.
How to enable it:
Log in through the official Binance app or website.Navigate to your account's Security settings.Find Anti-Phishing Code.Create a unique code that is difficult for others to guess.Save your settings.
Whenever you receive an email claiming to come from Binance, check whether your personal code is displayed.
If it is missing or incorrect, treat the email as suspicious and verify it independently.
Remember: This feature helps authenticate emails, not every SMS, phone call, or social media message. It should be used alongside Binance Verify.
5. What Binance Will Never Ask You to Do
This is perhaps the most important section for every crypto user.
Scammers often pretend to help users protect their accounts, but their real objective is to gain access to their funds.
Keep these rules in mind:
Never share your account password.Never disclose your 2FA or verification codes.Never share your wallet seed phrase or private keys.Never transfer cryptocurrency to a stranger claiming it is necessary to secure your account.Never scan an unknown QR code to log in or authorize access.Never install remote-access applications at the request of an unverified support agent.Never provide screenshots or sensitive account information to strangers.
Your credentials belong to you. No legitimate support conversation should require you to hand over your password, 2FA codes, or private keys.
6. What Should You Do If You Receive a Suspicious Message?
If you receive a suspicious message claiming to be from Binance, don't panic. Follow these steps:
Stop: Don't click links, download files, reply, or share information.Verify: Check the sender, URL, email, or social account through Binance Verify.Report: Report suspicious impersonation through official Binance Support.Secure: If you have interacted with a suspicious website or disclosed information, change your password through the official platform and review your security settings.Act immediately: If you suspect unauthorized access, contact Binance Support through the official app or website and follow its instructions to secure or disable your account.
Also review your account activity, login history, and withdrawal records for anything you don't recognize.
The sooner you respond, the better your chances of limiting potential damage.
7. Security Is a Shared Responsibility
Binance provides security tools and official verification channels, but users also play an important role in protecting their assets.
A strong password, 2FA, Anti-Phishing Code, and regular security checks can help reduce risks. However, the most valuable habit is learning to question unexpected communications before taking action.
Scammers don't necessarily need to break through a platform's security systems if they can convince users to give away their credentials.
The next time someone sends you an urgent message claiming to be from Binance, remember three simple words:
STOP. VERIFY. PROTECT.
Don't trust appearances. Verify the source before you trust the message.
Frequently Asked Questions
1. How can I verify whether a Binance employee is real?
Use Binance Verify to check their email address, phone number, or social media handle. If you cannot verify their identity, do not proceed with their requests.
2. Does Binance Verify check Telegram accounts?
Yes. You can enter Telegram usernames and other supported social media handles to check whether they are officially recognized.
3. What if Binance Verify says an account is verified, but the message still looks suspicious?
Remain cautious. Email and SMS sender information can be spoofed. Contact Binance Support independently if you have doubts.
4. Does Binance Support ever ask for my password or 2FA code?
You should never disclose your password, 2FA codes, seed phrase, or private keys to anyone claiming to be support.
5. Where can I report a fake Binance account?
Use the official Binance Support portal to report suspicious accounts, messages, and phishing websites.
Official Security Resources
Binance Verify – Official Verification ToolHow to Identify and Avoid Binance ImpostersHow to Identify Phishing EmailsHow to Prevent Phishing Attacks
#Binance #security #SAFE #safu
In the crypto world, not every message that looks official comes from the real source.
Scammers frequently impersonate trusted crypto platforms, especially after major security incidents or breaking news. They use fake emails, cloned websites, fraudulent social media accounts, and impersonated customer support agents to trick users into revealing sensitive information or transferring funds.
A message may carry the Binance logo, use professional language, and even appear to come from a familiar account. But appearances are not proof of authenticity.
The good news is that users have a way to check.
This guide explains how to verify whether a website, email, social media account, or other communication genuinely belongs to Binance, how to recognize common scam tactics, and what to do when something feels suspicious.
1. Use Binance Verify Before Trusting a Message
One of the simplest ways to check whether a communication is legitimate is Binance Verify.
Binance Verify is an official verification tool that allows users to check whether a website address, email address, phone number, or social media account is associated with Binance's official channels.
Instead of trusting a message because it looks professional, independently verify its source.
How to use it:
Visit Binance VerifyCopy the website URL, email address, phone number, or social media account you want to check.Enter the information into the verification tool.Review the result to determine whether the source is officially recognized.If the source cannot be verified, do not interact with it until you confirm through Binance's official channels.
Important: Always access Binance Verify by typing the official Binance website address yourself or using a trusted bookmark. Avoid clicking verification links sent by suspicious accounts.
2. Check Every Channel, Not Just the Logo
Scammers can imitate almost anything. Knowing where legitimate Binance communications originate is an important part of account security.
Here are the main channels to check:
A. Websites and URLs
Always check the domain name before entering login credentials.Watch for misspellings, extra characters, unusual extensions, and misleading subdomains.Avoid shortened URLs from unknown sources.Access Binance by typing its official address directly: binance.com
B. Social media accounts
Check the account handle and verification status.Be careful with accounts using similar usernames, copied profile pictures, and Binance branding.Verify the social media handle through Binance Verify.Never trust someone simply because they claim to be a Binance employee or Angel.
C. Emails
Inspect the complete sender address, not just the display name.Check your personal Anti-Phishing Code.Avoid opening unexpected attachments or clicking suspicious links.Remember that email sender addresses can be spoofed.
D. Customer Support
Start conversations through Binance's official app or website.Do not trust unsolicited messages from people claiming to be support agents.Never install remote-access software or share your screen because someone claiming to be support asks you to.
3. Recognize the Warning Signs of a Scam
Most impersonation scams follow a familiar pattern: create fear, establish false trust, and push the victim into making a quick decision.
Watch for these common warning signs:
Warning sign
What scammers might say
Urgency
"Your account will be suspended in 30 minutes!"
Security threats
"We detected suspicious activity. Verify immediately."
Fake rewards
"Claim your exclusive Binance bonus here."
Account recovery
"Send your verification code to restore access."
Fake support
"I am your assigned Binance security officer."
Fund transfers
"Move your assets to this secure wallet."
Suspicious links
"Click here to unlock your account."
One particularly important lesson:
Urgency combined with a request for credentials is one of the clearest signs of a scam.
Legitimate security notifications may inform you about account activity, but you should independently open Binance and investigate rather than following instructions from an unexpected message.
4. Understand the Power of Your Anti-Phishing Code
Binance provides an additional security feature called the Anti-Phishing Code.
It allows users to create a unique personal code that appears in genuine Binance emails.
When enabled, you can use this code to distinguish legitimate Binance emails from many phishing attempts.
How to enable it:
Log in through the official Binance app or website.Navigate to your account's Security settings.Find Anti-Phishing Code.Create a unique code that is difficult for others to guess.Save your settings.
Whenever you receive an email claiming to come from Binance, check whether your personal code is displayed.
If it is missing or incorrect, treat the email as suspicious and verify it independently.
Remember: This feature helps authenticate emails, not every SMS, phone call, or social media message. It should be used alongside Binance Verify.
5. What Binance Will Never Ask You to Do
This is perhaps the most important section for every crypto user.
Scammers often pretend to help users protect their accounts, but their real objective is to gain access to their funds.
Keep these rules in mind:
Never share your account password.Never disclose your 2FA or verification codes.Never share your wallet seed phrase or private keys.Never transfer cryptocurrency to a stranger claiming it is necessary to secure your account.Never scan an unknown QR code to log in or authorize access.Never install remote-access applications at the request of an unverified support agent.Never provide screenshots or sensitive account information to strangers.
Your credentials belong to you. No legitimate support conversation should require you to hand over your password, 2FA codes, or private keys.
6. What Should You Do If You Receive a Suspicious Message?
If you receive a suspicious message claiming to be from Binance, don't panic. Follow these steps:
Stop: Don't click links, download files, reply, or share information.Verify: Check the sender, URL, email, or social account through Binance Verify.Report: Report suspicious impersonation through official Binance Support.Secure: If you have interacted with a suspicious website or disclosed information, change your password through the official platform and review your security settings.Act immediately: If you suspect unauthorized access, contact Binance Support through the official app or website and follow its instructions to secure or disable your account.
Also review your account activity, login history, and withdrawal records for anything you don't recognize.
The sooner you respond, the better your chances of limiting potential damage.
7. Security Is a Shared Responsibility
Binance provides security tools and official verification channels, but users also play an important role in protecting their assets.
A strong password, 2FA, Anti-Phishing Code, and regular security checks can help reduce risks. However, the most valuable habit is learning to question unexpected communications before taking action.
Scammers don't necessarily need to break through a platform's security systems if they can convince users to give away their credentials.
The next time someone sends you an urgent message claiming to be from Binance, remember three simple words:
STOP. VERIFY. PROTECT.
Don't trust appearances. Verify the source before you trust the message.
Frequently Asked Questions
1. How can I verify whether a Binance employee is real?
Use Binance Verify to check their email address, phone number, or social media handle. If you cannot verify their identity, do not proceed with their requests.
2. Does Binance Verify check Telegram accounts?
Yes. You can enter Telegram usernames and other supported social media handles to check whether they are officially recognized.
3. What if Binance Verify says an account is verified, but the message still looks suspicious?
Remain cautious. Email and SMS sender information can be spoofed. Contact Binance Support independently if you have doubts.
4. Does Binance Support ever ask for my password or 2FA code?
You should never disclose your password, 2FA codes, seed phrase, or private keys to anyone claiming to be support.
5. Where can I report a fake Binance account?
Use the official Binance Support portal to report suspicious accounts, messages, and phishing websites.
Official Security Resources
Binance Verify – Official Verification ToolHow to Identify and Avoid Binance ImpostersHow to Identify Phishing EmailsHow to Prevent Phishing Attacks
#Binance #security #SAFE #safu
Abu Fahadأ:
💛
2
3
546
·
--
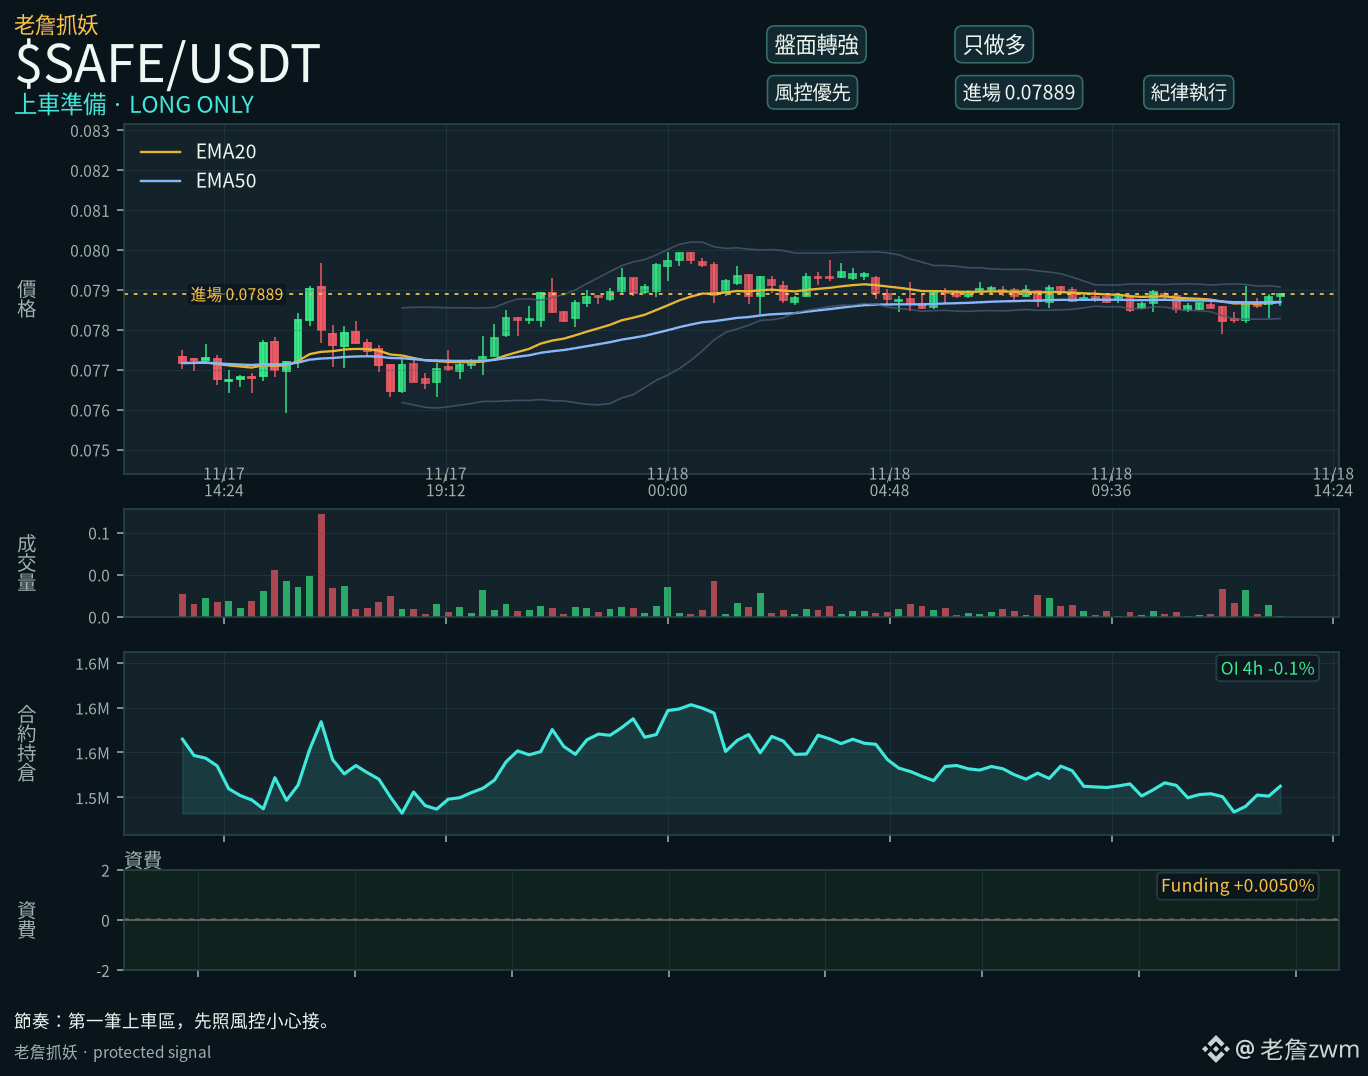
When everyone starts talking about it, the entry is no longer attractive
$SAFE is hovering near the low, and buyers are starting to step in
Over the past hour, active buy orders have clearly outnumbered sell orders, and the price is still close to its two-day low
One thing to watch: liquidity is average, so slippage is likely, and trading volume has been fluctuating sharply
Use limit orders; don’t chase with market orders. Exit if it drops below 0.06706, and take 30% off the table at 0.08678
#SAFE #山寨币 #Contract
When everyone starts talking about it, the entry is no longer attractive
$SAFE is hovering near the low, and buyers are starting to step in
Over the past hour, active buy orders have clearly outnumbered sell orders, and the price is still close to its two-day low
One thing to watch: liquidity is average, so slippage is likely, and trading volume has been fluctuating sharply
Use limit orders; don’t chase with market orders. Exit if it drops below 0.06706, and take 30% off the table at 0.08678
#SAFE #山寨币 #Contract
$SAFE is hovering near the low, and buyers are starting to step in
Over the past hour, active buy orders have clearly outnumbered sell orders, and the price is still close to its two-day low
One thing to watch: liquidity is average, so slippage is likely, and trading volume has been fluctuating sharply
Use limit orders; don’t chase with market orders. Exit if it drops below 0.06706, and take 30% off the table at 0.08678
#SAFE #山寨币 #Contract
14

·
--
🚨 $SAFE BETRAYAL WITHOUT A SINGLE SIGNATURE
A Gnosis Safe multisig wallet lost about $6.45M in a single transaction, and the most shocking part is that none of the owners signed anything: the attacker used a permission the wallet itself had granted to a module. To me, this shatters the idea that multisigs are untouchable: they didn’t hack the contract, they hacked the trust you placed in a third party.
Here’s the detail no one is noticing:
→ In a single transaction, at 11:35 UTC on November 16, 4.39 million USDC and 1.72 million syrupUSDC were transferred out—about $6.44M combined.
→ The attacker has already converted about $813,000 into Monero (XMR) via Hyperliquid and another ~$1.2M via Wagyu: the trail is being erased.
→ Safe and Zodiac say there’s no flaw in their contracts: the cause was a compromised role key and overly broad permissions. The owner has yet to be identified, and no reimbursement has been announced.
Do you still trust your multisig as it is, or will you review the permissions you’ve given to other modules today? 👇
$SAFE $USDC $XMR
#Safe #Multisig #HackeoCrypto
🚨 $SAFE BETRAYAL WITHOUT A SINGLE SIGNATURE
A Gnosis Safe multisig wallet lost about $6.45M in a single transaction, and the most shocking part is that none of the owners signed anything: the attacker used a permission the wallet itself had granted to a module. To me, this shatters the idea that multisigs are untouchable: they didn’t hack the contract, they hacked the trust you placed in a third party.
Here’s the detail no one is noticing:
→ In a single transaction, at 11:35 UTC on November 16, 4.39 million USDC and 1.72 million syrupUSDC were transferred out—about $6.44M combined.
→ The attacker has already converted about $813,000 into Monero (XMR) via Hyperliquid and another ~$1.2M via Wagyu: the trail is being erased.
→ Safe and Zodiac say there’s no flaw in their contracts: the cause was a compromised role key and overly broad permissions. The owner has yet to be identified, and no reimbursement has been announced.
Do you still trust your multisig as it is, or will you review the permissions you’ve given to other modules today? 👇
$SAFE $USDC $XMR
#Safe #Multisig #HackeoCrypto
A Gnosis Safe multisig wallet lost about $6.45M in a single transaction, and the most shocking part is that none of the owners signed anything: the attacker used a permission the wallet itself had granted to a module. To me, this shatters the idea that multisigs are untouchable: they didn’t hack the contract, they hacked the trust you placed in a third party.
Here’s the detail no one is noticing:
→ In a single transaction, at 11:35 UTC on November 16, 4.39 million USDC and 1.72 million syrupUSDC were transferred out—about $6.44M combined.
→ The attacker has already converted about $813,000 into Monero (XMR) via Hyperliquid and another ~$1.2M via Wagyu: the trail is being erased.
→ Safe and Zodiac say there’s no flaw in their contracts: the cause was a compromised role key and overly broad permissions. The owner has yet to be identified, and no reimbursement has been announced.
Do you still trust your multisig as it is, or will you review the permissions you’ve given to other modules today? 👇
$SAFE $USDC $XMR
#Safe #Multisig #HackeoCrypto
720

·
--
Article
Multisig wallet loses $6.45 million without a single signature from its owners$6.45 million was drained from a multisig wallet without a single signature.
On Monday, November 16, a Safe multisig wallet lost about $6.45 million, most of it comprising roughly $4.3 million in USDC and $1.7 million in syrupUSDC, with the rest made up of several hundred thousand dollars in other assets. Blockchain security firm PeckShield issued an alert that day, based on a tip from on-chain analyst Specter. The funds were transferred in a single transaction through a preconfigured authorization module called Zodiac Roles. Not one of the multisig’s owners had signed, yet the funds were gone.
That’s how a multisig wallet is supposed to work: several people have to approve a transfer; no single person can decide on their own. But this wallet had previously been configured with a “role authorization,” meaning a designated key could move funds on its own within the permissions that had been set, without needing to gather the owners’ signatures. A co-founder of Zodiac later responded that there was no vulnerability in the module’s contract itself; the transfer used a key belonging to a former role member, which had most likely been stolen. Combined with the wallet’s overly broad authorization policy, that’s how the door was opened. Safe also said its own contracts and wallet app were unaffected. This wasn’t the first time this year that someone had targeted a third-party module used with Safe.
Multisig wallet loses $6.45 million without a single signature from its owners
$6.45 million was drained from a multisig wallet without a single signature.
On Monday, November 16, a Safe multisig wallet lost about $6.45 million, most of it comprising roughly $4.3 million in USDC and $1.7 million in syrupUSDC, with the rest made up of several hundred thousand dollars in other assets. Blockchain security firm PeckShield issued an alert that day, based on a tip from on-chain analyst Specter. The funds were transferred in a single transaction through a preconfigured authorization module called Zodiac Roles. Not one of the multisig’s owners had signed, yet the funds were gone.
That’s how a multisig wallet is supposed to work: several people have to approve a transfer; no single person can decide on their own. But this wallet had previously been configured with a “role authorization,” meaning a designated key could move funds on its own within the permissions that had been set, without needing to gather the owners’ signatures. A co-founder of Zodiac later responded that there was no vulnerability in the module’s contract itself; the transfer used a key belonging to a former role member, which had most likely been stolen. Combined with the wallet’s overly broad authorization policy, that’s how the door was opened. Safe also said its own contracts and wallet app were unaffected. This wasn’t the first time this year that someone had targeted a third-party module used with Safe.
On Monday, November 16, a Safe multisig wallet lost about $6.45 million, most of it comprising roughly $4.3 million in USDC and $1.7 million in syrupUSDC, with the rest made up of several hundred thousand dollars in other assets. Blockchain security firm PeckShield issued an alert that day, based on a tip from on-chain analyst Specter. The funds were transferred in a single transaction through a preconfigured authorization module called Zodiac Roles. Not one of the multisig’s owners had signed, yet the funds were gone.
That’s how a multisig wallet is supposed to work: several people have to approve a transfer; no single person can decide on their own. But this wallet had previously been configured with a “role authorization,” meaning a designated key could move funds on its own within the permissions that had been set, without needing to gather the owners’ signatures. A co-founder of Zodiac later responded that there was no vulnerability in the module’s contract itself; the transfer used a key belonging to a former role member, which had most likely been stolen. Combined with the wallet’s overly broad authorization policy, that’s how the door was opened. Safe also said its own contracts and wallet app were unaffected. This wasn’t the first time this year that someone had targeted a third-party module used with Safe.
145
·
--
Not a single signature was given on the multisig, yet $6.45 million was transferred out—this time, there was nothing wrong with the Safe contract.
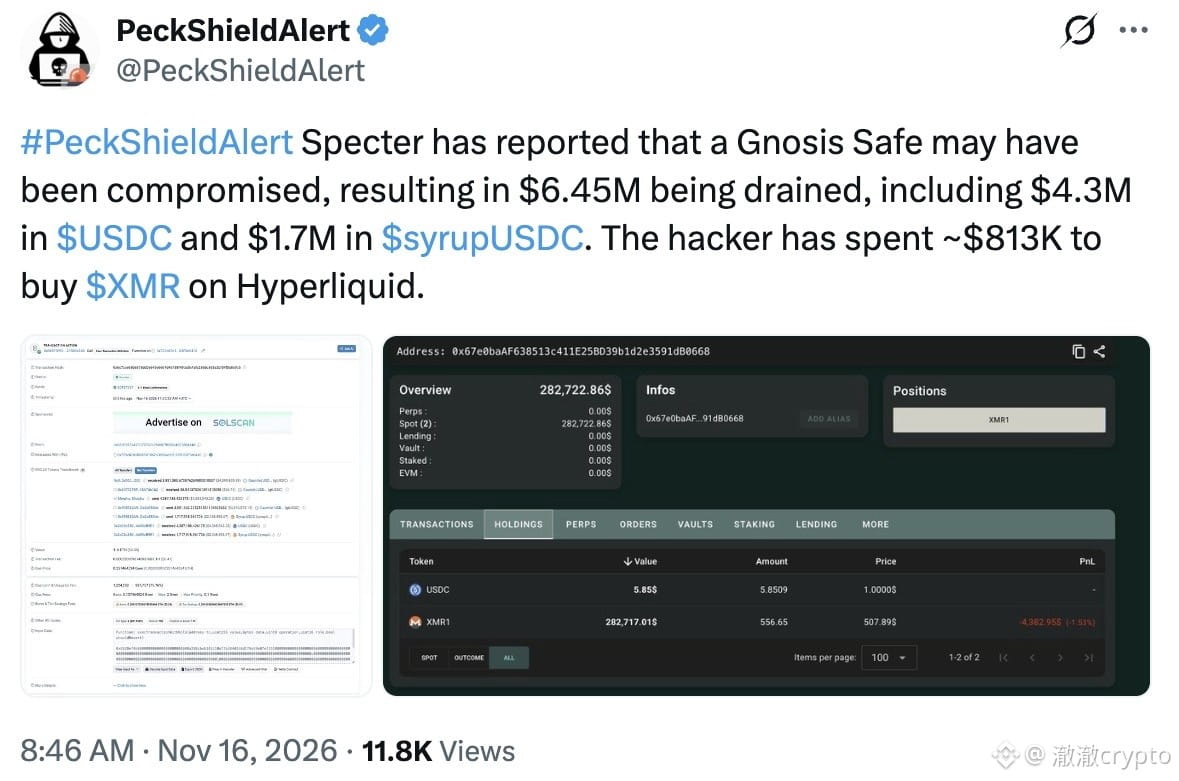
Here’s what happened: On Monday, November 16, a single transaction drained 4,387,188.43 USDC and 1,717,918.96 syrupUSDC from a Gnosis Safe multisig wallet, worth about $6.45 million in total (according to on-chain records, verified by Cointelegraph).
The funds were moved using the Zodiac Roles permissions module installed in the wallet itself, without requiring another signature from the owners.
The attacker then converted about $813,000 into Monero (XMR), while another roughly $1.2 million was laundered into XMR via Wagyu.
My take: This wasn’t Safe being hacked—it was a case of “keys + overly broad permissions” going wrong together.
A Zodiac co-founder said firsthand that the module had no vulnerability; a key belonging to a long-standing role member was suspected to have been stolen, and the wallet’s permissions were almost certainly configured to unintentionally allow the transfer.
What I’d do: If you use Safe as a team, check your Roles permissions list and immediately revoke any authorizations that exceed their intended scope.
What would change my mind: If further investigation finds a genuine vulnerability in the module itself, the assessment above no longer applies.
What do you think is the biggest multisig pitfall: contract vulnerabilities, or permissions configured incorrectly by users?
$BTC $ETH $SOL
#Safe #MultisigWallet
Not a single signature was given on the multisig, yet $6.45 million was transferred out—this time, there was nothing wrong with the Safe contract.
Here’s what happened: On Monday, November 16, a single transaction drained 4,387,188.43 USDC and 1,717,918.96 syrupUSDC from a Gnosis Safe multisig wallet, worth about $6.45 million in total (according to on-chain records, verified by Cointelegraph).
The funds were moved using the Zodiac Roles permissions module installed in the wallet itself, without requiring another signature from the owners.
The attacker then converted about $813,000 into Monero (XMR), while another roughly $1.2 million was laundered into XMR via Wagyu.
My take: This wasn’t Safe being hacked—it was a case of “keys + overly broad permissions” going wrong together.
A Zodiac co-founder said firsthand that the module had no vulnerability; a key belonging to a long-standing role member was suspected to have been stolen, and the wallet’s permissions were almost certainly configured to unintentionally allow the transfer.
What I’d do: If you use Safe as a team, check your Roles permissions list and immediately revoke any authorizations that exceed their intended scope.
What would change my mind: If further investigation finds a genuine vulnerability in the module itself, the assessment above no longer applies.
What do you think is the biggest multisig pitfall: contract vulnerabilities, or permissions configured incorrectly by users?
$BTC $ETH $SOL
#Safe #MultisigWallet
Here’s what happened: On Monday, November 16, a single transaction drained 4,387,188.43 USDC and 1,717,918.96 syrupUSDC from a Gnosis Safe multisig wallet, worth about $6.45 million in total (according to on-chain records, verified by Cointelegraph).
The funds were moved using the Zodiac Roles permissions module installed in the wallet itself, without requiring another signature from the owners.
The attacker then converted about $813,000 into Monero (XMR), while another roughly $1.2 million was laundered into XMR via Wagyu.
My take: This wasn’t Safe being hacked—it was a case of “keys + overly broad permissions” going wrong together.
A Zodiac co-founder said firsthand that the module had no vulnerability; a key belonging to a long-standing role member was suspected to have been stolen, and the wallet’s permissions were almost certainly configured to unintentionally allow the transfer.
What I’d do: If you use Safe as a team, check your Roles permissions list and immediately revoke any authorizations that exceed their intended scope.
What would change my mind: If further investigation finds a genuine vulnerability in the module itself, the assessment above no longer applies.
What do you think is the biggest multisig pitfall: contract vulnerabilities, or permissions configured incorrectly by users?
$BTC $ETH $SOL
#Safe #MultisigWallet
13
·
--
【No one signed the multisig wallet, yet $6.4 million was transferred in a single transaction! A Safe wallet was compromised through an “authorization module,” and some of the stolen funds have already been converted to Monero】
At around 7:30 p.m. on November 16 (Beijing time), a Safe multisig wallet on Ethereum requiring 2 of 4 signers transferred approximately 4.39 million USDC and 1.72 million syrupUSDC—about $6.44 million in total—in a single transaction without any signatures from its owners. The transfer was made through a Zodiac permissions module that had been enabled back in 2024. Some of the funds were subsequently converted into Monero, a privacy coin that is difficult to trace. So far, there appears to be no vulnerability in the contract itself; it is more likely that the private key of an address holding this permission for a long time was stolen, combined with the permission being set too broadly. If you’ve ever granted wallet permissions to a bot or fund manager, check whether it can transfer funds to external addresses.
#Safe #钱包安全 #HackAttack
【No one signed the multisig wallet, yet $6.4 million was transferred in a single transaction! A Safe wallet was compromised through an “authorization module,” and some of the stolen funds have already been converted to Monero】
At around 7:30 p.m. on November 16 (Beijing time), a Safe multisig wallet on Ethereum requiring 2 of 4 signers transferred approximately 4.39 million USDC and 1.72 million syrupUSDC—about $6.44 million in total—in a single transaction without any signatures from its owners. The transfer was made through a Zodiac permissions module that had been enabled back in 2024. Some of the funds were subsequently converted into Monero, a privacy coin that is difficult to trace. So far, there appears to be no vulnerability in the contract itself; it is more likely that the private key of an address holding this permission for a long time was stolen, combined with the permission being set too broadly. If you’ve ever granted wallet permissions to a bot or fund manager, check whether it can transfer funds to external addresses.
#Safe #钱包安全 #HackAttack
At around 7:30 p.m. on November 16 (Beijing time), a Safe multisig wallet on Ethereum requiring 2 of 4 signers transferred approximately 4.39 million USDC and 1.72 million syrupUSDC—about $6.44 million in total—in a single transaction without any signatures from its owners. The transfer was made through a Zodiac permissions module that had been enabled back in 2024. Some of the funds were subsequently converted into Monero, a privacy coin that is difficult to trace. So far, there appears to be no vulnerability in the contract itself; it is more likely that the private key of an address holding this permission for a long time was stolen, combined with the permission being set too broadly. If you’ve ever granted wallet permissions to a bot or fund manager, check whether it can transfer funds to external addresses.
#Safe #钱包安全 #HackAttack
105

$SAFE (Safe) spot check — the wallet token holding its low better than most today.
Price: ~$0.082, down ~5% in 24h, but still up ~6% over the last 7 days. 24h range $0.0817–$0.0869, market cap ~$65M.
Safe is the smart-account wallet behind most of crypto's multisig custody — real product, real usage — yet the token sits ~98% below its $3.63 ATH from April 2024. Down ~32% in 30 days, so it has not escaped this sell-off.
Levels: support $0.0817 (today's low), resistance $0.0869, then $0.09. Lose $0.0817 and the next stop is the $0.08 round number.
$BTC context: ~$69,335, down ~5.7% today after breaking below $70K, day low $67,568 — lowest since August. Fear & Greed at 20, and spot BTC ETF outflows are running 6 straight days.
Verdict: SAFE is holding up better than BTC today, but with the market this weak, spot buyers want $70K to flip back to support first.
Not financial advice. DYOR.
#Safe #Bitcoin #Crypto
$SAFE (Safe) spot check — the wallet token holding its low better than most today.
Price: ~$0.082, down ~5% in 24h, but still up ~6% over the last 7 days. 24h range $0.0817–$0.0869, market cap ~$65M.
Safe is the smart-account wallet behind most of crypto's multisig custody — real product, real usage — yet the token sits ~98% below its $3.63 ATH from April 2024. Down ~32% in 30 days, so it has not escaped this sell-off.
Levels: support $0.0817 (today's low), resistance $0.0869, then $0.09. Lose $0.0817 and the next stop is the $0.08 round number.
$BTC context: ~$69,335, down ~5.7% today after breaking below $70K, day low $67,568 — lowest since August. Fear & Greed at 20, and spot BTC ETF outflows are running 6 straight days.
Verdict: SAFE is holding up better than BTC today, but with the market this weak, spot buyers want $70K to flip back to support first.
Not financial advice. DYOR.
#Safe #Bitcoin #Crypto
Price: ~$0.082, down ~5% in 24h, but still up ~6% over the last 7 days. 24h range $0.0817–$0.0869, market cap ~$65M.
Safe is the smart-account wallet behind most of crypto's multisig custody — real product, real usage — yet the token sits ~98% below its $3.63 ATH from April 2024. Down ~32% in 30 days, so it has not escaped this sell-off.
Levels: support $0.0817 (today's low), resistance $0.0869, then $0.09. Lose $0.0817 and the next stop is the $0.08 round number.
$BTC context: ~$69,335, down ~5.7% today after breaking below $70K, day low $67,568 — lowest since August. Fear & Greed at 20, and spot BTC ETF outflows are running 6 straight days.
Verdict: SAFE is holding up better than BTC today, but with the market this weak, spot buyers want $70K to flip back to support first.
Not financial advice. DYOR.
#Safe #Bitcoin #Crypto
4
·
--
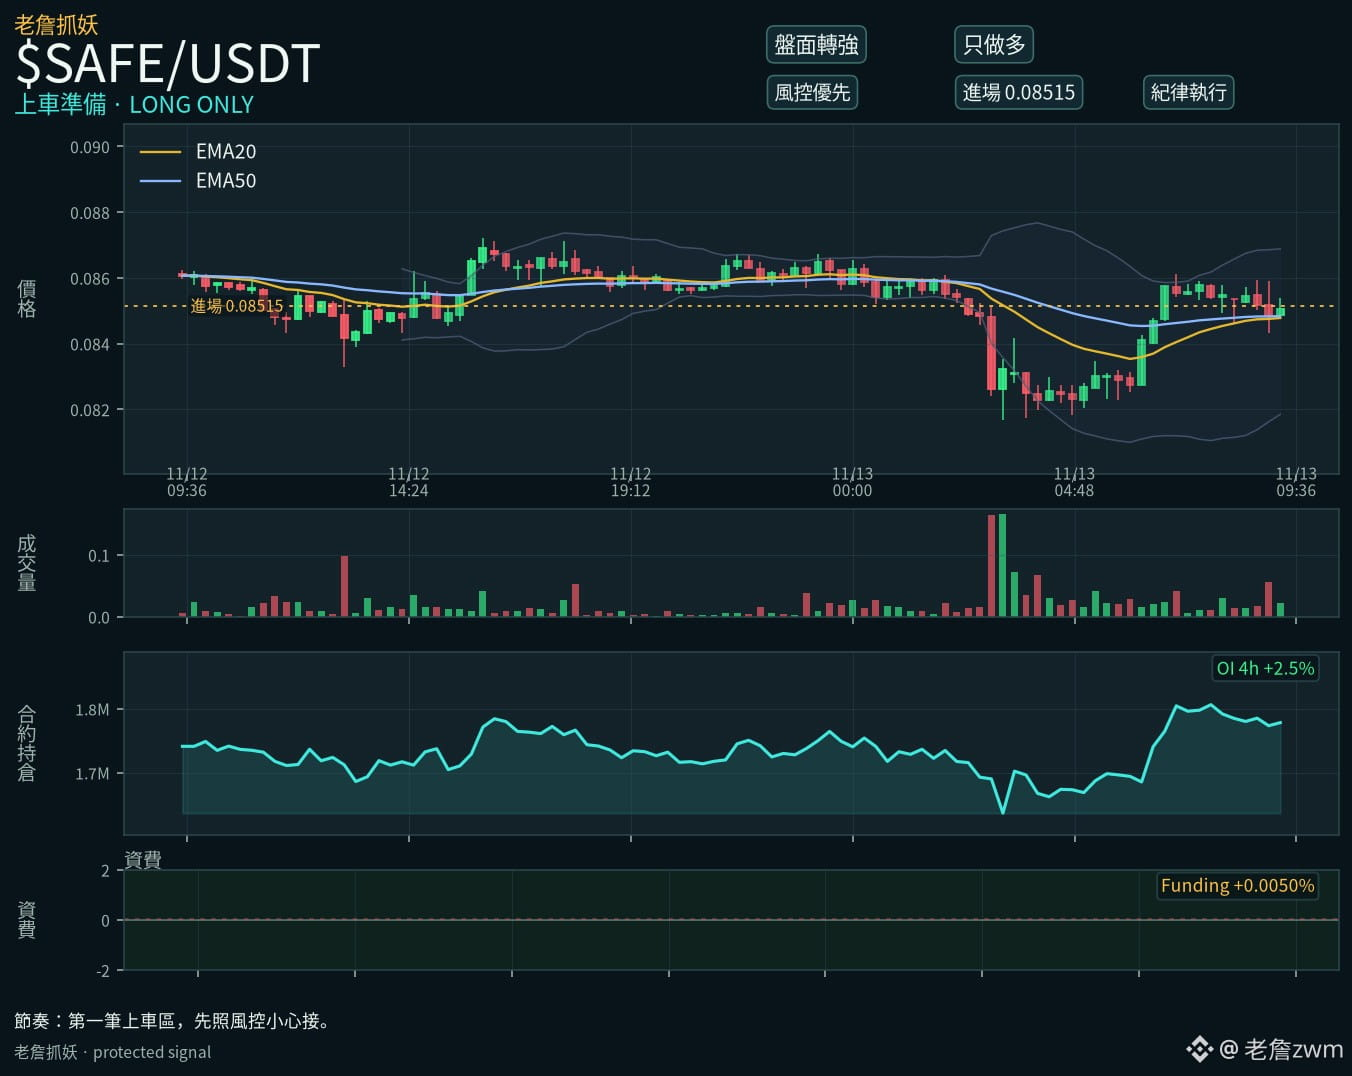
Good entry points often appear when nobody is paying attention.
$SAFE This looks interesting.
Buying pressure has been strong for 4 hours straight, and the price is just above the two-day low.
One thing to watch is that volume has been inconsistent.
Take a small position first, then wait for volume to pick up before deciding what to do next. Stop loss: 0.07238; first target: 0.09367. Take 30% off the table when it reaches the target.
#SAFE
Good entry points often appear when nobody is paying attention.
$SAFE This looks interesting.
Buying pressure has been strong for 4 hours straight, and the price is just above the two-day low.
One thing to watch is that volume has been inconsistent.
Take a small position first, then wait for volume to pick up before deciding what to do next. Stop loss: 0.07238; first target: 0.09367. Take 30% off the table when it reaches the target.
#SAFE
$SAFE This looks interesting.
Buying pressure has been strong for 4 hours straight, and the price is just above the two-day low.
One thing to watch is that volume has been inconsistent.
Take a small position first, then wait for volume to pick up before deciding what to do next. Stop loss: 0.07238; first target: 0.09367. Take 30% off the table when it reaches the target.
#SAFE
12

·
--
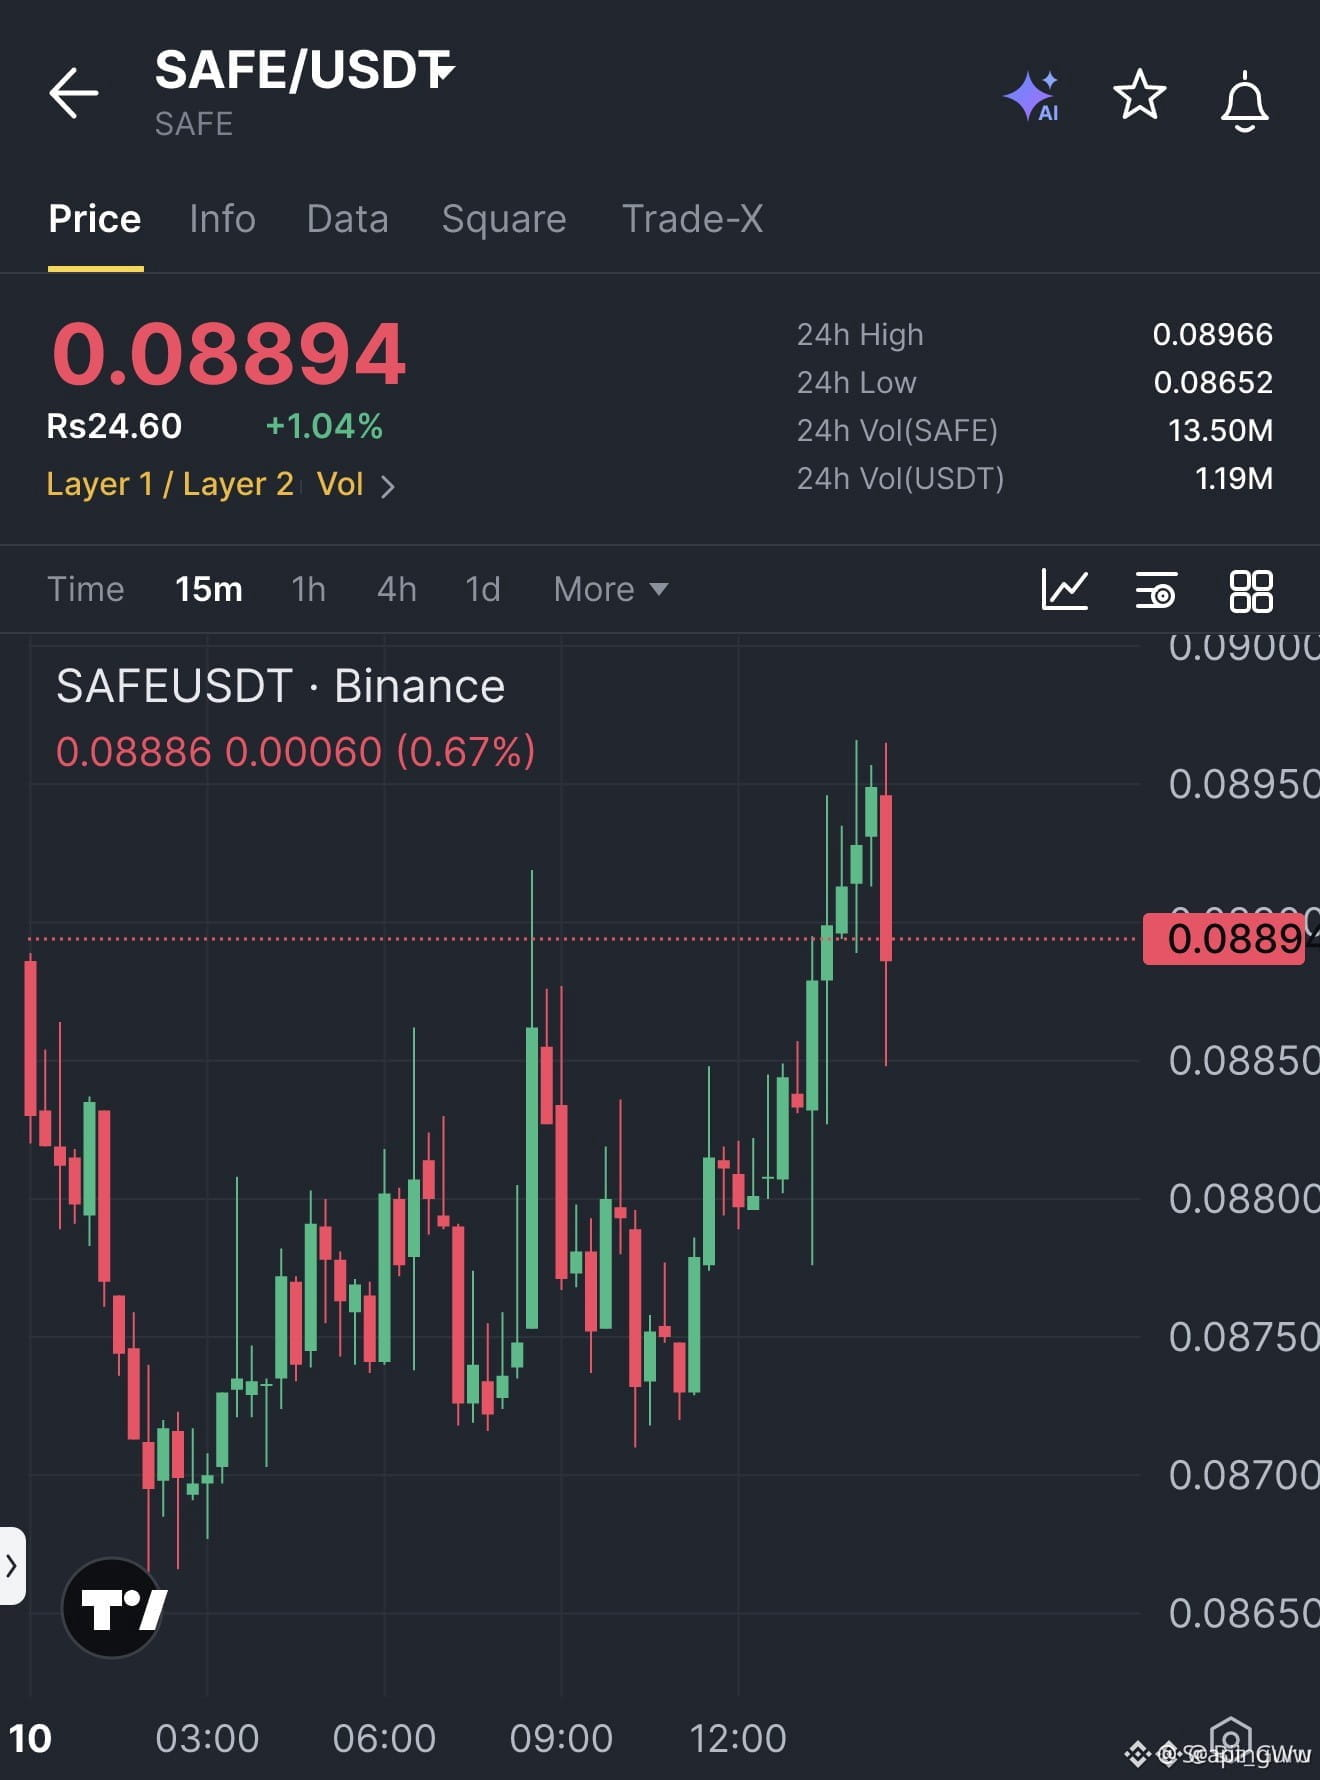
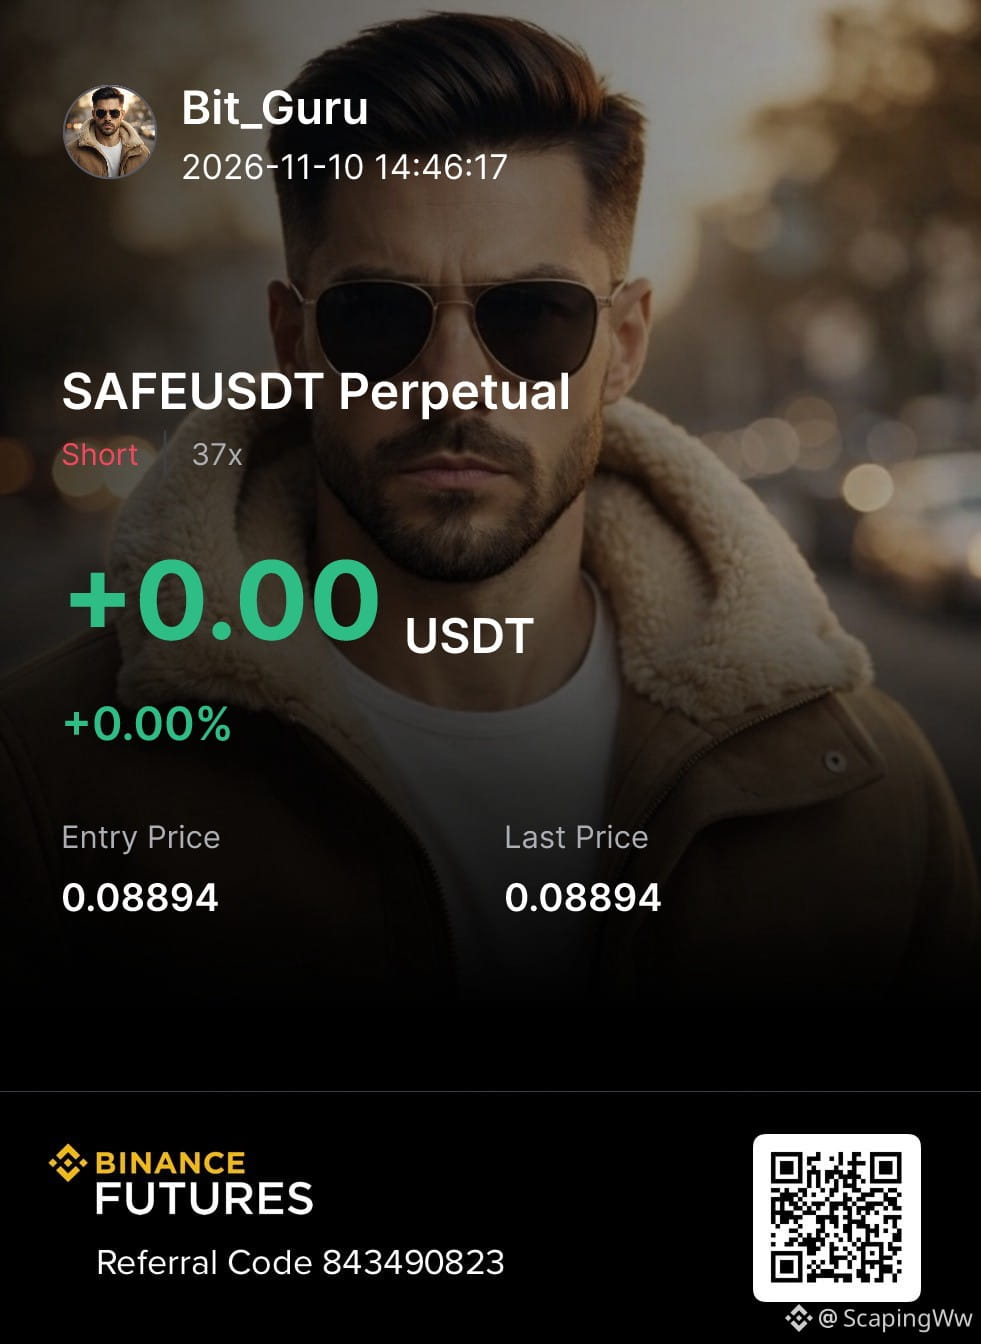
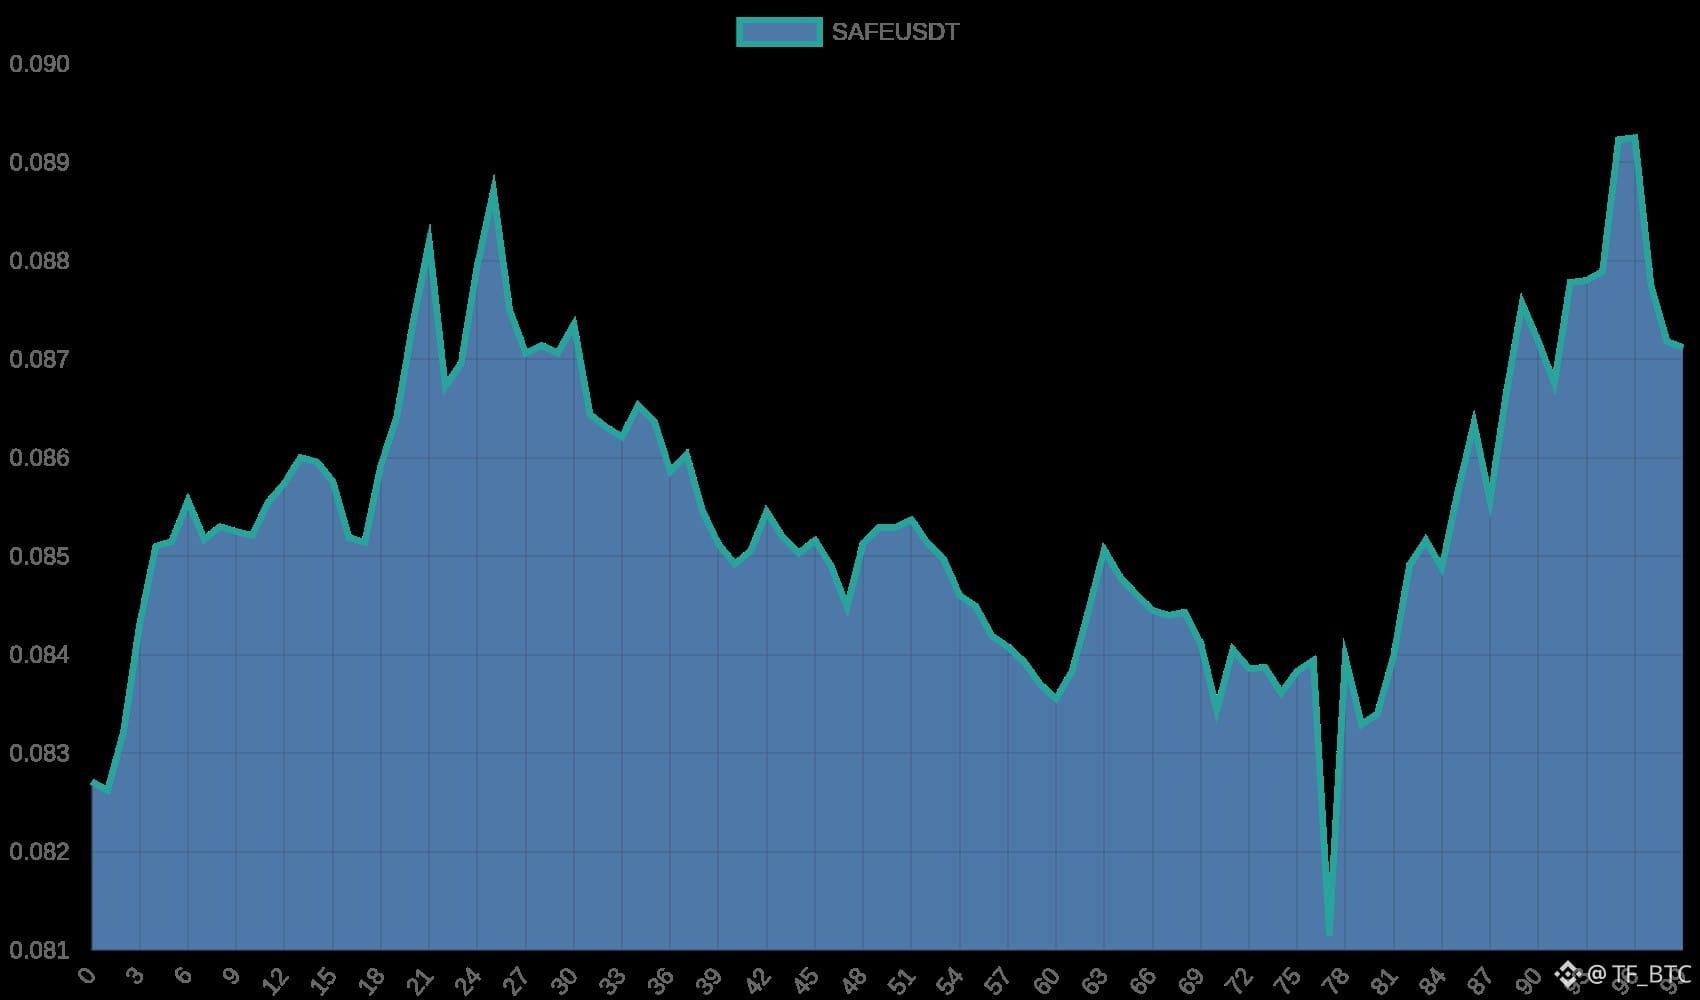
📉 $SAFE SELLERS CAPTURE CONTROL AFTER A SHARP EXHAUSTION RALLY! ⚡
Entry: 0.08894 ⚡
Target: 0.08578 🚀
Stop Loss: 0.08973 ⚠️
Exhaustion is finally creeping into the order books as buyers lose steam following a sustained vertical push. 📊 When previous candle lows fracture under heavy selling pressure, the shift in market structure opens a pristine window for downside continuation. ⚡
Execution requires strict discipline around our invalidation zone above the recent swing high. 📌 Are you fading this bounce or waiting for confirmation below the initial support level? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #PriceAction #Trading
📉 🦈
📉 $SAFE SELLERS CAPTURE CONTROL AFTER A SHARP EXHAUSTION RALLY! ⚡
Entry: 0.08894 ⚡
Target: 0.08578 🚀
Stop Loss: 0.08973 ⚠️
Exhaustion is finally creeping into the order books as buyers lose steam following a sustained vertical push. 📊 When previous candle lows fracture under heavy selling pressure, the shift in market structure opens a pristine window for downside continuation. ⚡
Execution requires strict discipline around our invalidation zone above the recent swing high. 📌 Are you fading this bounce or waiting for confirmation below the initial support level? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #PriceAction #Trading
📉 🦈
Entry: 0.08894 ⚡
Target: 0.08578 🚀
Stop Loss: 0.08973 ⚠️
Exhaustion is finally creeping into the order books as buyers lose steam following a sustained vertical push. 📊 When previous candle lows fracture under heavy selling pressure, the shift in market structure opens a pristine window for downside continuation. ⚡
Execution requires strict discipline around our invalidation zone above the recent swing high. 📌 Are you fading this bounce or waiting for confirmation below the initial support level? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #PriceAction #Trading
📉 🦈
13

·
--
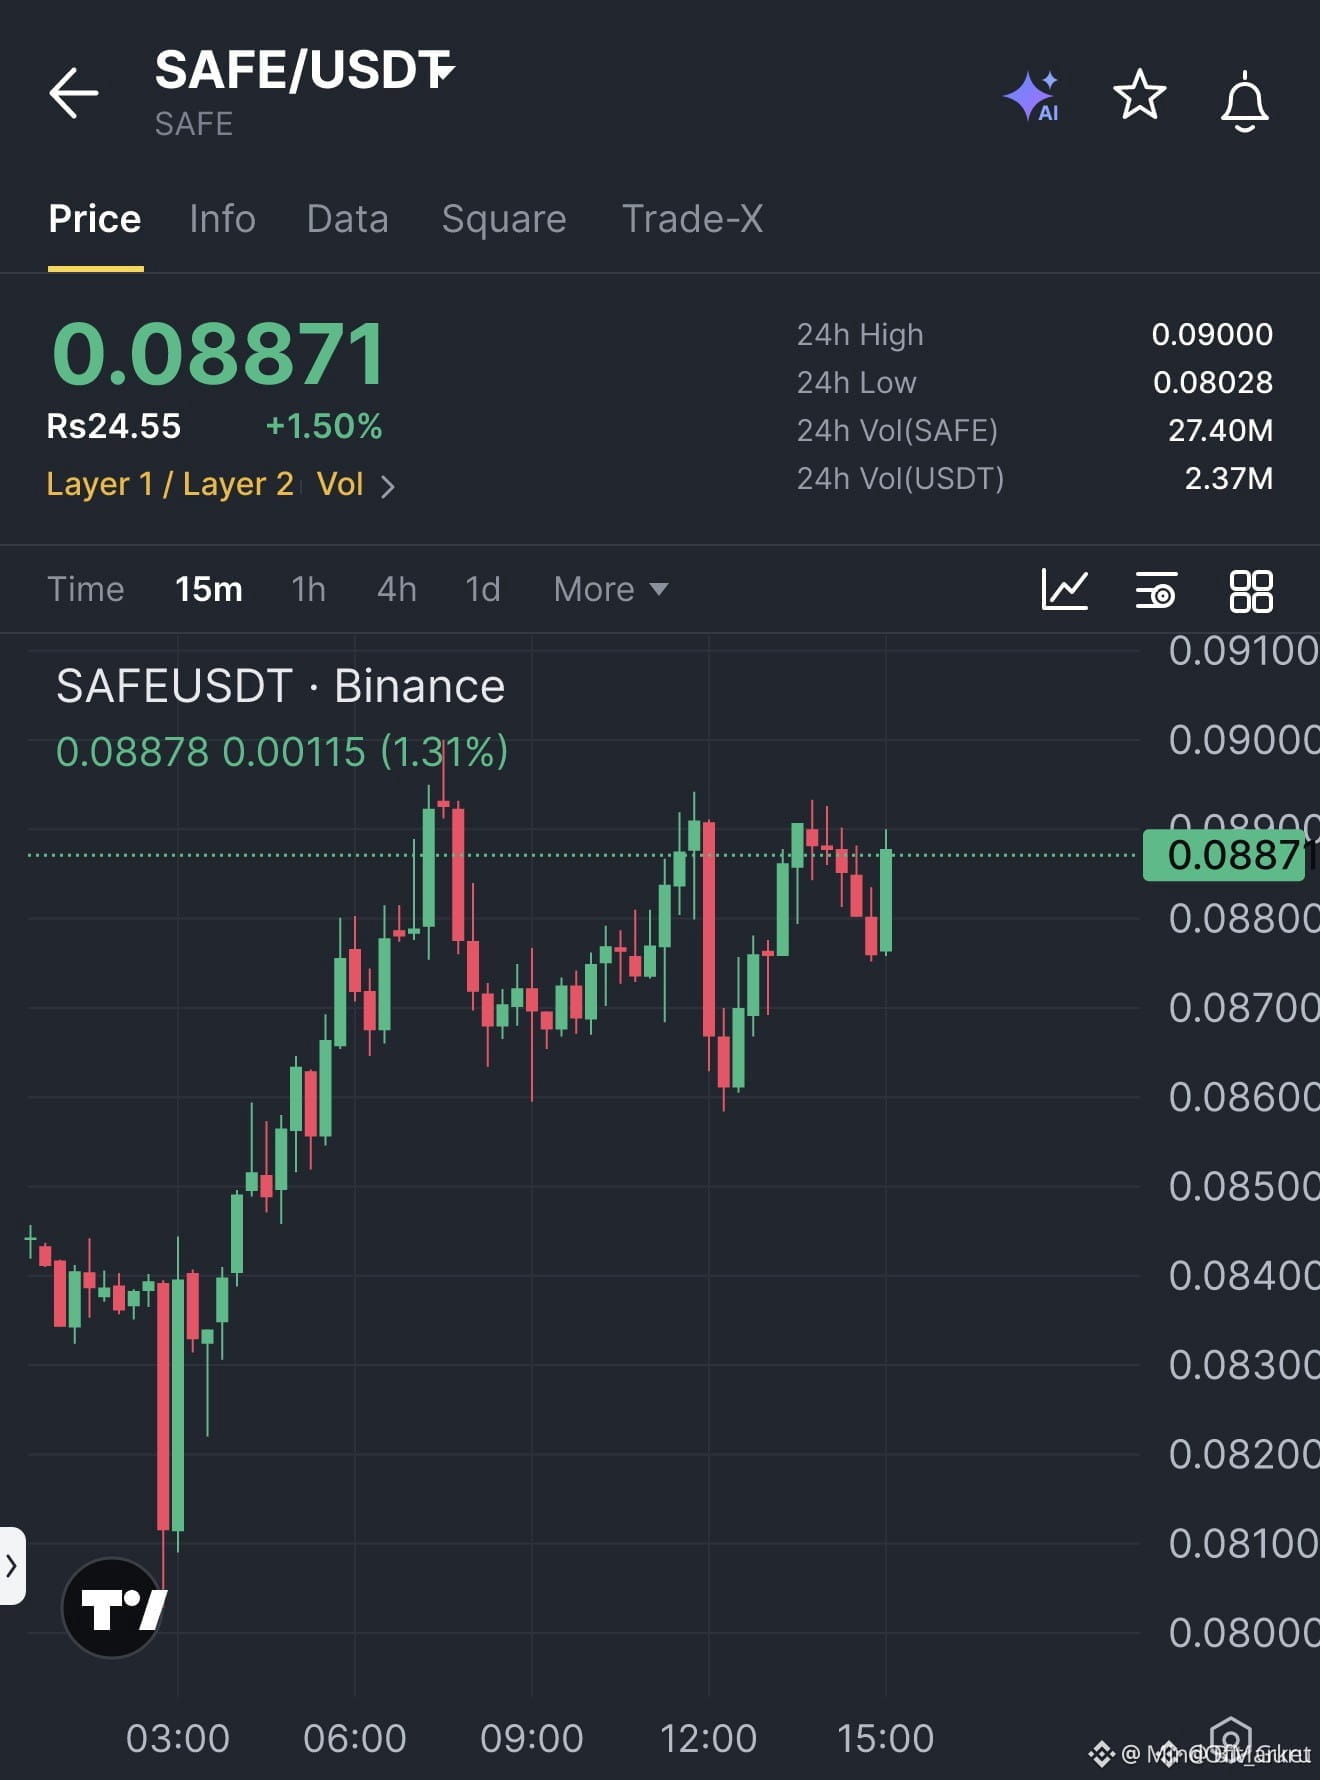
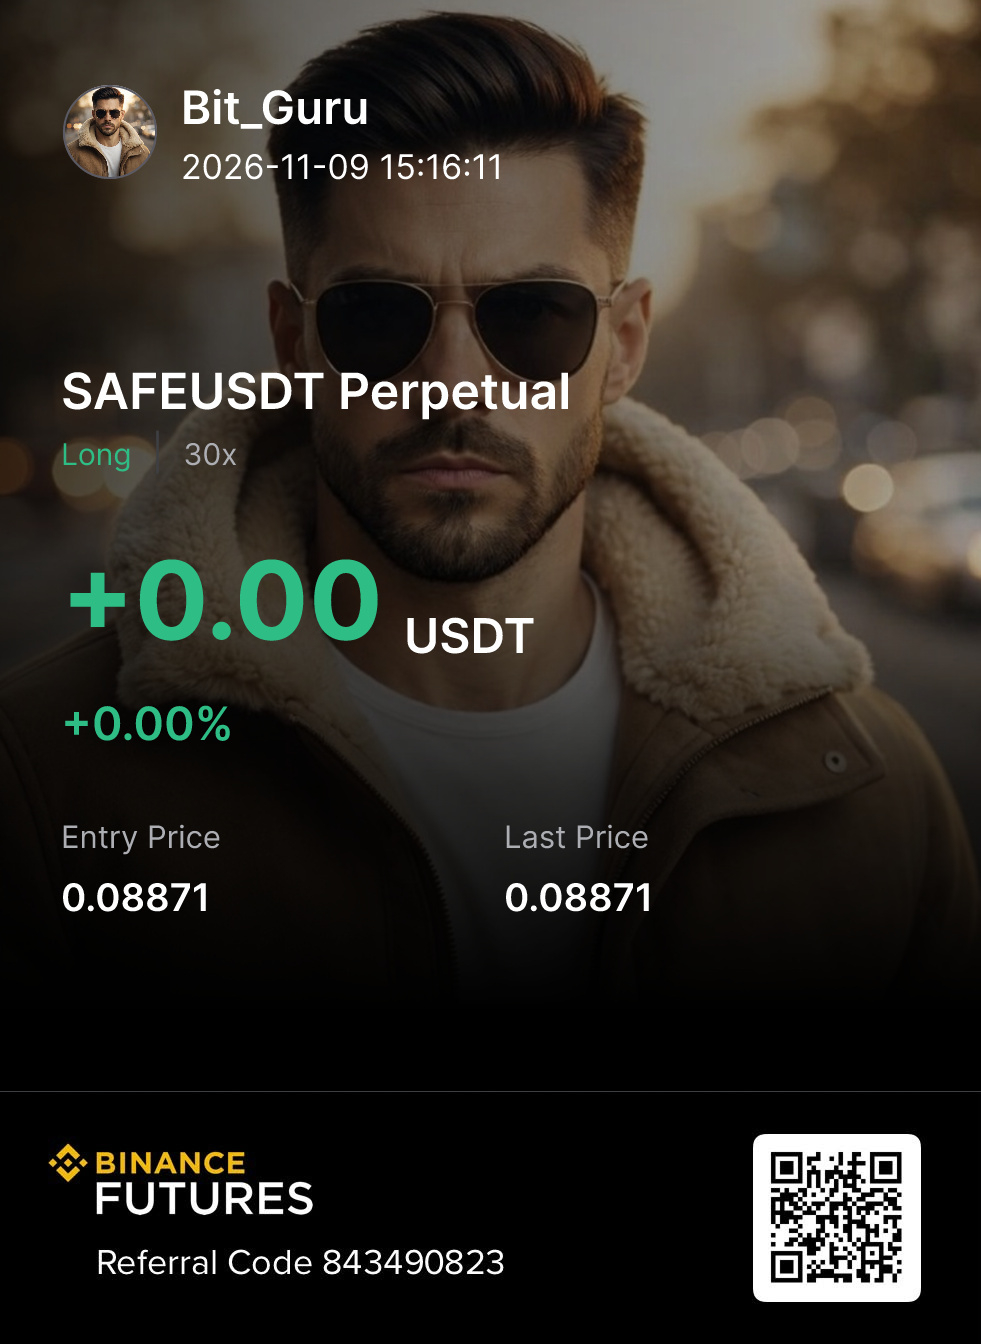
🦈 $SAFE SWEEPING LIQUIDITY AS SMART MONEY RECLAIMS KEY STRUCTURAL HIGHS! ⚡
Entry: 0.08871 ⚡
Target: 0.09068, 0.09199, 0.09395 🚀
Stop Loss: 0.0874 ⚠️
Institutional order flow is shifting as smart money aggressively absorbs supply following a sustained structural markdown across the order book. 📊 The sharp impulse break above the previous candle high confirms a clean liquidity sweep and a high-probability recovery trigger. 💡
Risk parameters are tightly defined below key institutional invalidation levels to protect capital while targeting sequential upper liquidity pools. 📌 Are you executing this structural reclaim now or waiting for a confirmation retest? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #SmartMoney #LongSetup #OrderBlock #Crypto
🦈 💎
🦈 $SAFE SWEEPING LIQUIDITY AS SMART MONEY RECLAIMS KEY STRUCTURAL HIGHS! ⚡
Entry: 0.08871 ⚡
Target: 0.09068, 0.09199, 0.09395 🚀
Stop Loss: 0.0874 ⚠️
Institutional order flow is shifting as smart money aggressively absorbs supply following a sustained structural markdown across the order book. 📊 The sharp impulse break above the previous candle high confirms a clean liquidity sweep and a high-probability recovery trigger. 💡
Risk parameters are tightly defined below key institutional invalidation levels to protect capital while targeting sequential upper liquidity pools. 📌 Are you executing this structural reclaim now or waiting for a confirmation retest? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #SmartMoney #LongSetup #OrderBlock #Crypto
🦈 💎
Entry: 0.08871 ⚡
Target: 0.09068, 0.09199, 0.09395 🚀
Stop Loss: 0.0874 ⚠️
Institutional order flow is shifting as smart money aggressively absorbs supply following a sustained structural markdown across the order book. 📊 The sharp impulse break above the previous candle high confirms a clean liquidity sweep and a high-probability recovery trigger. 💡
Risk parameters are tightly defined below key institutional invalidation levels to protect capital while targeting sequential upper liquidity pools. 📌 Are you executing this structural reclaim now or waiting for a confirmation retest? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #SmartMoney #LongSetup #OrderBlock #Crypto
🦈 💎
7

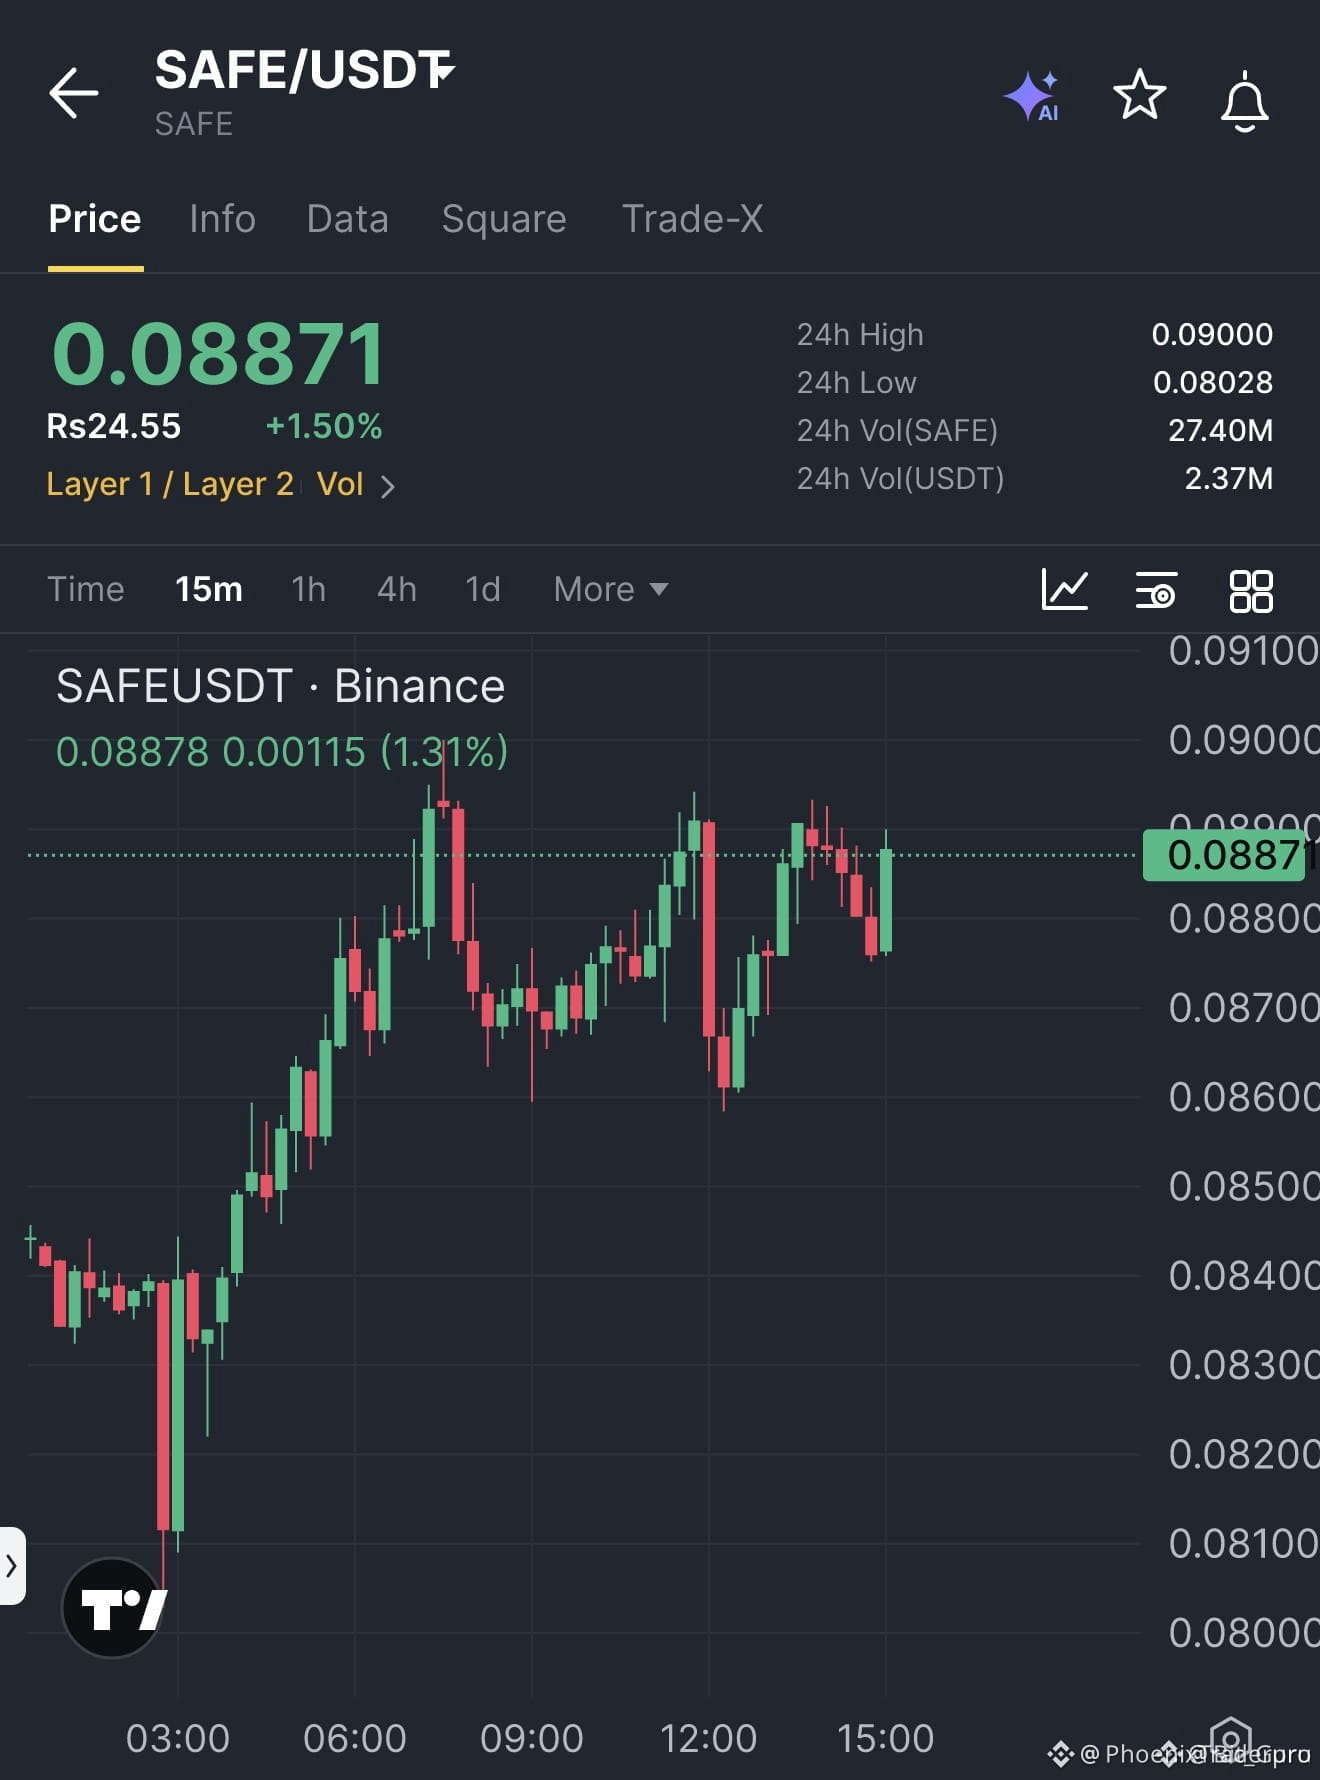
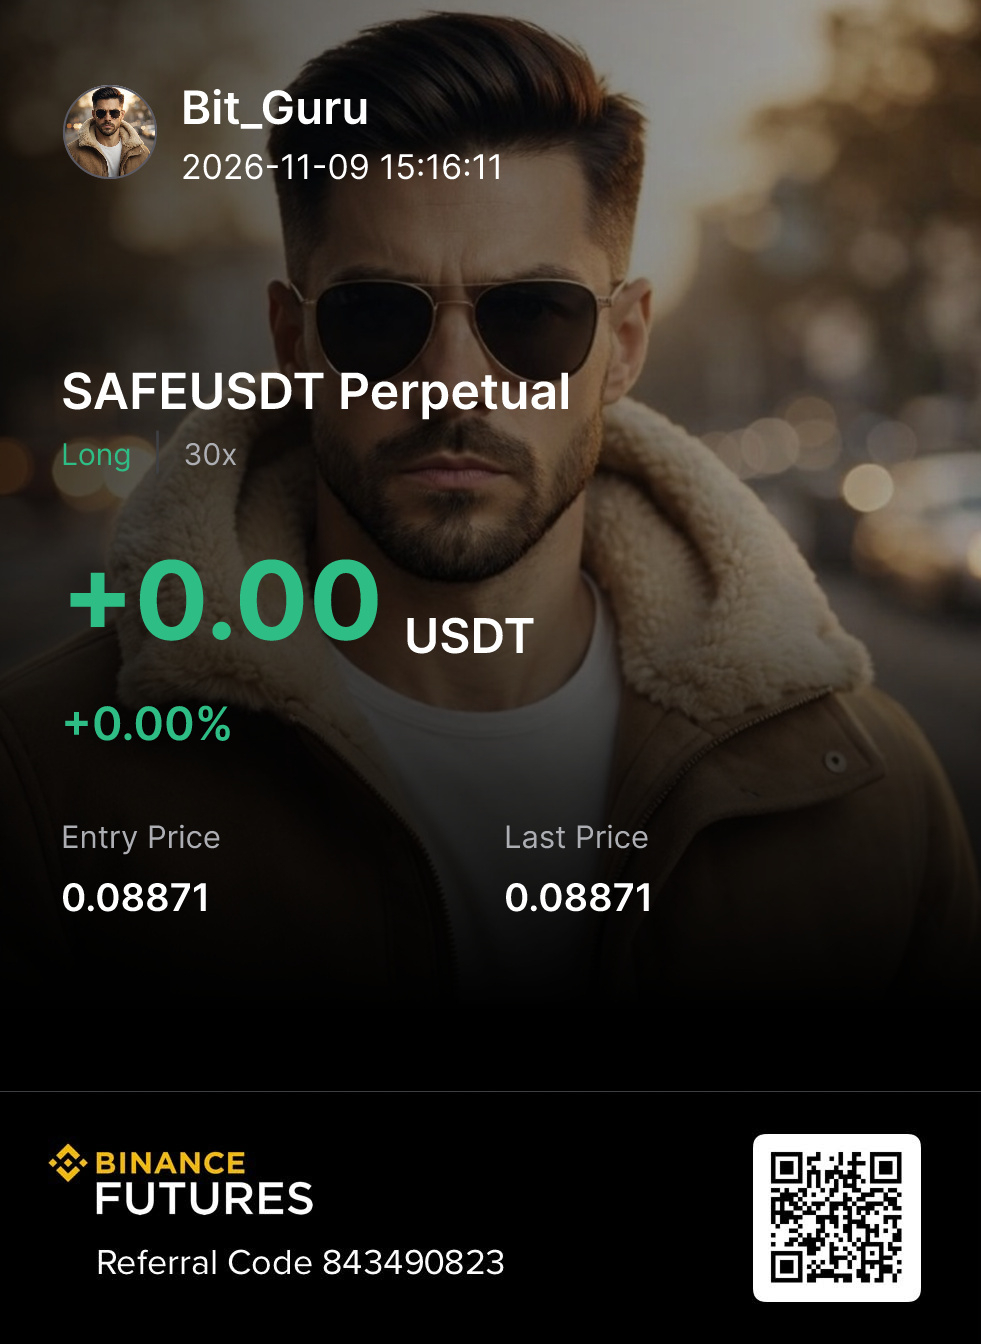
🚨 $SAFE BUYERS SHATTER RESISTANCE AFTER A BRUTAL FLUSH DOWN! 💥
Entry: 0.08871 ⚡
Target 1: 0.09068 🚀
Target 2: 0.09199 🎯
Target 3: 0.09395 💥
Stop Loss: 0.0874 ⚠️
Sellers exhausted themselves driving $SAFE down into a deep liquidity pocket, only for aggressive bids to sweep in and reclaim previous candle highs. This sudden structural shift confirms the recovery playbook is live as order flow flips in favor of the bulls.
Volume is ticking up across the board as momentum buyers step in to defend the breakout 📊 ⚡ 💬 Are you locking in early entries or waiting for confirmation near the upper targets? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #LongSetup #Crypto #Breakout
🔥 💎
🚨 $SAFE BUYERS SHATTER RESISTANCE AFTER A BRUTAL FLUSH DOWN! 💥
Entry: 0.08871 ⚡
Target 1: 0.09068 🚀
Target 2: 0.09199 🎯
Target 3: 0.09395 💥
Stop Loss: 0.0874 ⚠️
Sellers exhausted themselves driving $SAFE down into a deep liquidity pocket, only for aggressive bids to sweep in and reclaim previous candle highs. This sudden structural shift confirms the recovery playbook is live as order flow flips in favor of the bulls.
Volume is ticking up across the board as momentum buyers step in to defend the breakout 📊 ⚡ 💬 Are you locking in early entries or waiting for confirmation near the upper targets? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #LongSetup #Crypto #Breakout
🔥 💎
Entry: 0.08871 ⚡
Target 1: 0.09068 🚀
Target 2: 0.09199 🎯
Target 3: 0.09395 💥
Stop Loss: 0.0874 ⚠️
Sellers exhausted themselves driving $SAFE down into a deep liquidity pocket, only for aggressive bids to sweep in and reclaim previous candle highs. This sudden structural shift confirms the recovery playbook is live as order flow flips in favor of the bulls.
Volume is ticking up across the board as momentum buyers step in to defend the breakout 📊 ⚡ 💬 Are you locking in early entries or waiting for confirmation near the upper targets? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #LongSetup #Crypto #Breakout
🔥 💎
6
·
--
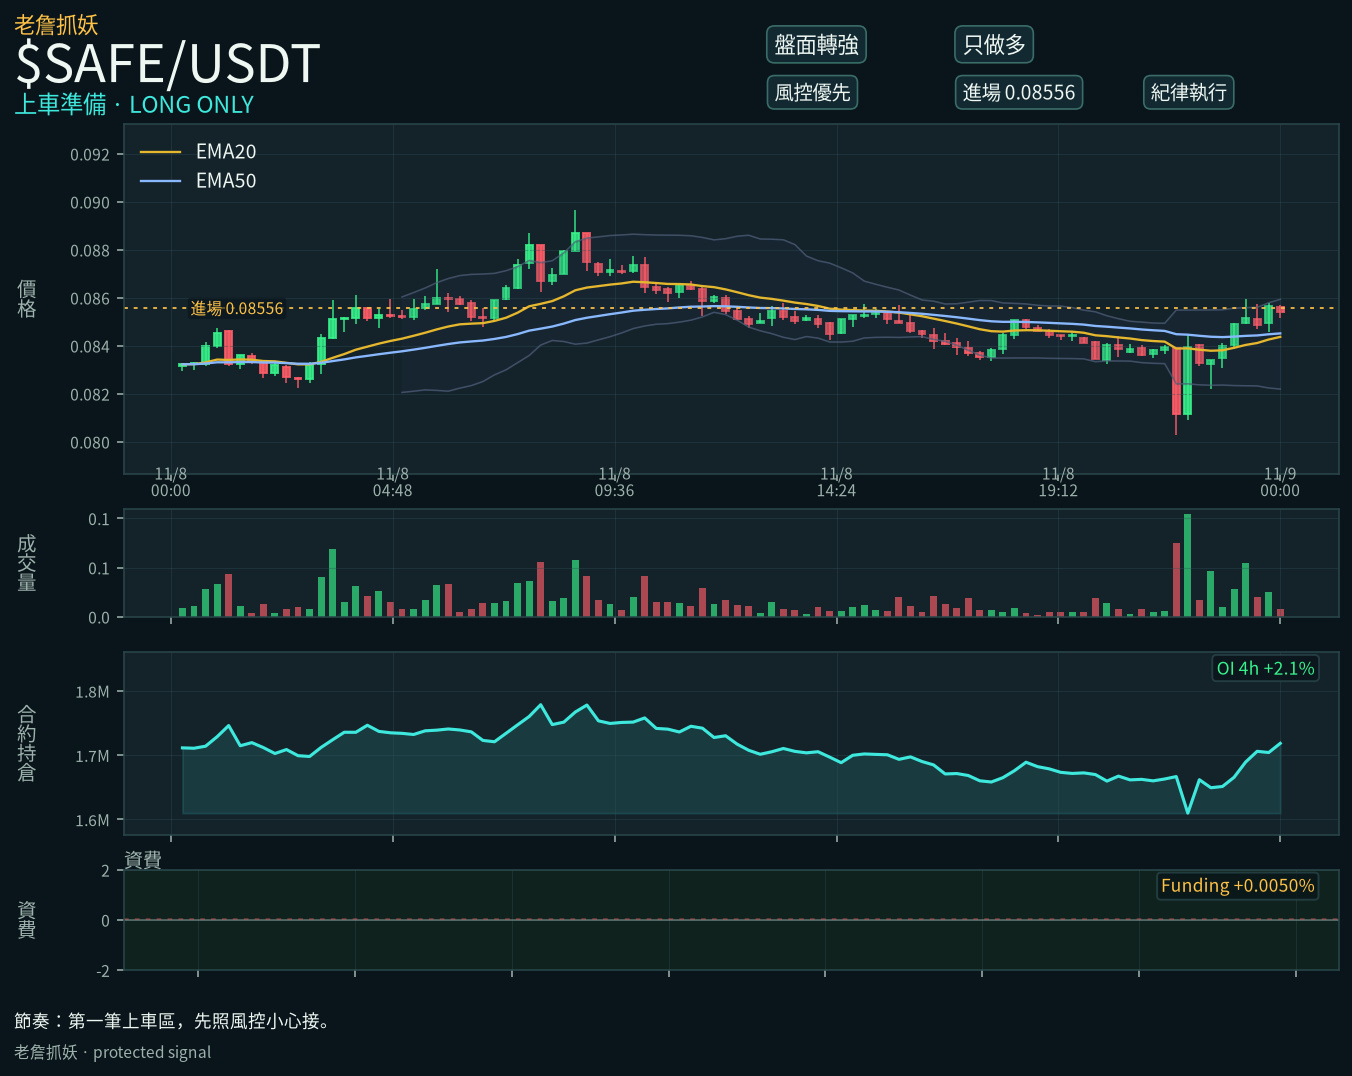
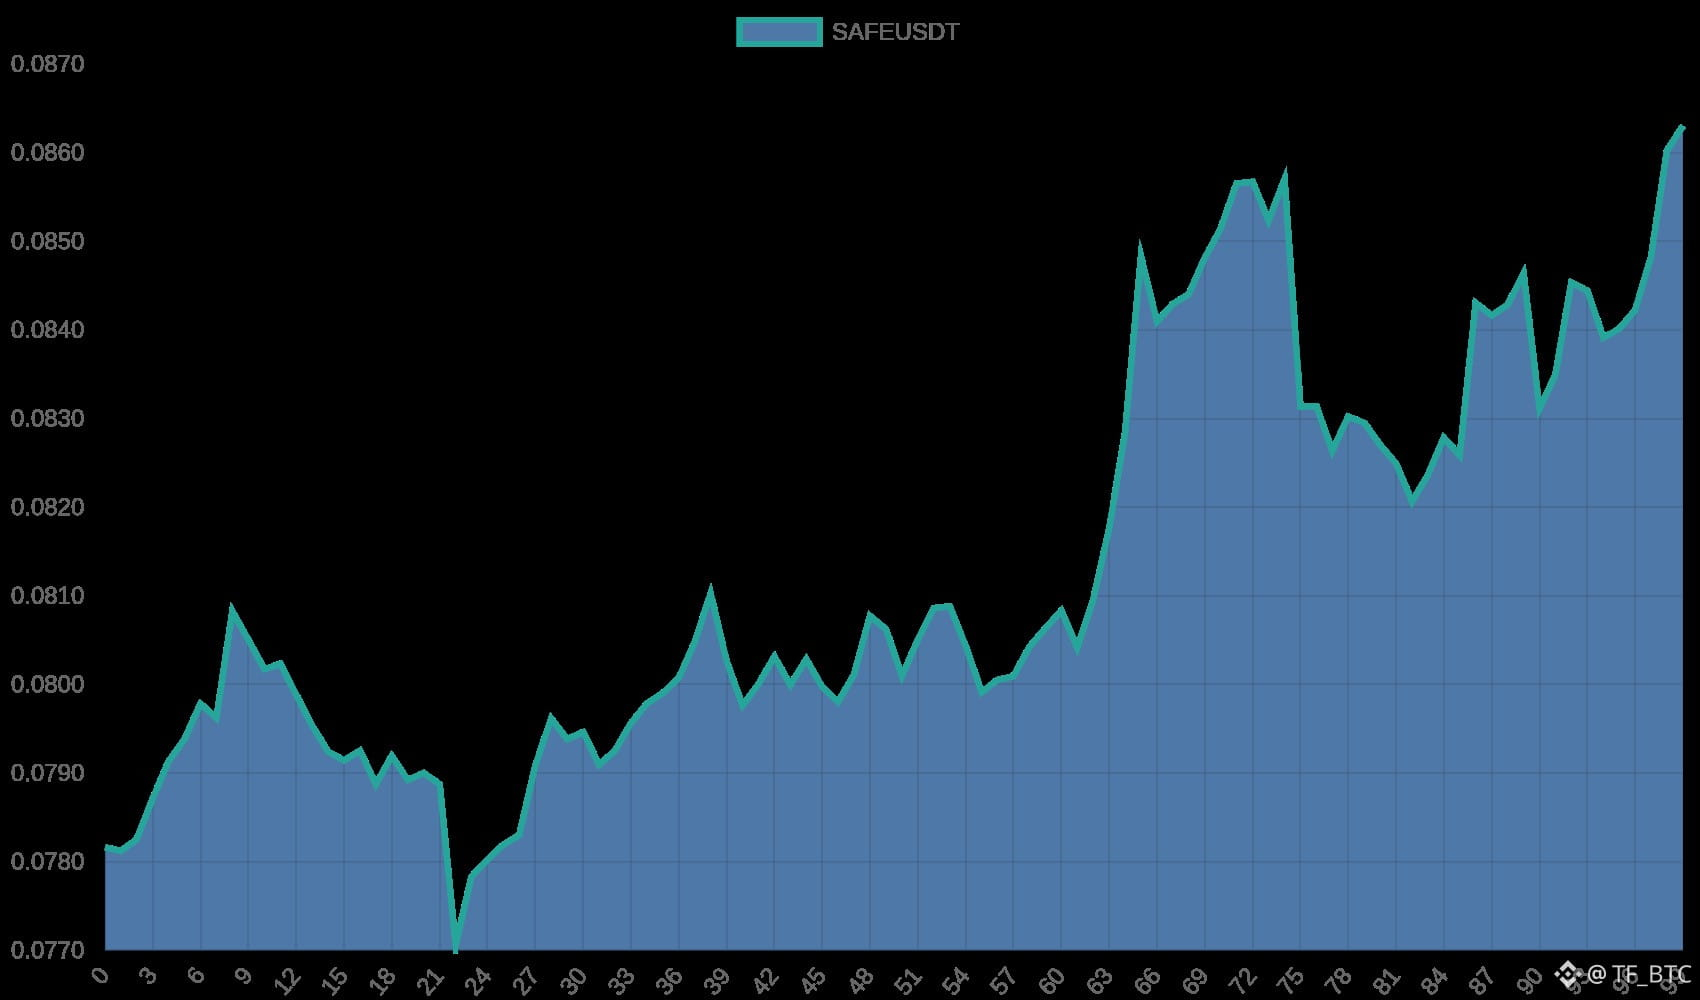
Plan your stop-loss first, then think about how much you can make
$SAFE People have started positioning early
New funds have come into the futures market within the past hour
The broader market hasn't stabilized yet, and trading volume is still a bit uneven
Cut your position in half, set the stop-loss at 0.07273, and take profit on 30% at 0.09412 first
#SAFE #wildcoin
Plan your stop-loss first, then think about how much you can make
$SAFE People have started positioning early
New funds have come into the futures market within the past hour
The broader market hasn't stabilized yet, and trading volume is still a bit uneven
Cut your position in half, set the stop-loss at 0.07273, and take profit on 30% at 0.09412 first
#SAFE #wildcoin
$SAFE People have started positioning early
New funds have come into the futures market within the past hour
The broader market hasn't stabilized yet, and trading volume is still a bit uneven
Cut your position in half, set the stop-loss at 0.07273, and take profit on 30% at 0.09412 first
#SAFE #wildcoin
89
·
--
🛡️ SECURITY AND IDENTITY MATTER IN WEB3!
$SAFE is connected to smart account and multisignature wallet infrastructure.
$MASK focuses on bringing Web3 features to social platforms.
$CYBER supports a social-focused Web3 ecosystem.
Adoption and practical utility are the metrics worth following.
#Safe #MaskNetwork #CyberConnect #Web3Social #CryptoUtility
🛡️ SECURITY AND IDENTITY MATTER IN WEB3!
$SAFE is connected to smart account and multisignature wallet infrastructure.
$MASK focuses on bringing Web3 features to social platforms.
$CYBER supports a social-focused Web3 ecosystem.
Adoption and practical utility are the metrics worth following.
#Safe #MaskNetwork #CyberConnect #Web3Social #CryptoUtility
$SAFE is connected to smart account and multisignature wallet infrastructure.
$MASK focuses on bringing Web3 features to social platforms.
$CYBER supports a social-focused Web3 ecosystem.
Adoption and practical utility are the metrics worth following.
#Safe #MaskNetwork #CyberConnect #Web3Social #CryptoUtility
1
28

·
--
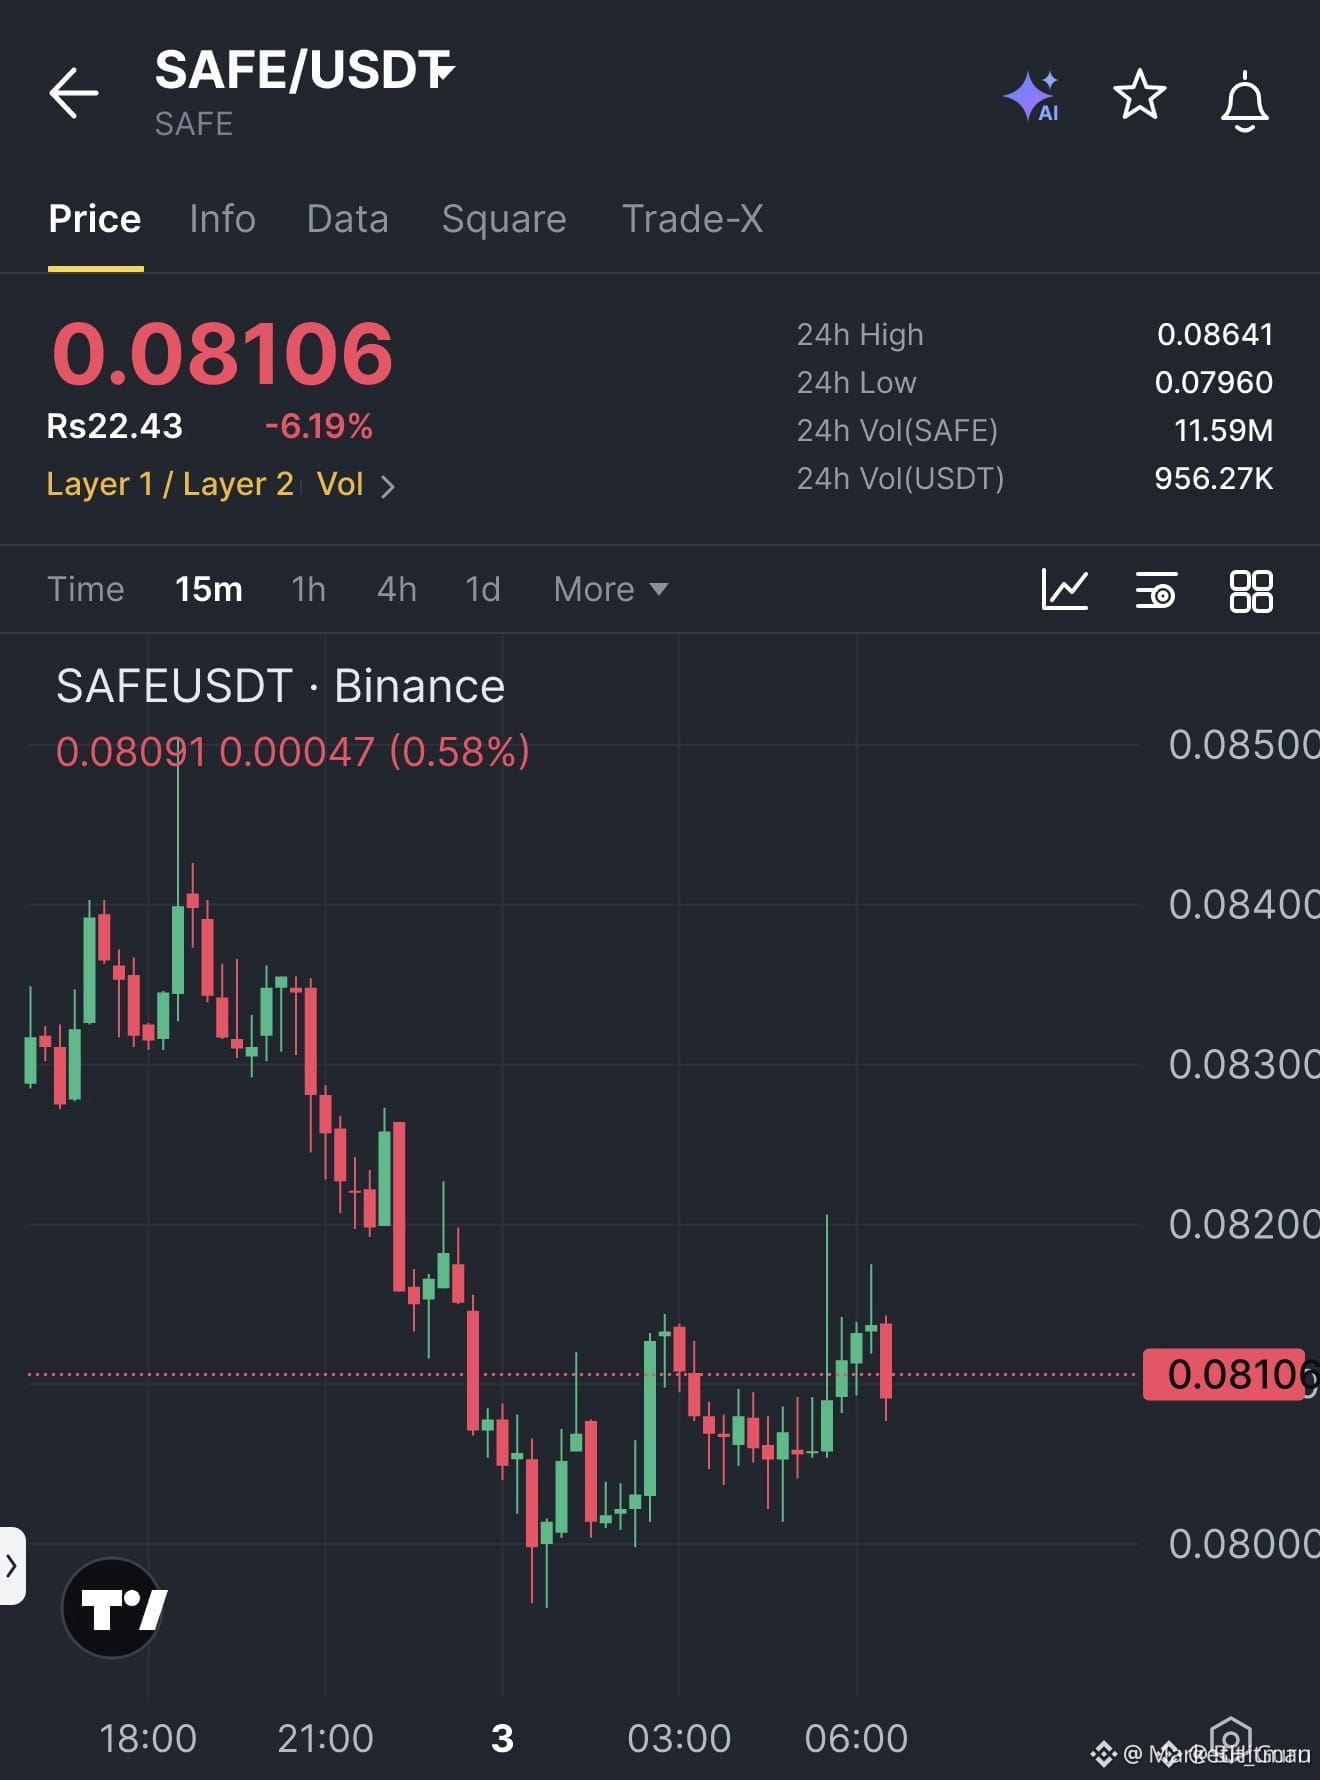
🔴 $SAFE SHORT SETUP FIRES WITH QUICK PULLBACK POTENTIAL! 🚀
Entry: 0.08106 ⚡
Stop Loss: 0.08181 ⚠️
Target: 0.07993, 0.07918, 0.07806 🚀
📊 Sellers just ripped the low of the previous candle after a hard‑fought rally, flipping the market into a clean short bias. The order flow shows a fresh liquidity sweep, with smart‑money whales swallowing the last sliver of buy pressure 🦈.
⚡ Entry sits at 0.08106, stop just above the broken low at 0.08181, and a tiered target ladder down to 0.07806 📌. Volume spikes on the 1‑hour chart confirm the momentum shift, while RSI drifts into oversold, signaling more downside potential.
💬 Are you ready to ride this pullback or waiting for a deeper dip? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #LiquiditySweep
🔥 💎
🔴 $SAFE SHORT SETUP FIRES WITH QUICK PULLBACK POTENTIAL! 🚀
Entry: 0.08106 ⚡
Stop Loss: 0.08181 ⚠️
Target: 0.07993, 0.07918, 0.07806 🚀
📊 Sellers just ripped the low of the previous candle after a hard‑fought rally, flipping the market into a clean short bias. The order flow shows a fresh liquidity sweep, with smart‑money whales swallowing the last sliver of buy pressure 🦈.
⚡ Entry sits at 0.08106, stop just above the broken low at 0.08181, and a tiered target ladder down to 0.07806 📌. Volume spikes on the 1‑hour chart confirm the momentum shift, while RSI drifts into oversold, signaling more downside potential.
💬 Are you ready to ride this pullback or waiting for a deeper dip? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #LiquiditySweep
🔥 💎
Entry: 0.08106 ⚡
Stop Loss: 0.08181 ⚠️
Target: 0.07993, 0.07918, 0.07806 🚀
📊 Sellers just ripped the low of the previous candle after a hard‑fought rally, flipping the market into a clean short bias. The order flow shows a fresh liquidity sweep, with smart‑money whales swallowing the last sliver of buy pressure 🦈.
⚡ Entry sits at 0.08106, stop just above the broken low at 0.08181, and a tiered target ladder down to 0.07806 📌. Volume spikes on the 1‑hour chart confirm the momentum shift, while RSI drifts into oversold, signaling more downside potential.
💬 Are you ready to ride this pullback or waiting for a deeper dip? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #LiquiditySweep
🔥 💎
10

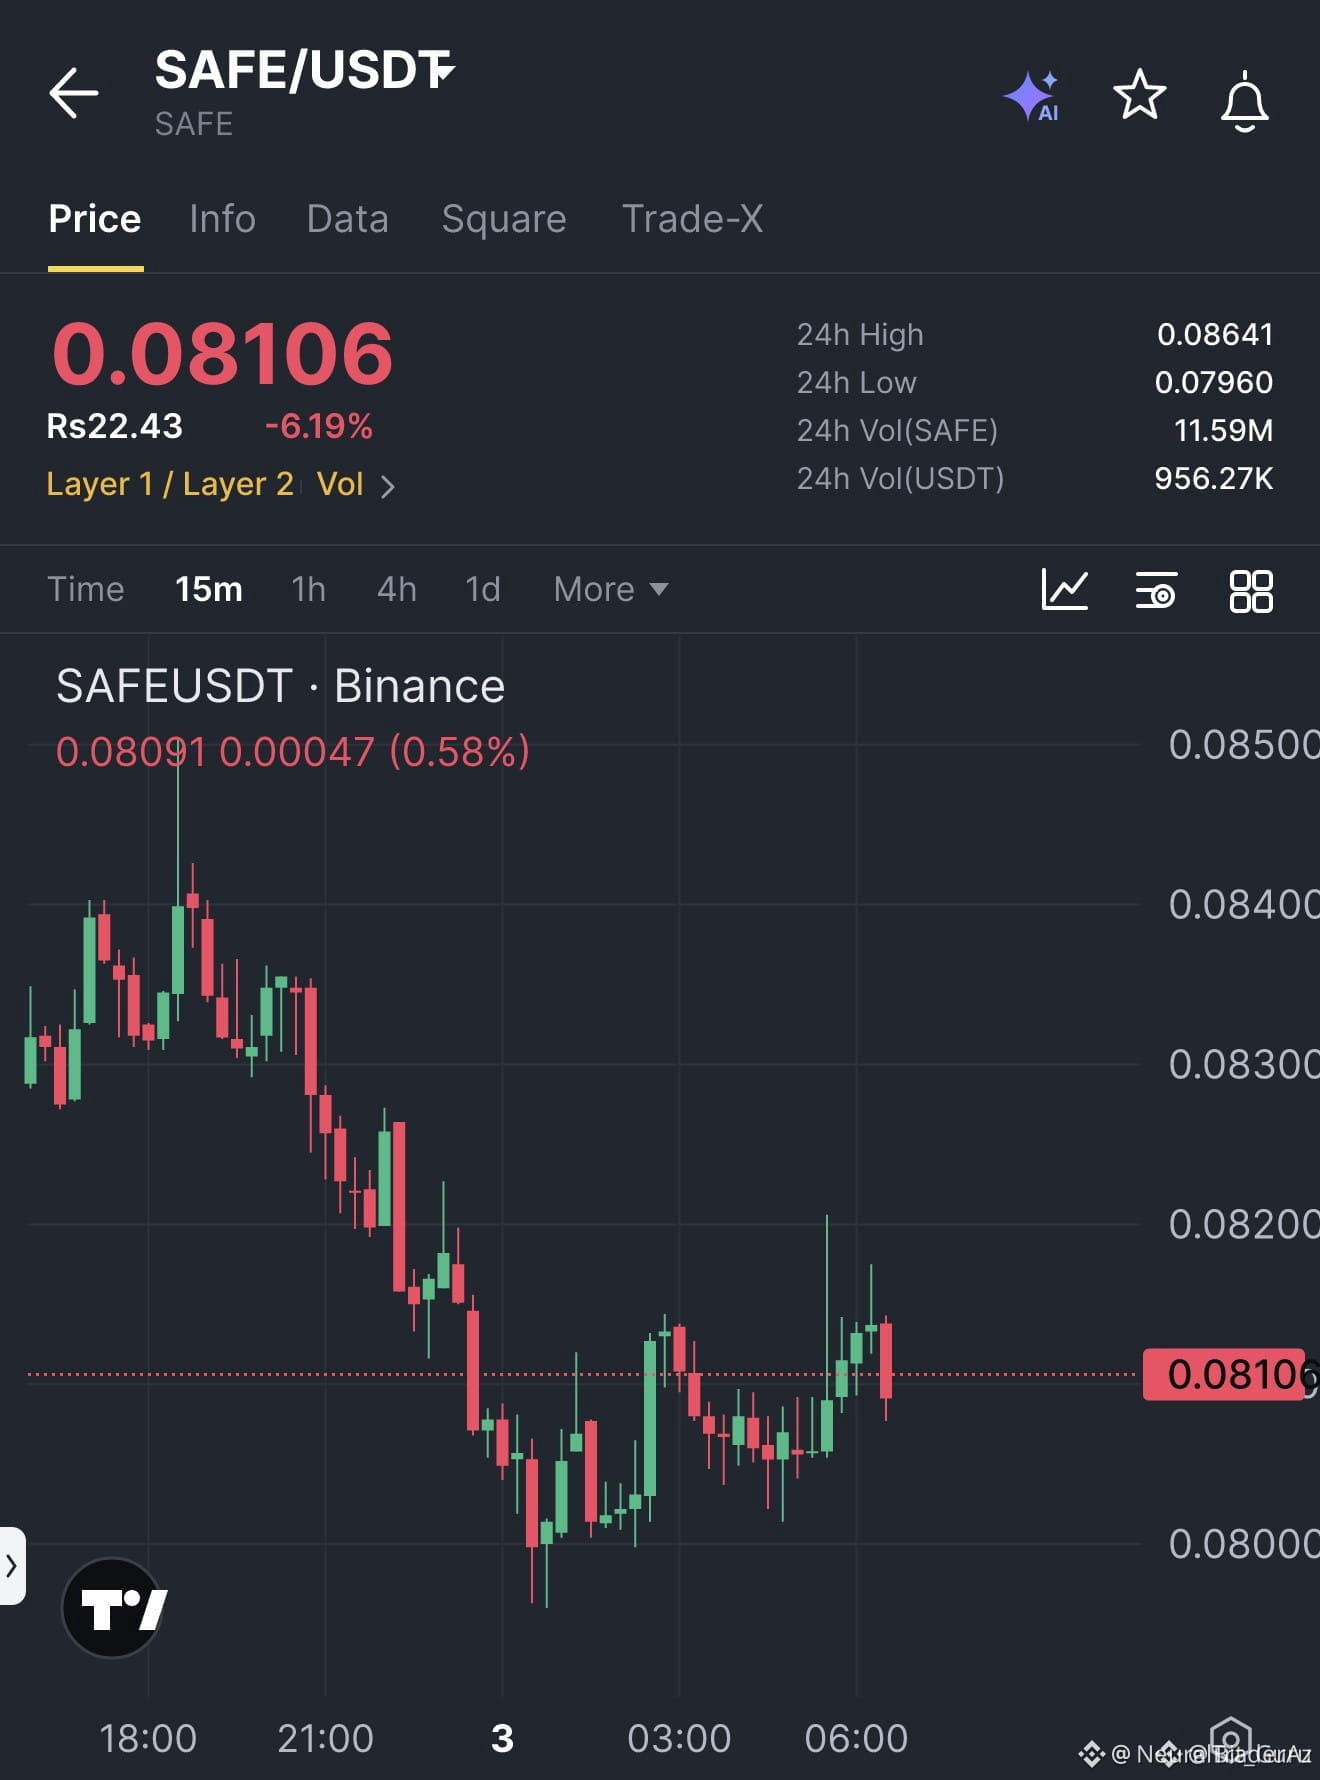
🔴🦈 $SAFE BEARISH LIQUIDITY SWEEP SET TO CRUSH ABOVE 0.08181!
Entry: 0.08106 ⚡
Target: 0.07993 🎯
Target: 0.07918 🎯
Target: 0.07806 🎯
Stop Loss: 0.08181 ⚠️
📊 Sellers shattered the prior candle low after a prolonged rise, exposing a fresh demand zone. 🦈 The breakout triggered a classic liquidity hunt, forcing the market into a controlled pull‑back. 📌 With order flow now aligning under the broken low, the short bias gains institutional backing and volume confirmation on the 4H.
💡 Risk‑to‑reward stacks neatly across three tiers, letting you scale out as price respects each liquidity pocket. 💬 Are you ready to short $SAFE on this liquidity bite? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #LiquiditySweep #Crypto
🦈 🔥
🔴🦈 $SAFE BEARISH LIQUIDITY SWEEP SET TO CRUSH ABOVE 0.08181!
Entry: 0.08106 ⚡
Target: 0.07993 🎯
Target: 0.07918 🎯
Target: 0.07806 🎯
Stop Loss: 0.08181 ⚠️
📊 Sellers shattered the prior candle low after a prolonged rise, exposing a fresh demand zone. 🦈 The breakout triggered a classic liquidity hunt, forcing the market into a controlled pull‑back. 📌 With order flow now aligning under the broken low, the short bias gains institutional backing and volume confirmation on the 4H.
💡 Risk‑to‑reward stacks neatly across three tiers, letting you scale out as price respects each liquidity pocket. 💬 Are you ready to short $SAFE on this liquidity bite? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #LiquiditySweep #Crypto
🦈 🔥
Entry: 0.08106 ⚡
Target: 0.07993 🎯
Target: 0.07918 🎯
Target: 0.07806 🎯
Stop Loss: 0.08181 ⚠️
📊 Sellers shattered the prior candle low after a prolonged rise, exposing a fresh demand zone. 🦈 The breakout triggered a classic liquidity hunt, forcing the market into a controlled pull‑back. 📌 With order flow now aligning under the broken low, the short bias gains institutional backing and volume confirmation on the 4H.
💡 Risk‑to‑reward stacks neatly across three tiers, letting you scale out as price respects each liquidity pocket. 💬 Are you ready to short $SAFE on this liquidity bite? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #LiquiditySweep #Crypto
🦈 🔥
5
·
--
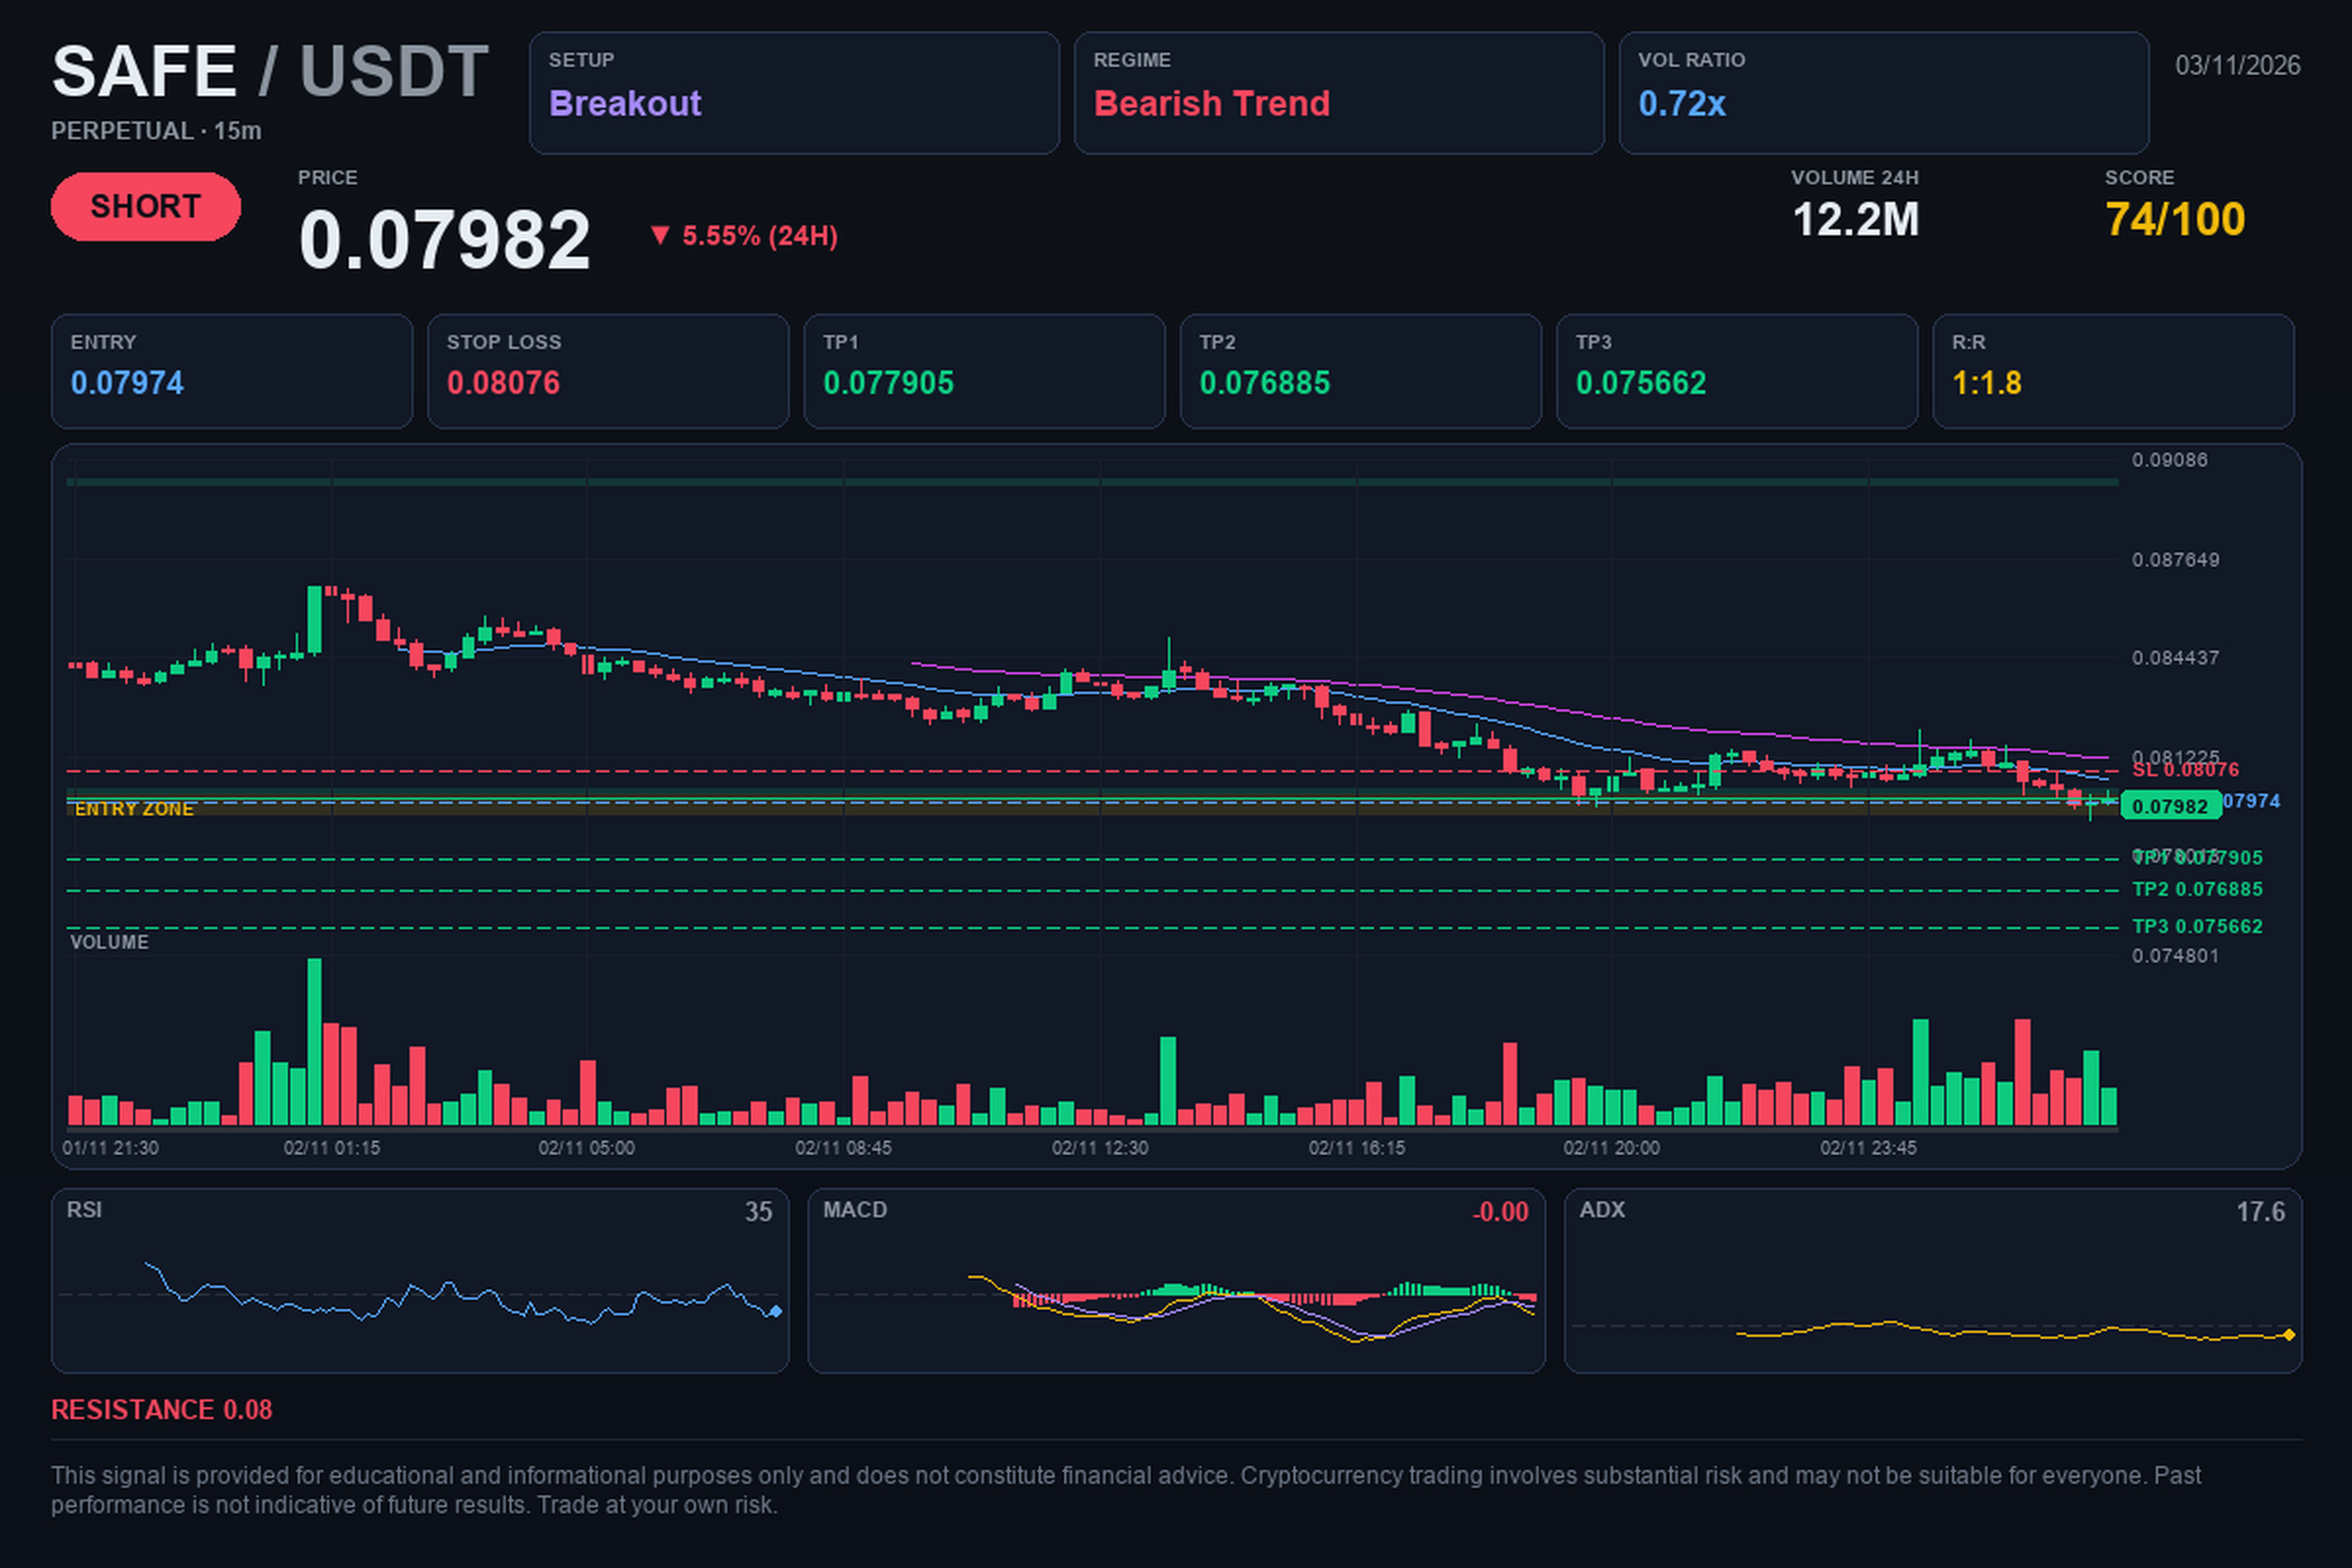
📢 $SAFE / USDT | 🔴 SHORT | ⭐ 74%
🎯 Target: $0.0779048. Will it reach it?
🎯 Trading levels:
🔴 Entry: $0.07974
🛑 Stop Loss: $0.08076
🏁 TP1: $0.077905
🏁 TP2: $0.076885
🏁 TP3: $0.075662
📈 Analysis:
The market shows a clear bearish structure, with confirmed support breaks across multiple timeframes. Selling pressure is supported by a significant increase in trading volume, which is above average, while the relative strength indicator remains at weak levels. This combination of factors suggests that sellers are in control in the short term.
⚖️ Risk/Reward: 1:1.8
⏱️ Timeframe: 15M
#crypto #SAFE #trading #Bearish
💡 This analysis is for educational purposes and does not constitute financial advice. Do your own research and make your decision calmly.
📢 $SAFE / USDT | 🔴 SHORT | ⭐ 74%
🎯 Target: $0.0779048. Will it reach it?
🎯 Trading levels:
🔴 Entry: $0.07974
🛑 Stop Loss: $0.08076
🏁 TP1: $0.077905
🏁 TP2: $0.076885
🏁 TP3: $0.075662
📈 Analysis:
The market shows a clear bearish structure, with confirmed support breaks across multiple timeframes. Selling pressure is supported by a significant increase in trading volume, which is above average, while the relative strength indicator remains at weak levels. This combination of factors suggests that sellers are in control in the short term.
⚖️ Risk/Reward: 1:1.8
⏱️ Timeframe: 15M
#crypto #SAFE #trading #Bearish
💡 This analysis is for educational purposes and does not constitute financial advice. Do your own research and make your decision calmly.
🎯 Target: $0.0779048. Will it reach it?
🎯 Trading levels:
🔴 Entry: $0.07974
🛑 Stop Loss: $0.08076
🏁 TP1: $0.077905
🏁 TP2: $0.076885
🏁 TP3: $0.075662
📈 Analysis:
The market shows a clear bearish structure, with confirmed support breaks across multiple timeframes. Selling pressure is supported by a significant increase in trading volume, which is above average, while the relative strength indicator remains at weak levels. This combination of factors suggests that sellers are in control in the short term.
⚖️ Risk/Reward: 1:1.8
⏱️ Timeframe: 15M
#crypto #SAFE #trading #Bearish
💡 This analysis is for educational purposes and does not constitute financial advice. Do your own research and make your decision calmly.
4
·
--
🔍 INFRASTRUCTURE AND SECURITY IN FOCUS! $SAFE , $SAGA , and $OMNI offer different approaches to blockchain infrastructure and ecosystem tooling. Review their current development, usage, and token economics. Strong narratives can create volatility in both directions, so plan for downside too.
#Safe #Saga #OmniNetwork #BlockchainTech #CryptoAnalysis
🔍 INFRASTRUCTURE AND SECURITY IN FOCUS! $SAFE , $SAGA , and $OMNI offer different approaches to blockchain infrastructure and ecosystem tooling. Review their current development, usage, and token economics. Strong narratives can create volatility in both directions, so plan for downside too.
#Safe #Saga #OmniNetwork #BlockchainTech #CryptoAnalysis
#Safe #Saga #OmniNetwork #BlockchainTech #CryptoAnalysis
1
32
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaLoses$2.7TrillionInMonthAndAHalf
29 views
7 Discussing
2
#CanBTCReboundAfterFallingBelow60K?
474,329 views
2,048 Discussing
3
#GlobalStocksFaceLongestLosingStreakSince2023
163,420 views
1,439 Discussing
4
#BlackRockIBITPostsRecord$541MSingleDayOutflow
7,166 views
44 Discussing
5
#AnthropicPlungesTowardIPOPriceonDay2
78,091 views
821 Discussing
6
#TwentyOneCapitalAdds172.25BTC
29,436 views
358 Discussing
7
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
2,948 views
37 Discussing
8
#BNBDropsBelow540USDTWith8.46%DailyDecline
45,752 views
410 Discussing
9
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,619 views
20 Discussing
10
#BitMineFaces$10.1BUnrealizedETHLoss
3,340 views
25 Discussing