
#walletsecurity
walletsecurity
178,737 views
469 Discussing
Hot
Latest
Disconnecting a crypto app is not the same as removing its permission to spend your tokens.
A wallet connection and a token approval are separate permissions. MetaMask explains that disconnecting an app does not revoke the on-chain allowance previously granted to its smart contract.
Think of disconnecting as closing a conversation, not cancelling a spending authorization.
Before retiring an app, review its token approvals on the correct network using a trusted approval checker. Check which contract can spend which token, then revoke permissions you no longer need.
The catch: revocation is an on-chain transaction and costs gas. It removes that allowance, not every possible wallet risk. Verify the checker’s address before connecting or signing anything.
Source: https://support.metamask.com/more-web3/learn/how-to-revoke-smart-contract-allowances-token-approvals
#WalletSecurity #TokenApprovals #CryptoEducation #DeFi #Web3
Disconnecting a crypto app is not the same as removing its permission to spend your tokens.
A wallet connection and a token approval are separate permissions. MetaMask explains that disconnecting an app does not revoke the on-chain allowance previously granted to its smart contract.
Think of disconnecting as closing a conversation, not cancelling a spending authorization.
Before retiring an app, review its token approvals on the correct network using a trusted approval checker. Check which contract can spend which token, then revoke permissions you no longer need.
The catch: revocation is an on-chain transaction and costs gas. It removes that allowance, not every possible wallet risk. Verify the checker’s address before connecting or signing anything.
Source: https://support.metamask.com/more-web3/learn/how-to-revoke-smart-contract-allowances-token-approvals
#WalletSecurity #TokenApprovals #CryptoEducation #DeFi #Web3
A wallet connection and a token approval are separate permissions. MetaMask explains that disconnecting an app does not revoke the on-chain allowance previously granted to its smart contract.
Think of disconnecting as closing a conversation, not cancelling a spending authorization.
Before retiring an app, review its token approvals on the correct network using a trusted approval checker. Check which contract can spend which token, then revoke permissions you no longer need.
The catch: revocation is an on-chain transaction and costs gas. It removes that allowance, not every possible wallet risk. Verify the checker’s address before connecting or signing anything.
Source: https://support.metamask.com/more-web3/learn/how-to-revoke-smart-contract-allowances-token-approvals
#WalletSecurity #TokenApprovals #CryptoEducation #DeFi #Web3
56

·
--
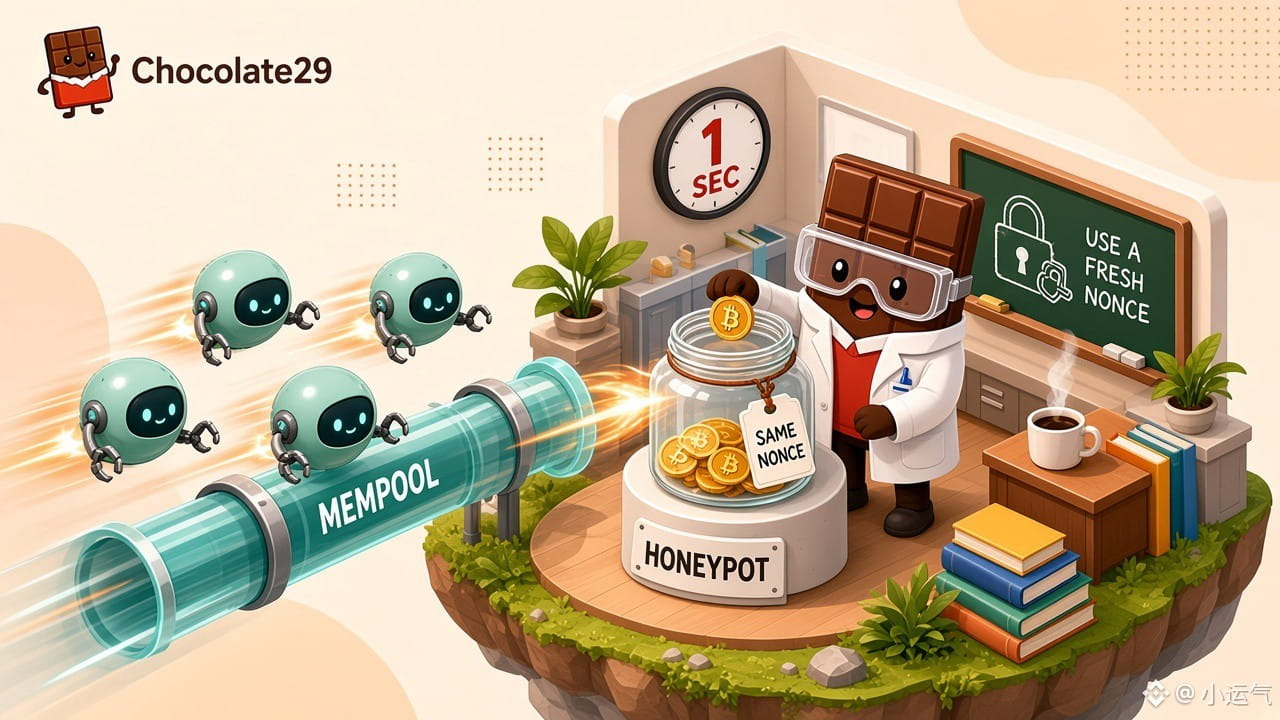
Two university researchers left a few dollars in deliberately flawed bitcoin wallets, and automated bots tried to grab the coins within seconds.
As reported by CoinDesk on November 20, 2026, Vincent Jacquot and Benoît Donnet of Belgium's University of Liège reused a signing "nonce" on purpose. Every ECDSA signature needs a fresh random number; if one key reuses it, anyone watching can work out the private key. On $BTC, rival transactions raced for the bait "a second or a few seconds" after it was set up.
Their scan of six blockchains through June 30, 2024 recovered 3,620 private keys, 3,278 of them on Bitcoin. Peak balances of the exposed addresses add up to about $106 million at November 2024 prices, though the team did not establish how much was actually taken. The weak spot is faulty wallet software, not the Bitcoin protocol, so stick to well-maintained, updated wallets.
#Bitcoin #WalletSecurity #CryptoResearch
DYOR. Not financial advice.
Two university researchers left a few dollars in deliberately flawed bitcoin wallets, and automated bots tried to grab the coins within seconds.
As reported by CoinDesk on November 20, 2026, Vincent Jacquot and Benoît Donnet of Belgium's University of Liège reused a signing "nonce" on purpose. Every ECDSA signature needs a fresh random number; if one key reuses it, anyone watching can work out the private key. On $BTC , rival transactions raced for the bait "a second or a few seconds" after it was set up.
Their scan of six blockchains through June 30, 2024 recovered 3,620 private keys, 3,278 of them on Bitcoin. Peak balances of the exposed addresses add up to about $106 million at November 2024 prices, though the team did not establish how much was actually taken. The weak spot is faulty wallet software, not the Bitcoin protocol, so stick to well-maintained, updated wallets.
#Bitcoin #WalletSecurity #CryptoResearch
DYOR. Not financial advice.
As reported by CoinDesk on November 20, 2026, Vincent Jacquot and Benoît Donnet of Belgium's University of Liège reused a signing "nonce" on purpose. Every ECDSA signature needs a fresh random number; if one key reuses it, anyone watching can work out the private key. On $BTC , rival transactions raced for the bait "a second or a few seconds" after it was set up.
Their scan of six blockchains through June 30, 2024 recovered 3,620 private keys, 3,278 of them on Bitcoin. Peak balances of the exposed addresses add up to about $106 million at November 2024 prices, though the team did not establish how much was actually taken. The weak spot is faulty wallet software, not the Bitcoin protocol, so stick to well-maintained, updated wallets.
#Bitcoin #WalletSecurity #CryptoResearch
DYOR. Not financial advice.
3
·
--
🎮 GTA VI had people refreshing feeds. Scammers wanted them connecting wallets.
Blockaid flagged 8,800+ GTA-themed tokens on Solana as malicious, suspicious or spam. If a GTA airdrop link lands in your feed, open the official publisher’s page separately and verify it there before connecting your wallet.
On the $SOL side, check whether the attention showed up in established meme names like $BONK Meanwhile, $RARE was up 14.96% in 24h. Tap the chart and see how much trading volume came in on the move.
What’s your first check when a viral headline suddenly has a token attached? 🔎
#GTAVI #Solana #WalletSecurity
🎮 GTA VI had people refreshing feeds. Scammers wanted them connecting wallets.
Blockaid flagged 8,800+ GTA-themed tokens on Solana as malicious, suspicious or spam. If a GTA airdrop link lands in your feed, open the official publisher’s page separately and verify it there before connecting your wallet.
On the $SOL side, check whether the attention showed up in established meme names like $BONK Meanwhile, $RARE was up 14.96% in 24h. Tap the chart and see how much trading volume came in on the move.
What’s your first check when a viral headline suddenly has a token attached? 🔎
#GTAVI #Solana #WalletSecurity
Blockaid flagged 8,800+ GTA-themed tokens on Solana as malicious, suspicious or spam. If a GTA airdrop link lands in your feed, open the official publisher’s page separately and verify it there before connecting your wallet.
On the $SOL side, check whether the attention showed up in established meme names like $BONK Meanwhile, $RARE was up 14.96% in 24h. Tap the chart and see how much trading volume came in on the move.
What’s your first check when a viral headline suddenly has a token attached? 🔎
#GTAVI #Solana #WalletSecurity
1
18

🚨 $BTC $ETH $BNB ALERT: APPROVAL PHISHING OPERATION NIAGARA UNVEILED! 🦈
🦈 Operation Niagara unites the OSC, U.S. Secret Service, RCMP and top analytics firms to sniff out approval phishing in real‑time. 📊 By flagging exposed token allowances before the drain, authorities turn the usual post‑mortem chase into a pre‑emptive shield for traders.
🔐 Your first line of defense remains personal: regularly revoke stale approvals, never sign contracts from unsolicited DMs, and keep cold storage isolated from active DeFi wallets. 📌 A disciplined audit routine cuts the most common leakage path used by smart‑money hunters.
💬 When was the last time you audited your wallet approvals?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ApprovalPhishing #WalletSecurity #Crypto
🛡️ 🔒
🚨 $BTC $ETH $BNB ALERT: APPROVAL PHISHING OPERATION NIAGARA UNVEILED! 🦈
🦈 Operation Niagara unites the OSC, U.S. Secret Service, RCMP and top analytics firms to sniff out approval phishing in real‑time. 📊 By flagging exposed token allowances before the drain, authorities turn the usual post‑mortem chase into a pre‑emptive shield for traders.
🔐 Your first line of defense remains personal: regularly revoke stale approvals, never sign contracts from unsolicited DMs, and keep cold storage isolated from active DeFi wallets. 📌 A disciplined audit routine cuts the most common leakage path used by smart‑money hunters.
💬 When was the last time you audited your wallet approvals?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ApprovalPhishing #WalletSecurity #Crypto
🛡️ 🔒
🦈 Operation Niagara unites the OSC, U.S. Secret Service, RCMP and top analytics firms to sniff out approval phishing in real‑time. 📊 By flagging exposed token allowances before the drain, authorities turn the usual post‑mortem chase into a pre‑emptive shield for traders.
🔐 Your first line of defense remains personal: regularly revoke stale approvals, never sign contracts from unsolicited DMs, and keep cold storage isolated from active DeFi wallets. 📌 A disciplined audit routine cuts the most common leakage path used by smart‑money hunters.
💬 When was the last time you audited your wallet approvals?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ApprovalPhishing #WalletSecurity #Crypto
🛡️ 🔒
1

🚨 $BTC HOLDERS, YOUR WALLET PERMISSIONS ARE A SILENT TICKING TIME BOMB! 💣
Smart money doesn't just protect capital from market corrections; we ruthlessly lock down on-chain permissions before exploiters drain our $ETH and $BNB bags. 🦈
Global law enforcement agencies and top analytics firms just launched real-time tracking to flag exposed wallets, but ultimate defense starts with your own hygiene routine. 📊
When was the last time you revoked a dead smart contract permission or audited your active allowances? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #WalletSecurity #CryptoSafety #OnChain #RiskManagement
🔥 💎
🚨 $BTC HOLDERS, YOUR WALLET PERMISSIONS ARE A SILENT TICKING TIME BOMB! 💣
Smart money doesn't just protect capital from market corrections; we ruthlessly lock down on-chain permissions before exploiters drain our $ETH and $BNB bags. 🦈
Global law enforcement agencies and top analytics firms just launched real-time tracking to flag exposed wallets, but ultimate defense starts with your own hygiene routine. 📊
When was the last time you revoked a dead smart contract permission or audited your active allowances? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #WalletSecurity #CryptoSafety #OnChain #RiskManagement
🔥 💎
Smart money doesn't just protect capital from market corrections; we ruthlessly lock down on-chain permissions before exploiters drain our $ETH and $BNB bags. 🦈
Global law enforcement agencies and top analytics firms just launched real-time tracking to flag exposed wallets, but ultimate defense starts with your own hygiene routine. 📊
When was the last time you revoked a dead smart contract permission or audited your active allowances? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #WalletSecurity #CryptoSafety #OnChain #RiskManagement
🔥 💎
1
·
--
Beyond the previous ETF news, a peer-reviewed study from the University of Liège reveals a different security angle: nonce reuse in an ECDSA signature can expose the private key. Researchers recovered 3,620 keys across 6 networks and observed bots moving within seconds; but the study doesn’t prove that all the funds were stolen. ⚠️🔐🧪 How can we prevent this mistake?
$BTC #Bitcoin #WalletSecurity
Beyond the previous ETF news, a peer-reviewed study from the University of Liège reveals a different security angle: nonce reuse in an ECDSA signature can expose the private key. Researchers recovered 3,620 keys across 6 networks and observed bots moving within seconds; but the study doesn’t prove that all the funds were stolen. ⚠️🔐🧪 How can we prevent this mistake?
$BTC #Bitcoin #WalletSecurity
$BTC #Bitcoin #WalletSecurity
26

A matching Merkle root no longer proves the transactions are the same.
Advisory GHSA-8vv3-6qpc-gpw6 (CVSS 9.3): bitcoinjs-lib's checkTxRoots misses duplicated transactions that pad an odd Merkle level. A peer can send a block with a different transaction list but the same root and hash. No mining needed.
Why it matters for $BTC builders: SPV clients, explorers or deposit logic that trust checkTxRoots could credit one deposit twice.
What to do:
• Check your lockfile
• Upgrade to 5.2.1, 6.1.8 or 7.0.2
• Below v5 there is no patch
• Don't just blacklist the block hash in response: it may reject an honest block
Verdict: PROVEN, confidence: high.
Watchpoint: if the advisory still lists no fix for versions below 5 on 16 Dec 2026, those users must migrate, not wait for a patch.
The Signal #004 from Cirqus Intelligence. Nihil sine probatione.
Does your deposit logic verify the transaction list itself, or only that its root looks right?
#Bitcoin #WalletSecurity #bitcoinjs #CryptoSecurity
A matching Merkle root no longer proves the transactions are the same.
Advisory GHSA-8vv3-6qpc-gpw6 (CVSS 9.3): bitcoinjs-lib's checkTxRoots misses duplicated transactions that pad an odd Merkle level. A peer can send a block with a different transaction list but the same root and hash. No mining needed.
Why it matters for $BTC builders: SPV clients, explorers or deposit logic that trust checkTxRoots could credit one deposit twice.
What to do:
• Check your lockfile
• Upgrade to 5.2.1, 6.1.8 or 7.0.2
• Below v5 there is no patch
• Don't just blacklist the block hash in response: it may reject an honest block
Verdict: PROVEN, confidence: high.
Watchpoint: if the advisory still lists no fix for versions below 5 on 16 Dec 2026, those users must migrate, not wait for a patch.
The Signal #004 from Cirqus Intelligence. Nihil sine probatione.
Does your deposit logic verify the transaction list itself, or only that its root looks right?
#Bitcoin #WalletSecurity #bitcoinjs #CryptoSecurity
Advisory GHSA-8vv3-6qpc-gpw6 (CVSS 9.3): bitcoinjs-lib's checkTxRoots misses duplicated transactions that pad an odd Merkle level. A peer can send a block with a different transaction list but the same root and hash. No mining needed.
Why it matters for $BTC builders: SPV clients, explorers or deposit logic that trust checkTxRoots could credit one deposit twice.
What to do:
• Check your lockfile
• Upgrade to 5.2.1, 6.1.8 or 7.0.2
• Below v5 there is no patch
• Don't just blacklist the block hash in response: it may reject an honest block
Verdict: PROVEN, confidence: high.
Watchpoint: if the advisory still lists no fix for versions below 5 on 16 Dec 2026, those users must migrate, not wait for a patch.
The Signal #004 from Cirqus Intelligence. Nihil sine probatione.
Does your deposit logic verify the transaction list itself, or only that its root looks right?
#Bitcoin #WalletSecurity #bitcoinjs #CryptoSecurity
1
119

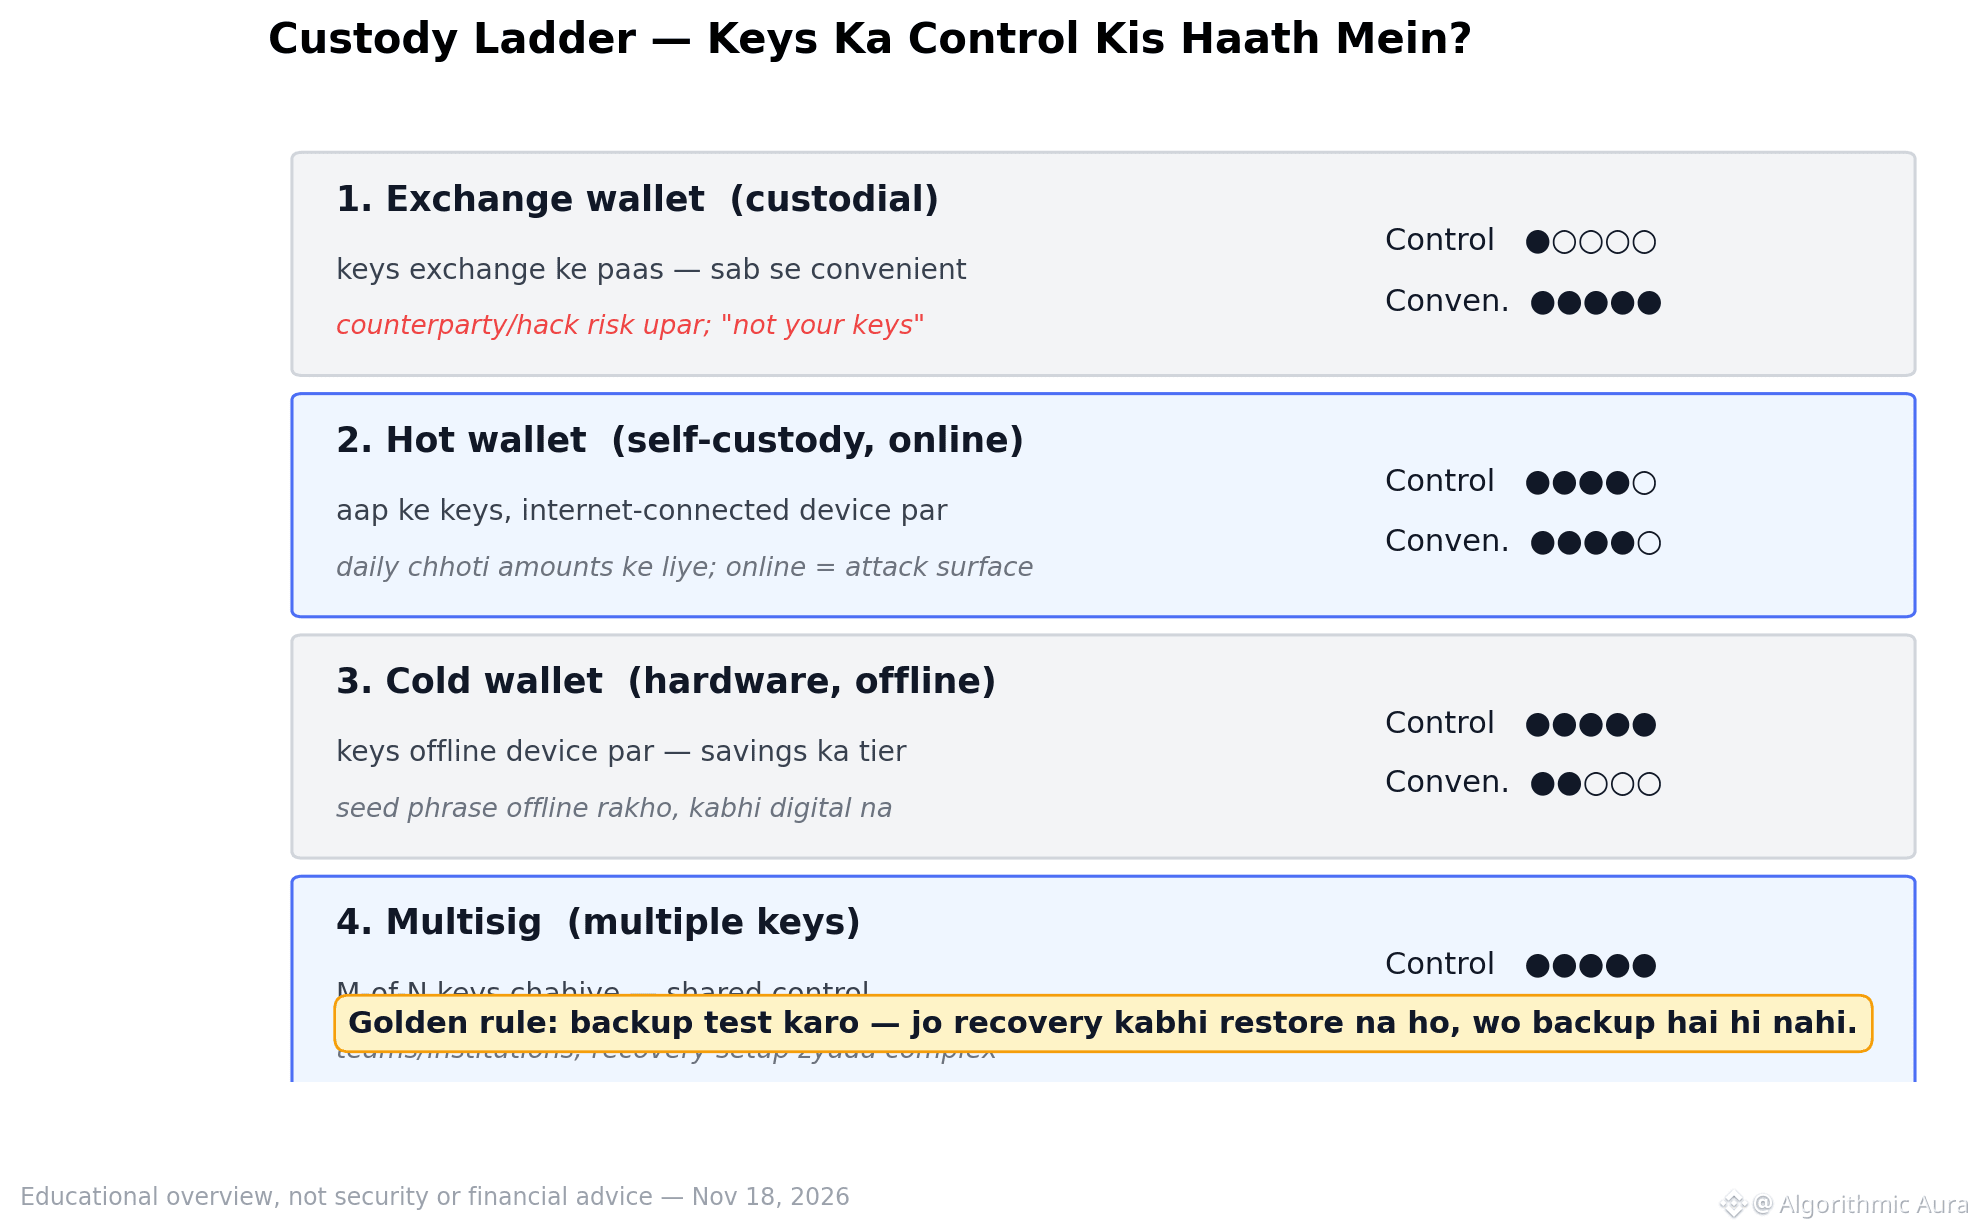
🔐 One chart: the custody ladder — who controls the keys?
1️⃣ Exchange (custodial): convenient, the exchange holds the keys — counterparty risk
2️⃣ Hot wallet: self-custody, online — daily amounts; online = attack surface
3️⃣ Cold wallet: hardware, offline — savings; keep the seed phrase offline, never digital
4️⃣ Multisig: multiple keys — for teams; recovery is more complex
Trade-off: as convenience increases, control decreases; with more control comes the responsibility of recovery.
Golden rule: test your backup — if it’s never been restored, it isn’t really a backup.
$BTC #SelfCustody #WalletSecurity #CryptoEducation
🔐 One chart: the custody ladder — who controls the keys?
1️⃣ Exchange (custodial): convenient, the exchange holds the keys — counterparty risk
2️⃣ Hot wallet: self-custody, online — daily amounts; online = attack surface
3️⃣ Cold wallet: hardware, offline — savings; keep the seed phrase offline, never digital
4️⃣ Multisig: multiple keys — for teams; recovery is more complex
Trade-off: as convenience increases, control decreases; with more control comes the responsibility of recovery.
Golden rule: test your backup — if it’s never been restored, it isn’t really a backup.
$BTC #SelfCustody #WalletSecurity #CryptoEducation
1️⃣ Exchange (custodial): convenient, the exchange holds the keys — counterparty risk
2️⃣ Hot wallet: self-custody, online — daily amounts; online = attack surface
3️⃣ Cold wallet: hardware, offline — savings; keep the seed phrase offline, never digital
4️⃣ Multisig: multiple keys — for teams; recovery is more complex
Trade-off: as convenience increases, control decreases; with more control comes the responsibility of recovery.
Golden rule: test your backup — if it’s never been restored, it isn’t really a backup.
$BTC #SelfCustody #WalletSecurity #CryptoEducation
3

·
--
Optimizely Code Hijacking Affects 176 Sites, Wallet Addresses Secretly Replaced
A wallet hijacking incident propagated through a third-party code platform is spreading. The number of affected sites has reached 176. The attack chain has expanded from crypto-mining sites to ordinary websites, posing a systemic threat to retail investors’ asset security.
According to Decrypt, malicious code was injected into website testing platform Optimizely. When visitors access compromised pages, their wallet addresses are quietly replaced with addresses controlled by the attackers, causing transferred funds to go to them instead. The incident involves well-known sites such as the BBC, and its scope far exceeds that of previous cases, which primarily involved crypto-mining hijacking.
The significance of this incident is that it reveals an escalation in attack methods. Wallet hijacking previously focused mostly on crypto-mining scenarios, but this attack was propagated through a SaaS code platform, meaning any website using the platform could become a stepping stone. The attack chain’s spread is more difficult to detect, making it more challenging to trace its origins and determine responsibility.
According to Decrypt, 176 sites have been hijacked. This means a vulnerability in a single third-party service could be amplified into a large-scale attack spanning multiple sites and users. Retail investors are generally not sufficiently aware of the risks. If an address is replaced without their noticing, the resulting losses may be impossible to recover.
For the market, the impact of such security incidents is usually limited, causing more localized disruption to trust than systemic risk. However, given how much crypto infrastructure depends on security, if the incident continues to spread, it could undermine users’ trust in third-party tools and on-chain interactions.
On the other hand, the scale of direct losses is currently difficult to quantify, and the incident is concentrated among users of a specific code platform, so it may not affect the prices of major assets. Market sentiment has not yet shown any clear spillover effects.
Next, it will be important to monitor Optimizely’s response and remediation progress, how affected sites are cleaned up, and whether cases involving larger-scale financial losses emerge. The chain through which security incidents spread warrants ongoing attention, rather than a one-time look.
#CryptoSecurity #WalletSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
Optimizely Code Hijacking Affects 176 Sites, Wallet Addresses Secretly Replaced
A wallet hijacking incident propagated through a third-party code platform is spreading. The number of affected sites has reached 176. The attack chain has expanded from crypto-mining sites to ordinary websites, posing a systemic threat to retail investors’ asset security.
According to Decrypt, malicious code was injected into website testing platform Optimizely. When visitors access compromised pages, their wallet addresses are quietly replaced with addresses controlled by the attackers, causing transferred funds to go to them instead. The incident involves well-known sites such as the BBC, and its scope far exceeds that of previous cases, which primarily involved crypto-mining hijacking.
The significance of this incident is that it reveals an escalation in attack methods. Wallet hijacking previously focused mostly on crypto-mining scenarios, but this attack was propagated through a SaaS code platform, meaning any website using the platform could become a stepping stone. The attack chain’s spread is more difficult to detect, making it more challenging to trace its origins and determine responsibility.
According to Decrypt, 176 sites have been hijacked. This means a vulnerability in a single third-party service could be amplified into a large-scale attack spanning multiple sites and users. Retail investors are generally not sufficiently aware of the risks. If an address is replaced without their noticing, the resulting losses may be impossible to recover.
For the market, the impact of such security incidents is usually limited, causing more localized disruption to trust than systemic risk. However, given how much crypto infrastructure depends on security, if the incident continues to spread, it could undermine users’ trust in third-party tools and on-chain interactions.
On the other hand, the scale of direct losses is currently difficult to quantify, and the incident is concentrated among users of a specific code platform, so it may not affect the prices of major assets. Market sentiment has not yet shown any clear spillover effects.
Next, it will be important to monitor Optimizely’s response and remediation progress, how affected sites are cleaned up, and whether cases involving larger-scale financial losses emerge. The chain through which security incidents spread warrants ongoing attention, rather than a one-time look.
#CryptoSecurity #WalletSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
A wallet hijacking incident propagated through a third-party code platform is spreading. The number of affected sites has reached 176. The attack chain has expanded from crypto-mining sites to ordinary websites, posing a systemic threat to retail investors’ asset security.
According to Decrypt, malicious code was injected into website testing platform Optimizely. When visitors access compromised pages, their wallet addresses are quietly replaced with addresses controlled by the attackers, causing transferred funds to go to them instead. The incident involves well-known sites such as the BBC, and its scope far exceeds that of previous cases, which primarily involved crypto-mining hijacking.
The significance of this incident is that it reveals an escalation in attack methods. Wallet hijacking previously focused mostly on crypto-mining scenarios, but this attack was propagated through a SaaS code platform, meaning any website using the platform could become a stepping stone. The attack chain’s spread is more difficult to detect, making it more challenging to trace its origins and determine responsibility.
According to Decrypt, 176 sites have been hijacked. This means a vulnerability in a single third-party service could be amplified into a large-scale attack spanning multiple sites and users. Retail investors are generally not sufficiently aware of the risks. If an address is replaced without their noticing, the resulting losses may be impossible to recover.
For the market, the impact of such security incidents is usually limited, causing more localized disruption to trust than systemic risk. However, given how much crypto infrastructure depends on security, if the incident continues to spread, it could undermine users’ trust in third-party tools and on-chain interactions.
On the other hand, the scale of direct losses is currently difficult to quantify, and the incident is concentrated among users of a specific code platform, so it may not affect the prices of major assets. Market sentiment has not yet shown any clear spillover effects.
Next, it will be important to monitor Optimizely’s response and remediation progress, how affected sites are cleaned up, and whether cases involving larger-scale financial losses emerge. The chain through which security incidents spread warrants ongoing attention, rather than a one-time look.
#CryptoSecurity #WalletSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
76
You approved it once. It's still active.
A token approval doesn't expire by itself. One approval covers one contract, one token, one network, and it stays there until you remove it.
A quick check:
— Type revoke.cash yourself. Don't tap a link
— Paste your public address. No wallet connection needed
— Pick a network. Approvals are per chain, so check each one you've used, $ETH side and $BNB side alike
— Sort by Allowance and find Unlimited
— Revoke what you no longer use
Keep it honest:
— Unlimited is a bigger risk, not proof of a hack
— Some apps need their approval, so don't revoke blindly
— Each revoke costs gas
— If your seed phrase is compromised, revoking is not enough: move to a new wallet
This is a how-to, not a verdict. No hallmark, no guarantees.
When did you last look at what your wallet still trusts?
#WalletSecurity #TokenApprovals #Web3Security #Revokecash
You approved it once. It's still active.
A token approval doesn't expire by itself. One approval covers one contract, one token, one network, and it stays there until you remove it.
A quick check:
— Type revoke.cash yourself. Don't tap a link
— Paste your public address. No wallet connection needed
— Pick a network. Approvals are per chain, so check each one you've used, $ETH side and $BNB side alike
— Sort by Allowance and find Unlimited
— Revoke what you no longer use
Keep it honest:
— Unlimited is a bigger risk, not proof of a hack
— Some apps need their approval, so don't revoke blindly
— Each revoke costs gas
— If your seed phrase is compromised, revoking is not enough: move to a new wallet
This is a how-to, not a verdict. No hallmark, no guarantees.
When did you last look at what your wallet still trusts?
#WalletSecurity #TokenApprovals #Web3Security #Revokecash
A token approval doesn't expire by itself. One approval covers one contract, one token, one network, and it stays there until you remove it.
A quick check:
— Type revoke.cash yourself. Don't tap a link
— Paste your public address. No wallet connection needed
— Pick a network. Approvals are per chain, so check each one you've used, $ETH side and $BNB side alike
— Sort by Allowance and find Unlimited
— Revoke what you no longer use
Keep it honest:
— Unlimited is a bigger risk, not proof of a hack
— Some apps need their approval, so don't revoke blindly
— Each revoke costs gas
— If your seed phrase is compromised, revoking is not enough: move to a new wallet
This is a how-to, not a verdict. No hallmark, no guarantees.
When did you last look at what your wallet still trusts?
#WalletSecurity #TokenApprovals #Web3Security #Revokecash
1
61

·
--
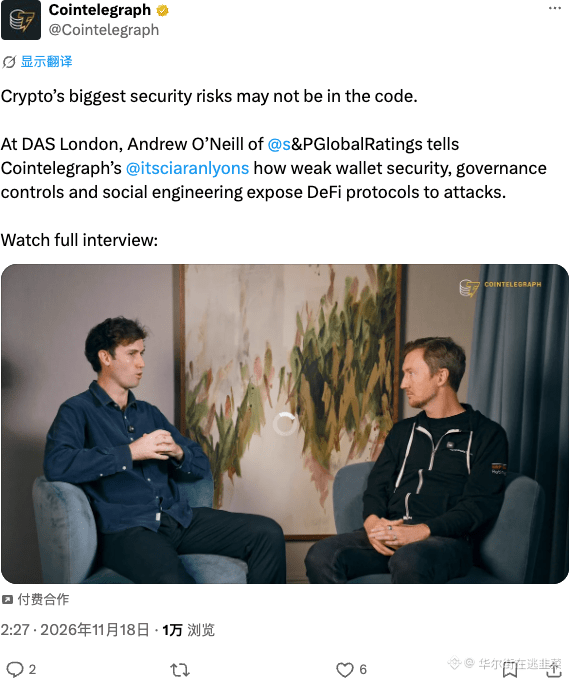
A Morgan Stanley executive put it bluntly: the biggest security vulnerabilities in crypto aren’t in the code, but in poor wallet security, out-of-control governance, and social engineering. People scrutinize code audits every day, yet manage their private keys terribly. That “the butcher holds the knife while I’m the meat” situation is the most deadly of all.
#DeFi #WalletSecurity
A Morgan Stanley executive put it bluntly: the biggest security vulnerabilities in crypto aren’t in the code, but in poor wallet security, out-of-control governance, and social engineering. People scrutinize code audits every day, yet manage their private keys terribly. That “the butcher holds the knife while I’m the meat” situation is the most deadly of all.
#DeFi #WalletSecurity
#DeFi #WalletSecurity
8
🚨 SAFE Wallet Suspected of Key Leak; $6.5 Million Stolen 🧠
📊 | $BTC | $ETH | $BNB |
- Follow and leave a comment to share your thoughts 📈
- SAFE Wallet reportedly had $6.5 million stolen after a suspected private key leak
- A Zodiac co-founder said the issue stemmed from a compromised key and overly broad wallet permissions
- They emphasized that the vulnerability was not due to a smart contract flaw
- The incident once again highlights the importance of wallet permission management and key security 🔥
- This crypto theft may lead to short-term caution in the market
- If the investigation confirms that a single key was compromised, the impact on overall trust in SAFE may be limited
- Large investors are expected to remain on the sidelines in the short term, with whale activity trending neutral
- The market will likely remain range-bound in the short term
- Do you think strengthening private key security should be a priority? Join the discussion
- Follow and leave a comment to discuss market developments rationally
#Crypto #WalletSecurity #DeFi #Whales #Blockchain
🚨 SAFE Wallet Suspected of Key Leak; $6.5 Million Stolen 🧠
📊 | $BTC | $ETH | $BNB |
- Follow and leave a comment to share your thoughts 📈
- SAFE Wallet reportedly had $6.5 million stolen after a suspected private key leak
- A Zodiac co-founder said the issue stemmed from a compromised key and overly broad wallet permissions
- They emphasized that the vulnerability was not due to a smart contract flaw
- The incident once again highlights the importance of wallet permission management and key security 🔥
- This crypto theft may lead to short-term caution in the market
- If the investigation confirms that a single key was compromised, the impact on overall trust in SAFE may be limited
- Large investors are expected to remain on the sidelines in the short term, with whale activity trending neutral
- The market will likely remain range-bound in the short term
- Do you think strengthening private key security should be a priority? Join the discussion
- Follow and leave a comment to discuss market developments rationally
#Crypto #WalletSecurity #DeFi #Whales #Blockchain
📊 | $BTC | $ETH | $BNB |
- Follow and leave a comment to share your thoughts 📈
- SAFE Wallet reportedly had $6.5 million stolen after a suspected private key leak
- A Zodiac co-founder said the issue stemmed from a compromised key and overly broad wallet permissions
- They emphasized that the vulnerability was not due to a smart contract flaw
- The incident once again highlights the importance of wallet permission management and key security 🔥
- This crypto theft may lead to short-term caution in the market
- If the investigation confirms that a single key was compromised, the impact on overall trust in SAFE may be limited
- Large investors are expected to remain on the sidelines in the short term, with whale activity trending neutral
- The market will likely remain range-bound in the short term
- Do you think strengthening private key security should be a priority? Join the discussion
- Follow and leave a comment to discuss market developments rationally
#Crypto #WalletSecurity #DeFi #Whales #Blockchain
124

·
--
🚨 $ETH ECOSYSTEM SHIFT: NAVIGATING THE BLAST NETWORK SUNSET AND ASSET RECOVERY PROTOCOLS 🔍
Structural shifts require absolute precision in asset management as network infrastructure evolves. With the upcoming discontinuation of network support on a major wallet interface, historical balances displayed on-chain may no longer reflect true liquidity access. 📊
Smart participants understand that interface cutoffs do not invalidate base-layer ownership. Eligible holders must route claims directly through official Ethereum mainnet recovery channels rather than relying on legacy UI dashboards. 🛡️
Security remains paramount during structural migrations. Never expose private credentials or interact with unverified third-party claim links masquerading as support tools. 💡 What steps are you taking to audit your cold and hot storage exposures before the upcoming network cutoff date? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
🦈 🔒
🚨 $ETH ECOSYSTEM SHIFT: NAVIGATING THE BLAST NETWORK SUNSET AND ASSET RECOVERY PROTOCOLS 🔍
Structural shifts require absolute precision in asset management as network infrastructure evolves. With the upcoming discontinuation of network support on a major wallet interface, historical balances displayed on-chain may no longer reflect true liquidity access. 📊
Smart participants understand that interface cutoffs do not invalidate base-layer ownership. Eligible holders must route claims directly through official Ethereum mainnet recovery channels rather than relying on legacy UI dashboards. 🛡️
Security remains paramount during structural migrations. Never expose private credentials or interact with unverified third-party claim links masquerading as support tools. 💡 What steps are you taking to audit your cold and hot storage exposures before the upcoming network cutoff date? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
🦈 🔒
Structural shifts require absolute precision in asset management as network infrastructure evolves. With the upcoming discontinuation of network support on a major wallet interface, historical balances displayed on-chain may no longer reflect true liquidity access. 📊
Smart participants understand that interface cutoffs do not invalidate base-layer ownership. Eligible holders must route claims directly through official Ethereum mainnet recovery channels rather than relying on legacy UI dashboards. 🛡️
Security remains paramount during structural migrations. Never expose private credentials or interact with unverified third-party claim links masquerading as support tools. 💡 What steps are you taking to audit your cold and hot storage exposures before the upcoming network cutoff date? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
🦈 🔒
13

·
--
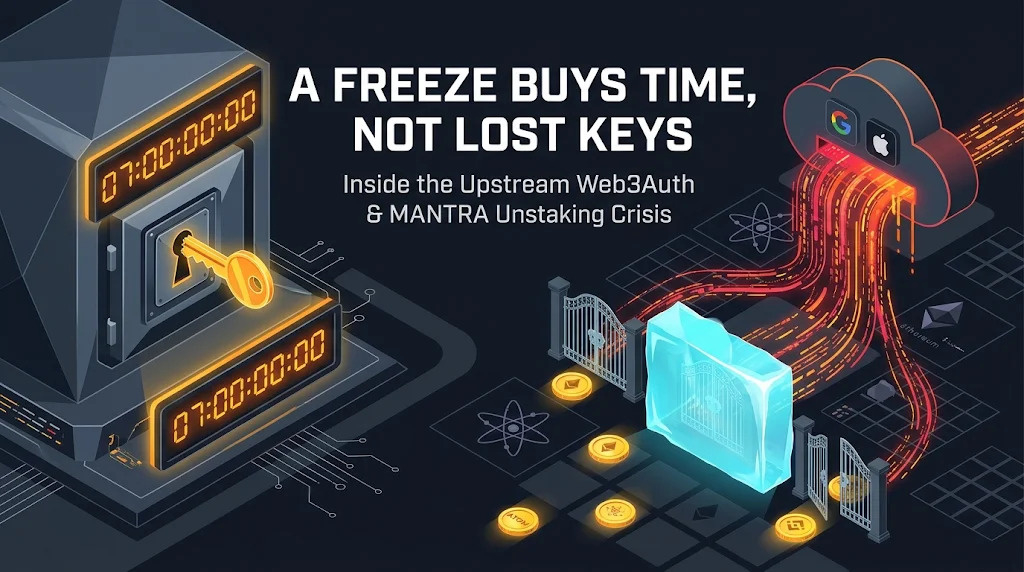
⚠️A seven-day unstaking freeze cannot reverse a stolen private key. It can only buy time.
On November 13, MANTRA paused all new unbonding transactions for seven days after reports that attackers were withdrawing staked MANTRA from compromised Keplr social-login wallets. It does not cancel withdrawals already in the eight-day unbonding queue.
MANTRA says affected holders must redelegate before that timer expires.
The weakness sits upstream: Web3Auth's embedded-wallet infrastructure, used by Keplr's Google/Apple login. Keplr says recovery-phrase and hardware-wallet accounts were not affected.
This is not evidence that Google or Apple accounts themselves were hacked.
Bitquery's November 12 investigation traced at least $1.82M taken between November 1–12 from 7,842 Cosmos wallets, 52 Ethereum wallets and 13 Hyperliquid accounts. More than $1.01M left before Web3Auth's first rescue sweep. Separately, Web3Auth moved roughly $6M into recovery wallets. That $6M is not a confirmed theft total.
The missing pieces are the technical root cause, final loss reconciliation and a confirmed return timetable.
MANTRA also suffered a separate upstream chain-accounting exploit in August. Different cause, but repeated security shocks across different layers matter for trust.
The freeze restricts exits; it does not repair compromised keys or protect every other chain.
Not financial advice.
$MANTRA
{future}(MANTRAUSDT)
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #mantra #WalletSecurity #CosmosEcosystem
⚠️A seven-day unstaking freeze cannot reverse a stolen private key. It can only buy time.
On November 13, MANTRA paused all new unbonding transactions for seven days after reports that attackers were withdrawing staked MANTRA from compromised Keplr social-login wallets. It does not cancel withdrawals already in the eight-day unbonding queue.
MANTRA says affected holders must redelegate before that timer expires.
The weakness sits upstream: Web3Auth's embedded-wallet infrastructure, used by Keplr's Google/Apple login. Keplr says recovery-phrase and hardware-wallet accounts were not affected.
This is not evidence that Google or Apple accounts themselves were hacked.
Bitquery's November 12 investigation traced at least $1.82M taken between November 1–12 from 7,842 Cosmos wallets, 52 Ethereum wallets and 13 Hyperliquid accounts. More than $1.01M left before Web3Auth's first rescue sweep. Separately, Web3Auth moved roughly $6M into recovery wallets. That $6M is not a confirmed theft total.
The missing pieces are the technical root cause, final loss reconciliation and a confirmed return timetable.
MANTRA also suffered a separate upstream chain-accounting exploit in August. Different cause, but repeated security shocks across different layers matter for trust.
The freeze restricts exits; it does not repair compromised keys or protect every other chain.
Not financial advice.
$MANTRA
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #mantra #WalletSecurity #CosmosEcosystem
On November 13, MANTRA paused all new unbonding transactions for seven days after reports that attackers were withdrawing staked MANTRA from compromised Keplr social-login wallets. It does not cancel withdrawals already in the eight-day unbonding queue.
MANTRA says affected holders must redelegate before that timer expires.
The weakness sits upstream: Web3Auth's embedded-wallet infrastructure, used by Keplr's Google/Apple login. Keplr says recovery-phrase and hardware-wallet accounts were not affected.
This is not evidence that Google or Apple accounts themselves were hacked.
Bitquery's November 12 investigation traced at least $1.82M taken between November 1–12 from 7,842 Cosmos wallets, 52 Ethereum wallets and 13 Hyperliquid accounts. More than $1.01M left before Web3Auth's first rescue sweep. Separately, Web3Auth moved roughly $6M into recovery wallets. That $6M is not a confirmed theft total.
The missing pieces are the technical root cause, final loss reconciliation and a confirmed return timetable.
MANTRA also suffered a separate upstream chain-accounting exploit in August. Different cause, but repeated security shocks across different layers matter for trust.
The freeze restricts exits; it does not repair compromised keys or protect every other chain.
Not financial advice.
$MANTRA
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #mantra #WalletSecurity #CosmosEcosystem
1
433

·
--
Bearish
MANTRA PAUSED UNSTAKING — BUT SOME WITHDRAWAL CLOCKS ARE STILL RUNNING
Imagine having your crypto locked in staking, only to discover someone else has started withdrawing it
That's the situation MANTRA is trying to contain
$MANTRA
{future}(MANTRAUSDT)
⚠️ Following reports of compromised Web3Auth and Keplr wallet access, MANTRA announced a 7-day emergency pause on new unstaking requests
Attackers reportedly stole liquid tokens before initiating unauthorized unstaking of $OM
But there's a dangerous exception
Existing unstaking requests are NOT frozen
The 8-day withdrawal countdown continues, potentially allowing attackers with compromised keys to claim the tokens when they become available
🔐 MANTRA has urged affected users to redelegate before that countdown ends
Redelegation may stop an ongoing withdrawal, but it cannot make an exposed private key secure again
Not every Keplr wallet is necessarily compromised
If you're affected, check your staking status and follow official recovery instructions — never enter your recovery phrase into an unsolicited website
A temporary pause buys time
What users do with that time matters
{spot}(MANTRAUSDT)
$MANTRA #WalletSecurity #CryptoSecurity
MANTRA PAUSED UNSTAKING — BUT SOME WITHDRAWAL CLOCKS ARE STILL RUNNING
Imagine having your crypto locked in staking, only to discover someone else has started withdrawing it
That's the situation MANTRA is trying to contain
$MANTRA
⚠️ Following reports of compromised Web3Auth and Keplr wallet access, MANTRA announced a 7-day emergency pause on new unstaking requests
Attackers reportedly stole liquid tokens before initiating unauthorized unstaking of $OM
But there's a dangerous exception
Existing unstaking requests are NOT frozen
The 8-day withdrawal countdown continues, potentially allowing attackers with compromised keys to claim the tokens when they become available
🔐 MANTRA has urged affected users to redelegate before that countdown ends
Redelegation may stop an ongoing withdrawal, but it cannot make an exposed private key secure again
Not every Keplr wallet is necessarily compromised
If you're affected, check your staking status and follow official recovery instructions — never enter your recovery phrase into an unsolicited website
A temporary pause buys time
What users do with that time matters
$MANTRA #WalletSecurity #CryptoSecurity
Imagine having your crypto locked in staking, only to discover someone else has started withdrawing it
That's the situation MANTRA is trying to contain
$MANTRA
⚠️ Following reports of compromised Web3Auth and Keplr wallet access, MANTRA announced a 7-day emergency pause on new unstaking requests
Attackers reportedly stole liquid tokens before initiating unauthorized unstaking of $OM
But there's a dangerous exception
Existing unstaking requests are NOT frozen
The 8-day withdrawal countdown continues, potentially allowing attackers with compromised keys to claim the tokens when they become available
🔐 MANTRA has urged affected users to redelegate before that countdown ends
Redelegation may stop an ongoing withdrawal, but it cannot make an exposed private key secure again
Not every Keplr wallet is necessarily compromised
If you're affected, check your staking status and follow official recovery instructions — never enter your recovery phrase into an unsolicited website
A temporary pause buys time
What users do with that time matters
$MANTRA #WalletSecurity #CryptoSecurity
423

⚠️ $MANTRA PAUSED UNSTAKING WHILE ATTACKERS KEEP THE CLOCK TICKING 🦈
📊 The 7‑day emergency pause bought a narrow window, but the 8‑day withdrawal countdown stays alive, letting compromised keys still pull liquid tokens. 🕵️♂️ Smart money is already scanning the order flow for any residual exits, and volume spikes could signal a last‑minute sweep.
💡 Redelegate now if you spot an active request – it can halt the pending pull, though it won’t patch a leaked . Stay razor‑sharp, audit your Keplr access, and keep the recovery steps locked down. 🤔 Are you redelegating before the timer runs out?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #MANTRA #WalletSecurity #Staking #Crypto
🦈 🔥
⚠️ $MANTRA PAUSED UNSTAKING WHILE ATTACKERS KEEP THE CLOCK TICKING 🦈
📊 The 7‑day emergency pause bought a narrow window, but the 8‑day withdrawal countdown stays alive, letting compromised keys still pull liquid tokens. 🕵️♂️ Smart money is already scanning the order flow for any residual exits, and volume spikes could signal a last‑minute sweep.
💡 Redelegate now if you spot an active request – it can halt the pending pull, though it won’t patch a leaked . Stay razor‑sharp, audit your Keplr access, and keep the recovery steps locked down. 🤔 Are you redelegating before the timer runs out?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #MANTRA #WalletSecurity #Staking #Crypto
🦈 🔥
📊 The 7‑day emergency pause bought a narrow window, but the 8‑day withdrawal countdown stays alive, letting compromised keys still pull liquid tokens. 🕵️♂️ Smart money is already scanning the order flow for any residual exits, and volume spikes could signal a last‑minute sweep.
💡 Redelegate now if you spot an active request – it can halt the pending pull, though it won’t patch a leaked . Stay razor‑sharp, audit your Keplr access, and keep the recovery steps locked down. 🤔 Are you redelegating before the timer runs out?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #MANTRA #WalletSecurity #Staking #Crypto
🦈 🔥
15
On 31 October 2024, one SMS stopped a thief mid-withdrawal.
About $2,000 was taken from our founder in total, including 1.088 BNB. It was stolen from MetaMask, Trust Wallet and an OKX account.
On HTX, the attacker got into the account and converted the assets to $BNB. The withdrawal still failed: an SMS confirmation went to a separate phone number.
We could not establish how they got in. Working hypothesis: the laptop, handed to a stranger for repair, running unlicensed Windows with no antivirus. Circumstances, not a proven cause.
This is not a claim that SMS is strong. SIM-swaps exist. It is one narrow observation: a separate channel stopped the withdrawal. That is all the first C·H·A·O· hallmark on HTX says. It is not a security audit of the exchange.
The lesson: don't trust, verify. Nihil sine probatione.
So Cirqus Intelligence is launching The Cirqus Register. It publishes shifts, not news. Every forecast gets a date and a criterion for whether it came true. Once a month we check our own calls, misses first. No trading signals, no price calls.
The Q is not a typo. It's the lens.
AI agents help with research, a Verifier checks the claims, and a human approves every issue.
Which of your withdrawals still depends on a single device?
#CryptoSecurity #Binance #WalletSecurity #CirqusRegister
On 31 October 2024, one SMS stopped a thief mid-withdrawal.
About $2,000 was taken from our founder in total, including 1.088 BNB. It was stolen from MetaMask, Trust Wallet and an OKX account.
On HTX, the attacker got into the account and converted the assets to $BNB . The withdrawal still failed: an SMS confirmation went to a separate phone number.
We could not establish how they got in. Working hypothesis: the laptop, handed to a stranger for repair, running unlicensed Windows with no antivirus. Circumstances, not a proven cause.
This is not a claim that SMS is strong. SIM-swaps exist. It is one narrow observation: a separate channel stopped the withdrawal. That is all the first C·H·A·O· hallmark on HTX says. It is not a security audit of the exchange.
The lesson: don't trust, verify. Nihil sine probatione.
So Cirqus Intelligence is launching The Cirqus Register. It publishes shifts, not news. Every forecast gets a date and a criterion for whether it came true. Once a month we check our own calls, misses first. No trading signals, no price calls.
The Q is not a typo. It's the lens.
AI agents help with research, a Verifier checks the claims, and a human approves every issue.
Which of your withdrawals still depends on a single device?
#CryptoSecurity #Binance #WalletSecurity #CirqusRegister
About $2,000 was taken from our founder in total, including 1.088 BNB. It was stolen from MetaMask, Trust Wallet and an OKX account.
On HTX, the attacker got into the account and converted the assets to $BNB . The withdrawal still failed: an SMS confirmation went to a separate phone number.
We could not establish how they got in. Working hypothesis: the laptop, handed to a stranger for repair, running unlicensed Windows with no antivirus. Circumstances, not a proven cause.
This is not a claim that SMS is strong. SIM-swaps exist. It is one narrow observation: a separate channel stopped the withdrawal. That is all the first C·H·A·O· hallmark on HTX says. It is not a security audit of the exchange.
The lesson: don't trust, verify. Nihil sine probatione.
So Cirqus Intelligence is launching The Cirqus Register. It publishes shifts, not news. Every forecast gets a date and a criterion for whether it came true. Once a month we check our own calls, misses first. No trading signals, no price calls.
The Q is not a typo. It's the lens.
AI agents help with research, a Verifier checks the claims, and a human approves every issue.
Which of your withdrawals still depends on a single device?
#CryptoSecurity #Binance #WalletSecurity #CirqusRegister
1
135

·
--
Disconnecting Isn’t the Same as Revoking Wallet Permissions
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
Disconnecting Isn’t the Same as Revoking Wallet Permissions
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
7
·
--
Bearish
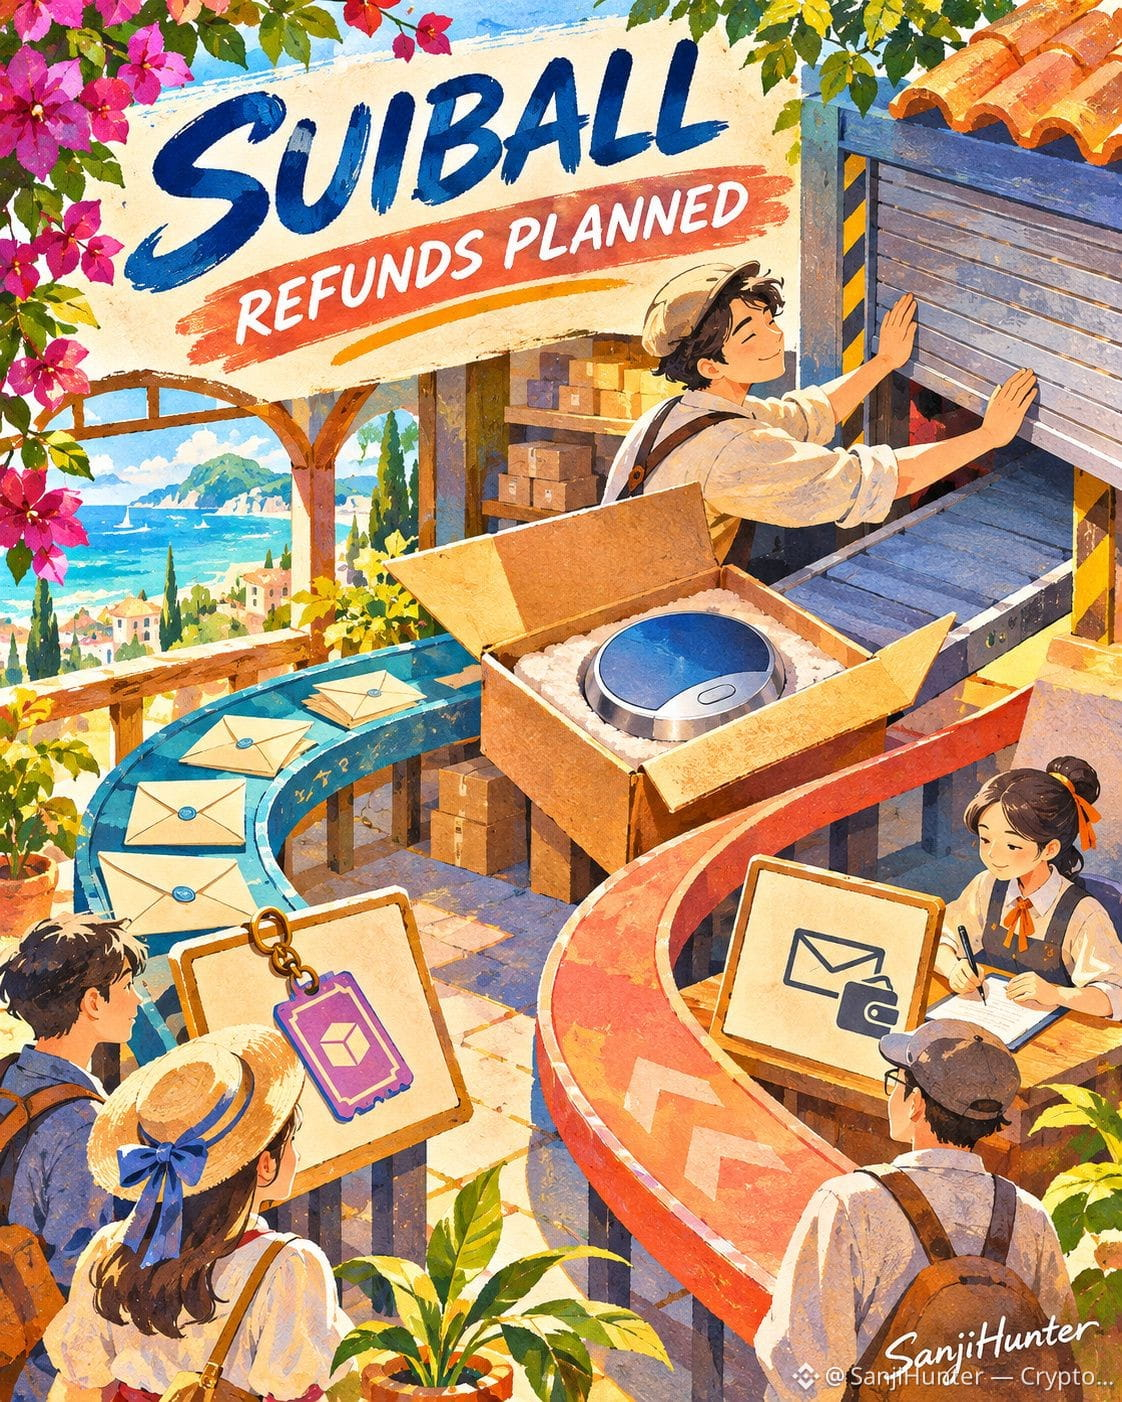
🚨 A $SUI hardware wallet was ready to ship — now the entire project is shutting down
Suiball has announced the cancellation of its hardware wallet launch and promised USDC refunds for all pre-orders
The team says security concerns led the Sui Foundation to withdraw support
But the most important detail for customers is HOW they paid 👇
$SUI
{future}(SUIUSDT)
🔹 On-chain pre-orders — Around 80% of orders will receive automatic USDC refunds to wallets holding their soulbound reservation NFTs
No claim or wallet connection required
🔹 Credit-card pre-orders — Customers will receive an email requesting a Sui wallet address for a separate refund distribution
⚠️ Suiball says it will NEVER request seed phrases, private keys or additional payments
Verify communications through official channels before responding
A refund email can be spoofed — even when the sender looks familiar
This is a hardware wallet project shutdown, NOT evidence that the Sui blockchain itself was hacked
{spot}(SUIUSDT)
The next milestone is confirmed refund transactions, not another promise
A scheduled refund isn't the same as money returned
$SUI #SUİ #WalletSecurity
🚨 A $SUI hardware wallet was ready to ship — now the entire project is shutting down
Suiball has announced the cancellation of its hardware wallet launch and promised USDC refunds for all pre-orders
The team says security concerns led the Sui Foundation to withdraw support
But the most important detail for customers is HOW they paid 👇
$SUI
🔹 On-chain pre-orders — Around 80% of orders will receive automatic USDC refunds to wallets holding their soulbound reservation NFTs
No claim or wallet connection required
🔹 Credit-card pre-orders — Customers will receive an email requesting a Sui wallet address for a separate refund distribution
⚠️ Suiball says it will NEVER request seed phrases, private keys or additional payments
Verify communications through official channels before responding
A refund email can be spoofed — even when the sender looks familiar
This is a hardware wallet project shutdown, NOT evidence that the Sui blockchain itself was hacked
The next milestone is confirmed refund transactions, not another promise
A scheduled refund isn't the same as money returned
$SUI #SUİ #WalletSecurity
Suiball has announced the cancellation of its hardware wallet launch and promised USDC refunds for all pre-orders
The team says security concerns led the Sui Foundation to withdraw support
But the most important detail for customers is HOW they paid 👇
$SUI
🔹 On-chain pre-orders — Around 80% of orders will receive automatic USDC refunds to wallets holding their soulbound reservation NFTs
No claim or wallet connection required
🔹 Credit-card pre-orders — Customers will receive an email requesting a Sui wallet address for a separate refund distribution
⚠️ Suiball says it will NEVER request seed phrases, private keys or additional payments
Verify communications through official channels before responding
A refund email can be spoofed — even when the sender looks familiar
This is a hardware wallet project shutdown, NOT evidence that the Sui blockchain itself was hacked
The next milestone is confirmed refund transactions, not another promise
A scheduled refund isn't the same as money returned
$SUI #SUİ #WalletSecurity
233
Multiple Bitcoin keys do not help much if one theft exposes all of them.
A multisignature wallet can require several independent approvals before spending $BTC. For example, a two-of-three setup needs any two signing keys—not just a password on one device.
The practical benefit is separation: stealing one key alone is insufficient. But keeping every key and backup together can undermine that protection.
Before choosing this setup, map which devices and locations could fail together. Then check whether enough signing keys would remain available to recover access.
The trade-off is complexity: losing access to too many keys can lock you out. Multisignature changes the security design; it does not remove the need for careful backups.
Source: Bitcoin.org — https://bitcoin.org/en/secure-your-wallet
#Bitcoin #WalletSecurity #Multisig #CryptoEducation #SelfCustody
Multiple Bitcoin keys do not help much if one theft exposes all of them.
A multisignature wallet can require several independent approvals before spending $BTC . For example, a two-of-three setup needs any two signing keys—not just a password on one device.
The practical benefit is separation: stealing one key alone is insufficient. But keeping every key and backup together can undermine that protection.
Before choosing this setup, map which devices and locations could fail together. Then check whether enough signing keys would remain available to recover access.
The trade-off is complexity: losing access to too many keys can lock you out. Multisignature changes the security design; it does not remove the need for careful backups.
Source: Bitcoin.org — https://bitcoin.org/en/secure-your-wallet
#Bitcoin #WalletSecurity #Multisig #CryptoEducation #SelfCustody
A multisignature wallet can require several independent approvals before spending $BTC . For example, a two-of-three setup needs any two signing keys—not just a password on one device.
The practical benefit is separation: stealing one key alone is insufficient. But keeping every key and backup together can undermine that protection.
Before choosing this setup, map which devices and locations could fail together. Then check whether enough signing keys would remain available to recover access.
The trade-off is complexity: losing access to too many keys can lock you out. Multisignature changes the security design; it does not remove the need for careful backups.
Source: Bitcoin.org — https://bitcoin.org/en/secure-your-wallet
#Bitcoin #WalletSecurity #Multisig #CryptoEducation #SelfCustody
71
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanBTCReboundAfterFallingBelow60K?
369,886 views
1,555 Discussing
2
#GlobalStocksFaceLongestLosingStreakSince2023
122,357 views
1,094 Discussing
3
#BlackRockIBITPostsRecord$541MSingleDayOutflow
692 views
17 Discussing
4
#AnthropicPlungesTowardIPOPriceonDay2
58,891 views
596 Discussing
5
#TwentyOneCapitalAdds172.25BTC
11,483 views
162 Discussing
6
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
972 views
14 Discussing
7
#BNBDropsBelow540USDTWith8.46%DailyDecline
32,204 views
277 Discussing
8
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,056 views
14 Discussing
9
#BitMineFaces$10.1BUnrealizedETHLoss
2,007 views
18 Discussing
10
#StrategyReports$35BNetReserves
1,983 views
18 Discussing